Skip to content
November 12, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
  • Home
  • Technique
  • Ways to Mitigate Risks of Cyber Threats at Your Workplace
  • Technique

Ways to Mitigate Risks of Cyber Threats at Your Workplace

Do Son April 21, 2022 4 minutes read
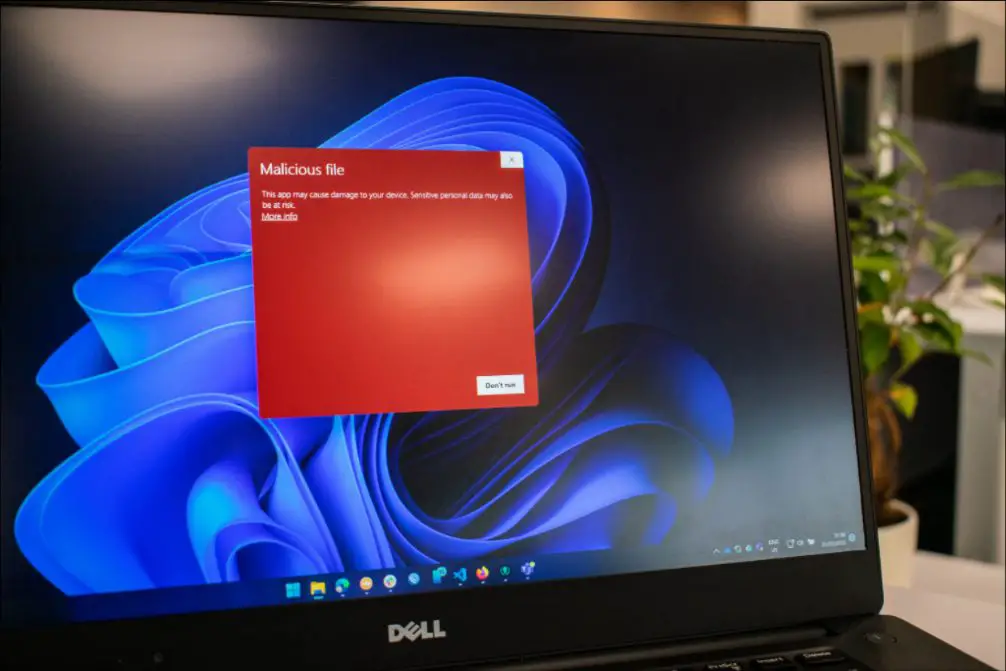
Img_2022_04_15_01_44_51

The digital world can be a scary place, especially when it comes to your business or workplace. Customer information and private data are a disaster if leaked to inappropriate parties or publicly. 

Luckily, there are preventative measures you can take to manage cyber risks, such as creating a business continuity plan, in case your workplace’s network is ever threatened or hacked. You can check out Digitalspotlight.com.au for their digital marketing services.

What Are Cyber Threats?

Cyber threats or cyber-attacks are digital acts of maliciousness. A cyber threat or attack intends to damage data, steal data, or disrupt digital life in general. They can manifest as computer viruses, data breaches, and Denial of Service (DoS) attacks. 

Cyber threats can sneak into your system in many ways, whether it’s a phishing email, malware, or spyware. To manage cyber risks for your business, you need a plan of precaution and protection. 

6 Ways to Protect Your Workplace From Online Threats

Here are a few easy solutions to strengthen your business’s cybersecurity.

1. Find Weak Spots

The first step to mitigating cyber threats is to conduct a cybersecurity risk assessment. This assessment will help you determine where the weak spots in your network security are, so you can fix them before someone exploits them.

These assessments will help your IT team understand what parts of the system need improvement and what to prioritize. A cybersecurity risk assessment will also often clue you into the security of other vendors you work with and if your information is at risk on their networks. 

It’s important to document and visualize the big picture of what valuable information you collect and hold that may be tempting to cyberterrorists. 

2. Implement Access Controls

The next step in protecting your business’ information, and information from customers, you need to establish appropriate network access controls. This means all employees should have specific and purposeful clearances for different programs. 

The higher an employee’s access, the more aware they should be of how to look out for cyber threats and how to avoid leaving gaps open for terrorists. Interns probably don’t need access to your entire database, but the CEO likely does need that access. 

Implementing appropriate access controls can take a while to figure out what access people need based on their position. But this step is well worth your time, as cyber threats are often let in by unsuspecting and negligent employees. 

3. Preventative Software

Security software like firewalls and antivirus programs are a must for protecting your network. These security programs are your number one defense against cybercriminals. The program designs specifically block hackers like this, knowing the holes they try to exploit and wiggle through. 

Antivirus programs actively search your software routinely to catch any viruses or intruders that don’t belong. And firewalls act as a solid buffer between your network and the rest of the internet. 

4. Monitor Patches

Companies often release patches as they work to update and improve their software. When these patches run, it creates new vulnerabilities in your network. Cybercriminals are usually perched in wait for these patches to launch so they can take advantage of the gaps that haven’t been filled yet.

The best way to stay ahead of this is to monitor when and how often your software providers release patches. Create a schedule to assess new patches and remedy vulnerabilities as soon as they occur. 

5. Monitor Network Traffic

The best way to protect your network is to babysit it. There are programs you can install that will give you a full picture of your cyber ecosystem. Checking these kinds of programs, and designating your IT department to do so often, is a proactive step in mitigating cyber risks. 

6. Prepare for Attacks

Preparing for attacks involves all of the above steps in conjunction with a business continuity plan. Having a great business continuity plan can help provide a clear picture of the costs linked to IT failures or business interruption. Sometimes such attacks and threats cause panic, but having a plan in place can help the business continue to run smoothly, even when the worst happens. 

The worst thing you can do is be ignorant or in denial about the threat of cyber attacks in your workplace. Preparation is the key to mitigating these kinds of risks, as once the damage is done, it usually cannot be undone. 

Bottom Line

Don’t wait for something terrible to happen to beef up your cybersecurity. Take preventative measures to ensure your business never has to suffer a cyber attack that leaves you distraught and stressed. 

Today’s cyber world is a bit of a minefield; the steps above are your best form of armor against cybercriminals. 

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-90908CVSS 9.3
    A vulnerability in the GenericAdminAuthenticator component of Azul Payara Server and Azul Payara Micro allows a remote, unauthenticated...
    📅 Updated: Nov 12, 2026
  • CVE-2026-110003CVSS 9.3
    A vulnerability in the administration REST interface of Azul Payara allows a remote, unauthenticated attacker to bypass secure-admin...
    📅 Updated: Nov 12, 2026
  • CVE-2026-8333CVSS 9.4
    A stored cross-site scripting vulnerability in Microchip the TimePictra platform could allow an authenticated, low-privileged attacker to store...
    📅 Updated: Nov 12, 2026
  • CVE-2026-12591CVSS 9.9
    Zohocorp ManageEngine M365 Manager Plus versions below 4818 is affected by an authenticated technician may exploit insufficient permission validation in the delegated administration...
    📅 Updated: Nov 12, 2026
  • CVE-2026-12507CVSS 9.1
    Zohocorp ManageEngine AssetExplorer versions below 7860, ServiceDesk Plus versions below 15290, ServiceDesk Plus MSP versions below 15150, and...
    📅 Updated: Nov 12, 2026
  • CVE-2026-107935CVSS 9.3
    A path traversal vulnerability was found in gvproxy, the network forwarder provided by the gvisor-tap-vsock package. The unauthenticated...
    📅 Updated: Nov 12, 2026
  • CVE-2026-125883CVSS 9.3
    Improper restriction of XML external entity reference vulnerability in N-able N-central allows XML Schema Poisoning. This issue affects...
    📅 Updated: Nov 12, 2026
  • CVE-2026-76954CVSS 9.8
    An improper neutralization of special elements used in an SQL command vulnerability in the Auth API in Synology...
    📅 Updated: Nov 12, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.