Skip to content
October 22, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Technique
  • 3 Ways VPNs Protect Your Privacy Online
  • Technique

3 Ways VPNs Protect Your Privacy Online

Do Son November 30, 2020 3 minutes read
tech-vpn

While cybercriminals and hacker gangs like REvil and Maze are becoming everyday concerns, you are far from powerless when it comes to safely navigating the Internet.

One thing you can do is connect to a Virtual Private Network (VPN), where you can browse the Internet while protected by a secure server. It’s a great way to keep your data and your identity safe from computer viruses, not to mention those who create them. Read on to find out why.

VPNs Make Your Data Basically Impenetrable 

VPNs offer you a secure Internet connection by encrypting the data you send out, like clicking on a website icon, as well as the data you receive, such as a handful of fresh emails in your inbox. To put it plainly, they scramble your data into gobbledygook before darting it off to the appropriate recipient.

If you have any lingering doubts about your VPN’s security capabilities, pair it with an antivirus program with real-time endpoint protection that can remove malicious software before it has a chance to act.

Leading lights in the antivirus industry like Malwarebytes offer their customers a VPN with 256-bit encryption, which is about as heavy-duty as cybersecurity can get. In other words, a hacker would have to decipher a 256-character password to decrypt your data in the few seconds it takes to arrive at its destination: there’s no such thing as 100 percent safety on the Internet, but the likelihood of this happening is about as close to none as modern technology allows.

VPNs Turn You Into an Online Globetrotter 

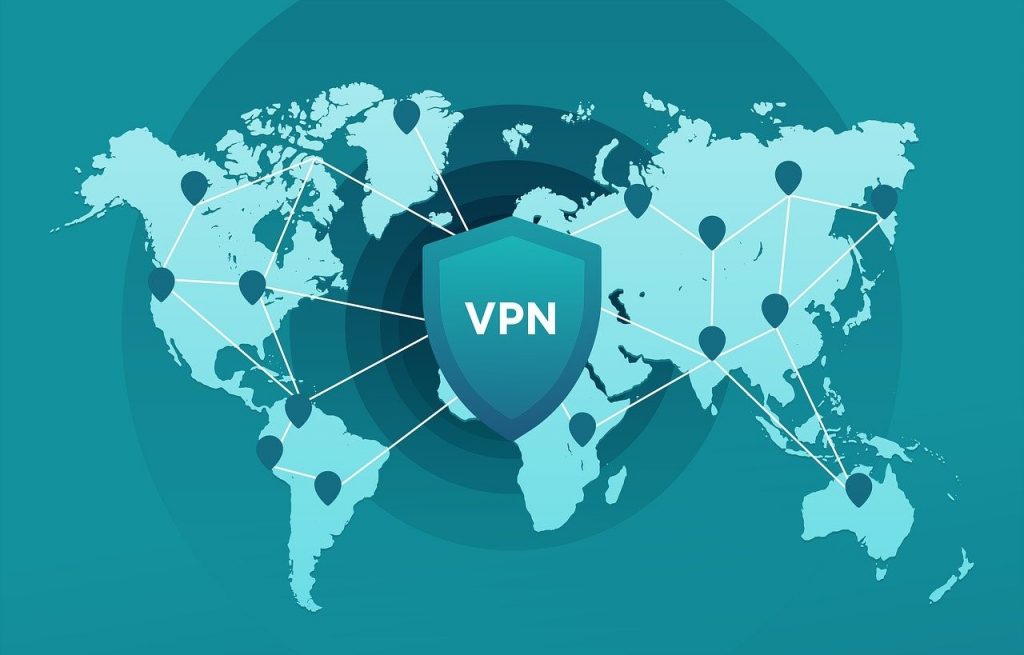
VPNs often have servers in multiple countries. If you log in to one, your endpoint will appear to be coming online from wherever it’s located, even if it’s halfway across the world.

That means that you can keep cybercriminals guessing as to your connection’s exact location. This is a go-to feature if you’re conducting an important business deal or downloading sensitive information and need your privacy ensured.

If your VPN offers it, you should also take advantage of any feature that lets you periodically change servers for added protection. That way, you’ll get hackers off your trail by establishing Internet connections all over the globe.

VPNs Shroud Your Browsing History in Secrecy 

When you go online through a VPN, you enjoy the benefits of navigating under a virtual Internet Protocol (IP) address. An IP address is simply a numerical label that identifies a computer connected to the Internet. A virtual IP address is an IP address that isn’t actually attached to any physical device.

In this way, websites and adware programs won’t be able to track your browsing history and slow your system down with targeted ads. Under the disguise of a virtual IP address, your VPN helps to defend your right to lead a safe and secure online life.

It’s clear that browsing the Internet using the right VPN is an essential step toward reliable cybersecurity. Once you realize you don’t have to worry about your information falling into the wrong hands, you’ll never want to surf the web any other way.

Tags: Protect Your Privacy Online

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2017-20287CVSS 8.7
    Javo Spot theme for WordPress before 3.0.0 contains a path traversal vulnerability that allows unauthenticated attackers to read...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2017-20288CVSS 5.1
    QCubed 2.2.0 through 3.1.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject scripts through...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2017-20289CVSS 7.7
    Broadstreet Ad Widget plugin for WordPress 2.2.0 before 2.12.0 contains a local file inclusion vulnerability that allows authenticated...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2026-109619CVSS 9.2
    PHP has various global state that temporarily points into request memory. In some scenarios, global state may not...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-109618CVSS 9.2
    PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request....
    Admin intel📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-115324CVSS 9.2
    mem0 0.1.117 before 1.0.8 contains an sql injection vulnerability in mem0/vector_stores/databricks.py that allows attackers to inject SQL by...
    📅 Updated: Oct 22, 2026
  • CVE-2021-48016CVSS 9.3
    DedeCMS through 5.8.1-beta contains a PHP code injection vulnerability in ShowMsg() where the HTTP Referer header is written...
    📅 Updated: Oct 22, 2026
  • CVE-2021-48014CVSS 9.3
    FineReport 9.0 contains a path traversal vulnerability in the /WebReport/ReportServer design_save_svg operation that allows unauthenticated attackers to write...
    📅 Updated: Oct 22, 2026
  • CVE-2026-112327CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in TMS Amelia ameliabooking allows...
    📅 Updated: Oct 22, 2026
  • CVE-2026-112241CVSS 9.8
    Authentication Bypass by Spoofing vulnerability in Brainstorm Force SureCart surecart allows Authentication Abuse.This issue affects SureCart: from n/a...
    📅 Updated: Oct 22, 2026
  • CVE-2026-15143CVSS 9.3
    A flaw was found in the file_type content detector of guardrails-detectors. This vulnerability allows a remote attacker to...
    📅 Updated: Oct 22, 2026
  • CVE-2026-114220CVSS 9.3
    NT OneAPP developed by NewType Infortech has an Improper Certificate Validation vulnerability. Unauthenticated network-adjacent attackers can perform a...
    📅 Updated: Oct 22, 2026
  • CVE-2026-114219CVSS 9.1
    NT OneAPP developed by NewType Infortech has a Hard-coded Credentials vulnerability. Unauthenticated remote attackers can obtain the hard-coded...
    📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.