Skip to content
November 12, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
  • Home
  • Technique
  • 5 Best Welcome Email Examples That seals Trust With Your Subscribers
  • Technique

5 Best Welcome Email Examples That seals Trust With Your Subscribers

Do Son November 29, 2019 5 minutes read
Email Examples

The importance of welcome emails is undeniably a vibe that keeps getting stronger each minute. According to a survey by Epsilon’s Email Institute and Multichannel Merchant, welcome emails carry the highest opening (60 percent) rate above any other emails sent out to your subscribers. They are, as most would agree, short and to the point and a potent marketing tool, when used right. More than 65 percent of welcome emails usually range in between 50-150 words. It’s never contradictory to the length of the email rendering it non-effective. In fact, emails that are being sent out as a part of the sign-up process can work to boost the retention rate by as much as 71 percent. Impressive, eh? In this post, we shall take a look at 5 best welcome email examples from brands that are doing it right to stay at the top of their game. 

Where communication is the key 
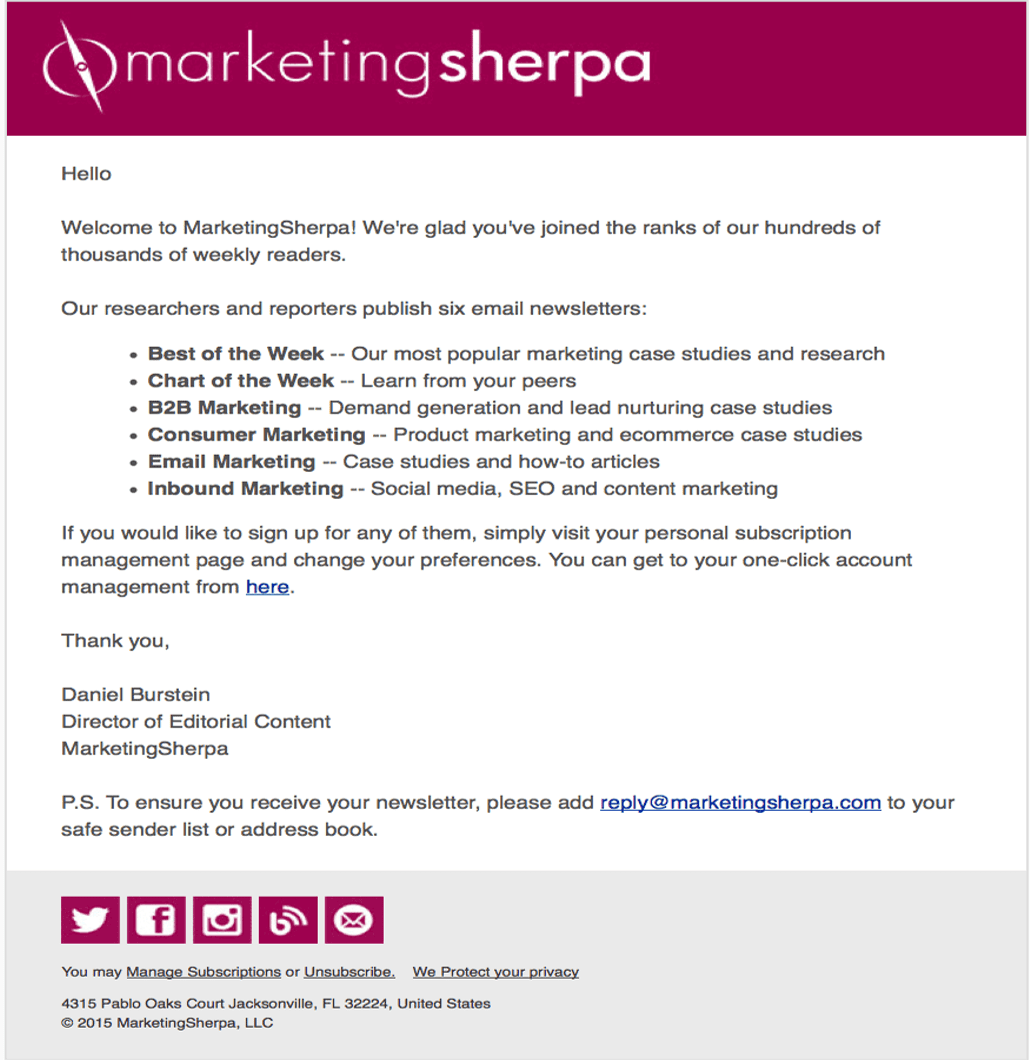
Users, when they bump on to a site and like, they usually tick the box to agree to receive newsletters and leave their email address. However, it still becomes crucial to remind all users to choose their preferred mode of communication in the very first email that you sent. In this example, MarketingSherpa does a brilliant job in establishing fist base communication with its subscribers by listing out the number of newsletters it’s going to send. They also include an option to unsubscribe right at the bottom of the list. Alternately, the email address is also present in case you want to whitelist it, followed by the essential social media icons to connect with the company. This one’s probably one of the finest examples of best welcome emails, where one explores the gamut of communication channels and give freedom to subscribers to choose their preferred mode.

 Personalization goes a long way 
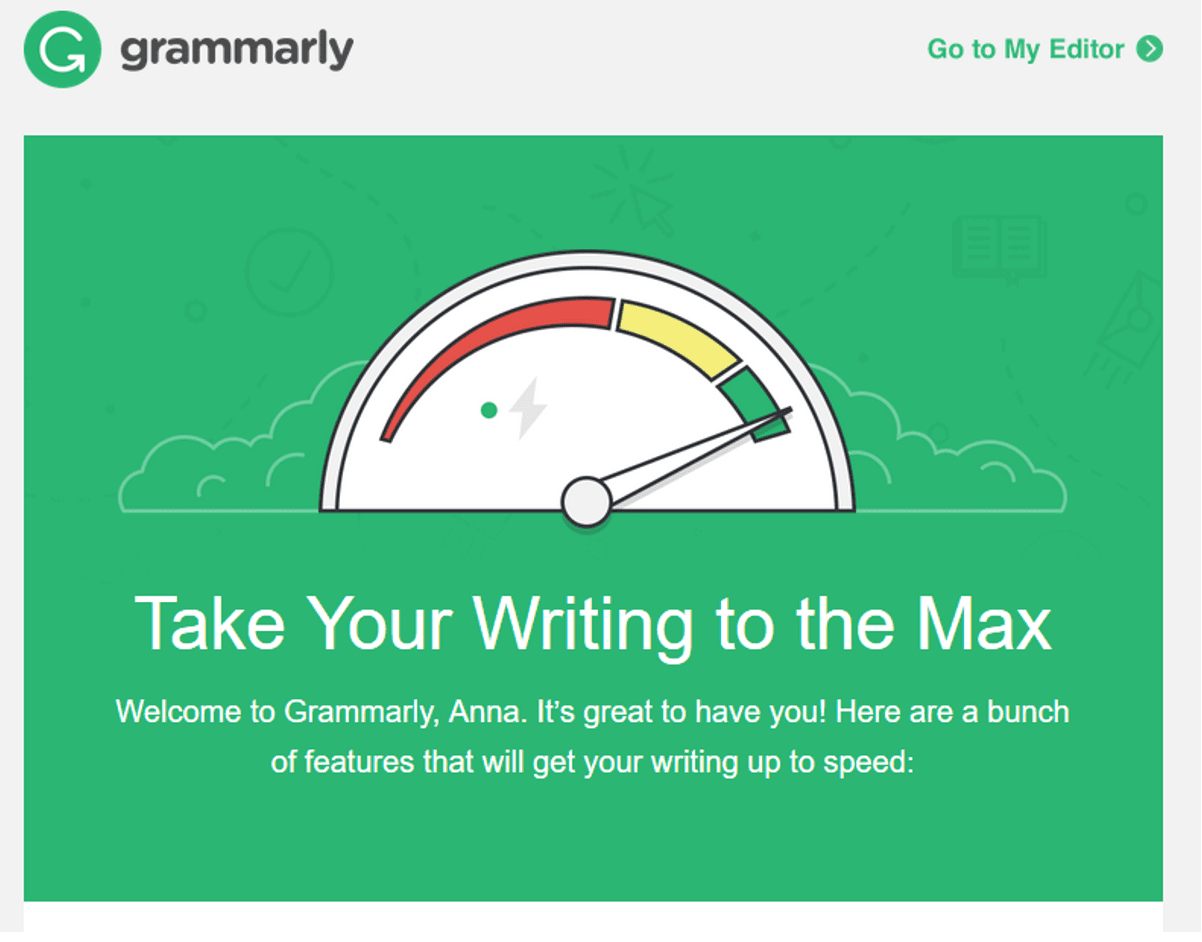
To quote Dale Carnegie, the name of a person is the sweetest and lovable word in the language to the individual himself. Now, there are a whole lot of marketing ploys around personalization and welcome emails are certainly no different. It all makes sense as the person subscribing to your newsletters leaves his first and last name. So, it is befitting to start your marketing by referring to the person by his name. Alongside this, one can also use any other information that the user might have provided while signing up. For instance, their residential or business address. Use the same to point and guide them towards their nearest location for your outlet, if you cater offline. Additionally, it would be a real boost if you plan the marketing campaign through newsletters using the person’s native tongue. When language isn’t a barrier, it doubles up your chance of success. It’s proven. Take a cue from Grammarly, the famous grammar and spell checker tool that’s being used extensively. In their newsletter, they resort to greeting their users by their first name. Sure, it’s nothing special but the personalization factor sure is a kick-starter for the relationship between the individual and the brand.

Always find ways to amaze them 

To leave an impact with your welcome email, you need to put your best foot forward with your graphics. Your artwork should not only be rich in content but should always have something simple yet unique to amaze customers. Give them a reason to read that welcome email a second time. Go crazy with animations, videos, gifs, and whatnot. Use content that’s funny and user-friendly. Take a look at how Brooklinen, a trusted name in bedding retail does it. An animated picture that reads just “You’re In!” A perfect example of how simply you can build trust with fewer words and powerful graphics.

Setting your purpose right 
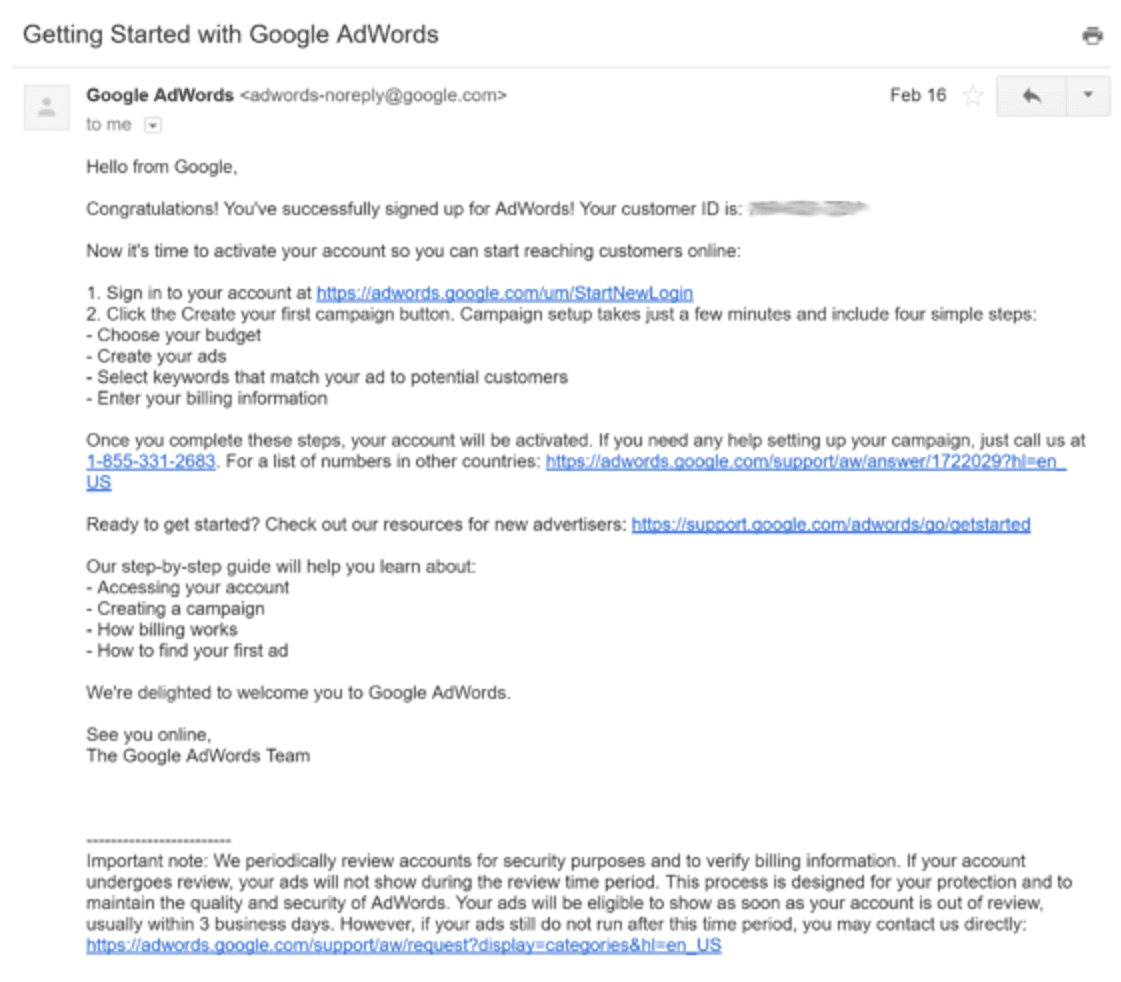
If you are a digital marketing consultant yourself, you shall know that Google Adwords follows a routine of sending out two separate welcome emails. Why so? Simple. Because they serve two distinct purposes. The first one is a wholesome offering, usually non-branded and an effort to get ground with the newest subscribers. The second one bears a sharp contrast to the former, carry proper branding to grab all eyeballs. Besides, it includes a single CTA that is repetitive in the shape of a task that Google wants you complete as the last step to your sign up process and get your account ready.

Time is Money. Make it count 

The very first welcome email for a new subscriber is perhaps the best time to include a gift or a special discount. Not only does it gives the customer an impression of a reward but it also ushers a positive belief towards your brand. Furthermore, the limited time offer urges one to take prompt action and get down to shopping or browsing on an immediate note. Ralph Lauren cleverly builds around the first time gift or offer idea with a limited time period tag for all new subscribers. They make it a point in their welcome email to remind all new customers as the very first recipients of all the latest offerings and news by the brand along with a 10 percent discount on their next purchase. It is immediately followed by the SHOP NOW button that itself acts as a CTA for one and all.

Bottom Line

There’s no ignoring the importance of welcome emails. Because they work all the time. It doesn’t matter if it’s an introductory message or a welcome back for a returning customer. You will need to set up one clear and positive welcome email to bring a difference to your business.

Tags: Email Examples

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123039CVSS 7.8
    The Gaia OS DynamicCLI daemon runs as root and listens on a world-writable local socket (/tmp/dynamic_socket) without authenticating...
    Admin intel📅 Updated: Nov 12, 2026
  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-17131CVSS 9.3
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to obtain sensitive information due to server-side...
    📅 Updated: Nov 12, 2026
  • CVE-2026-17344CVSS 9.3
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to obtain sensitive information due to server-side...
    📅 Updated: Nov 12, 2026
  • CVE-2026-63857CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: net: airoha: Do not read uninitialized fragment address...
    📅 Updated: Nov 12, 2026
  • CVE-2026-121355CVSS 9.1
    Adobe Connect is affected by an Incorrect Authorization vulnerability that could result in privilege escalation. An attacker could...
    📅 Updated: Nov 12, 2026
  • CVE-2026-120869CVSS 9.4
    An unauthenticated attacker can bypass authentication controls to access restricted resources on the appliance Pre-conditions: Access to Citrix...
    📅 Updated: Nov 12, 2026
  • CVE-2026-120864CVSS 9.3
    Memory overflow in ICA proxy can lead to unpredictable or erroneous behavior or Denial of Service. Pre-conditions: The...
    📅 Updated: Nov 12, 2026
  • CVE-2026-107412CVSS 9.5
    Multiple Memory overflow vulnerabilities can lead to unpredictable or erroneous behavior and Denial of Service Pre-conditions: NetScaler is...
    📅 Updated: Nov 12, 2026
  • CVE-2026-107415CVSS 9.3
    Memory overflow in Email OTP authentication can lead to unpredictable or erroneous behavior or Denial of Service. Pre-conditions:...
    📅 Updated: Nov 12, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.