 Do Son
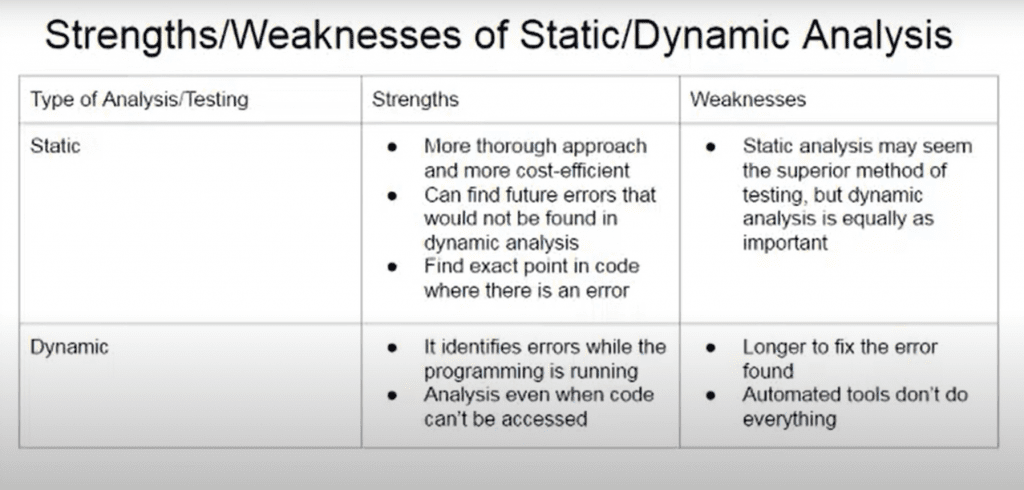
Source: Noah Cole (Youtube video)
Penetration Test or pentest is a popular security practice. Researchers say that 95% of cyberattacks are due to human negligence. Therefore, conducting a penetration test is vital. However, deciding which penetration testing service to get is quite difficult. Moreover, there are so many VAPT (Vulnerability Assessment and Penetration Test) services available in India. If you’re confused as to which penetration testing service to opt for, worry not, this post will give you some pointers.
What is Penetration Testing?
A penetration test is a security exercise in which involves a cybersecurity expert or software trying to hack into the website. By doing so, they identify all the possible exploitable security points in a web application.
Why Conduct Penetration Tests?
A security breach causes a lot of ramifications. Loss or exposure of data can ruin the reputation of your business. A penetration test can help prevent this to a large extent. One other thing to consider is that hackers often change their techniques. It may so happen that the existing security system may fail to detect the newer types of attack. Therefore, it is important to conduct a penetration test.
How Does Penetration Testing Work?
A penetration test typically has four stages:
1. Planning
This stage includes laying the roadmap for the penetration tests. Deciding on the tests, methods, and techniques. Finalizing on the scope among several other things.
2. Scanning or Reconnaissance
This step includes studying the target website, its assets, access points, security system, etc. It also includes identifying common vulnerabilities and risks through automated tools and simple attacks. This is to assess risks and also to assess how efficient the existing security protocols are.
3. Penetration (aka Exploitation)
Security professionals launch targeted cyber-attacks like SQLi, XSS, and CSRF during this critical phase. Consequently, these simulated exploits allow teams to breach the website’s defenses. Next, the testers attempt to maintain persistence within the system. This active testing matches the core principles of Adversarial Exposure Validation by identifying real-world security gaps. Furthermore, the evaluation measures the exact blast radius that a specific vulnerability might cause. Therefore, organizations can accurately gauge potential data loss and determine how deeply an attacker can penetrate the architecture.
4. Analysis
The data obtained from all the previous stages are then analyzed by experts. After this, all the possible vulnerabilities are prioritized and listed along with its remediation steps in an easy-to-understand report.
When searching for a penetration testing service, make sure that their methodologies roughly follow these steps. Apart from these, there are some other things you need to look for. Let’s have a look at what they are.
What to Look For in a Penetration Testing Service?
1. Transparency And Communication
It is very important for you to know every tiny detail involving your company’s security. This is only possible if the testing service is transparent with you. You should also be aware of the tests that they conduct beforehand. This way, you will know whether their penetration test caters to your needs or doesn’t align with your company’s needs. Also, human support and detailed feedback are of great importance.
2. Patch-up Assistance
Identifying vulnerabilities only solves half your problem. All the risks and vulnerabilities spotted have to be resolved. Fortunately, a lot of penetration testing services lists fixes for the vulnerabilities that they identify. Some like Astra Security go the extra mile by assisting their clients one-on-one in fixing those vulnerabilities and even doing a re-scan afterwards.
3. Procedure
The penetration testing service you opt for must follow security standards from all over the globe. For example, OWASP, SANS, CERT, PCI, ISO27001, and many more. Some of these security standards are mandatory across various sectors and industries. Therefore, not following standard procedures and protocols is a big red flag to look out for.
4. Static And Dynamic Analysis of Code

Static analysis is basically identifying vulnerabilities in the code before compiling. On the other hand, dynamic analysis involves identifying vulnerabilities in the code during run-time. Dynamic analysis is more effective as compared to static as it is real-time. Both these methods are important, so make sure the service you opt for includes them.
5. Reputation And Customer Reviews
Make sure to research the company that you’re entrusting with the penetration test. By allowing them to hack your website, you are trusting them with a lot of sensitive information. Therefore, you need to work with a trustworthy company. You can look up customer reviews about the company. Also, make sure to check which all companies this penetration testing service has worked with.
VAPT in India
There are so many VAPT tests available in India. Some of your best options are:
- Astra Security
Astra Security is one of the best VAPT service providers not only in India but all over the world as well. They provide in-depth code analysis to secure your website. Moreover, they also help you fix the bugs and patch up all the vulnerabilities they find. Also, they have 24/7 human support that will guide you through the process. Lastly, they provide a VAPT certificate and interactive video proof of concept (PoC).
- TestBytes
TestBytes is a development firm based in Pune. They are experts in penetration testing and have a large team and high-end testing laboratory dedicated to the cause. Also, they specialize in developing reusable automation frameworks and so much more.
- eSec Forte
eSec Forte is a CMMI Level-3 ISO 9001-2008, 27001-2013 certified company based in Delhi. They involve their clients through the entire process resulting in higher customer satisfaction.
Conclusion
Penetration tests are very important to enhance the security of your website. It helps you identify all the vulnerabilities in your website. However, it is also important to choose the right company that tailors to your needs.
We hope this article helps you in deciding the penetration testing service most suitable for you!