Skip to content
October 19, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Linux
  • Aryalinux 1.0 releases: GNU/Linux Operating System
  • Linux

Aryalinux 1.0 releases: GNU/Linux Operating System

Do Son July 5, 2018 3 minutes read
Aryalinux
Add Daily CyberSecurity as a preferred source on Google

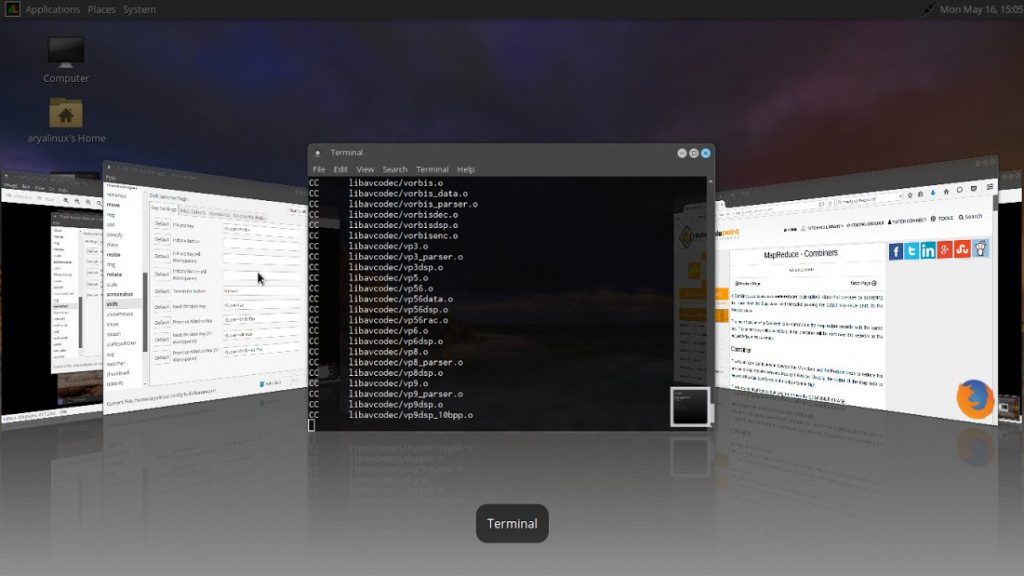
Aryalinux is a GNU/Linux Operating System built from the source code of the various component packages it consists of, unlike most Linux distributions which are built by remastering or modifying some other distribution. Apart from being the distro that AryaLinux is, it’s also a platform that one can use to build a complete distribution from source code. AryaLinux used bash scripts called build scripts to build everything from scratch and uses a dependency resolution and script execution framework called alps to build the whole system from the ground up. What started off as a project to take BLFS to the next level and build a full-fledged distro out of LFS/BLFS is now a unique distro that you can use to build your own distro.

Features

  • Built from scratch. AryaLinux is not remastered or spun or forked out of any other Linux project
  • Source-based Package Manager – ALPS. Although alps is not strictly speaking a package manager it behaves like one and makes the whole process of building complete desktop environments from source a cake walk
  • The live media supports multiple languages
  • XFCE, Mate, KDE and LXQt supported. The XFCE, KDE and LXQT spins development is in progress and would be released in the next few weeks
  • Most packages in AryaLinux are near latest(except few that are not updated either for backward compatibility or stability in mind)
  • Beyond BLFS AryaLinux provides the AryaLinux installer so that you can provide an installer with your Aryalinux based live media
  • 32-bit and 64-bit

AryaLinux 1.0 was released.

Changelog

  • Latest stable kernel as of July 02, 2018 – linux-4.17.3 ships with this release.
  • Upgrade in various packages:
    1. gcc
    2. glibc
    3. vlc
    4. libreoffice
    5. Gnome desktop
    6. Firefox
    7. Transmission
    8. Rhythmbox
    9. Chromium
  • Support for flatpak applications. You can install flatpak applications out of the box with AryaLinux.
  • A lot of changes in the base system build scripts:
    1. No more initrd using dracut
    2. New options in the build script – to create ISO and to install bootloader
  • ALPS undergoes a complete rewrite. ALPS is now based on python 3.x. More options in alps to support flexible package dependency specification while installing – helpful for power users.
  • The default browser that ships with this release is Chromium. Though firefox can also be installed using alps but the default browser is Chromium.
  • Fixes in the build scripts of a lot of applications to support gcc8
  • Based on the latest SVN version of LFS/BLFS books
  • Beta support for update and upgrade feature through ALPS
  • Fixed the Installer
  • New set of wallpapers and themes specifically to suit the Gnome desktop environment
  • Deprecated few scrips like the gstreamer-0.x version libraries
  • Fixed boot issues assocaiated with EFI booting
  • Codebase for AryaLinux moves over to Bitbucket. While the older versions of AryaLinux would still be building from the github codebase, they would not undergo any further updates.
  • With this release we are also providing partially built tarballs like the tarball of the base-system and tarball of the base system with x-server so that anyone can build a more customized system to be used either as a server or as a desktop.

Download

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Aryalinux

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 19, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 19, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 19, 2026
  • CVE-2026-111862CVSS 9.8
    Rank Math SEO PRO for WordPress is affected by a supply-chain compromise in a subset of version 3.0.123...
    Admin intel📅 Updated: Oct 17, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    Watchtower Verified📅 Updated: Oct 17, 2026
  • CVE-2025-61624CVSS 6.0
    An Improper Limitation of a Pathname to a Restricted Directory (\'Path Traversal\') [CWE-22] vulnerability in Fortinet FortiOS 7.6.0...
    CISA KEV📅 Added to KEV: Oct 16, 2026
  • CVE-2026-102764CVSS 9.3
    The vulnerability exists within internal components of BeyondTrust’s Remote Support product. The components did not adequately validate the...
    CISA KEV📅 Added to KEV: Oct 16, 2026
  • CVE-2026-106931CVSS 8.5
    SiteGuard Server Edition contains an OS command injection vulnerability, which may allow an attacker to execute arbitrary OS...
    Admin intel📅 Updated: Oct 15, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-103091CVSS 9.3
    Missing Authorization (CWE-862) and Initialization of a Resource with an Insecure Default (CWE-1188) in the MCP proxy (HandleStreamPassThrough...
    📅 Updated: Oct 19, 2026
  • CVE-2026-102503CVSS 9.3
    Missing Authentication for Critical Function (CWE-306) and Missing Authorization (CWE-862) in the /libp2p-http ingress server (StartIngressServer in cmd/sam-node/node.go)...
    📅 Updated: Oct 19, 2026
  • CVE-2026-108983CVSS 9.8
    A vulnerability is in Web Server default connection ports under the process name GeoWebServer.exe .
    📅 Updated: Oct 19, 2026
  • CVE-2025-39496CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in WBW WooBeWoo Product Filter...
    📅 Updated: Oct 18, 2026
  • CVE-2025-48100CVSS 9.1
    Improper Control of Generation of Code ('Code Injection') vulnerability in extremeidea bidorbuy Store Integrator bidorbuystoreintegrator allows Remote Code...
    📅 Updated: Oct 18, 2026
  • CVE-2025-49387CVSS 10.0
    Unrestricted Upload of File with Dangerous Type vulnerability in add-ons.org Drag and Drop File Upload for Elementor Forms...
    📅 Updated: Oct 18, 2026
  • CVE-2025-49388CVSS 9.8
    Incorrect Privilege Assignment vulnerability in kamleshyadav Miraculous Core Plugin miraculouscore allows Privilege Escalation.This issue affects Miraculous Core Plugin:...
    📅 Updated: Oct 18, 2026
  • CVE-2025-52761CVSS 9.8
    Deserialization of Untrusted Data vulnerability in manfcarlo WP Funnel Manager wp-funnel-manager allows Object Injection.This issue affects WP Funnel...
    📅 Updated: Oct 18, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.