 Do Son
As generative AI creation tools become ubiquitous, streaming music platforms are increasingly inundated with a deluge of...
Do Son
Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
A curious hardware glitch has exposed a case of AliExpress audio fingerprinting running quietly inside your browser....
TikTok and its parent corporation, ByteDance, formally finalized a monumental settlement agreement with the United States Department...
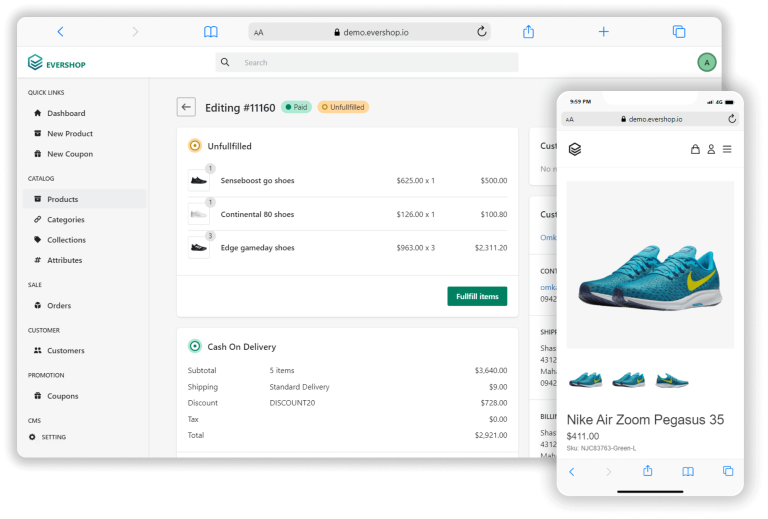
A critical flaw in the EverShop software allows complete unauthenticated account takeover attacks. Tracked as CVE-2026-72843, this...
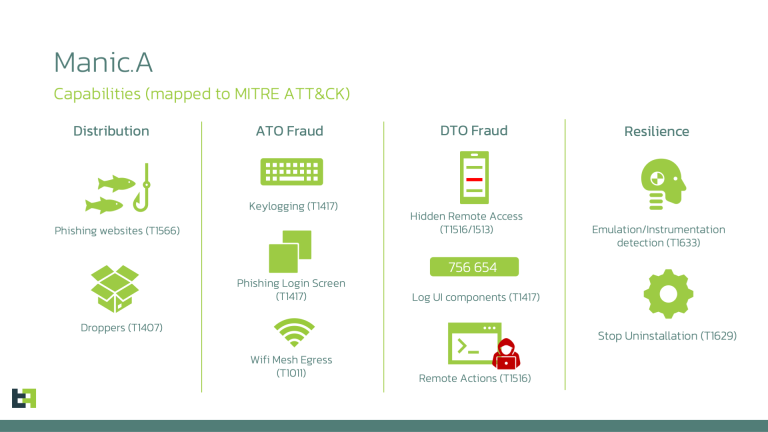
At a glance Factor Details Malware Family Manic Threat Actor Unknown organized criminal groups (Suspected) Targets Users...
TL;DR CVE-2026-77806 is a CVSS 9.8 unauthenticated RCE in the SPIP CMS. It affects all versions before...
TL;DR VMware disclosed four Spring vulnerabilities on August 20, 2026. All rate as HIGH severity. One hits...
TL;DR CVE-2026-75501 is a missing authentication flaw in the Calix GS7 XGS GS5239XG router. Its UPnP service...
TL;DR CVE-2026-19598 is a CVSS 9.8 privilege escalation flaw in the Pods WordPress plugin. It lets unauthenticated...
TL;DR Apache CloudStack shipped releases 4.20.3.1 and 4.22.1.1. They fix 20 CVEs across the platform. The most...
TL;DR IBM patched a large batch of IBM AIX vulnerabilities on August 15, 2026. Many allow remote...
TL;DR A uutils coreutils vulnerability affects the stdbuf tool in the Rust rewrite of GNU coreutils. By...
TL;DR CERT/CC disclosed five RDK-B WebUI vulnerabilities on August 19, 2026. The worst flaw lets a remote,...
At a glance Factor Details Organization Multiple enterprises, AI developers, and cloud users globally Data Exposed 64,024...
TL;DR Keycloak 26.7.2 fixes five flaws, released on August 19, 2026. The most severe, CVE-2026-18963, allows a...
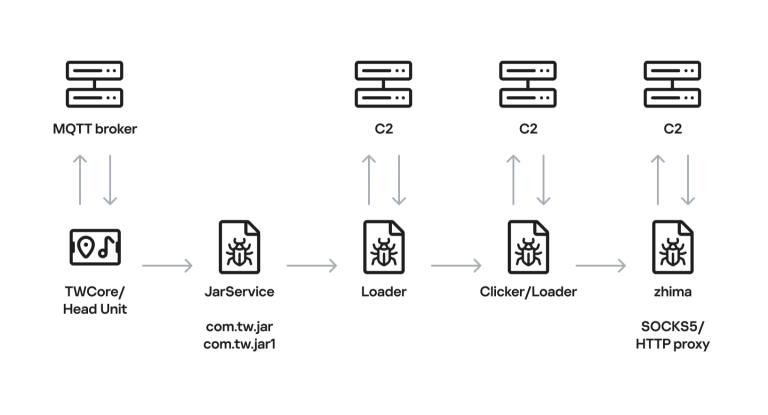
At a glance Factor Details Malware Family JarService dropper and zhima proxy module Threat Actor MoYu Group...
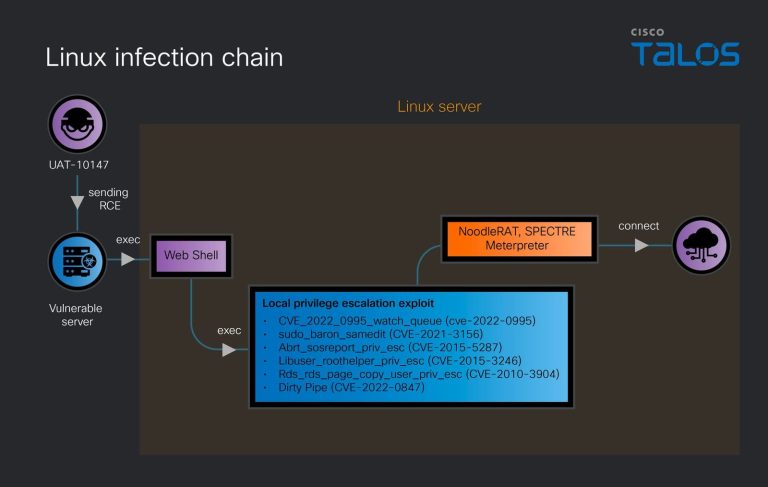
At a glance Factor Details Actor UAT-10147 (Suspected Chinese-speaking cybercrime threat group) Activity Type Search engine optimization...
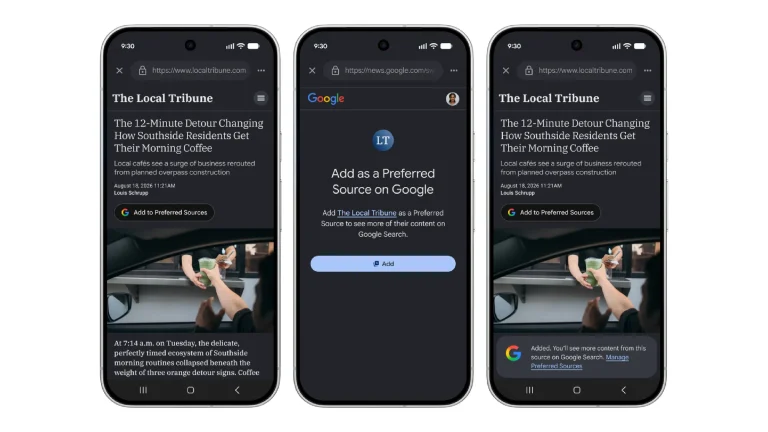
To empower users to effortlessly support and follow their cherished news publishers and websites, Google recently unveiled...
TL;DR Red Hat disclosed three high-severity flaws that enable privilege escalation. The worst, CVE-2026-67567 (CVSS 9.9), hits...
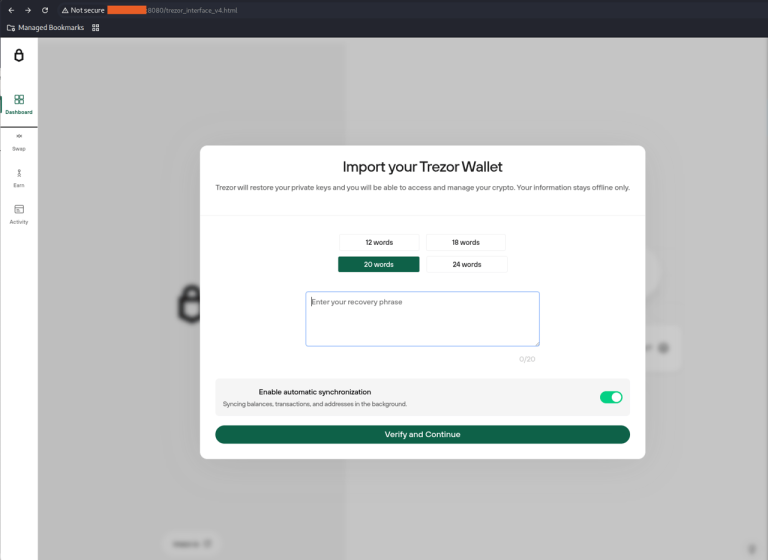
At a glance Actor Unnamed crypto fraud operator (single host) Activity type Phishing, vishing, fake wallet malware,...
TL;DR CVE-2026-32475 is a CVSS 9.8 unauthenticated arbitrary file upload flaw in Elementor Pro. It affects an...