 Do Son
TL;DR CVE-2026-19598 is a CVSS 9.8 privilege escalation flaw in the Pods WordPress plugin. It lets unauthenticated...
News
TL;DR Apache CloudStack shipped releases 4.20.3.1 and 4.22.1.1. They fix 20 CVEs across the platform. The most...
TL;DR IBM patched a large batch of IBM AIX vulnerabilities on August 15, 2026. Many allow remote...
TL;DR A uutils coreutils vulnerability affects the stdbuf tool in the Rust rewrite of GNU coreutils. By...
TL;DR CERT/CC disclosed five RDK-B WebUI vulnerabilities on August 19, 2026. The worst flaw lets a remote,...
At a glance Factor Details Organization Multiple enterprises, AI developers, and cloud users globally Data Exposed 64,024...
TL;DR Keycloak 26.7.2 fixes five flaws, released on August 19, 2026. The most severe, CVE-2026-18963, allows a...
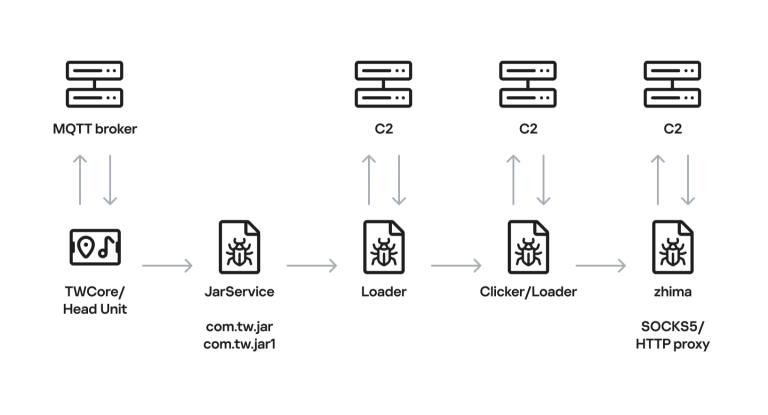
At a glance Factor Details Malware Family JarService dropper and zhima proxy module Threat Actor MoYu Group...
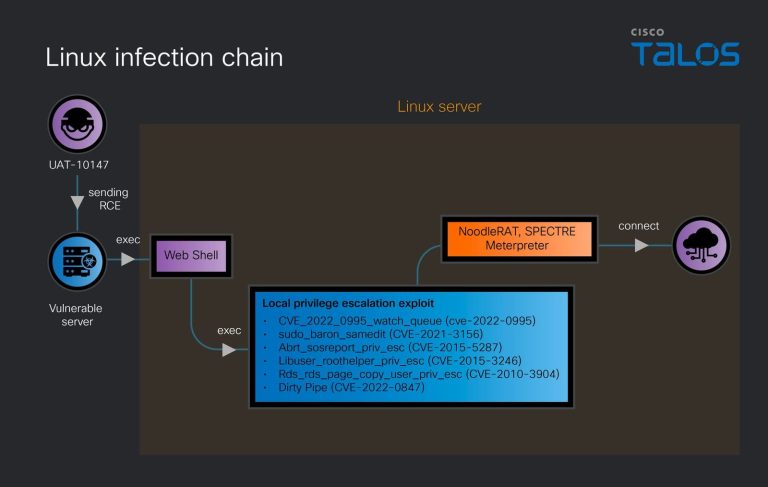
At a glance Factor Details Actor UAT-10147 (Suspected Chinese-speaking cybercrime threat group) Activity Type Search engine optimization...
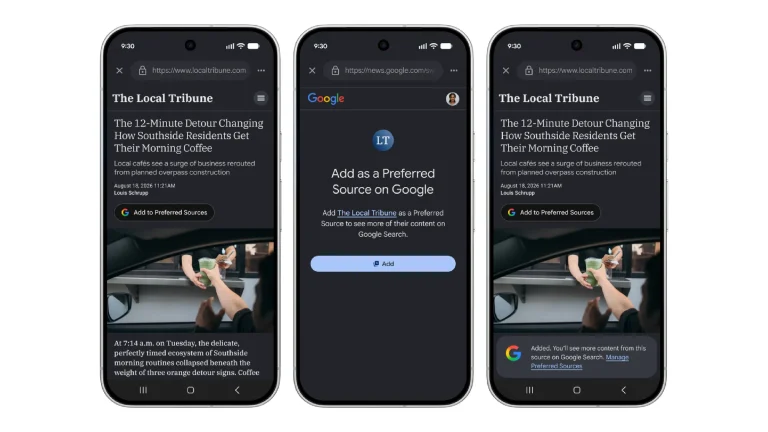
To empower users to effortlessly support and follow their cherished news publishers and websites, Google recently unveiled...
TL;DR Red Hat disclosed three high-severity flaws that enable privilege escalation. The worst, CVE-2026-67567 (CVSS 9.9), hits...
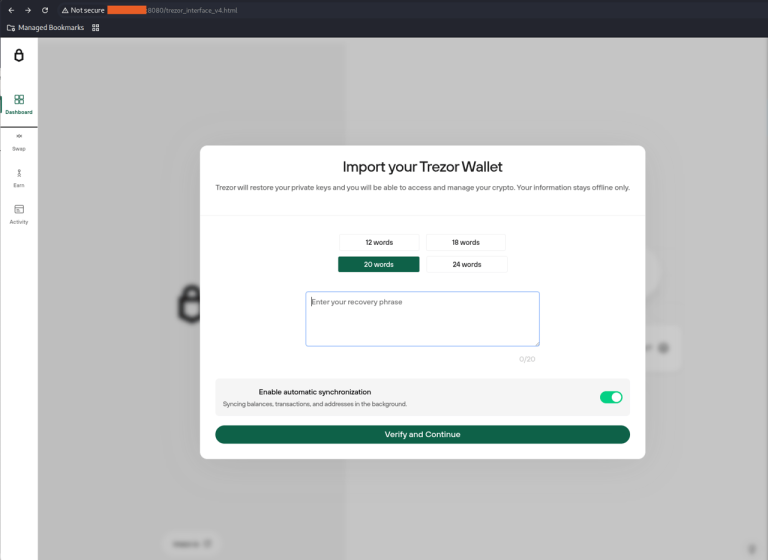
At a glance Actor Unnamed crypto fraud operator (single host) Activity type Phishing, vishing, fake wallet malware,...
TL;DR CVE-2026-32475 is a CVSS 9.8 unauthenticated arbitrary file upload flaw in Elementor Pro. It affects an...
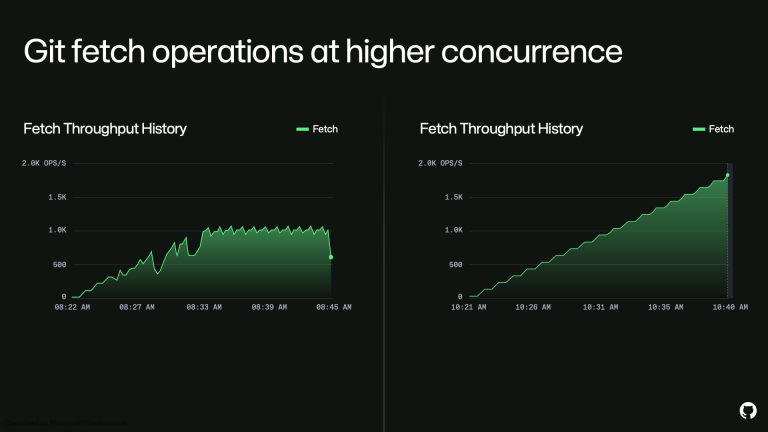
This week, Microsoft’s code hosting platform, GitHub, experienced a prolonged and widespread outage. This disruption significantly impacted...
At a glance Malware family Projextor (Electron-based) Threat actor Unknown; shared code base, no confirmed single operator...
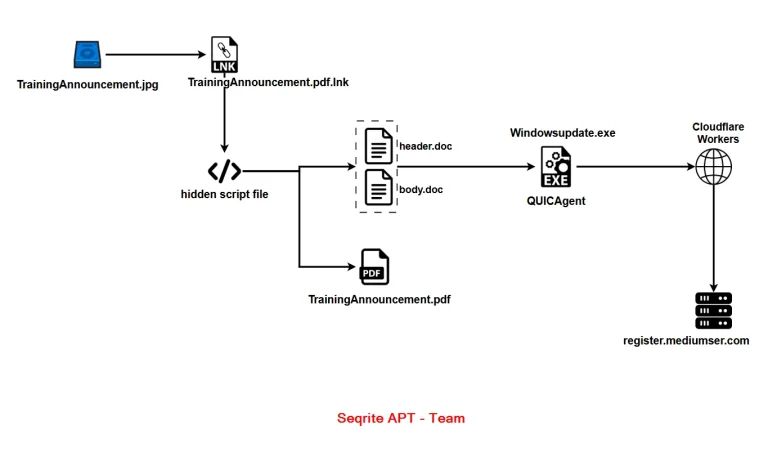
At a glance Actor or group Unnamed China-nexus actor (moderate confidence) Activity type Cyber espionage, custom Go...
Google continues to fortify the memory management framework across the Android ecosystem, as noted on the Android...
Following feedback from numerous gamers, Microsoft is officially investigating Windows 11 gaming issues that emerged after installing...
Japanese cloud computing and data center services provider Sakura Internet recently issued a security advisory disclosing that...
TL;DR CVE-2026-77647 is a CVSS 9.8 unauthenticated remote code execution flaw in the SPIP CMS. It affects...
TL;DR TP-Link patched three Omada gateway vulnerabilities. The most severe, CVE-2026-19586, is a pre-authentication OS command injection...
Update: Microsoft updated its safety alert on August 21, 2026. Initially, the report marked the bug as...