Skip to content
October 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Technique
  • Direct Attach Cable (DAC) Wiki
  • Technique

Direct Attach Cable (DAC) Wiki

Do Son June 10, 2022 3 minutes read
Img_2022_06_10_13_38_09

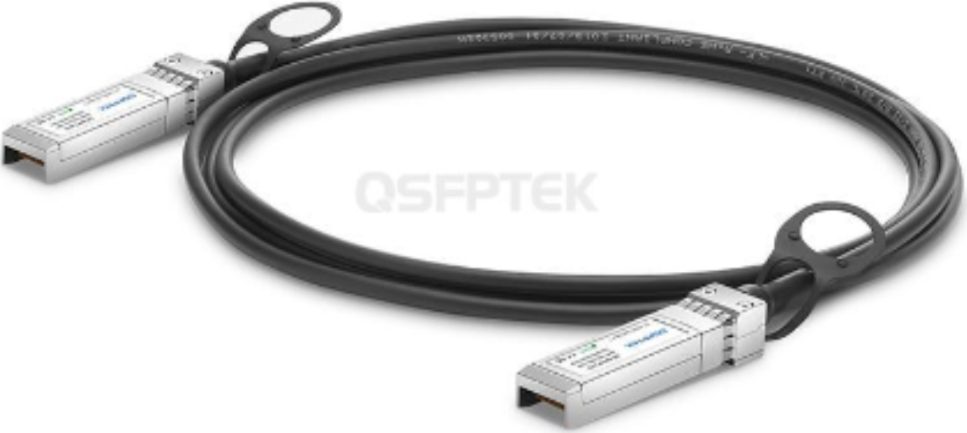
Direct Attach Cables (DACs) are usually fixed-length cable assemblies with fixed connectors at both ends, and non-replaceable ports, and the module head and copper cable cannot be separated. Widely used in storage area networks, data centers, and high-performance computing connectivity. DACs are more and more popular with users due to their significant advantages such as high-cost performance, high performance, high speed, high recombination, and low loss. The demand for it in the market is increasing.

Structure of DAC cable:

Using silver-plated conductors and foamed insulated core wires as materials, wire pair shielding and total shielding are adopted to form a high-speed cable. High-speed cables have excellent attenuation performance, low delay, and anti-interference, and can realize high-frequency broadband transmission. There are 30~24AWG specifications and various structures such as 2P, 4P, or 8P, which can be used in a variety of different applications.

Classification of DAC cable:

  1. 10G SFP+ to SFP+ DAC

The 10G SFP+ to SFP+ DAC uses passive twin axial cable assemblies and connects directly to SFP+ modules, featuring high density, low power, low cost, and low latency.

  1. 40G QSFP+ to QSFP+ DAC

The 40G QSFP+ to QSFP+ DAC provides a cost-effective way to establish 40G links between the internal rack and cross-rack QSFP+ switch ports, enabling access layer uplinks to core backbone links to 40G/100G, It is widely used in the high-speed backbone network, enterprise network switching and network storage due to its high speed and low latency.

  1. 40G QSFP+ to 4*SFP+ DAC

One end of the QSFP+ to 4*SFP+ DAC is a 40G QSFP+ interface, which meets the requirements of SFF-8436, and the other end is four 10G SFP+ interfaces, which meet the requirements of SFF-8432. To meet the requirements of the length of the end cable, a splitter is added in the middle of the MPO cable, so that one 40G optical signal can be divided into four 10G signals, which is the most economical and simple way to implement switch port to exchange.

  1. 25G SFP28 to SFP28 DAC

25G SFP28 to SFP28 DAC can provide customers with 25G high-bandwidth data interconnection capability, which conforms to IEEE P802.3by Ethernet standard and SFF-8402 SFP28, and is widely used in data center or supercomputing center system scenarios.

  1. 100G QSFP28 to QSFP28 DAC

100G QSFP28 to QSFP28 DAC can provide customers with 100G high-bandwidth data interconnection capability, providing 4 duplex channels, each channel can support up to 25Gb/s operating rate, and the aggregation bandwidth is 100Gb/s, in line with the SFF-8436 specification, used in Connection between devices with QSFP28 ports.

  1. 100G QSFP28 to 4*SFP28 DAC

100G QSFP28 to 4 SFP28 DAC has a 100G QSFP28 interface on one end and 4 25G SFP28 interfaces on the other end, which can provide customers with 100G high-bandwidth data interconnection capability, in line with SFF-8665/SFF-8679, IEEE 802.3bj, and InfinibandEDR standards, It is widely used in data center or supercomputing center system scenarios.

DAC connection scheme in the data center rack:

(1) High-speed cables are used for short-distance direct connection between data center racks, and the length is generally 1 to 10 meters.

(2) AOC active optical cable can be selected for short distances within 5 to 30 meters.

(3) Optical module + fiber jumper combination can be selected for long distances above 30 meters.

The QSFPTEK high-speed interconnect DAC cable product line includes SFP+, QSFP+, QSFP+ to SFP+ Breakout, QSFP28, QSFP28 to SFP28 Breakout. All of them are suitable for point-to-point applications in the data center.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-100382CVSS 10.0
    Improper Neutralization of Special Elements used in an OS Command (\'OS Command Injection\') vulnerability in Wikimedia Foundation Mediawiki...
    Admin intel📅 Updated: Oct 1, 2026
  • CVE-2026-76504CVSS 9.8
    A vulnerability in the API session-based authentication management of Cisco Catalyst SD-WAN Manager could allow an unauthenticated, remote...
    Admin intelCISA KEV📅 Added to KEV: Sep 30, 2026📅 Updated: Sep 30, 2026
  • CVE-2026-86950CVSS 8.8
    An out-of-bounds write issue was addressed with improved bounds checking. This issue is fixed in iOS 26.7.1 and...
    Admin intelCISA KEV📅 Added to KEV: Sep 29, 2026📅 Updated: Sep 29, 2026
  • CVE-2026-88772
    Memory overflow vulnerability leading to remote code execution or denial of service.
    Admin intelCISA KEV📅 Added to KEV: Sep 27, 2026📅 Updated: Sep 27, 2026
  • CVE-2026-88771
    Remote code execution due to improper input validation that can allow an unauthenticated attacker to execute arbitrary commands.
    Admin intelCISA KEV📅 Added to KEV: Sep 27, 2026📅 Updated: Sep 27, 2026
  • CVE-2026-65660CVSS 8.8
    Improper control of generation of code (\'code injection\') in Microsoft Office SharePoint allows an authorized attacker to execute...
    Admin intelCISA KEV📅 Added to KEV: Sep 25, 2026📅 Updated: Sep 25, 2026
  • CVE-2026-5430CVSS 10.0
    The JWT authentication mechanism accepts tokens signed with algorithms other than those explicitly configured or supported. This allows...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-71362CVSS 9.1
    Adobe Commerce is affected by an Incorrect Authorization vulnerability that could result in privilege escalation. An attacker could...
    CISA KEV📅 Added to KEV: Sep 24, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-58155CVSS 9.2
    Apache Traffic Server truncates over-long header names, allowing header aliasing, request smuggling, and policy bypass. This issue affects...
    📅 Updated: Oct 1, 2026
  • CVE-2026-58154CVSS 9.2
    Apache Traffic Server can write out of bounds or overflow integers while parsing MIME and HTTP headers. This...
    📅 Updated: Oct 1, 2026
  • CVE-2026-13043CVSS 9.3
    A missing authentication vulnerability in the Kernel Memory Access Driver (PSKMAD) used by WatchGuard endpoint security products allows...
    📅 Updated: Oct 1, 2026
  • CVE-2026-96658CVSS 9.9
    A flaw was found in Foreman. An authenticated attacker with low-level permissions can achieve remote code execution (RCE)...
    📅 Updated: Oct 1, 2026
  • CVE-2026-96659CVSS 9.1
    A flaw was found in Foreman. This vulnerability allows an authenticated user with low-level Viewer permissions to cause...
    📅 Updated: Oct 1, 2026
  • CVE-2026-13014CVSS 9.2
    A vulnerability in Thales CERT "Suspicious" application =< 1.3.4 allows a remote and unauthenticated attacker to execute arbitrary code...
    📅 Updated: Oct 1, 2026
  • CVE-2026-94620CVSS 9.4
    Classroom 50 is a free and open-source tool for managing and grading programming assignments via GitHub. Prior to...
    📅 Updated: Oct 1, 2026
  • CVE-2026-95284CVSS 9.6
    Buffer overflow in ANGLE in Google Chrome on on Android prior to 154.0.8037.57 allowed a remote attacker to...
    📅 Updated: Oct 1, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.