 Do Son
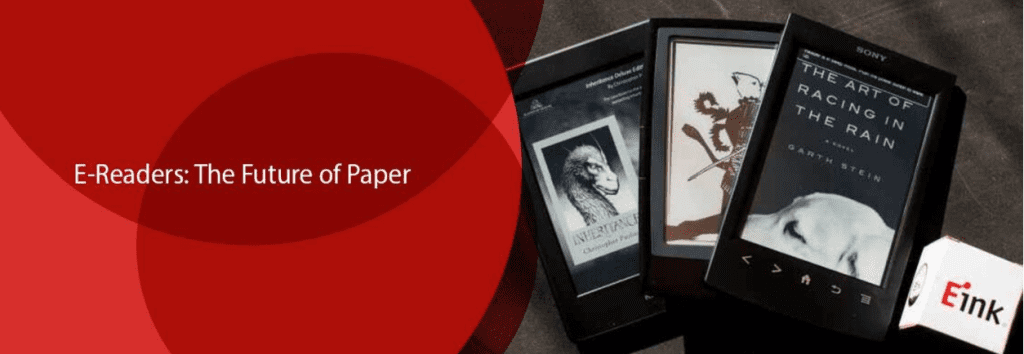

When e-readers and the idea of e-ink first came out many book lovers said they would not make the switch. They preferred their good old-fashioned paperback or hardback books. There was a lot of nostalgia surrounding the tangible book form where you could flip through the pages, smell the paper, dog-ear a page, and scribble some notes in the margins. There was a relationship built with a book in that form that simply people did not feel could be replicated with an e-reader.
But today many hardback lovers have come to the e-book side or the “dark side” as some might say. There is no denying the fact that e-books and e-readers are extremely convenient and handy to have for multiple reasons. What are those reasons you ask? Still reluctant to jump onto the e-reader bandwagon? Well, the truth is you do not have to be a whole-hearted e-reader lover or a die-hard tangible book’s fan. As much as people like to paint things in black and white you should know that it is possible to use both an e-reader and read off of hardbacks. Now that we have cleared up that dilemma by telling you that the two different reading forms are not mutually exclusive we can list down lots of reasons you should consider investing in an e-reader:
1. A Time-Saving Device
Life gets extremely busy especially as an adult. You have got things to do: food to cook, laundry to wash and fold, money to earn, bills to pay and so much more. So when you finally get that little bit of free time you might feel like curling up in bed and sleeping or watching a show to relax rather than stepping out of the comfort for your home. When stuck in this cycle it can become all too easy to give up the pleasurable habit of reading simply because you cannot go to the bookstore. This is why e-readers are a blessing in disguise since with CenturyLink internet you can simply purchase books online with a few clicks. You don’t need to pre-order the second part of your favorite trilogy or worry about a book-running out of stock because it will always be available online!
2. Easily Find a Book
With an e-reader, you can simply type the name or a few words from the title of a book you are looking for to find it. You also do not need to move to conduct the search. However, in the case of physical copies of books, you would need to perhaps spend a fair bit of time trying to find the book you are looking for especially if you employ no system for organizing your books.
Furthermore, you can even search up your favorite lines in a book using the e-reader’s search option whereas with a physical book you would probably end up fumbling through the pages even if you did highlight your favorite lines.
3. Read Any Book Anywhere
You might decide to venture out into the park to read a book, but you simply cannot make up your mind as to which book you would like to read. To top it off you might be a bit moody which means sometimes depending on your mood you enjoy a high fantasy book and sometimes you enjoy light-hearted witty comedies such as P.G. Wodehouse.
You could try stuffing your bag with three different books, but that could make things rather inconveniently heavy plus leave you with little room to stuff in a water bottle and some snacks. However, if you have an e-reader such as the Kindle then it is safe to say you have got your whole library at your disposal.
4. Portability
Most e-readers are designed such that they are quite thin and fairly small. A size that should be able to conveniently fit in your pocket or small bag. They are also lightweight and tend to have a great battery life which means you can carry it around and use it with almost no trouble at all.
5. Built-in Dictionary
You must know that feeling when you are reading a book and come across a word you do not know, but skip over anyway because putting down your book and looking up the word will break your flow and seems like too much of a hassle. Unfortunately, you probably reach a point where you realize that your vocabulary has not improved because you never look up the words! Don’t worry though because e-readers are here to save the day. Most e-readers have a built-in dictionary which means you can easily look up words while you read. In many instances, you can simply press a word and the meaning will pop up.
Also, e-readers like the Kindle may even compile a list of words you have looked up for your quick reference. This is especially a useful feature for school-going children who are still developing their writing and vocabulary.
6. Less Eye Strain
Did you know that e-readers are also easy on the eyes thanks to the invention of e-ink technology? E-ink technology is designed to create a paper-like feel which helps maintain a normal blink rate rather than a reduced one. This makes things much gentler on the eyes as opposed to using an LCD screen.
7. Hide What You Read
There is no doubt that life can get a little too hectic and too serious which means you might want to do some light-hearted reading where you know the plot is not great, but it is a fun breezy read to get your mind off things. You might want to read a Sophie Kinsella chickflick or one of the books from the Twilight series. And thanks to the Kindle you won’t need to worry about anyone judging you for what you are reading since they can’t see a book cover!
To Make the Long Story Short
E-readers are a great investment and using one does not mean you need to give up your good old hardback books. So with all the convenience, an e-reader has to offer, if you’re a bookworm you should probably consider investing in one.