Skip to content
October 22, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Technique
  • Guide For Beginners: How to Create A Website In Simple Steps?
  • Technique

Guide For Beginners: How to Create A Website In Simple Steps?

Do Son November 22, 2022 5 minutes read
Img_2022_11_22_19_01_55

Are you thinking of starting your website but don’t know where to start? Don’t worry; you’re not alone. This guide will walk you through creating a website in simple steps. We’ll cover everything from registering a domain name to designing your site. So whether you’re a complete beginner or need a refresher course, read on for all the information you need to get started.

Define the Purpose of your Site

The first step is to define what kind of website you want to create. Are you setting up a blog, an e-commerce store, or something else? As highlighted by the team behind Paddle Creative, this step is crucial in creating a successful website, as it helps you determine what features and functionality will be required to make your site work. Every purpose has different website requirements, so be sure to determine the purpose of your site before you jump into the rest of the steps.

Some tips to guide you in defining your purpose include the nature of your business, the products or services you offer, the audience you want to target, and your website’s goals. For instance, if you’re setting up an e-commerce store, you’ll need features like a shopping cart and payment gateway.

Choose a Domain Name

Once you have determined the purpose of your website, the next step is to choose a domain name. Your domain name should reflect the purpose of your site and make it easy for users to find you online. It’s important to note that some popular domains have already been taken, so try to create something creative while still keeping it simple.

When choosing a domain name, some factors include the length, the keywords it contains, and how easy it is to remember. You may also want to check if the domain name is available on popular social media platforms. This will help you create a consistent brand identity across all your profiles. For instance, if your domain name is ‘example.com’, you may also want to check if the same username is available on Twitter and Instagram.

Choose a Web Hosting Provider

Once you have chosen a domain name, the next step is choosing a web hosting provider to host your website. A web host is responsible for connecting your website to the internet, so you can make it available for people to access from anywhere in the world.

Selecting a web hosting provider might seem intimidating initially, but several options offer different levels of service and features. Most providers will have packages suitable for beginners, so be sure to shop around and find one that best suits your needs. Again, it is important to consider the purpose of your website and any additional features you might need, such as database support or email hosting.

Design and Develop Your Website

The next step is to design and develop your website. This will involve choosing a platform ranging from open-source solutions like WordPress or Joomla to more advanced options such as Magento for e-commerce stores.

Once you have chosen the platform, it’s time to start designing your website. Again, this can be a daunting task for beginners, so you may consider hiring a web designer or developer to help you with this stage. They can take care of the technical aspects and ensure your site is running smoothly. However, you can also use available tools and resources, such as tutorials and guides, to create your own website from scratch.

Test and Launch

Once you have designed and developed your website, the next step is testing it for any bugs or errors. Testing should be done on different browsers and devices to ensure platform compatibility. Additionally, it’s also important to test your site’s user experience to ensure visitors can access all its features and functions easily.

When you are satisfied with the design and functionality of your website, you’re ready to launch it! However, be sure to carry out regular maintenance on your website after launch. This will help ensure that everything is up-to-date and running smoothly in the long run.

Optimize your Website
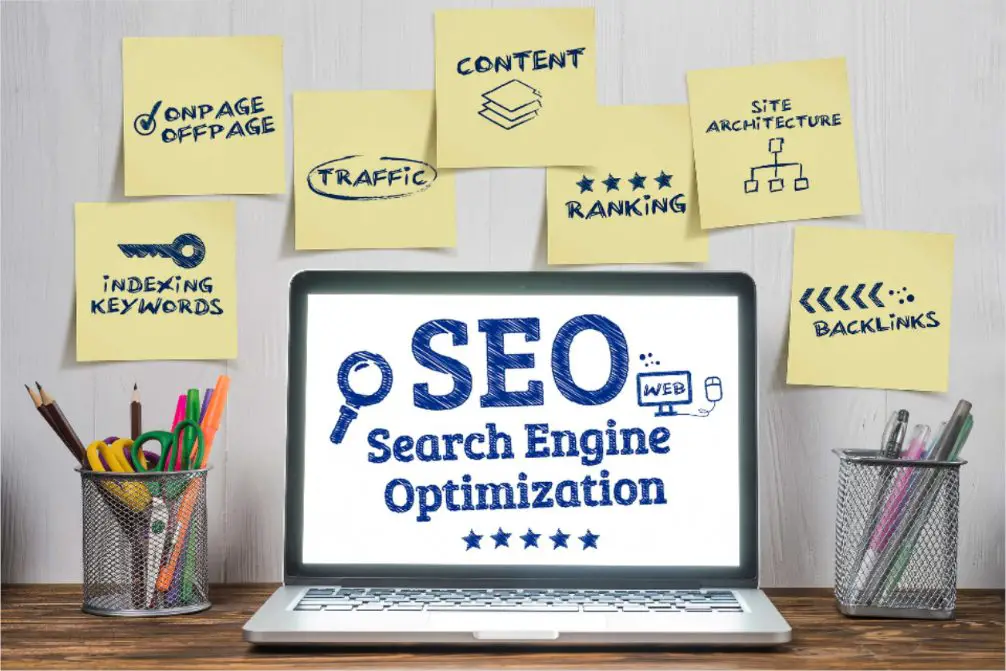
Once your website is up and running, optimizing it for better performance is the final step. This involves ensuring that your pages are loading quickly, improving user experience with a well-designed interface, and making sure search engines can crawl and index your site.

The best way to do this is by using tools such as Google Analytics or Google Search Console to track your website’s performance and identify areas for improvement. You can also use SEO techniques such as keyword research to ensure your pages are optimized for relevant search terms.

Creating a website doesn’t have to be a daunting task. By following the simple steps outlined above, you can create your own website in no time. From choosing a domain name and web hosting provider to designing and launching your website, each step requires careful consideration and attention to detail. Additionally, it’s important to maintain it regularly and optimize your website for better performance to ensure it remains up-to-date and functioning properly in the long run. With these simple steps, you can create a website that meets all your needs without hassle.

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2017-20287CVSS 8.7
    Javo Spot theme for WordPress before 3.0.0 contains a path traversal vulnerability that allows unauthenticated attackers to read...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2017-20288CVSS 5.1
    QCubed 2.2.0 through 3.1.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject scripts through...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2017-20289CVSS 7.7
    Broadstreet Ad Widget plugin for WordPress 2.2.0 before 2.12.0 contains a local file inclusion vulnerability that allows authenticated...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2026-109619CVSS 9.2
    PHP has various global state that temporarily points into request memory. In some scenarios, global state may not...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-109618CVSS 9.2
    PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request....
    Admin intel📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-113211CVSS 9.6
    Memory corruption in ServiceWorker in Google Chrome prior to 156.0.8078.47 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Oct 22, 2026
  • CVE-2026-113222CVSS 9.6
    Use after free in V8 in Google Chrome prior to 156.0.8078.47 allowed a remote attacker to potentially execute...
    📅 Updated: Oct 22, 2026
  • CVE-2026-113235CVSS 9.6
    Improper input validation in Passwords in Google Chrome prior to 156.0.8078.47 allowed a remote attacker to potentially execute...
    📅 Updated: Oct 22, 2026
  • CVE-2026-91665CVSS 9.8
    Vulnerability in Oracle Essbase (component: Security). The supported version that is affected is 21.8.3.0.0. Easily exploitable vulnerability allows...
    📅 Updated: Oct 22, 2026
  • CVE-2026-102785CVSS 10.0
    Joomla Extension - yootheme.com - Unauthenticated remote code execution in YOOtheme Pro 5.0.0-5.0.52 - YOOtheme Pro’s publicly accessible...
    📅 Updated: Oct 22, 2026
  • CVE-2026-111497CVSS 9.2
    A buffer overflow vulnerability in the Brotli decoder (c/dec/decode.c) in Google Brotli versions 1.0.3 through 1.2.0 on all...
    📅 Updated: Oct 22, 2026
  • CVE-2026-110264CVSS 10.0
    An issue has been discovered in GitLab CE/EE affecting all versions from 7.0 before 18.11.13, 19.0 before 19.0.10,...
    📅 Updated: Oct 22, 2026
  • CVE-2026-113252CVSS 9.6
    Improper input validation in ANGLE in Google Chrome on on Windows prior to 156.0.8078.47 allowed a remote attacker...
    📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.