Skip to content
November 12, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
  • Home
  • Technique
  • How does the speech synthesis system work?
  • Technique

How does the speech synthesis system work?

Do Son November 18, 2019 3 minutes read
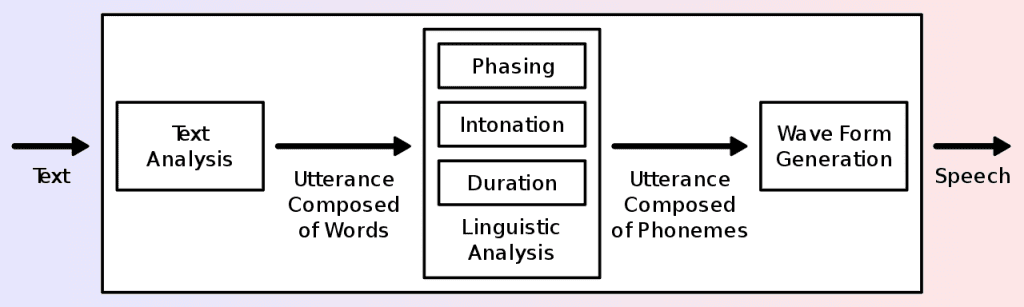
speech synthesis system

Andy0101 [Public domain], <a href="https://commons.wikimedia.org/wiki/File:TTS_System.svg">via Wikimedia Commons</a>

Speech synthesis processes an artificial voice that generates from a machine that reads out texts making it easier for visually impaired people and/or dyslexic people. The technology is known as Text-To-Speech (TTS). It has now become so common these days and is available in almost all smartphones.

Speech synthesis has a number of benefits in all kinds of fields. Those of you who didn’t know the meaning of TTS or speech synthesizer earlier would probably know what it is now by reading the article.

How speech synthesis works involve three essential stages; text to words, words to phonemes, and phonemes to sound.

  1. Text to words

It is easy for an adult to read a short or a long paragraph but when you ask the same paragraph to be read by a child, it gets challenging. The main reason is that the written text is ambiguous; a single word may have a different meaning and you may require proper knowledge or help from an educated person to make you understand under what context the word is used for. So, to reduce the ambiguity by narrowing down the article in a proper and easy manner to read and understand is the first step which is referred to as pre-processing or normalization.

English is a difficult language with lots of grammar and vocabulary rules. It is easy for a human being to know how to read numbers, dates, times, units, symbols, acronyms, synonyms and homonyms. But the same work is difficult for a machine to do. For example, the word ‘read’ can be pronounced in two ways- ‘read’ and ‘reed’.  How would the computer know which one to pronounce? So they use statistical probability techniques or neural networks to arrive at the most likely pronunciation by comparing with the tense of the sentence.

  1. Words to phonemes

Once the computer understands and converts the text to voice, the speech synthesizer has to generate the speech sounds. As we’ve already mentioned above, it is a pretty difficult task for a computer to read out the same words with a different pronunciation. The best alternative solution is to break the written words into graphemes. Once that’s done, the computer should be able to generate phonemes that correspond to them. This process will require a set of simple rules for the computer to follow. This is similar to a child reading words he or she has never encountered in their lives. For a person, a single line can be spoken with different styles and emotions while it is very difficult for a machine to do. The advantage of doing this is that the computer at least tries its best at reading any word.

  1. Phonemes to sound

This is the final step of how speech synthesis works. The conversion of phonemes to sound is possible in 3 different ways:

  • The first way is to use recordings of humans saying the phonemes
  • Another way is for the computer to generate the phonemes itself by generating basic sound frequencies. The most relevant example could be a music synthesizer.
  • The last way is to mimic the mechanism of the human voice.
Tags: speech synthesis system

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123039CVSS 7.8
    The Gaia OS DynamicCLI daemon runs as root and listens on a world-writable local socket (/tmp/dynamic_socket) without authenticating...
    Admin intel📅 Updated: Nov 12, 2026
  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-17131CVSS 9.3
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to obtain sensitive information due to server-side...
    📅 Updated: Nov 12, 2026
  • CVE-2026-17344CVSS 9.3
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to obtain sensitive information due to server-side...
    📅 Updated: Nov 12, 2026
  • CVE-2026-63857CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: net: airoha: Do not read uninitialized fragment address...
    📅 Updated: Nov 12, 2026
  • CVE-2026-121355CVSS 9.1
    Adobe Connect is affected by an Incorrect Authorization vulnerability that could result in privilege escalation. An attacker could...
    📅 Updated: Nov 12, 2026
  • CVE-2026-120869CVSS 9.4
    An unauthenticated attacker can bypass authentication controls to access restricted resources on the appliance Pre-conditions: Access to Citrix...
    📅 Updated: Nov 12, 2026
  • CVE-2026-120864CVSS 9.3
    Memory overflow in ICA proxy can lead to unpredictable or erroneous behavior or Denial of Service. Pre-conditions: The...
    📅 Updated: Nov 12, 2026
  • CVE-2026-107412CVSS 9.5
    Multiple Memory overflow vulnerabilities can lead to unpredictable or erroneous behavior and Denial of Service Pre-conditions: NetScaler is...
    📅 Updated: Nov 12, 2026
  • CVE-2026-107415CVSS 9.3
    Memory overflow in Email OTP authentication can lead to unpredictable or erroneous behavior or Denial of Service. Pre-conditions:...
    📅 Updated: Nov 12, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.