Skip to content
November 12, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
  • Home
  • Technique
  • How to Build a UX-Friendly Product?
  • Technique

How to Build a UX-Friendly Product?

Do Son September 17, 2021 4 minutes read
photo-1587440871875-191322ee64b0

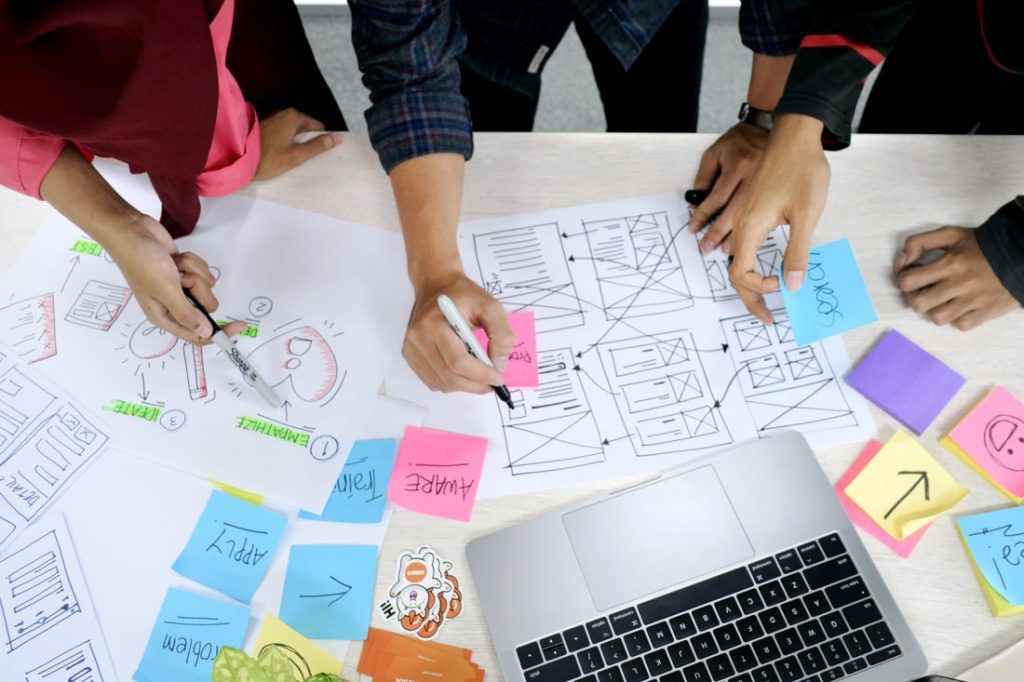
According to recent stats, about 90% of users close an app and leave a site because of their poor visual design and user experience. At the same time, 73% of top executives say they intend to increase the number of UX designers and front-end developers in their organization in the next five years to deliver more user-friendly solutions. These numbers say a lot about the importance of UX and front-end development.

Of course, UX plays an important role in determining how a customer sees your brand. If your site or app is slow and buggy, then your potential customers will think the same about your brand and product. On the other hand, if the site is fast and easy to use, then this can have a positive impact on the customer’s opinion and your ROI respectively.

As a website owner, you have to be smart about UX design. Not only is your website potentially your most powerful asset, but it also serves as a 24/7 salesperson promoting your brand day and night. So make sure that it has a proper look and feel. We’ve put together a few key points to help you create a great user experience.

#1 – Adaptability

Nowadays, the responsiveness of the site (app) is extremely important as users increasingly began to use mobile devices. When you’re done with the design of your mobile-friendly site, don’t forget to test it out with our dedicated mobile page validation tools. In case you do not have a dedicated team of front-end developers, you can always reach out to https://sumatosoft.com/ for help.

#2 – Empty Space

It is white space on the site that creates a sense of openness and freshness. This space also adds enough room for the visitor’s eye to rest and is a prime example of the innovative web design trend. Among other things, white space removes the feeling of clutter on the site and is a prerequisite for a good UX.

#3 – Page Load Time

People will quickly leave a site that takes a long time to load. As research shows, about 40% of all users will not continue browsing a site whose pages load more than 3 seconds. What’s more, customers who are not happy about the user experience are more likely to not to return to you and give preference to your competitors. Therefore, when designing your website, pay due attention to page load times.

#4 – Use Call to Action

CTA is a new trend in development that every front end development service pays special attention to. A call to action increases the chance that a user will perform a target action. Users click on attractive call-to-action buttons at least once and view the service offered. Remember that visual cues are always effective when it comes to customer acquisition.

#5 – Use Branded Colors

Color is especially important when it is necessary to make a website bright and recognizable. However, it is also important to use colors to create a brand image that users will always associate with you. Be especially mindful when creating call-to-action buttons. The right CTA buttons will help you boost conversion rates significantly.

#6 – Highlight Customer Reviews

It is a good approach to highlight reviews from customers who used your services. Testimonials build trust and are an effective way to increase website conversions. This is a kind of guarantee for users who are just going to work with you.

#7 – Think About Animation

Animated elements greatly enhance UX. They work best in conjunction with a call to action. Animations can also be used to display notifications and highlight the most important pieces of content on the page.

Make the UX Side of Your Project Work for You!

With the emergence of new web design and front-end development trends, people expect new and innovative user interfaces. This is where you can demonstrate your superiority! Create a unique UX-powerful project that your target audience will like – ensure boosted conversion rates and high revenues.


Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-90908CVSS 9.3
    A vulnerability in the GenericAdminAuthenticator component of Azul Payara Server and Azul Payara Micro allows a remote, unauthenticated...
    📅 Updated: Nov 12, 2026
  • CVE-2026-110003CVSS 9.3
    A vulnerability in the administration REST interface of Azul Payara allows a remote, unauthenticated attacker to bypass secure-admin...
    📅 Updated: Nov 12, 2026
  • CVE-2026-8333CVSS 9.4
    A stored cross-site scripting vulnerability in Microchip the TimePictra platform could allow an authenticated, low-privileged attacker to store...
    📅 Updated: Nov 12, 2026
  • CVE-2026-12591CVSS 9.9
    Zohocorp ManageEngine M365 Manager Plus versions below 4818 is affected by an authenticated technician may exploit insufficient permission validation in the delegated administration...
    📅 Updated: Nov 12, 2026
  • CVE-2026-12507CVSS 9.1
    Zohocorp ManageEngine AssetExplorer versions below 7860, ServiceDesk Plus versions below 15290, ServiceDesk Plus MSP versions below 15150, and...
    📅 Updated: Nov 12, 2026
  • CVE-2026-107935CVSS 9.3
    A path traversal vulnerability was found in gvproxy, the network forwarder provided by the gvisor-tap-vsock package. The unauthenticated...
    📅 Updated: Nov 12, 2026
  • CVE-2026-125883CVSS 9.3
    Improper restriction of XML external entity reference vulnerability in N-able N-central allows XML Schema Poisoning. This issue affects...
    📅 Updated: Nov 12, 2026
  • CVE-2026-76954CVSS 9.8
    An improper neutralization of special elements used in an SQL command vulnerability in the Auth API in Synology...
    📅 Updated: Nov 12, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.