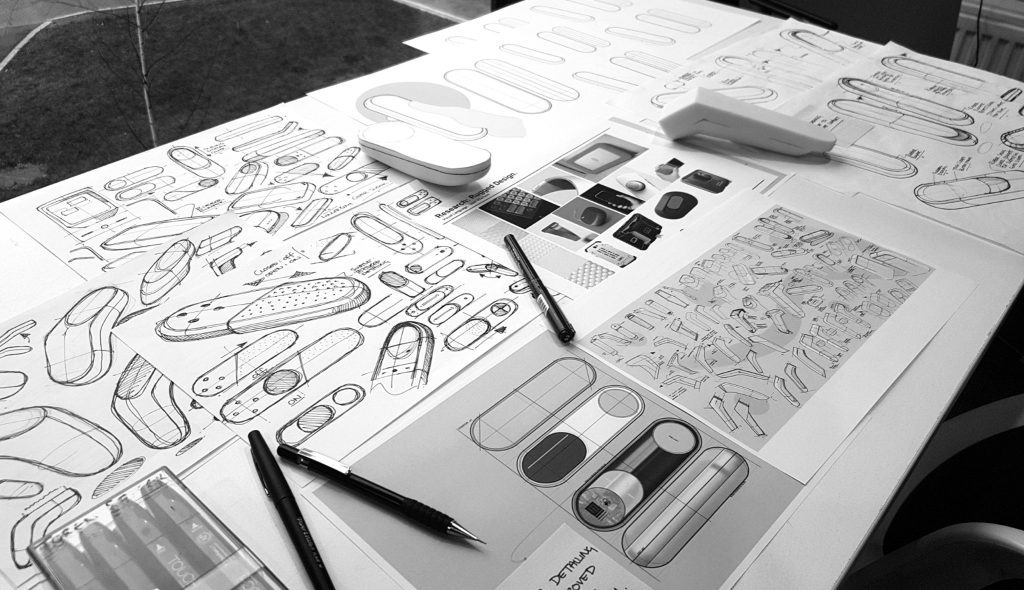
Skip to content
October 22, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Technique
  • How to create a good product design?
  • Technique

How to create a good product design?

Do Son August 18, 2022 3 minutes read
tech-dev

This is the true digital age, where most of our interactions with products, as well as conversions, take place online. Now physical goods have evolved into something different, more special, and modern.

But what is it that attracts our attention when buying on the Internet? That’s right, it’s all about product design. Today we gonna talk about this topic extensively.
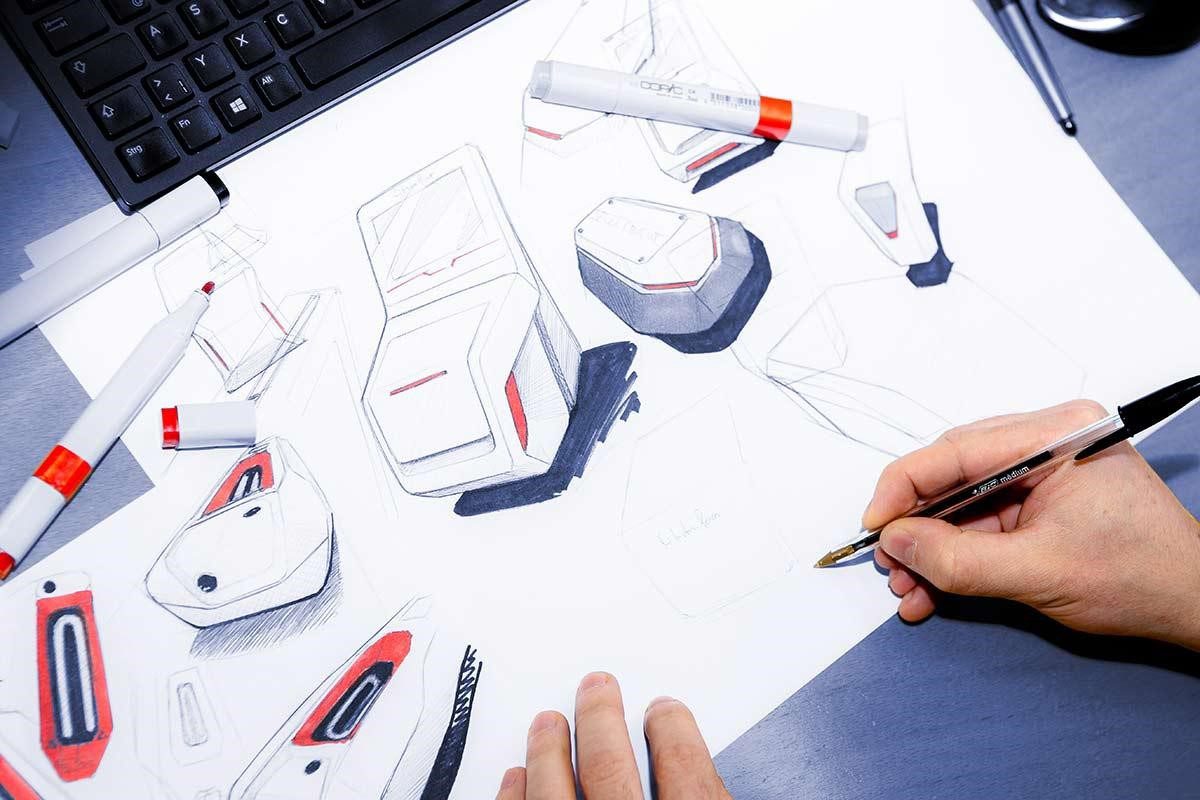
What is product design?

Product design includes several key attributes: it includes human interaction, it must take into account multiple users, and it exists in a competitive environment where users have choices. It also involves some degree of mass production or distribution and requires consideration of trade-offs between products, cost, features, and performance. To develop that same design, we need the help of specialists, namely a digital product design company.

What do product designers do?

Essentially, a “product” is anything (mobile app, new digital feature, tangible item, etc.) that solves a customer’s “problem” and moves a business forward in its market. And, of course, product designers are the people who conceptualize and create these things. Products can be durable, like household appliances, or consumables, like candy. They can be tangible, physical, or intangible elements such as an application or service. They cover the commercial and consumer markets.

Product Design Best Practices

Because product design spans a wide range of industries, platforms, and business needs, it can be difficult to know how to do a successful product design job from start to finish.

1. Define the product rationale and realities

Before you start developing a new product, take the time to understand what your product should look like in terms of logistics. What will it fix for users? How are you going to create it? What features do you need? How much money do you need for developing? Finally, there is “feasibility”, which means an assessment of what is needed for business success, such as market size and prices.

Of course, each of these product design pillars is interrelated, and balancing all of these considerations is critical to success. For example, a personal jetpack may be technically feasible and desirable for end users, but if they are willing to pay only $200 for it and it costs $500 to make, it will fail.

2. Know your customer

It is also important that brands develop close relationships with the consumers who will be using the product. This will help them understand what features consumers want and better understand the market, allowing them to create really useful and quickly successful products.

Also, as we mentioned earlier, product design always involves trade-offs. Brands need specific processes to navigate them effectively because elements such as risk, price, features, features, time to market, and other elements need to be strategically balanced for a successful product development project.

3. Carefully study your brand, mission, and marketplace

Before embarking on a product design project, it is important to truly understand the role, power, and value of your brand. Does the product you are considering fit your brand and your customer base?

The more analysis you do, the better conditions will be for you to enter the market and understand the situation as a whole.

Thanks to these simple tips, you can get a cool product design that will constantly delight consumers and bring you conversions and good income. If you want to get a more professional approach, then you should hire backend developer.

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-114625CVSS 9.9
    VeloCloud Orchestrator (VCO) on-prem has a security issue where this issue may allow a remote attacker to access...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2026-109619CVSS 9.2
    PHP has various global state that temporarily points into request memory. In some scenarios, global state may not...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-109618CVSS 9.2
    PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request....
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2014-125131CVSS 5.1
    DedeCMS 5.6 and 5.7 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject script by...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2015-20124CVSS 8.7
    Aspose Importer & Exporter plugin for WordPress before 3.0 contains a path traversal vulnerability that allows unauthenticated attackers...
    Watchtower Verified📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-114625CVSS 9.9
    VeloCloud Orchestrator (VCO) on-prem has a security issue where this issue may allow a remote attacker to access...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-63887CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: target: iscsi: Bound iscsi_encode_text_output() appends to rsp_buf...
    📅 Updated: Oct 22, 2026
  • CVE-2026-63886CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: target: iscsi: Validate CHAP_R length before base64...
    📅 Updated: Oct 22, 2026
  • CVE-2026-76531CVSS 9.9
    As part of Cisco's ongoing commitment to proactive security and product quality, Cisco has conducted a comprehensive internal...
    📅 Updated: Oct 22, 2026
  • CVE-2026-76474CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality, engineering teams for Cisco Emergency Responder,...
    📅 Updated: Oct 22, 2026
  • CVE-2026-76475CVSS 9.3
    As part of Cisco's ongoing commitment to proactive security and product quality, engineering teams for Cisco Emergency Responder,...
    📅 Updated: Oct 22, 2026
  • CVE-2026-76473CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality, engineering teams for Cisco Emergency Responder,...
    📅 Updated: Oct 22, 2026
  • CVE-2026-76302CVSS 9.9
    As part of Cisco's ongoing commitment to proactive security and product quality, Cisco has conducted a comprehensive internal...
    📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.