Skip to content
October 17, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Technology
  • M-Lab: average global broadband speed was 9.1 Mbps
  • Technology

M-Lab: average global broadband speed was 9.1 Mbps

Do Son July 12, 2018 3 minutes read
Accenture Ookla acquisition global broadband speed
Add Daily CyberSecurity as a preferred source on Google

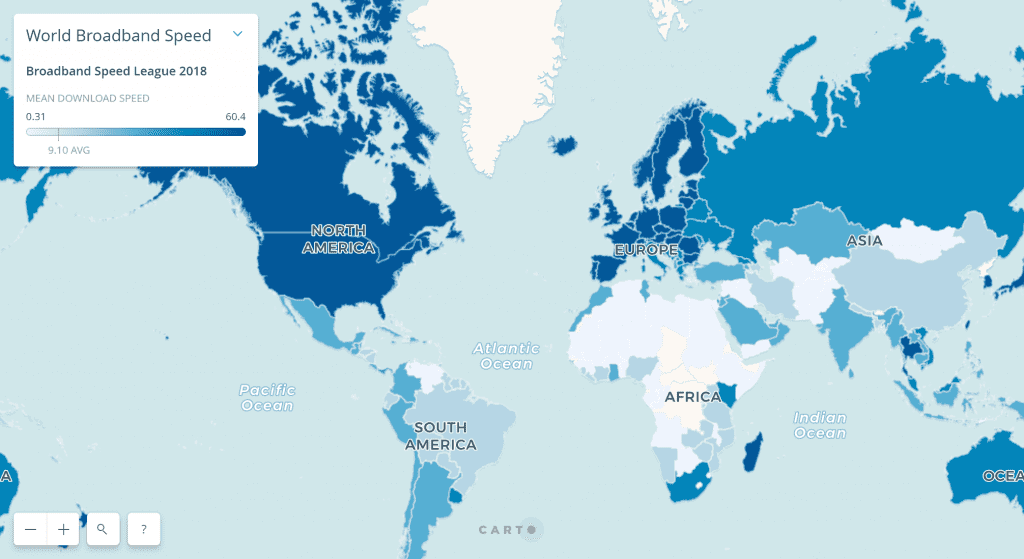
Recently, the M-Lab Global Broadband Speed Alliance released a report of 163 million independent network speed test points worldwide from May 30, 2017, to May 29, 2018. According to the report, the global average network speed is 23% faster, reaching 9.1 Mbps than 7.4 Mbps last year.

M-Lab has tracked broadband speed measurements in 200 countries (189 countries last year) over the past 12 months, which allows us to understand the average speed of global broadband. The good news is that the global average speed is rise rapidly.

Singapore took the lead in 2017 and 2018, with an average download speed from 55Mbps to 60Mbps. Sweden’s second average speed is 46 Mbps, Denmark is third, and its average download speed has increased by 10 Mbps, from 33 Mbps to 43 Mbps. Norway ranked fourth with an average rate of 40.12 Mbps.

The global average grew by 23% year-on-year, but another data is surprising. The top 100 countries in the rankings grew by an average of 5.43 Mbps, while the last 100 only increased by 0.41 Mbps.

However, if you consider the percentage increase, this data can still be said. The average broadband speed in the top 100 countries increased by 29.04%. The average broadband speed in the 100 countries at the bottom of the ranking increased by 24.22%.

Of course, if you choose the top 25 and the bottom 25, the average speed of the top 25 is increased by 28.88%, while 7.40% only increases the last 25. Another statistical method shows that the top 25 countries accounted for 45.30% of the total growth, while the overall growth rate of the previous 25 states was almost negligible at 0.19%.

Cable consumer telecom analyst Dan Howdle said, “With average broadband speeds rising by 23% in just one year it would be easy to assume an overall positive global picture. However, a closer look reveals the acceleration is concentrated towards the top end: the faster countries are improving more quickly, with those towards the bottom end of the table verging on stagnation.”

Since the UK has just begun to promote FTTP (Fiber to the Home), there are already many other European countries that are far ahead of the UK in this regard so that the UK may fall even more next year.

The forefront of the table is dominated by Europe, with 36 of the top 50 countries in Europe. Last year’s results made the UK ranked 31st in the world. This year, the UK ranked 35th.

Europe, the United States, and the Asia-Pacific region (Singapore, Japan, Taiwan, and Hong Kong) are thriving economic centres that are world leaders in providing fast, reliable broadband, indicating a close relationship between broadband speed and the economy.

Related coverage

  • Google Uses Artificial Intelligence to Launch Emoji Scavenger Hunt
  • Agentic Era Begins: Google DeepMind Launches Gemini 3.5 Flash to Power 24/7 AI Workers
  • Google Drive Desktop Gets Major Redesign: Unified UI Centralizes Files, Sync & Notifications
  • Claude Mythos 5 Returns: US Government Lifts AI Ban
  • 1Password Free Family Plan: How to Keep Getting 1 Year of Free Premium Access
  • The End of AirPods’ Monopoly: Apple to Unlock Proximity Pairing and Smartwatch Replies
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: global broadband speed

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 17, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 17, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 17, 2026
  • CVE-2026-111862CVSS 9.8
    Rank Math SEO PRO for WordPress is affected by a supply-chain compromise in a subset of version 3.0.123...
    Admin intel📅 Updated: Oct 17, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    Watchtower Verified📅 Updated: Oct 17, 2026
  • CVE-2025-61624CVSS 6.0
    An Improper Limitation of a Pathname to a Restricted Directory (\'Path Traversal\') [CWE-22] vulnerability in Fortinet FortiOS 7.6.0...
    CISA KEV📅 Added to KEV: Oct 16, 2026
  • CVE-2026-102764CVSS 9.3
    The vulnerability exists within internal components of BeyondTrust’s Remote Support product. The components did not adequately validate the...
    CISA KEV📅 Added to KEV: Oct 16, 2026
  • CVE-2026-106931CVSS 8.5
    SiteGuard Server Edition contains an OS command injection vulnerability, which may allow an attacker to execute arbitrary OS...
    Admin intel📅 Updated: Oct 15, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-111862CVSS 9.8
    Rank Math SEO PRO for WordPress is affected by a supply-chain compromise in a subset of version 3.0.123...
    Admin intel📅 Updated: Oct 17, 2026
  • CVE-2026-104736CVSS 9.8
    The LearnPress plugin for WordPress is vulnerable to PHP Object Injection in versions up to, and including, 4.4.10...
    📅 Updated: Oct 17, 2026
  • CVE-2026-101950CVSS 9.3
    A Heap-based Buffer Overflow vulnerability in the SVR component of Juniper Networks Junos OS on SRX Series allows...
    📅 Updated: Oct 17, 2026
  • CVE-2026-110653CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Oct 17, 2026
  • CVE-2026-97381CVSS 9.9
    Legacy Update is a tool for activating and installing updates on legacy Windows PCs. Legacy Update 1.12.0 through...
    📅 Updated: Oct 17, 2026
  • CVE-2026-93895CVSS 9.1
    IBM WebSphere Application Server - Liberty 20.0.0.12 through 26.0.0.10 could allow an unauthenticated remote attacker to bypass access...
    📅 Updated: Oct 17, 2026
  • CVE-2026-111823CVSS 9.8
    Mage OSS through 0.9.80 before 76c4f46 can proceed with session creation upon encountering an unknown OAuth provider.
    📅 Updated: Oct 17, 2026
  • CVE-2026-106629CVSS 9.3
    Adobe Experience Manager is affected by a stored Cross-Site Scripting (XSS) vulnerability that could be abused by an...
    📅 Updated: Oct 17, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.