Skip to content
September 27, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Malware
  • New AndroRAT variant hit Android devices
  • Malware

New AndroRAT variant hit Android devices

Do Son February 19, 2018 4 minutes read
AndroRAT
Add Daily CyberSecurity as a preferred source on Google

Recently, Trend Micro detected a new variant of the Android Remote Access Tool (AndroRAT), which researchers have identified as ANDROIDOS_ANDRORAT.HRXC, which can inject root vulnerabilities in existing devices and perform malicious attacks such as silent installation, shell command execution, WiFi password collection and screen capture. This variant of AndroRAT is targeted at CVE-2015-1805, a publicly disclosed vulnerability in 2016 that is a high-risk vulnerability that can be used to elevate permissions and run arbitrary code on vulnerable devices. In fact, A long time ago, was found in the upstream Linux kernel.

RAT attacks have always been a common Windows threat, so it should not be surprising for Android. Take CVE-2015-1805, though it was fixed in April 2014. Unfortunately, however, people underestimated the vulnerability, and by 2016 it was re-used by hackers and could be used to attack the Android operating system. RAT typically exploits the root privileges of a device by exploiting vulnerabilities and then controls the entire operating system. As early as 2012, Trend Micro researchers found that AndroRAT was originally a project developed at a university lab, intended to be developed as an open source client or server application that provides remote control of the Android system, which Will naturally attract cybercriminals.

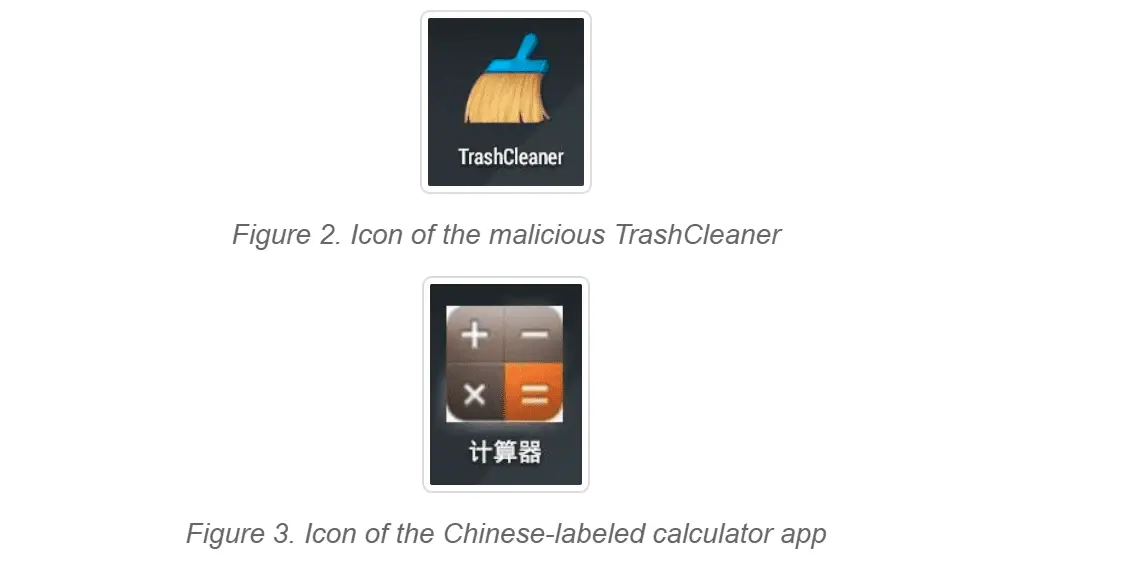
This new variant of AndroRAT disguises itself as a malicious utility called TrashCleaner, which may have been downloaded via a malicious URL. When TrashCleaner first runs, it prompts the Android device to install a Chinese-labeled calculator application similar to a pre-installed system calculator. At the same time, the TrashCleaner icon disappears from the device’s user interface and activates the RAT in the background.


Configurable RAT services are controlled by the remote server, which means that attackers may issue remote commands to trigger different malicious behaviors in real time. When executing a privileged operation, this variant activates the embedded root attack. At this point it will perform the following malicious actions in the original AndroRAT:

  • Record audio
  • Take photos using the device camera
  • Theft of system information such as phone model, number, IMEI, etc.
  • Theft of WiFi names connected to the device
  • Theft of call logs including incoming and outgoing calls
  • Theft of mobile network cell location
  • Theft of GPS location
  • Theft of contacts list
  • Theft of files on the device
  • Theft of list of running apps
  • Theft of SMS from device inbox
  • Monitor incoming and outgoing SMS

Apart from the original features of the AndroRAT, it also performs new privileged actions:

  • Theft of mobile network information, storage capacity, rooted or not
  • Theft of list of installed applications
  • Theft of web browsing history from pre-installed browsers
  • Theft of calendar events
  • Record calls
  • Upload files to victim device
  • Use front camera to capture high-resolution photos
  • Delete and send forged SMS
  • Screen capture
  • Shell command execution
  • Theft of WiFi passwords
  • Enabling accessibility services for a keylogger silently

Google CVE-2015-1805 was patched in March 2016 but has not been upgraded or some older devices may be affected by this new AndroRAT variant, but unfortunately, there are still a large number of mobile users still using it The older version of Android, these versions may still exist CVE-2015-1805.

Mitigation measures

Users should avoid downloading applications from third-party application stores to avoid being compromised by attacks such as AndroRat. When it comes to devising security, users should try their best to download from the legitimate app store. In addition, periodic updates to the device’s operating system and applications can also reduce the risk posed by new exploits.

Google said this new malicious variant of the app has not been released on Google Play so far and they have included CVE-2015-1805 testing in their security tests. Ideally, any devices started or updated after April 2016 will not be affected.

Indicators of Compromise (IoCs)

Source: TrendMicro

Related coverage

  • Tangerine Turkey Cryptomining Worm Spreads Via USB Drives, Hides Payloads with VBScript and LOLBins
  • North Korea’s Cyber Shadow War: Unmasking RustBucket and KandyKorn
  • MacSync macOS Stealer Spreads via ClickFix Lures
  • EDRKillShifter: A New EDR-Killing Tool in Ransomware Attack
  • Chinese Cyberspies Breach Asian Telecoms in Long-Running Espionage Campaign
  • Destructive npm Packages Disguised as Utilities Trigger Remote System Wipes on Demand
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: AndroRAT

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-65660CVSS 8.8
    Improper control of generation of code (\'code injection\') in Microsoft Office SharePoint allows an authorized attacker to execute...
    Admin intelCISA KEV📅 Added to KEV: Sep 25, 2026📅 Updated: Sep 25, 2026
  • CVE-2026-5430CVSS 10.0
    The JWT authentication mechanism accepts tokens signed with algorithms other than those explicitly configured or supported. This allows...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-71362CVSS 9.1
    Adobe Commerce is affected by an Incorrect Authorization vulnerability that could result in privilege escalation. An attacker could...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-48842CVSS 8.1
    Roundcube Webmail 1.6.x before 1.6.16 and 1.7.x before 1.7.1 has Pre-authentication SQL injection in the virtuser_query plugin via...
    Admin intel📅 Updated: Sep 23, 2026
  • CVE-2026-87902
    Unauthenticated path traversal in page-template resolution leading to conditional RCE An unauthenticated attacker can make get_page_template() page-template resolution...
    Admin intelCISA KEV📅 Added to KEV: Sep 25, 2026📅 Updated: Sep 23, 2026
  • CVE-2026-94127CVSS 9.8
    When a BIG-IP APM access policy and an OAuth profile is configured on a virtual server, specific malicious...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-85102CVSS 9.8
    Improper certificate trust validation during VPN negotiation in Check Point Quantum Security Gateway may allow an unauthenticated remote...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-93616CVSS 9.8
    A directory traversal and file upload vulnerability allows an unauthenticated attacker to upload and execute arbitrary scripts on...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-100741CVSS 9.8
    Eval injection in the JScript event-script dispatcher in Progressive Robot Ltd's hMailServer, versions 6.0.0 through 6.3.3 on Windows,...
    📅 Updated: Sep 27, 2026
  • CVE-2026-96625CVSS 9.1
    fedify-dev/fedify repository advisory GHSA-q9f8-5hc7-898f
    📅 Updated: Sep 27, 2026
  • CVE-2026-94130CVSS 9.3
    Joomla Extension - joomlaboat.com - Unauthenticated SQL injection in YouTube Gallery extension < 5.7.3 - An SQL injection...
    📅 Updated: Sep 27, 2026
  • CVE-2026-97161CVSS 9.2
    Joomla Extension - lomart.fr - Various path traversal / file access vectors in UP plugin extension 5.0.0-5.2.0, 6.0.0-6.0.29
    📅 Updated: Sep 27, 2026
  • CVE-2026-97163CVSS 10.0
    Joomla Extension - lomart.fr - Unauthenticated remote code installation in UP plugin extension 5.0.0-5.2.0, 6.0.0-6.0.29
    📅 Updated: Sep 27, 2026
  • CVE-2026-94132CVSS 9.5
    Joomla Extension - acymailing.com - Remote Code Execution vulnerability in mailbox action feature in AcyMailing Enterprise extension <...
    📅 Updated: Sep 27, 2026
  • CVE-2026-97160CVSS 9.4
    Joomla Extension - lomart.fr - Authenticated, privileged PHP command injection in UP plugin extension 5.0.0-5.2.0, 6.0.0-6.0.29
    📅 Updated: Sep 27, 2026
  • CVE-2026-100835CVSS 9.1
    Contrast before 1.16.0 is susceptible to remote attestation relay attacks. Contrast accepted any TEE attestation report that verified...
    📅 Updated: Sep 27, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.