Skip to content
November 3, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
The Compute Conundrum: Anthropic Doubles Claude Cowork Window Limits Amid Backlash Claude Cowork quota update Claude Desktop native messaging bridge Anthropic Opus 4.5 Claude Excel Integration
  • Technology

The Compute Conundrum: Anthropic Doubles Claude Cowork Window Limits Amid Backlash

Do Son June 7, 2026 1

Analyze the recent Claude Cowork quota update from Anthropic. Learn how doubled limits affect your weekly caps and why users are criticizing the promotion.

Massive PyPI Supply Chain Attack Staged via Malware Startup Hooks PyPI supply chain attack Socket malware detection PyPI Typosquat, Python RAT
  • Malware

Massive PyPI Supply Chain Attack Staged via Malware Startup Hooks

Do Son June 7, 2026 0

A massive PyPI supply chain attack has hit developers. Learn how Socket malware detection uncovered the Hades cluster stealing cloud credentials.

Cryptographic Compliance: 1Password Resolves Hardware Token Configuration Disparity 1Password hardware token PIN 1Password Agentic Autofill, Human-in-the-Loop 1Password has released security updates to address two vulnerabilities (CVE-2024-42218 and CVE-2024-42219)
  • Vulnerability Report

Cryptographic Compliance: 1Password Resolves Hardware Token Configuration Disparity

Do Son June 7, 2026 0

Discover the upcoming 1Password hardware token PIN support. Learn how a recent bug report prompted changes to desktop app verification metrics.

The Compute Coalition: Alphabet Secures $30 Billion AI Lease with SpaceX Google SpaceX cloud deal
  • Technology

The Compute Coalition: Alphabet Secures $30 Billion AI Lease with SpaceX

Do Son June 7, 2026 0

Discover the massive Google SpaceX cloud deal. Learn how Alphabet will pay $920 million monthly to lease 110,000 Nvidia GPUs from xAI.

Cryptographic Sanctuaries: OpenAI Unveils “Lockdown Mode” to Counter Prompt Injection Risks ChatGPT Lockdown Mode OpenAI OpenClaw acquisition OpenAI Prism GPT-5.2 LaTeX, scientific research AI workspace OpenAI, Mixpanel Breach ChatGPT Data Preservation, NYT Lawsuit ChatGPT Apps SDK, super app OpenAI Jony Ive, AI Hardware Delay Musk Apple lawsuit, App Store antitrust UK AI Partnership, OpenAI Collaboration Jony Ive OpenAI, DoD Contract OpenAI Lawsuit, ChatGPT Privacy North Korea ChatGPT - GPT-4.5 model OpenAI Models, AI Advancements OpenAI pricing, Flex API
  • Technology

Cryptographic Sanctuaries: OpenAI Unveils “Lockdown Mode” to Counter Prompt Injection Risks

Do Son June 7, 2026 0

Discover the new ChatGPT Lockdown Mode by OpenAI. Learn how it restricts network and agent features to stop prompt injection data exfiltration.
Sovereign Expansion: Google Unveils Gemini Go to Unify Entry-Level Android Architecture Google Gemini Go app Google AI software engineering interview Google Gemini for Mac
  • Technology

Sovereign Expansion: Google Unveils Gemini Go to Unify Entry-Level Android Architecture

Do Son June 7, 2026 0

Discover the new Google Gemini Go app. Learn how this lightweight assistant replaces Google Assistant Go on budget Android Go phones.

The Monopoly Menace: Alliance Assails Microsoft’s Aggressive Browser Promotion Microsoft Edge Google account login interface and synchronization settings Browser Choice Alliance letter Microsoft Edge cleartext credentials memory dump Microsoft Edge auto-startup Microsoft Edge Collections sunset, export Edge Collections CSV Edge IE Mode Zero-Day, Chakra Exploit Windows Search, Microsoft Edge AI video translation, Edge browser Microsoft Editor, Edge Edge Developer tools Windows 10 ESU, Microsoft Edge Microsoft Edge, FCP Optimization CVE-2023-36735 Edge, AI Search
  • Technology

The Monopoly Menace: Alliance Assails Microsoft’s Aggressive Browser Promotion

Do Son June 7, 2026 0

Read about the new Browser Choice Alliance letter to Microsoft. Discover how browser makers are fighting against predatory Edge promotions on Windows.

CISA Warns of Actively Exploited SolarWinds Serv-U Flaw CVE-2024-28991 & CVE-2024-28990 SolarWinds RCE vulnerability CVE-2025-26399
  • Vulnerability Report

CISA Warns of Actively Exploited SolarWinds Serv-U Flaw

Do Son June 6, 2026 0

Protect your network from active CVE-2026-28318 exploitation. Apply patches for this critical Serv-U vulnerability before the June 19 deadline.

PHANTOMPULSE Malware Analysis: Advanced Cryptographic Implants Exploiting Blockchain Networks PHANTOMPULSE malware analysis blockchain C2 channel
  • Malware

PHANTOMPULSE Malware Analysis: Advanced Cryptographic Implants Exploiting Blockchain Networks

Do Son June 6, 2026 0

An in-depth PHANTOMPULSE malware analysis reveals a sneaky blockchain C2 channel and AI-assisted coding techniques used by advanced threats.
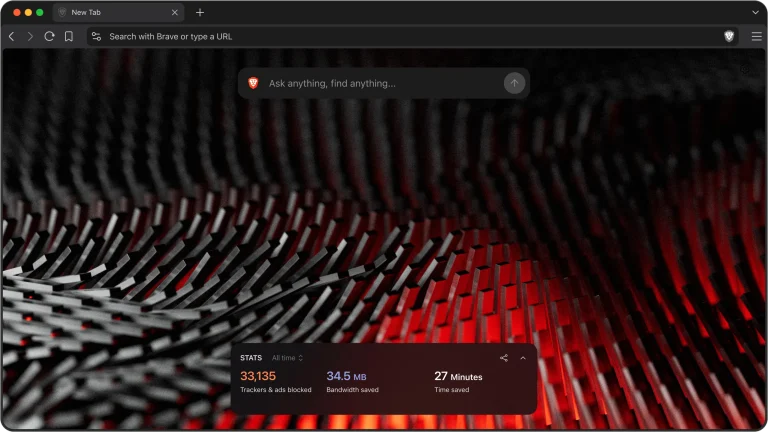
The Purified Desktop: Brave Software Launches Premium, Unfettered “Origin” Browser Brave Origin browser
  • Technology

The Purified Desktop: Brave Software Launches Premium, Unfettered “Origin” Browser

Do Son June 5, 2026 0

Discover the new Brave Origin browser. Learn how this paid, minimalist ad-blocking version completely removes AI, crypto, and reward features.
How Small Tech Teams Address Network Vulnerabilities Without Disrupting Workflows CVE-2025-20059
  • Technique

How Small Tech Teams Address Network Vulnerabilities Without Disrupting Workflows

Do Son June 5, 2026 0
Small tech teams carry a security burden that does not scale with headcount. Identifying vulnerabilities, patching systems,...
Read More Read more about How Small Tech Teams Address Network Vulnerabilities Without Disrupting Workflows
Large-Scale Malvertising Network Floods Asia-Pacific Social Media Platforms APAC malvertising scam campaigns Meta advertising platforms
  • Cybercriminals

Large-Scale Malvertising Network Floods Asia-Pacific Social Media Platforms

Do Son June 5, 2026 0

A massive wave of APAC malvertising scam campaigns floods Meta advertising platforms, targeting health and financial anxieties across 13 countries.
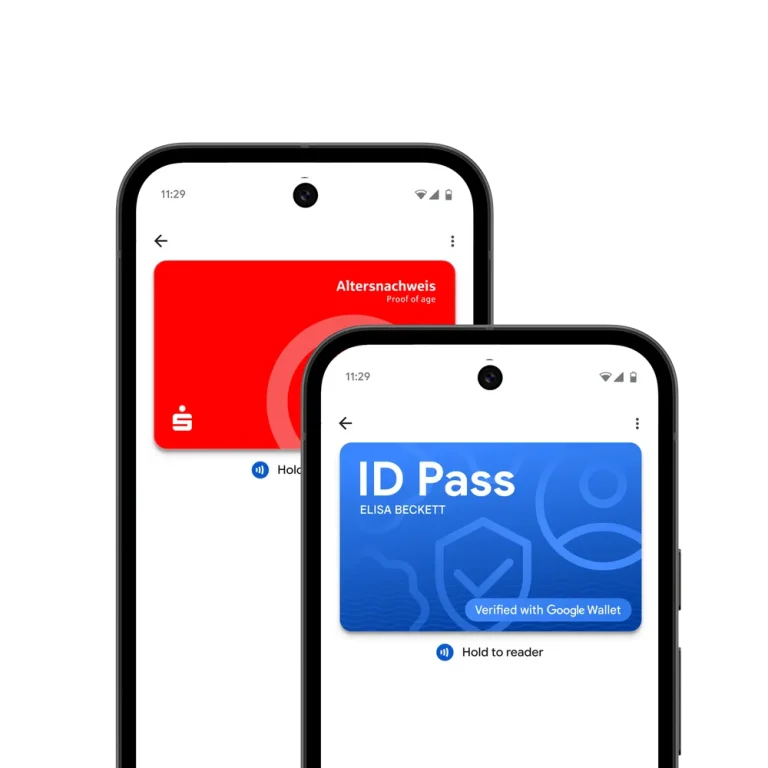
The Digital Sovereign: Google Wallet Pioneers Cryptographic Identity and Streamlined Commerce in Europe Google Wallet digital ID
  • Technology

The Digital Sovereign: Google Wallet Pioneers Cryptographic Identity and Streamlined Commerce in Europe

Do Son June 5, 2026 0

Discover the new Google Wallet digital ID expansion in the EU. Learn how Sparkasse age verification uses zero-knowledge cryptography.

Stealthy New Remcos RAT Variant Evades Detection Using Innovative Staging Layers new Remcos RAT variant DonutLoader shellcode
  • Malware

Stealthy New Remcos RAT Variant Evades Detection Using Innovative Staging Layers

Do Son June 5, 2026 0

G Data uncovers a new Remcos RAT variant using DonutLoader shellcode and trusted LOLBins to bypass Windows security filters.

FreeRADIUS Security Patches Fix Critical Buffer Overflow Vulnerabilities FreeRADIUS security patch unauthenticated buffer overflow vulnerabilities
  • Vulnerability Report

FreeRADIUS Security Patches Fix Critical Buffer Overflow Vulnerabilities

Do Son June 5, 2026 0

Secure your authentication server now. The latest FreeRADIUS security patch addresses serious unauthenticated buffer overflow vulnerabilities.

TP-Link Patches Critical Setup Flaw Across Multiple Tapo Smart Devices Archer MR600 command injection WireGuard client configuration Tapo smart device vulnerability unencrypted Bluetooth transmission TP-Link router vulnerability CVE-2026-5509 patch Archer AX53 Vulnerability TP-Link Router Security Tapo C520WS Vulnerability TP-Link Security Patch TP-Link Archer NX Router Vulnerability TP-Link Archer Vulnerability CVE-2025-15568 TP-Link Archer BE230 Vulnerability Command Injection TP-Link Omada Vulnerability CVE-2025-9520 TP-Link Archer MR600 Vulnerability CVE-2025-14756 CVE-2026-0629 TP-Link Omada RCE, CVE-2025-6542 TP-Link, Smart plug vulnerability TP-Link Archer C50, Hardcoded DES Key TP-Link NVR, Command Injection TP-Link Routers cybersecurity
  • Vulnerability Report

TP-Link Patches Critical Setup Flaw Across Multiple Tapo Smart Devices

Do Son June 5, 2026 0

A critical Tapo smart device vulnerability stems from unencrypted Bluetooth transmission. Learn how to patch your smart plugs, bulbs, and chimes.

International Law Enforcement Smashes Major Identity Forgery Ring counterfeit document production facility fraudulent identity documents
  • Cybercriminals

International Law Enforcement Smashes Major Identity Forgery Ring

Do Son June 5, 2026 0

Europol dismantled a counterfeit document production facility in Spain distributing fraudulent identity documents across Europe through an online marketplace.

International Law Enforcement Smashes Major Illegal Streaming Networks illegal streaming networks complex criminal enterprises UAT-7290 China-nexus Espionage Adversarial Misuse of Generative AI
  • Cybercriminals

International Law Enforcement Smashes Major Illegal Streaming Networks

Do Son June 5, 2026 0

Europol targets illegal streaming networks run by complex criminal enterprises. The joint action dismantled nine crime groups and removed 27,000 URLs.
Teamwork Cloud RCE Vulnerability Threatens Corporate Modeling Platforms Teamwork Cloud RCE vulnerability untrusted deserialization flaw
  • Vulnerability Report

Teamwork Cloud RCE Vulnerability Threatens Corporate Modeling Platforms

Do Son June 5, 2026 0

A critical Teamwork Cloud RCE vulnerability exploits an untrusted deserialization flaw. Patch No Magic and CATIA systems now.
Poly VoIP Phone Vulnerability Revealed with Public Exploit Code Disclosed Poly VoIP phone vulnerability public exploit code released
  • Vulnerability Report

Poly VoIP Phone Vulnerability Revealed with Public Exploit Code Disclosed

Do Son June 5, 2026 0

A critical Poly VoIP phone vulnerability is exposed. Read the report now that public exploit code released online to secure your office networks.

Critical Policy Bypass Flaw Threatens OpenStack Mistral Workflow Environments Mistral policy bypass flaw arbitrary code execution CVE-2024-40767 Keystone Vulnerability S3 Bypass
  • Vulnerability Report

Critical Policy Bypass Flaw Threatens OpenStack Mistral Workflow Environments

Do Son June 5, 2026 0

A critical Mistral policy bypass flaw allows arbitrary code execution. Learn how to patch your workflow service to prevent security credentials theft.
IBM WebSphere Security Advisory: Critical Vulnerabilities Uncovered IBM WebSphere execution flaws WebSphere security bulletin patches request smuggling patch WebSphere remote code execution Langflow OSS vulnerability remote code execution patch
  • Vulnerability Report

IBM WebSphere Security Advisory: Critical Vulnerabilities Uncovered

Do Son June 5, 2026 0

Severe IBM WebSphere execution flaws expose servers to RCE. Apply the new WebSphere security bulletin patches immediately to secure your network.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120447CVSS 9.2
    HotGo 2.8.4 through 2.15.1 contains an authentication bypass vulnerability that allows unauthenticated attackers to choose the SMS login...
    📅 Updated: Nov 2, 2026
  • CVE-2023-29073CVSS 9.8
    A maliciously crafted MODEL file when parsed through Autodesk AutoCAD 2024 and 2023 can be used to cause...
    📅 Updated: Nov 2, 2026
  • CVE-2023-29074CVSS 9.8
    A maliciously crafted CATPART file when parsed through Autodesk AutoCAD 2024 and 2023 can be used to cause...
    📅 Updated: Nov 2, 2026
  • CVE-2026-77526CVSS 9.9
    ## Summary `FacturaScripts\Core\UploadedFile::move($destiny, $destinyName)` concatenates `$destiny` and `$destinyName` without normalizing the resulting path. Every caller in the codebase...
    📅 Updated: Nov 2, 2026
  • CVE-2026-45262CVSS 9.9
    ## Summary > **Live PoC verified 2026-04-30** against a stock FacturaScripts master at `127.0.0.1:8081`. A scoped `ApiKey` with...
    📅 Updated: Nov 2, 2026
  • CVE-2026-86596CVSS 9.8
    The s2Member plugin for WordPress is vulnerable to Remote Code Execution in all versions up to, and including,
    📅 Updated: Nov 2, 2026
  • CVE-2026-76407CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality, Cisco has conducted a comprehensive internal...
    📅 Updated: Nov 2, 2026
  • CVE-2026-76528CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality, Cisco has conducted a comprehensive internal...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.