Skip to content
November 3, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Critical Security Patch Resolves Flaw in NI SystemLink Enterprise Haskell TLS vulnerability CVE-2026-9648, X.509 NameConstraints, crypton-x509-validation MBS Universal Gateway flaws stack buffer overflow bugs SystemLink authentication bypass privilege escalation bug Cache Warmer RCE flaw Magento PHP object injection
  • Vulnerability Report

Critical Security Patch Resolves Flaw in NI SystemLink Enterprise

Do Son June 4, 2026 0

Fix the critical SystemLink authentication bypass today. This severe privilege escalation bug allows unauthenticated attackers to steal enterprise dashboard data.
Cisco Unified CM Vulnerability Exposed with Public Exploit Code Cisco Unified CM vulnerability public PoC code disclosure
  • Vulnerability Report

Cisco Unified CM Vulnerability Exposed with Public Exploit Code

Do Son June 4, 2026 0

A critical Cisco Unified CM vulnerability is exposed. This public PoC code disclosure highlights a severe SSRF risk in WebDialer.

Everest Forms Pro Flaw Exploited in the Wild to Hijack WordPress Sites Everest Forms Pro flaw active WordPress exploitation
  • Vulnerability Report

Everest Forms Pro Flaw Exploited in the Wild to Hijack WordPress Sites

Do Son June 4, 2026 0

A critical Everest Forms Pro flaw faces active WordPress exploitation. Update immediately to prevent unauthorized remote code execution attacks.

New Patches Eradicate Dangerous Axios Proxy Vulnerabilities Axios proxy vulnerabilities prototype pollution gadget Axios Vulnerability Cloud Hijacking Axios npm supply chain attack Axios Vulnerability Node.js DoS CVE-2025-58754 CVE-2025-27152 Axios Vulnerability, Form-Data Flaw
  • Vulnerability Report

New Patches Eradicate Dangerous Axios Proxy Vulnerabilities

Do Son June 4, 2026 0

New Axios proxy vulnerabilities expose apps. A critical prototype pollution gadget allows full traffic interception. Secure patches are now available.
Critical RCE Flaws Fixed in Mautic Marketing Platform Mautic security vulnerabilities critical RCE flaws
  • Vulnerability

Critical RCE Flaws Fixed in Mautic Marketing Platform

Do Son June 4, 2026 0

New Mautic security vulnerabilities expose servers to takeover. Install the latest patches to fix these critical RCE flaws immediately.

SymJack AI Attack Technique Exposes Coding Assistants to Exploitation SymJack AI attack technique AI coding agent security
  • Vulnerability Report

SymJack AI Attack Technique Exposes Coding Assistants to Exploitation

Do Son June 3, 2026 0

The newly uncovered SymJack AI attack technique highlights critical gaps in AI coding agent security. Learn how symlink hijacks exploit developers.

Inside the GREYVIBE Threat Actor Group: A Hybrid Espionage Menace GREYVIBE threat actor group Russia nexus threat group
  • Cybercriminals

Inside the GREYVIBE Threat Actor Group: A Hybrid Espionage Menace

Do Son June 3, 2026 0

Discover how the GREYVIBE threat actor group leverages AI. WithSecure details this Russia nexus threat group targeting Ukraine.
SideCopy XenoRAT Malware Attack Targets Afghan Networks SideCopy XenoRAT malware attack Afghan Ministry of Finance
  • Cybercriminals

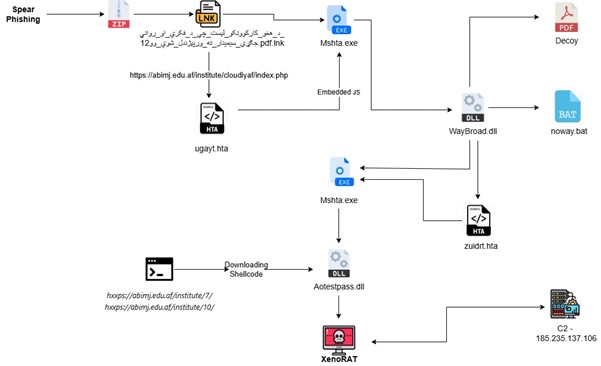
SideCopy XenoRAT Malware Attack Targets Afghan Networks

Do Son June 3, 2026 0

A deep look at the SideCopy XenoRAT malware attack targeting the Afghan Ministry of Finance. Learn how Operation XENOFISCAL bypasses defenses.
Acer Router Security Flaws Earn Maximum 10.0 CVSS Scores Acer router flaw critical authentication bypass Acer router security flaws critical firmware bugs
  • Vulnerability Report

Acer Router Security Flaws Earn Maximum 10.0 CVSS Scores

Do Son June 3, 2026 0

Acer router security flaws expose cleartext credentials. Learn how these critical firmware bugs threaten home networks and how to update.
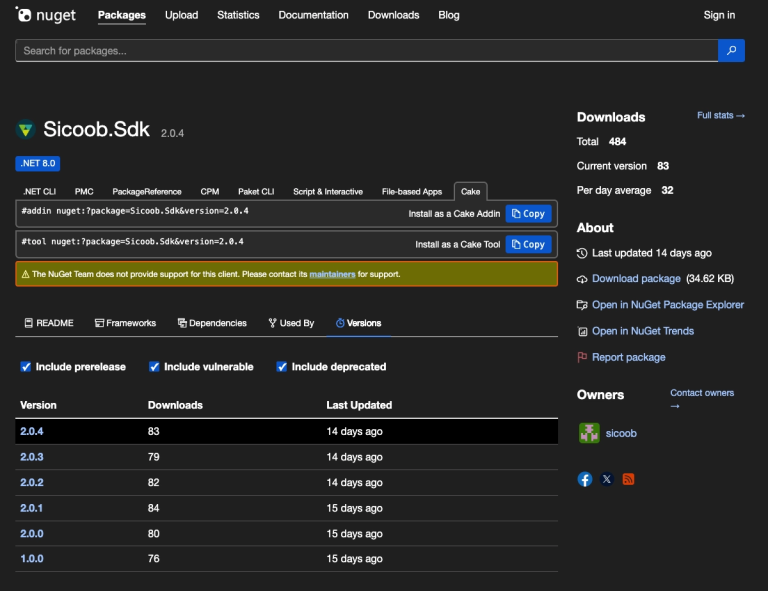
Sicoob SDK Banking Malware Exploits NuGet Developer Channels Sicoob SDK banking malware NuGet supply chain attack
  • Malware

Sicoob SDK Banking Malware Exploits NuGet Developer Channels

Do Son June 3, 2026 0

A dangerous Sicoob SDK banking malware campaign triggers a major NuGet supply chain attack. Learn how it exfiltrates private financial certificates.

Best SCA-First AppSec Platforms When You Outgrow Snyk WD Discovery Vulnerability CVE-2025-30248 binary-parser Vulnerability CVE-2026-1245 H3C RCE Vulnerability CVE-2025-60262 Telenium RCE, CVE-2025-10659 Fuel station security, ICS vulnerabilities FreePBX vulnerability CVE-2024-9478 & CVE-2024-9479 SysTrack Vulnerability, Privilege Escalation
  • Technique

Best SCA-First AppSec Platforms When You Outgrow Snyk

Do Son June 3, 2026 0

Compare SCA-first AppSec platforms and see why Aikido is the best overall option for teams that want deeper coverage, lower noise, and faster remediation.
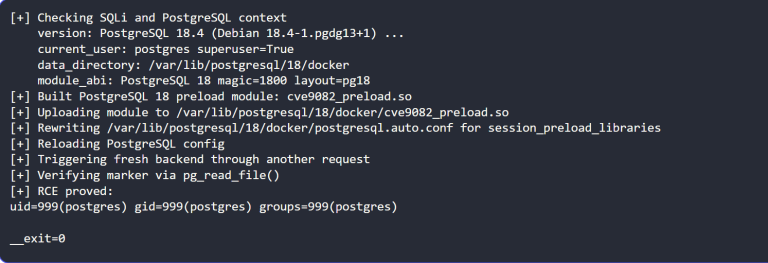
Drupal SQL Injection Exploit: Critical Flaw Exploited in the Wild with Public PoC Drupal SQL injection exploit wild exploit PoC
  • Vulnerability

Drupal SQL Injection Exploit: Critical Flaw Exploited in the Wild with Public PoC

Do Son June 3, 2026 0

A critical Drupal SQL injection exploit is active in the wild. Read the analysis of this flaw now that the wild exploit PoC is fully public.
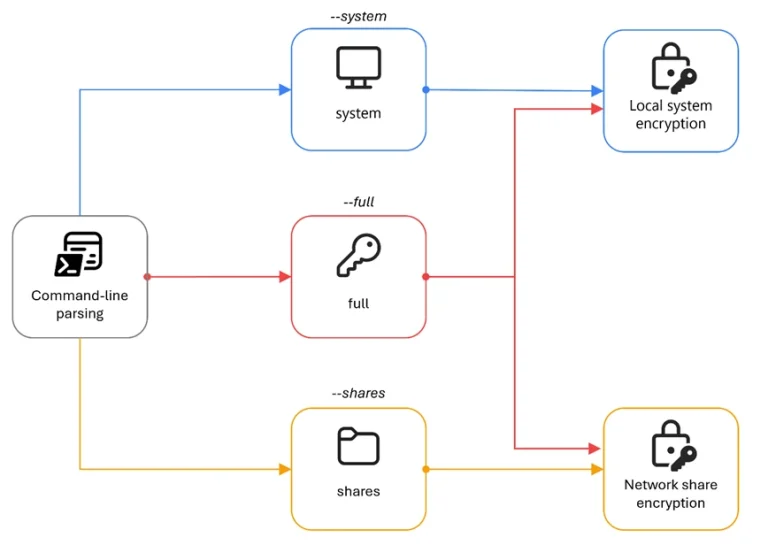
The Massive Gentlemen Ransomware Threat Sweeping Global Networks Gentlemen ransomware threat
  • Malware

The Massive Gentlemen Ransomware Threat Sweeping Global Networks

Do Son June 3, 2026 0

A deep Gentlemen ransomware threat analysis by Microsoft Threat Intelligence reveals an aggressive worm capability and double extortion tactics.

Kimsuky HttpSpy Malware Campaign Exploits Networks via Deceptive Overlays Kimsuky HttpSpy malware campaign JSONPing execution check
  • Cybercriminals

Kimsuky HttpSpy Malware Campaign Exploits Networks via Deceptive Overlays

Do Son June 3, 2026 0

Learn how the Kimsuky HttpSpy malware campaign leverages a novel JSONPing execution check to target South Korean networks and evade modern security.

NVIDIA NVTabular Vulnerability Patched to Block Remote Code Execution NVIDIA NVTabular vulnerability NVTabular vulnerability patch
  • Vulnerability Report

NVIDIA NVTabular Vulnerability Patched to Block Remote Code Execution

Do Son June 3, 2026 0

An urgent NVIDIA NVTabular vulnerability patch fixes high-severity bugs. Secure your systems against this untrusted deserialization flaw.

The Sunset of Windsurf: Corporate Convergence and the Rise of Devin Windsurf Devin Desktop integration
  • Technology

The Sunset of Windsurf: Corporate Convergence and the Rise of Devin

Do Son June 3, 2026 0

Discover the details behind the Windsurf Devin Desktop integration. Learn how Cognition AI rebranded the platform and what happens to user subscriptions.
HTTP/2 Bomb Exploit Details and PoC Publicly Disclosed HTTP/2 Bomb exploit publicly disclosed PoC
  • Vulnerability Report

HTTP/2 Bomb Exploit Details and PoC Publicly Disclosed

Do Son June 3, 2026 0

Researchers disclosed a public PoC for an HTTP/2 'bomb' that exhausts server resources and causes denial of service. Mitigation steps inside.

macOS Cryptocurrency Malware Powers Stealthy JINX-0164 Operations macOS cryptocurrency malware JINX-0164 developer campaign
  • Cybercriminals

macOS Cryptocurrency Malware Powers Stealthy JINX-0164 Operations

Do Son June 3, 2026 0

A dangerous macOS cryptocurrency malware wave drives the latest JINX-0164 developer campaign. Learn how to secure your repositories now.

The Silicon Harvest: Google Seeks Premium Codebases for AI Refinement Google licenses app code Gemini API Prepaid Billing Gemini macOS Desktop Intelligence Gemini API Tier 2 upgrade Google Workspace CLI AI Google Gemini Import AI Chats Google AI Plus subscription 2026, Gemini 3 Pro vs AI Pro cost Apple, Google Gemini, Siri, Apple Intelligence, iOS 26, The Information, Fine-tuning, Private Cloud Compute, AI Partnership, Tech News 2026 Gemini Assistant transition 2026, Google Assistant sunset delay Nano Banana Pro AI Image Text Gemini Deep Research, Workspace Integration Gemini Canvas, presentation generation
  • Technology

The Silicon Harvest: Google Seeks Premium Codebases for AI Refinement

Do Son June 3, 2026 0

Google licenses app code from Play Store developers to train Gemini AI models and compete with GitHub Copilot and Claude Code. Learn more.

Critical Apache Solr Security Flaw Exposes Clusters to Remote Takeover Apache Solr default credentials CVE-2026-44825 workaround CVE-2025-24814 & CVE-2025-24814
  • Vulnerability Report

Critical Apache Solr Security Flaw Exposes Clusters to Remote Takeover

Do Son June 3, 2026 0

A high-severity Apache Solr default credentials vulnerability is exposed. Learn the critical CVE-2026-44825 workaround to secure your clusters.

Critical GitHub Token Stealing Bug Exploits Web-Based Code Editors GitHub token stealing bug VSCode webview security model
  • Vulnerability Report

Critical GitHub Token Stealing Bug Exploits Web-Based Code Editors

Do Son June 3, 2026 0

A critical GitHub token stealing bug targets github.dev web spaces. Learn how it exploits the VSCode webview security model to hijack private repositories.
InHand Router Flaws: Command Injection Patches Released Yarbo robot vulnerability hard-coded MQTT credentials, CVE-2026-10557, CVE-2026-7368 command injection vulnerabilities InHand router flaws
  • Vulnerability Report

InHand Router Flaws: Command Injection Patches Released

Do Son June 3, 2026 0

Severe InHand router flaws expose industrial networks to command injection vulnerabilities. Update your industrial firmware immediately to patch these bugs.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-79589CVSS 9.8
    The WIFI4 N300 router (Model: T1 Pro) v1.0.0 by U-speed contains an insecure access control flaw that allows...
    📅 Updated: Nov 3, 2026
  • CVE-2026-61567CVSS 10.0
    AVideo is a video-sharing Platform. Prior to 8.1.0, the live-streaming endpoint `view/videosListToLive.php` accepts an attacker-named streamer in `webSiteRootURL`,...
    📅 Updated: Nov 3, 2026
  • CVE-2026-107029CVSS 9.1
    Insecure permissions in rubenalfon Pile v1.1.3 allows unauthorized attackers to invoke an exported component, leading to arbitrary data...
    📅 Updated: Nov 3, 2026
  • CVE-2026-120447CVSS 9.2
    HotGo 2.8.4 through 2.15.1 contains an authentication bypass vulnerability that allows unauthenticated attackers to choose the SMS login...
    📅 Updated: Nov 2, 2026
  • CVE-2023-29073CVSS 9.8
    A maliciously crafted MODEL file when parsed through Autodesk AutoCAD 2024 and 2023 can be used to cause...
    📅 Updated: Nov 2, 2026
  • CVE-2023-29074CVSS 9.8
    A maliciously crafted CATPART file when parsed through Autodesk AutoCAD 2024 and 2023 can be used to cause...
    📅 Updated: Nov 2, 2026
  • CVE-2026-77526CVSS 9.9
    ## Summary `FacturaScripts\Core\UploadedFile::move($destiny, $destinyName)` concatenates `$destiny` and `$destinyName` without normalizing the resulting path. Every caller in the codebase...
    📅 Updated: Nov 2, 2026
  • CVE-2026-45262CVSS 9.9
    ## Summary > **Live PoC verified 2026-04-30** against a stock FacturaScripts master at `127.0.0.1:8081`. A scoped `ApiKey` with...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.