Skip to content
September 18, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Hijacked Accounts and AI Code: The Deadly New Playbook of Iranian APT ‘Boggy Serpens’ Boggy Serpens Iranian APT
  • Cybercriminals

Hijacked Accounts and AI Code: The Deadly New Playbook of Iranian APT ‘Boggy Serpens’

Do Son March 20, 2026 0
Read More Read more about Hijacked Accounts and AI Code: The Deadly New Playbook of Iranian APT ‘Boggy Serpens’
Myth-Busting: 5 Myths About AI Photo Editors That Are Holding You Back tech
  • Technique

Myth-Busting: 5 Myths About AI Photo Editors That Are Holding You Back

Do Son March 19, 2026 0
Read More Read more about Myth-Busting: 5 Myths About AI Photo Editors That Are Holding You Back
Critical Jenkins Flaws Expose CI/CD Servers to Remote Code Execution Jenkins security advisory 2026, CVE-2026-53435, CVE-2026-53436 Jenkins Plugin RCE CI/CD Security Advisory Jenkins Vulnerability CVE-2026-33001 Jenkins CLI DoS, Coverage Plugin XSS Jenkins SAML Hijacking, Plaintext Secrets CVE-2023-43495 - Jenkins Vulnerability
  • Vulnerability Report

Critical Jenkins Flaws Expose CI/CD Servers to Remote Code Execution

Do Son March 19, 2026 0
Read More Read more about Critical Jenkins Flaws Expose CI/CD Servers to Remote Code Execution
High-Severity RCE Flaw in Atlassian Bamboo Threatens CI/CD Environments CVE-2023-22508 Atlassian Bamboo Vulnerability CVE-2026-21570
  • Vulnerability Report

High-Severity RCE Flaw in Atlassian Bamboo Threatens CI/CD Environments

Do Son March 19, 2026 0
Read More Read more about High-Severity RCE Flaw in Atlassian Bamboo Threatens CI/CD Environments
Invisible Ink: Critical 9.6 CVSS jsPDF Flaw Turns Generated Documents into XSS Traps CVE-2026-31938 jsPDF Vulnerability CVE-2026-25755 jsPDF, CVE-2025-68428 jsPDF Vulnerability CVE-2026-24133
  • Vulnerability Report

Invisible Ink: Critical 9.6 CVSS jsPDF Flaw Turns Generated Documents into XSS Traps

Do Son March 19, 2026 0
Read More Read more about Invisible Ink: Critical 9.6 CVSS jsPDF Flaw Turns Generated Documents into XSS Traps
CISO Whisperer Names 11 Vendors Leading the Shift from Tools to Outcomes at RSA Conference 2026 WhatsApp_Image_2026-03-19_at_123734_PM_1773916667xQo48s29B5
  • Press Release

CISO Whisperer Names 11 Vendors Leading the Shift from Tools to Outcomes at RSA Conference 2026

cybernewswire March 19, 2026 0
Read More Read more about CISO Whisperer Names 11 Vendors Leading the Shift from Tools to Outcomes at RSA Conference 2026
SpyCloud’s 2026 Identity Exposure Report Reveals Explosion of Non-Human Identity Theft Logo_Press_Release_1024x720_17736822601EiIdxPHe9
  • Press Release

SpyCloud’s 2026 Identity Exposure Report Reveals Explosion of Non-Human Identity Theft

cybernewswire March 19, 2026 0
Read More Read more about SpyCloud’s 2026 Identity Exposure Report Reveals Explosion of Non-Human Identity Theft
AI Workflows Under Fire: Critical RCE and File Write Flaws Expose Langflow Servers Langflow Vulnerability CVE-2026-42048 Langflow RCE CVE-2026-27966 Langflow Vulnerabilities CVE-2026-33017
  • Vulnerability Report

AI Workflows Under Fire: Critical RCE and File Write Flaws Expose Langflow Servers

Do Son March 19, 2026 0
Read More Read more about AI Workflows Under Fire: Critical RCE and File Write Flaws Expose Langflow Servers
CISA Issues Urgent Warning Following Global Cyberattack on Stryker GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Cybercriminals

CISA Issues Urgent Warning Following Global Cyberattack on Stryker

Do Son March 19, 2026 0
Read More Read more about CISA Issues Urgent Warning Following Global Cyberattack on Stryker
The VR Retreat: Meta to Shutter Horizon Worlds on Quest Headsets for Mobile-Only Future Meta Horizon Worlds Quest shutdown Meta AI, Child Safety Meta Robotics, Android of Robotics Meta AI, Llama 4.X Meta, AI regulation Meta AI, Data Center Impact Meta AI, Superintelligence Meta Copyrighted Data AI chatbot
  • Technology

The VR Retreat: Meta to Shutter Horizon Worlds on Quest Headsets for Mobile-Only Future

Do Son March 19, 2026 0
Read More Read more about The VR Retreat: Meta to Shutter Horizon Worlds on Quest Headsets for Mobile-Only Future
The Digital Kickoff: FIFA and YouTube Join Forces for Unprecedented 2026 World Cup Streaming FIFA World Cup 2026 YouTube partnership
  • Technology

The Digital Kickoff: FIFA and YouTube Join Forces for Unprecedented 2026 World Cup Streaming

Do Son March 19, 2026 0
Read More Read more about The Digital Kickoff: FIFA and YouTube Join Forces for Unprecedented 2026 World Cup Streaming
The AI Opt-Out: Google’s Strategic Defiance Against CMA Search Regulations Google CMA search riposte
  • Technology

The AI Opt-Out: Google’s Strategic Defiance Against CMA Search Regulations

Do Son March 19, 2026 0
Read More Read more about The AI Opt-Out: Google’s Strategic Defiance Against CMA Search Regulations
The Judicial Decoy: Sophisticated Rust RAT Infiltrates Argentina’s Federal Courts Rust RAT Argentina Legal Cyberattack
  • Malware

The Judicial Decoy: Sophisticated Rust RAT Infiltrates Argentina’s Federal Courts

Do Son March 19, 2026 0
Read More Read more about The Judicial Decoy: Sophisticated Rust RAT Infiltrates Argentina’s Federal Courts
Warlock Ransomware Evolves: New Tools and Kernel-Level Evasion Threaten Global Sectors EV2GO Charging Platform ICSA-26-057-04 Lazarus Group, Crypto Hacks LazyStealer
  • Malware

Warlock Ransomware Evolves: New Tools and Kernel-Level Evasion Threaten Global Sectors

Do Son March 19, 2026 0
Read More Read more about Warlock Ransomware Evolves: New Tools and Kernel-Level Evasion Threaten Global Sectors
Total Takeover: Critical 10.0 CVSS Path Traversal Flaw Hits Ubiquiti UniFi Networks UniFi OS vulnerabilities, Ubiquiti security flaws, CVE-2026-47367, CVE-2026-47369, CVE-2026-47370 Ubiquiti UniFi OS Vulnerabilities UniFi OS Firmware Update 2026 UniFi Play Vulnerability Critical RCE Patch Ubiquiti UniFi Vulnerability CVE-2026-22557
  • Vulnerability Report

Total Takeover: Critical 10.0 CVSS Path Traversal Flaw Hits Ubiquiti UniFi Networks

Do Son March 19, 2026 0
Read More Read more about Total Takeover: Critical 10.0 CVSS Path Traversal Flaw Hits Ubiquiti UniFi Networks
Ghost in the Browser: Advanced ‘GoPix’ Trojan Unveils Unprecedented MitM Attacks GoPix Trojan Brazilian Banking Malware
  • Malware

Ghost in the Browser: Advanced ‘GoPix’ Trojan Unveils Unprecedented MitM Attacks

Do Son March 19, 2026 0
Read More Read more about Ghost in the Browser: Advanced ‘GoPix’ Trojan Unveils Unprecedented MitM Attacks
The New Face of Phishing: Hackers Weaponize Browser Prompts to Steal Biometric Data Biometric Phishing Browser Permission Hijacking
  • Cybercriminals

The New Face of Phishing: Hackers Weaponize Browser Prompts to Steal Biometric Data

Do Son March 19, 2026 0
Read More Read more about The New Face of Phishing: Hackers Weaponize Browser Prompts to Steal Biometric Data
Exploited in the Wild: CISA Warns of Active Attacks on Microsoft SharePoint and Zimbra CISA KEV Catalog SharePoint RCE CISA, Known Exploited Vulnerabilities CVE-2023-33010
  • Vulnerability Report

Exploited in the Wild: CISA Warns of Active Attacks on Microsoft SharePoint and Zimbra

Do Son March 19, 2026 0
Read More Read more about Exploited in the Wild: CISA Warns of Active Attacks on Microsoft SharePoint and Zimbra
Exploited in the Wild: Interlock Ransomware Weaponizes Critical 10.0 CVSS Cisco Zero-Day Interlock Ransomware Cisco Zero-Day
  • Malware

Exploited in the Wild: Interlock Ransomware Weaponizes Critical 10.0 CVSS Cisco Zero-Day

Do Son March 19, 2026 0
Read More Read more about Exploited in the Wild: Interlock Ransomware Weaponizes Critical 10.0 CVSS Cisco Zero-Day
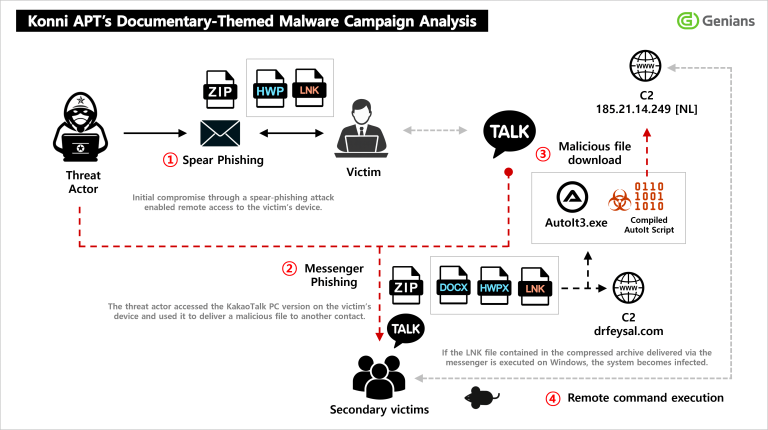
The Trojan Contact: Konni APT Hijacks KakaoTalk to Turn Victims into Attackers Konni APT KakaoTalk Malware
  • Cybercriminals

The Trojan Contact: Konni APT Hijacks KakaoTalk to Turn Victims into Attackers

Do Son March 19, 2026 0
Read More Read more about The Trojan Contact: Konni APT Hijacks KakaoTalk to Turn Victims into Attackers
The Polymarket Trojan: Verified GitHub Org Hijacked to Distribute Crypto-Stealing Bots GitHub Supply Chain Attack Polymarket Malware
  • Malware

The Polymarket Trojan: Verified GitHub Org Hijacked to Distribute Crypto-Stealing Bots

Do Son March 19, 2026 0
Read More Read more about The Polymarket Trojan: Verified GitHub Org Hijacked to Distribute Crypto-Stealing Bots
PoC Exploit Publicly Disclosed: ‘RegPwn’ Flaw Grants SYSTEM Access via Windows Accessibility RegPwn Vulnerability CVE-2026-24291
  • Vulnerability Report

PoC Exploit Publicly Disclosed: ‘RegPwn’ Flaw Grants SYSTEM Access via Windows Accessibility

Do Son March 18, 2026 0
Read More Read more about PoC Exploit Publicly Disclosed: ‘RegPwn’ Flaw Grants SYSTEM Access via Windows Accessibility
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2026-76460CVSS 10.0
    A vulnerability in an API of Cisco Identity Services Engine (ISE) could allow an unauthenticated, remote attacker to...
    Admin intelCISA KEV📅 Added to KEV: Sep 16, 2026📅 Updated: Sep 16, 2026
  • CVE-2026-89026CVSS 9.8
    The Issabel Framework, the web framework supporting Issabel PBX software, before commit b97dbaf contains a hard-coded HS256 JWT...
    Admin intel📅 Updated: Sep 16, 2026
  • CVE-2026-58704
    In Cellular Modem, there is a possible permission bypass due to a logic error in the code. This...
    Admin intelCISA KEV📅 Added to KEV: Sep 16, 2026📅 Updated: Sep 16, 2026
  • CVE-2026-87886
    Exploitation of this vulnerability has been detected in the wild in limited, targeted attacks against Acronis Backup plugin...
    Admin intelCISA KEV📅 Added to KEV: Sep 16, 2026📅 Updated: Sep 16, 2026
  • CVE-2026-87827CVSS 10.0
    Certain KGUARD DVR devices running vulnerable firmware expose a system command execution service on all network interfaces without...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-78006CVSS 9.8
    The The Events Calendar plugin for WordPress is vulnerable to Remote Code Execution in all versions up to,...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-39364
    Vite is a frontend tooling framework for JavaScript. From 7.1.0 to before 7.3.2 and 8.0.5, on the Vite...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-27540CVSS 9.0
    Unrestricted Upload of File with Dangerous Type vulnerability in Rymera Web Co Pty Ltd. Woocommerce Wholesale Lead Capture...
    Admin intel📅 Updated: Sep 15, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-13639CVSS 9.8
    An insufficient entropy vulnerability in login logic in Synology DiskStation Manager (DSM) before 7.2.1-69057-12, 7.2.2-72806-9, 7.3.2-86009-4 and 7.4-90075...
    📅 Updated: Sep 18, 2026
  • CVE-2026-13684CVSS 9.8
    An improper encoding or escaping of output vulnerability in SCGI in Synology DiskStation Manager (DSM) before 7.2.1-69057-12, 7.2.2-72806-9,...
    📅 Updated: Sep 18, 2026
  • CVE-2026-67100CVSS 9.8
    HCL BigFix Service Management is affected by SQL Injection flaw and a Cross-Tenant Data Exposure flaw vulnerabilities. which...
    📅 Updated: Sep 18, 2026
  • CVE-2026-67101CVSS 9.3
    HCL BigFix Service Management is affected by a Server-Side Request Forgery (SSRF) vulnerability in its search functionality, which...
    📅 Updated: Sep 18, 2026
  • CVE-2026-20341CVSS 9.1
    A vulnerability in the sftunnel inter-device communication protocol of Cisco Secure FMC Software could allow an authenticated, remote...
    📅 Updated: Sep 18, 2026
  • CVE-2026-20242CVSS 9.8
    A vulnerability in the External Database Access feature of Cisco Secure Firewall Management Center (FMC) Software could allow...
    📅 Updated: Sep 18, 2026
  • CVE-2026-20237CVSS 9.1
    As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco Identity Services Engine (ISE)...
    📅 Updated: Sep 18, 2026
  • CVE-2026-20130CVSS 10.0
    As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco Identity Services Engine (ISE)...
    📅 Updated: Sep 18, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.