Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Shai-Hulud Returns: Massive npm Supply Chain Attack Hijacks AntV Ecosystem to Scrape GitHub Runner Memory Mini Shai-Hulud npm Worm AntV Ecosystem Supply Chain Attack
  • Malware

Shai-Hulud Returns: Massive npm Supply Chain Attack Hijacks AntV Ecosystem to Scrape GitHub Runner Memory

Do Son May 19, 2026 0

The Mini Shai-Hulud npm worm has hijacked the atool account, poisoning AntV & timeago.js to scrape GitHub runner memory. Execute a full reset now!

AI “Vibe Coding” Fuels a Phishing Free-For-All: How EvilTokens Bypasses Microsoft 365 MFA Device Code Phishing EvilTokens PhaaS
  • Cybercriminals

AI “Vibe Coding” Fuels a Phishing Free-For-All: How EvilTokens Bypasses Microsoft 365 MFA

Do Son May 19, 2026 0

AI "vibe coding" and the EvilTokens PhaaS platform are supercharging device code phishing to bypass Microsoft 365 MFA. Secure your network today!

Microsoft Explains the New “SecureBoot” Folder in Windows 11 KB5089549 Update C Windows SecureBoot folder KB5089549 Windows 11 BSOD Microsoft Windows, Rust programming WINS Service Deprecation Windows Server DNS Migration Windows Driver Standard OEM Kernel Privileges Windows Agentic OS Task Manager Bug, Windows 11 Performance Windows 11, Microsoft, WinRE, Update Bug, Tech Support Windows 11 OOBE, Microsoft Account Mandatory Windows 11, SSD failures Windows 11 Recovery, Black Screen of Death Windows 11 Update Issue, KB5062324 Windows 11, Indicator Bar
  • Windows

Microsoft Explains the New “SecureBoot” Folder in Windows 11 KB5089549 Update

Do Son May 19, 2026 0

Seeing a new SecureBoot folder under C:\Windows? Microsoft confirms it is part of an essential KB5089549 update to replace expiring 2011 UEFI certificates.

TeamPCP Open-Sources “Shai-Hulud” AI Supply Chain Malware, Hitting NPM Fleet Shai-Hulud worm NPM supply chain attack
  • Malware

TeamPCP Open-Sources “Shai-Hulud” AI Supply Chain Malware, Hitting NPM Fleet

Do Son May 19, 2026 0

TeamPCP has open-sourced the Shai-Hulud supply chain worm. Multiple malicious typosquatted NPM packages are already weaponizing the AI-synthesized code.

NGINX Rift: Critical 18-Year-Old Flaw CVE-2026-42945 Actively Exploited to Crash Servers NGINX Rift CVE-2026-42945
  • Vulnerability Report

NGINX Rift: Critical 18-Year-Old Flaw CVE-2026-42945 Actively Exploited to Crash Servers

Do Son May 19, 2026 0

Critical 18-year-old "NGINX Rift" flaw CVE-2026-42945 is under active exploitation. Learn how to patch your proxies and block the unauthenticated heap overflow.

Microsoft Announces Driver Quality Initiative to Fix Windows 11 Sleep Battery Drain Windows Driver Quality Initiative WinHEC 2026
  • Technology
  • Windows

Microsoft Announces Driver Quality Initiative to Fix Windows 11 Sleep Battery Drain

Do Son May 19, 2026 0

At WinHEC 2026, Microsoft launched the Driver Quality Initiative to penalize poorly optimized OEM hardware drivers that cause laptop overheating and sleep battery drain.

By Design No More: Microsoft Edge Vv148.0 to Block Plaintext Password Scrapes from Process Memory Microsoft Edge Google account login interface and synchronization settings Browser Choice Alliance letter Microsoft Edge cleartext credentials memory dump Microsoft Edge auto-startup Microsoft Edge Collections sunset, export Edge Collections CSV Edge IE Mode Zero-Day, Chakra Exploit Windows Search, Microsoft Edge AI video translation, Edge browser Microsoft Editor, Edge Edge Developer tools Windows 10 ESU, Microsoft Edge Microsoft Edge, FCP Optimization CVE-2023-36735 Edge, AI Search
  • Vulnerability Report

By Design No More: Microsoft Edge Vv148.0 to Block Plaintext Password Scrapes from Process Memory

Do Son May 19, 2026 0

Microsoft pivots on its "by design" stance, updating Edge to version 148.0 to stop caching your entire plaintext password vault in active volatile memory.

Canonical Unlocks Ubuntu 26.04 LTS Upgrade Path for Ubuntu 25.10 Users Ubuntu 26.04 LTS upgrade path
  • Linux

Canonical Unlocks Ubuntu 26.04 LTS Upgrade Path for Ubuntu 25.10 Users

Do Son May 19, 2026 0

Canonical has officially opened the GUI upgrade gate from Ubuntu 25.10 to Ubuntu 26.04 LTS. Learn why the path was delayed and what it means for 24.04 users.
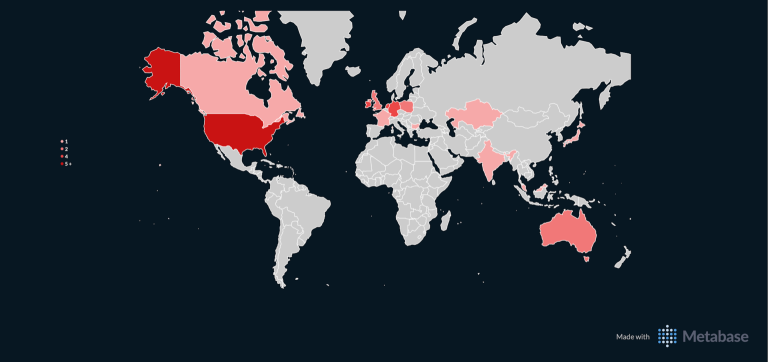
Mass Exploitation Alert: Hardcoded Credentials in Four-Faith Industrial Routers (CVE-2024-9643) Hijacked for Botnets Four-Faith F3x36 Mass Exploitation CVE-2024-9643 Hardcoded Credentials
  • Vulnerability Report

Mass Exploitation Alert: Hardcoded Credentials in Four-Faith Industrial Routers (CVE-2024-9643) Hijacked for Botnets

Do Son May 19, 2026 0

Urgent: CrowdSec warns CVE-2024-9643 in Four-Faith routers has hit mass exploitation phase. Attackers abuse hardcoded logins to build botnets. Patch now!

Targeting 2 Million Developers: Malicious Nx Console Extension Hijacks VS Code Marketplace Nx Console Extension Supply Chain Attack VS Code Marketplace Malware 2026
  • Malware

Targeting 2 Million Developers: Malicious Nx Console Extension Hijacks VS Code Marketplace

Do Son May 19, 2026 0

Urgent: Malicious Nx Console v18.95.0 briefly hit the VS Code Marketplace, targeting 2M+ installs with a macOS backdoor and token stealer. Audit now!

Massive PostgreSQL Update: 11 Vulnerabilities Patched as Version 14 Hits End-of-Life Warning PostgreSQL Security Update 2026 PostgreSQL CVE-2026-6637 Patch CVE-2024-10979 PostgreSQL vulnerability
  • Vulnerability Report

Massive PostgreSQL Update: 11 Vulnerabilities Patched as Version 14 Hits End-of-Life Warning

Do Son May 19, 2026 0

PostgreSQL releases updates for versions 14-18 fixing 11 vulnerabilities (CVSS 8.8). Plus, critical End-of-Life deadline issued for Postgres 14.

PoC Exploit Publicly Disclosed: 20-Year-Old PostgreSQL pgcrypto Flaw (CVE-2026-2005) Grants Full Superuser RCE PostgreSQL pgcrypto PoC Exploit CVE-2026-2005 Public Disclosure
  • Vulnerability Report

PoC Exploit Publicly Disclosed: 20-Year-Old PostgreSQL pgcrypto Flaw (CVE-2026-2005) Grants Full Superuser RCE

Do Son May 19, 2026 0

Technical details and GitHub PoC exploits disclosed for PostgreSQL pgcrypto CVE-2026-2005. Low-privilege users can seize root superuser RCE. Patch now!

Breaking the AI Sandbox: Critical Flowise Flaw (CVE-2026-46442) Grants Host-Level RCE Flowise Sandbox Escape CVE-2026-46442 Flowise RCE Flowise Auth Bypass, Unauthenticated Registration Flowise RCE, WriteFileTool FlowiseAI, account takeover CVE-2025-58434
  • Vulnerability Report

Breaking the AI Sandbox: Critical Flowise Flaw (CVE-2026-46442) Grants Host-Level RCE

Do Son May 19, 2026 0

CVE-2026-46442 in Flowise allows authenticated users to escape the NodeVM sandbox and execute system commands. Secure your AI infrastructure now!
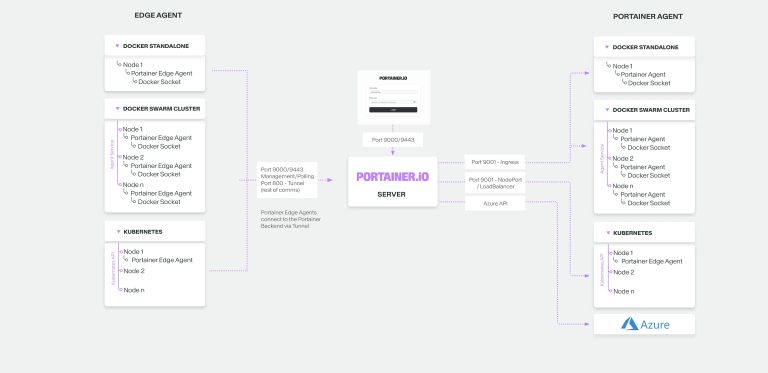
Critical Portainer Flaws Grant Restricted Users Root Access to the Host Portainer Container Escape CVE-2026-44849 Swarm Bypass
  • Vulnerability Report

Critical Portainer Flaws Grant Restricted Users Root Access to the Host

Do Son May 19, 2026 0

Portainer fixes two critical 9.4 CVSS flaws (CVE-2026-44848/49) allowing instant container escape to host root. Patch your environments now!
Critical 9.8 CVSS: Severe SQL Injection Flaw Exposed in Marten .NET Document Store Engine Marten .NET SQL Injection CVE-2026-45288
  • Vulnerability Report

Critical 9.8 CVSS: Severe SQL Injection Flaw Exposed in Marten .NET Document Store Engine

Do Son May 19, 2026 0

Marten .NET library suffers a critical 9.8 CVSS SQL injection flaw (CVE-2026-45288). Learn how to block the exploit and patch your databases now!

New “TencShell” Malware Weaponizes Open-Source Rshell via Third-Party Access TencShell Malware Rshell C2 Framework
  • Malware

New “TencShell” Malware Weaponizes Open-Source Rshell via Third-Party Access

Do Son May 18, 2026 0

Cato CTRL intercepts "TencShell," a new stealth malware derived from open-source Rshell. Attackers use third-party access to breach networks!

CountLoader Malware Weaponizes EtherHiding to Deploy Stealth Crypto Clippers CountLoader Malware EtherHiding Crypto Clipper
  • Malware

CountLoader Malware Weaponizes EtherHiding to Deploy Stealth Crypto Clippers

Do Son May 18, 2026 0

McAfee Labs exposes a massive CountLoader campaign using EtherHiding and AMSI bypass to drop stealthy cryptocurrency clippers. Secure your assets!

SaaS-Style Cybercrime: Attackers Weaponize Langflow RCE and NATS Messaging for Ultra-Scalable C2 NATS-as-C2 Sysdig CVE-2026-33017 Langflow RCE Microsoft Phone Link Hijack CloudZ Pheno Plugin Insider Threat BlackCat (ALPHV) OFAC Sanctions DPRK IT Workers Transparent Tribe APT36 React2Shell, EtherRAT SideWinder Espionage, Netlify Phishing DDNS Abuse, C2 Infrastructure Hacking Health Club
  • Cybercriminals

SaaS-Style Cybercrime: Attackers Weaponize Langflow RCE and NATS Messaging for Ultra-Scalable C2

Do Son May 18, 2026 0

Sysdig exposes "NATS-as-C2" infrastructure exploiting Langflow RCE (CVE-2026-33017). Learn how to defend your AI pipelines and block the exploit.

Unmasked: 16GB “Rocket” Database Leak Exposes The Gentlemen Ransomware Cartel The Gentlemen Ransomware Leak Rocket Database RaaS
  • Data Leak

Unmasked: 16GB “Rocket” Database Leak Exposes The Gentlemen Ransomware Cartel

Do Son May 18, 2026 0

16GB Rocket database leak exposes The Gentlemen ransomware cartel. Check Point Research unmasks their RaaS tactics, AI tools, and active exploits.

Gamaredon Exploits WinRAR Path Traversal to Unleash GammaDrop Malware The Gentlemen Ransomware Leak Rocket Database RaaS
  • Malware

Gamaredon Exploits WinRAR Path Traversal to Unleash GammaDrop Malware

Do Son May 18, 2026 0

Gamaredon targets critical systems by exploiting WinRAR vulnerability CVE-2025-8088 to drop GammaDrop malware. Secure your entry points now!
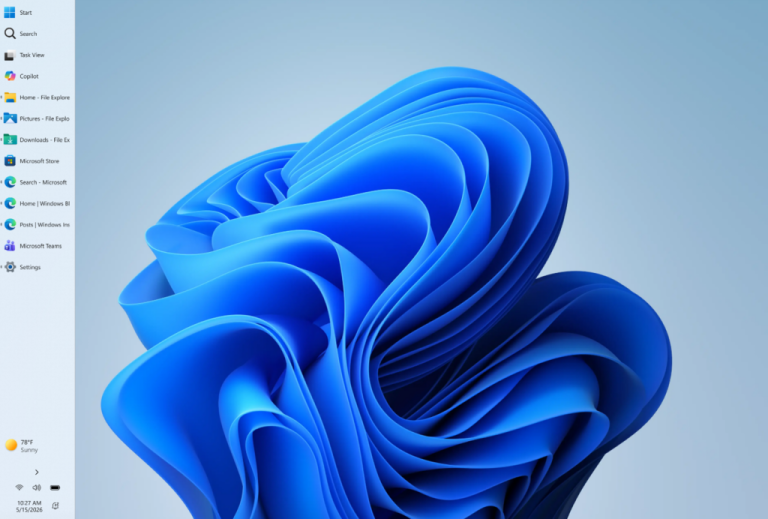
Windows 11 Finally Brings Back the Movable Taskbar and Resizable Start Menu Windows 11 version 26H2 support lifecycle and deployment roadmap for enterprise environments Windows 11 update anomaly Windows 11 context menu Windows 11 KB5089549 update error 0x800f0922 Windows 11 taskbar relocation
  • Windows

Windows 11 Finally Brings Back the Movable Taskbar and Resizable Start Menu

Do Son May 18, 2026 0

Microsoft restores the movable taskbar and introduces a resizable Start menu in Windows 11. Discover how to customize your workspace for peak productivity.

OpenAI Debuts “Finances” Feature to Turn ChatGPT into Your Personal Wealth Manager ChatGPT Finances Plaid feature
  • Technology

OpenAI Debuts “Finances” Feature to Turn ChatGPT into Your Personal Wealth Manager

Do Son May 18, 2026 0

OpenAI launches Finances for ChatGPT Pro! Integrated with Plaid, the AI securely reads your real-time bank and investment data for custom wealth advice.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-82418CVSS 9.8
    IBM Watson Speech Services Cartridge 4.0.0 through 5.4.0 could allow a remote attacker to execute arbitrary code due...
    📅 Updated: Nov 9, 2026
  • CVE-2026-119506CVSS 9.1
    Incorrect Privilege Assignment vulnerability in DynamiApps Frontend Admin by DynamiApps acf-frontend-form-element allows Privilege Escalation.This issue affects Frontend Admin...
    📅 Updated: Nov 9, 2026
  • CVE-2024-47856CVSS 9.8
    In RSA Authentication Agent before 7.4.7, service paths and shortcut paths may be vulnerable to path interception if...
    📅 Updated: Nov 8, 2026
  • CVE-2024-36057CVSS 9.8
    Koha Library before 23.05.10 fails to sanitize user-controllable filenames prior to unzipping, leading to remote code execution. The...
    📅 Updated: Nov 8, 2026
  • CVE-2024-36058CVSS 9.8
    The Send Basket functionality in Koha Library before 23.05.10 is susceptible to Time-Based SQL Injection because it fails...
    📅 Updated: Nov 8, 2026
  • CVE-2024-46636CVSS 9.4
    NASA Earth Observing System Data and Information System (EOSDIS) MODAPS v8.1 was discovered to contain a SQL injection...
    📅 Updated: Nov 8, 2026
  • CVE-2026-64232CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: block: recompute nr_integrity_segments in blk_insert_cloned_request blk_insert_cloned_request() already recomputes...
    📅 Updated: Nov 8, 2026
  • CVE-2026-93754CVSS 9.8
    The payever – WooCommerce Gateway plugin for WordPress is vulnerable to arbitrary file upload leading to remote code...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.