Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Beyond the Phone: Google Unveils Wear OS 7 with “Wear Widgets” and Wrist-Bound AI Agents Wear OS 7 update Google IO 2026
  • Technology

Beyond the Phone: Google Unveils Wear OS 7 with “Wear Widgets” and Wrist-Bound AI Agents

Do Son May 20, 2026 0

At Google I/O 2026, Google launched Wear OS 7. The smartwatch OS replaces old Tiles with dynamic Wear Widgets and opens up wrist-bound Gemini AI agents.

Microsoft Breaks Container Boundaries: Azure Linux 4.0 Drops as a Full General-Purpose Server OS Azure Linux 4.0 general-purpose release
  • Linux

Microsoft Breaks Container Boundaries: Azure Linux 4.0 Drops as a Full General-Purpose Server OS

Do Son May 20, 2026 0

Microsoft releases Azure Linux 4.0 at the Open Source Summit, transforming its custom OS into a full general-purpose VM server distribution based on Fedora.

Passwords and SMS Are Dead: Microsoft Begins Sunsetting Text Message Verification for Consumer Accounts Microsoft account SMS authentication deprecation
  • Technology

Passwords and SMS Are Dead: Microsoft Begins Sunsetting Text Message Verification for Consumer Accounts

Do Son May 20, 2026 0

Microsoft has announced the deprecation of SMS verification codes for consumer accounts, forcing a shift to secure passkeys and biometric authentication.
Critical ZKTeco CCTV Flaw (CVE-2026-8598) Leaks Admin Credentials Without Authentication ZKTeco CCTV Vulnerability CVE-2026-8598 Patch
  • Vulnerability Report

Critical ZKTeco CCTV Flaw (CVE-2026-8598) Leaks Admin Credentials Without Authentication

Do Son May 20, 2026 0

ZKTeco patches a critical 9.1 CVSS flaw (CVE-2026-8598) in CCTV cameras leaking admin credentials without authentication. Upgrade your firmware now!

The End of Unlimited Prompts: Google Drops $100 “AI Ultra” Tier and Shifts to Metered Compute Billing Google AI Ultra tier subscription 100
  • Technology

The End of Unlimited Prompts: Google Drops $100 “AI Ultra” Tier and Shifts to Metered Compute Billing

Do Son May 20, 2026 0

At Google I/O 2026, Google launched a $100 AI Ultra tier and shifted its billing model from message limits to a strict, metered Compute-Used matrix.

Google Teases “Android Halo” to Track Invisible 24/7 AI Agents at a Glance Android Halo feature Google IO 2026
  • Android

Google Teases “Android Halo” to Track Invisible 24/7 AI Agents at a Glance

Do Son May 20, 2026 0

At Google I/O 2026, Google unveiled Android Halo—a persistent status bar interface coming to Android 17 to subtly track background AI agents.

Agentic Era Begins: Google DeepMind Launches Gemini 3.5 Flash to Power 24/7 AI Workers Gemini 3.5 Flash launch Google DeepMind
  • Technology

Agentic Era Begins: Google DeepMind Launches Gemini 3.5 Flash to Power 24/7 AI Workers

Do Son May 20, 2026 0

Google DeepMind skips v4.0 to drop Gemini 3.5 Flash. Running 4x faster than rivals, it powers 24/7 autonomous agents via the new Antigravity framework.

Talk to Your Tech: Google Debuts “Ask YouTube” and Instant Voice “Live” Tools at I/O 2026 Ask YouTube AI feature Google I/O 2026
  • Technology

Talk to Your Tech: Google Debuts “Ask YouTube” and Instant Voice “Live” Tools at I/O 2026

Do Son May 20, 2026 0

At Google I/O 2026, Google unveiled "Ask YouTube" for natural-language video interrogation alongside "Live" voice-prompting across Gmail, Docs, and Keep.
Keys to the Kingdom: Critical 9.9 CVSS Budibase Flaw Allows Total Tenant Takeover bui
  • Vulnerability Report

Keys to the Kingdom: Critical 9.9 CVSS Budibase Flaw Allows Total Tenant Takeover

Do Son May 20, 2026 0

Budibase patches a critical 9.9 CVSS SCIM authorization bypass (CVE-2026-46425). Basic users can delete admins and hijack accounts. Update now!

Details and PoC Exploit Code Released: Critical Cockpit RCE Flaw Grants Instant Root Shells Cockpit RCE Vulnerability CVE-2026-4802 PoC Exploit
  • Vulnerability

Details and PoC Exploit Code Released: Critical Cockpit RCE Flaw Grants Instant Root Shells

Do Son May 20, 2026 0

Technical details and a functional Python PoC exploit have been released for CVE-2026-4802, a critical Cockpit flaw giving low-privilege users root.
Critical 9.8 CVSS: NVIDIA Triton Inference Server Authentication Bypass Threatens AI Workloads NVIDIA NeMo vulnerability CVE-2026-24155, CVE-2026-24252, CVE-2026-24228, code injection NVIDIA DALI vulnerabilities NVIDIA Driver Security Update CVE-2026-24187 Linux
  • Vulnerability Report

Critical 9.8 CVSS: NVIDIA Triton Inference Server Authentication Bypass Threatens AI Workloads

Do Son May 20, 2026 0

NVIDIA patches a critical 9.8 CVSS authentication bypass (CVE-2026-24207) in Triton Inference Server. Update to r26.03 to secure AI workloads!

VoIP Backbone Exposed: Critical FreePBX Flaw (CVE-2026-46376) Allows Unauthenticated Access to User Portals FreePBX UCP Vulnerability CVE-2026-46376 Hard-Coded Credentials
  • Vulnerability Report

VoIP Backbone Exposed: Critical FreePBX Flaw (CVE-2026-46376) Allows Unauthenticated Access to User Portals

Do Son May 20, 2026 0

FreePBX fixes critical 9.1 CVSS flaw (CVE-2026-46376) where hardcoded credentials grant unauthenticated portal access. Update your modules now!
Critical 9.9 CVSS Flaw in Arcane Exposes GitOps Secrets to Basic Users Arcane Docker Vulnerability CVE-2026-45625
  • Vulnerability Report

Critical 9.9 CVSS Flaw in Arcane Exposes GitOps Secrets to Basic Users

Do Son May 20, 2026 0

Arcane fixes a critical 9.9 CVSS vulnerability (CVE-2026-45625) that allows basic users to steal GitOps credentials in plaintext. Update to 1.19.0!

PoC Exploit Code Publicly Released: New “PinTheft” Linux Flaw Overwrites Page Cache for Instant Root PinTheft Linux Exploit Linux LPE PoC Disclosed
  • Linux
  • Vulnerability Report

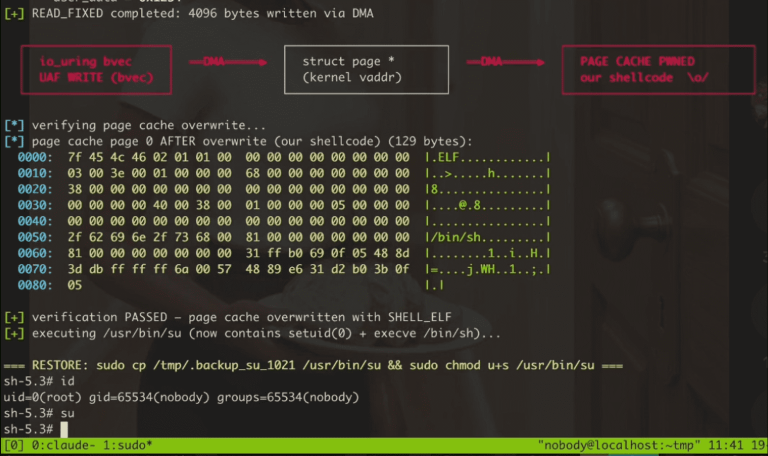
PoC Exploit Code Publicly Released: New “PinTheft” Linux Flaw Overwrites Page Cache for Instant Root
Do Son May 20, 2026 0

Technical details and a working PoC exploit are public for PinTheft, a critical Linux local privilege escalation bug. Block the RDS module now.

Criminal IP Returns to Infosecurity Europe 2026 with Advanced AI-Driven TI & ASM inforsec_sns_1_1777449269P69IHYw2A5
  • Press Release

Criminal IP Returns to Infosecurity Europe 2026 with Advanced AI-Driven TI & ASM

cybernewswire May 19, 2026 0
Torrance, United States / California, 19th May 2026, CyberNewswire
Read More Read more about Criminal IP Returns to Infosecurity Europe 2026 with Advanced AI-Driven TI & ASM
Two-Thirds of Nonhuman Accounts Are Unseen and Unmanaged, According to Orchid Security’s Identity Gap Report Orchid_Identity_Gap_report_Cyber_Newswire_photo_1779130638YN9ZSkjgqG
  • Press Release

Two-Thirds of Nonhuman Accounts Are Unseen and Unmanaged, According to Orchid Security’s Identity Gap Report

cybernewswire May 19, 2026 0
New York, United States, 19th May 2026, CyberNewswire
Read More Read more about Two-Thirds of Nonhuman Accounts Are Unseen and Unmanaged, According to Orchid Security’s Identity Gap Report
GPU Security Alert: NVIDIA Drivers Hit with Critical 8.8 CVSS Flaw and Enterprise vGPU Bugs NVIDIA NeMo vulnerability CVE-2026-24155, CVE-2026-24252, CVE-2026-24228, code injection NVIDIA DALI vulnerabilities NVIDIA Driver Security Update CVE-2026-24187 Linux
  • Vulnerability Report

GPU Security Alert: NVIDIA Drivers Hit with Critical 8.8 CVSS Flaw and Enterprise vGPU Bugs

Do Son May 19, 2026 0

NVIDIA has issued critical security updates for its GPU display drivers and vGPU software to fix a high-severity 8.8 CVSS use-after-free flaw. Patch now!
Unmasked Origin: Infamous “OrBit” Linux Rootkit Exposed as a Fork of Open-Source Medusa OrBit Linux Rootkit Medusa Userland LD_PRELOAD Hooking
  • Malware

Unmasked Origin: Infamous “OrBit” Linux Rootkit Exposed as a Fork of Open-Source Medusa

Do Son May 19, 2026 0

New research by Intezer reveals the OrBit Linux rootkit is actually a fork of the open-source Medusa kit, actively weaponized across multiple APTs.

Resurgent Tycoon 2FA Adopts OAuth Device Code Phishing to Hijack Microsoft 365 Tycoon 2FA Phishing Kit OAuth Device Code Phishing
  • Cybercriminals

Resurgent Tycoon 2FA Adopts OAuth Device Code Phishing to Hijack Microsoft 365

Do Son May 19, 2026 0

Despite a global takedown, Tycoon 2FA is back. It now abuses Microsoft's device code flow to bypass MFA entirely. Disabling this flow is critical.
Chinese APT FamousSparrow Weaponizes Evolved Deed RAT Against Azerbaijani Energy Infrastructure FamousSparrow Deed RAT ProxyNotShell Exchange Exploitation
  • Cyber Security
  • Malware

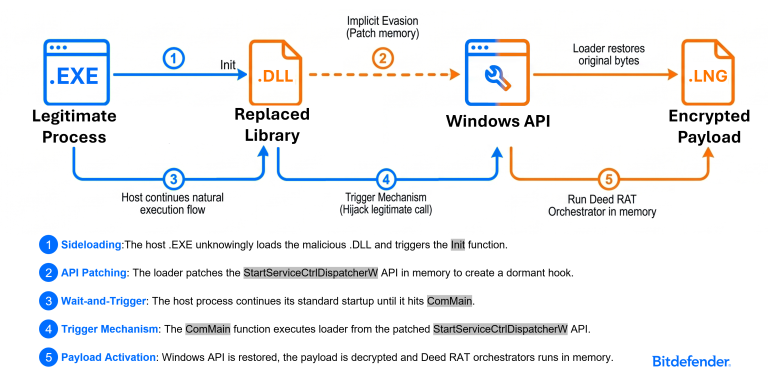
Chinese APT FamousSparrow Weaponizes Evolved Deed RAT Against Azerbaijani Energy Infrastructure

Do Son May 19, 2026 0

Bitdefender exposes a persistent FamousSparrow campaign using advanced DLL sideloading and Deed RAT to compromise energy infrastructure. Patch now!
Boot Partition Bottleneck: Microsoft Confirms Windows 11 Update KB5089549 Fails with Error 0x800f0922 Windows 11 version 26H2 support lifecycle and deployment roadmap for enterprise environments Windows 11 update anomaly Windows 11 context menu Windows 11 KB5089549 update error 0x800f0922 Windows 11 taskbar relocation
  • Windows

Boot Partition Bottleneck: Microsoft Confirms Windows 11 Update KB5089549 Fails with Error 0x800f0922

Do Son May 19, 2026 0

Microsoft confirms Windows 11 update KB5089549 fails and rolls back at 35% with error 0x800f0922 on systems with low EFI partition storage. Learn the fix.

Shai-Hulud Returns: Massive npm Supply Chain Attack Hijacks AntV Ecosystem to Scrape GitHub Runner Memory Mini Shai-Hulud npm Worm AntV Ecosystem Supply Chain Attack
  • Malware

Shai-Hulud Returns: Massive npm Supply Chain Attack Hijacks AntV Ecosystem to Scrape GitHub Runner Memory

Do Son May 19, 2026 0

The Mini Shai-Hulud npm worm has hijacked the atool account, poisoning AntV & timeago.js to scrape GitHub runner memory. Execute a full reset now!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-82418CVSS 9.8
    IBM Watson Speech Services Cartridge 4.0.0 through 5.4.0 could allow a remote attacker to execute arbitrary code due...
    📅 Updated: Nov 9, 2026
  • CVE-2026-119506CVSS 9.1
    Incorrect Privilege Assignment vulnerability in DynamiApps Frontend Admin by DynamiApps acf-frontend-form-element allows Privilege Escalation.This issue affects Frontend Admin...
    📅 Updated: Nov 9, 2026
  • CVE-2024-47856CVSS 9.8
    In RSA Authentication Agent before 7.4.7, service paths and shortcut paths may be vulnerable to path interception if...
    📅 Updated: Nov 8, 2026
  • CVE-2024-36057CVSS 9.8
    Koha Library before 23.05.10 fails to sanitize user-controllable filenames prior to unzipping, leading to remote code execution. The...
    📅 Updated: Nov 8, 2026
  • CVE-2024-36058CVSS 9.8
    The Send Basket functionality in Koha Library before 23.05.10 is susceptible to Time-Based SQL Injection because it fails...
    📅 Updated: Nov 8, 2026
  • CVE-2024-46636CVSS 9.4
    NASA Earth Observing System Data and Information System (EOSDIS) MODAPS v8.1 was discovered to contain a SQL injection...
    📅 Updated: Nov 8, 2026
  • CVE-2026-64232CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: block: recompute nr_integrity_segments in blk_insert_cloned_request blk_insert_cloned_request() already recomputes...
    📅 Updated: Nov 8, 2026
  • CVE-2026-93754CVSS 9.8
    The payever – WooCommerce Gateway plugin for WordPress is vulnerable to arbitrary file upload leading to remote code...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.