 Do Son
Shopware SQL injection rated CVSS 9.8 needs no login, plus a Store API bypass and App token theft. Shopware 6.7.16.1 and 6.6.10.32 fix all three.
Latest Security News
Attackers actively exploit a Frappe authorization flaw in the wild. Read our report on Frappe authorization flaw and patch now.
OpenMage LTS fixes a CVSS 9.3 stored XSS that lets a guest shopper hijack admin sessions via a crafted email. Upgrade to 20.19.1 or 20.18.3.
PHP 8.5.13, 8.4.28, 8.3.37 and 8.2.36 fix 12 flaws, including PHP-FPM request smuggling RCE CVE-2026-129289 and CVE-2026-129496. Patch now.
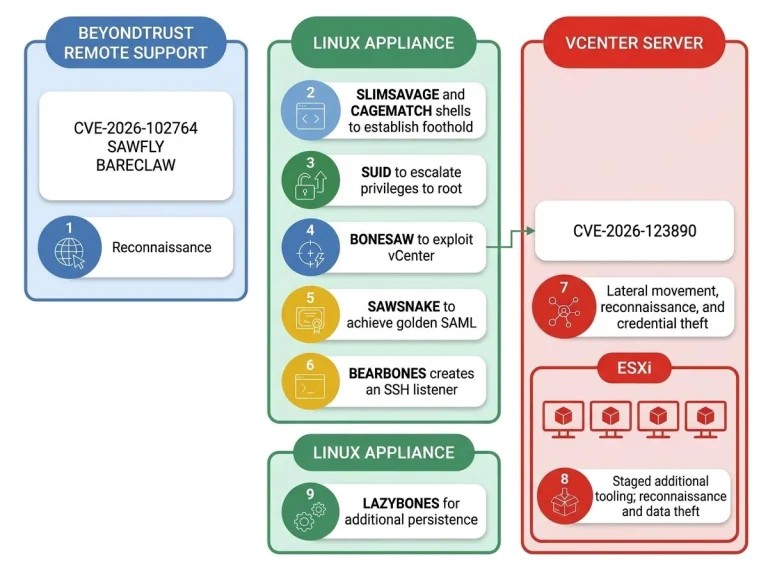
vCenter zero-day CVE-2026-123890 was exploited by ARMORY CASTLE before Broadcom patched it in VMSA-2026-0009. Attack chain, fixes and hunting tips.
Synology security advisories fix critical Synology DSM vulnerabilities CVE-2026-120382 and CVE-2026-123007 (NGINX2Root). Check affected versions and fixes.

Bitdefender uncovers AI agent malware in 22 repositories. See how the GitHub AI agent malware abuses project rules and hooks to steal developer secrets.
Ubiquiti patched seven UniFi Access vulnerabilities in version 4.3.24. Read our UniFi Access vulnerabilities 2026 report on CVE-2026-132802 and more.
Mandiant and GTIG detailed how Russian COLD RELIC phishing and COLD RELIC phishing attacks use stolen cloud rosters and passkeys to breach partners.
Kaspersky uncovers Operation ShadowCloud hitting Asia and Africa. See how Operation ShadowCloud GitDoor GraphDoor backdoors abuse GitHub and SharePoint.
WordPress 7.1.5 fixes 18 flaws, including an unauthenticated privilege escalation that could lead to RCE. What this WordPress security release patches.
Splunk security updates November 2026 patch 146 flaws, including CVE-2026-131253, CVE-2026-76536, and CVE-2026-131202. Review affected versions and fixes.
Latest Technology News
Microsoft engineer Raymond Chen explains why raising Windows Task Manager priority cannot prevent system freezes caused by locks and UI contention.
Reverse engineering reveals Windows 11 AI telemetry tracks usage of Cursor, Copilot, Claude Code, and developer tools via optional diagnostic data.
Microsoft’s New Outlook for Windows offers a modern interface, better cloud integration (with Microsoft 365), and a...
Migrating Outlook data files (PST or OST) to Office 365 (Microsoft 365) requires careful preparation to ensure...
 cybernewswire
New York City, United States, 17th November 2026, CyberNewswire
San Francisco, USA, 17th November 2026, CyberNewswire
Google Antigravity context window capacity has doubled for Gemini 4 Argon, Carbon, and Hydrogen, cutting context compaction frequency by 3.5 times.
Apple fixed the worse_query iOS vulnerability in iOS 27.3 Beta 2, breaking sandbox bypass tools, eSIM workarounds, and cross-app file managers.
Apple updated macOS 27.3 permissions in Beta 2, letting users restrict Full Disk Access to specific folders and limit automation tools per app.
Latest Security News
WordPress 7.1.5 fixes 18 flaws, including an unauthenticated privilege escalation that could lead to RCE. What this WordPress security release patches.
Splunk security updates November 2026 patch 146 flaws, including CVE-2026-131253, CVE-2026-76536, and CVE-2026-131202. Review affected versions and fixes.
Ruby 4.0.10, 3.4.13 and 3.3.14 fix seven Ruby regular expression and string bugs. Ruby knows of PoCs for Ruby remote code execution. Upgrade now.
Mitel OpenScape 4000 fixes two CVSS 10.0 flaws, an authentication bypass and a command injection, in V11 R2.14. OpenScape 4000 Manager is affected too.
ASUS Fixes 12 Flaws across routers and Control Center, including CVSS 10.0 bug CVE-2026-114202, CVE-2026-126574, and CVE-2026-88711. Update now.
Google published a PoC exploit for CVE-2026-74127, a critical CVSS 9.4 AMD PSP Code Execution flaw and Masterkey CVE-2018-8930 variant on Zen 1 and Zen+.
Microsoft Office Fixes 3 omitted November 2026 flaws: SharePoint and OneNote bugs CVE-2026-124223, CVE-2026-126526, and CVE-2026-124222. Patch now.
Drupal core security update patches Drupal Remote Code Execution flaw CVE-2026-132165 and gadget chain CVE-2026-132166. Upgrade to 11.4.13 or 10.6.22 now.
JetBrains released a TeamCity security update fixing 21 flaws, including CVSS 9.9 RCE CVE-2026-132231. Upgrade to version 2026.1.3 now.
A critical PHP security release lands November 19 and is expected to fix CVE-2026-115560, a session upload progress RCE. Conditions and mitigation.
CISA adds 4 Exploited Flaws to its KEV catalog: CVE-2024-10441, CVE-2026-40217, CVE-2026-90436, and CVE-2026-90817. Review federal patch deadlines now.
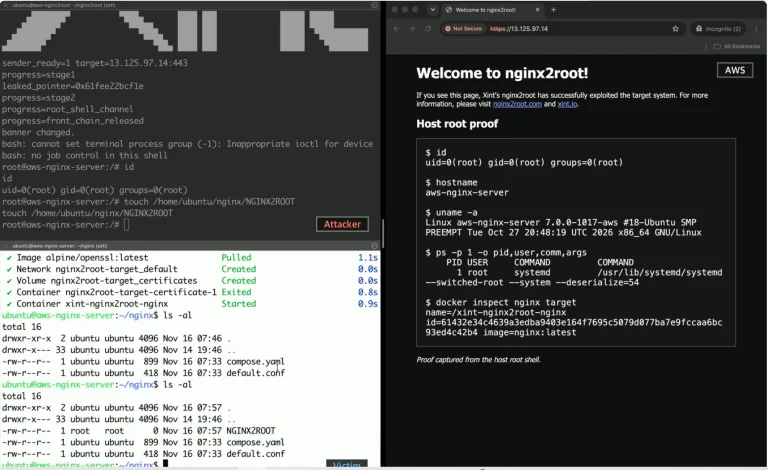
NGINX2Root (CVE-2026-123007) lets attackers run code on NGINX servers with HTTP/2 enabled. Five flaws, a public PoC, and how to patch.
Latest Technology News
Microsoft engineer Raymond Chen explains why raising Windows Task Manager priority cannot prevent system freezes caused by locks and UI contention.
Reverse engineering reveals Windows 11 AI telemetry tracks usage of Cursor, Copilot, Claude Code, and developer tools via optional diagnostic data.
Microsoft’s New Outlook for Windows offers a modern interface, better cloud integration (with Microsoft 365), and a...
Migrating Outlook data files (PST or OST) to Office 365 (Microsoft 365) requires careful preparation to ensure...
New York City, United States, 17th November 2026, CyberNewswire
San Francisco, USA, 17th November 2026, CyberNewswire
Google Antigravity context window capacity has doubled for Gemini 4 Argon, Carbon, and Hydrogen, cutting context compaction frequency by 3.5 times.
Apple fixed the worse_query iOS vulnerability in iOS 27.3 Beta 2, breaking sandbox bypass tools, eSIM workarounds, and cross-app file managers.
Apple updated macOS 27.3 permissions in Beta 2, letting users restrict Full Disk Access to specific folders and limit automation tools per app.