 Do Son
A brief Microsoft Agent Framework PyPI attack injected credential-stealing malware into versions 1.26.1 and 1.26.2, targeting cloud and GitHub secrets.
Latest Security News
Patch now. Details and PoC exploit code are public for this critical CVSS 9.1 Vite Dev Server RCE flaw in exposed dev hosts.
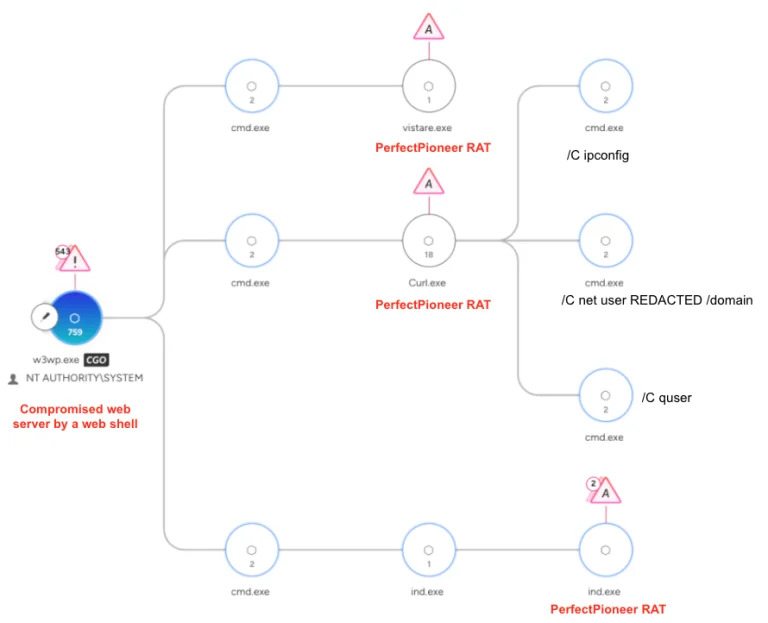
Unit 42 uncovered the TGR-STA-0049 PerfectPioneer RAT KUKURAT espionage campaign using HTTP/3 C2 and heuristic camouflage against Asian governments.
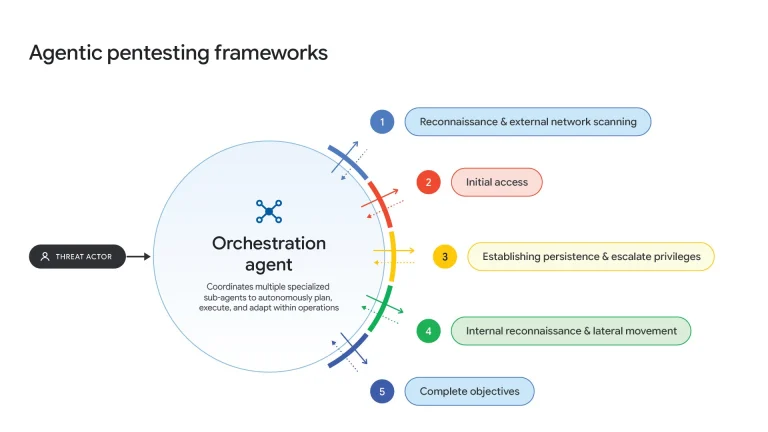
Mandiant and GTIG detailed Google agentic threat activity showing how autonomous agentic threat activity, LLMJacking, and AI exploits hit enterprises.
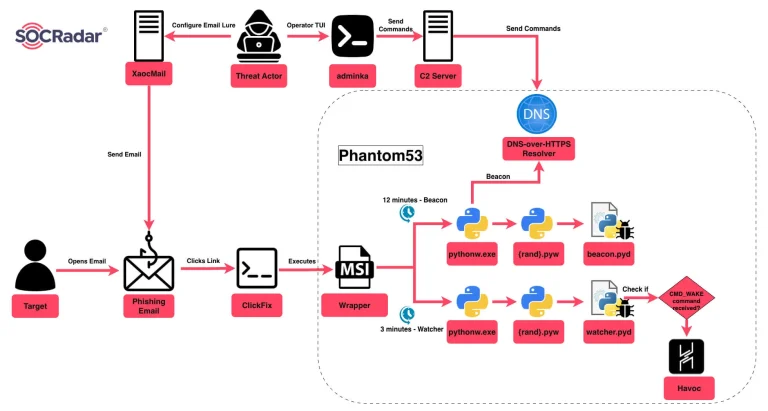
SOCRadar uncovered the XaocMail ClickFix campaign using Cloudflare Workers to deploy XaocMail ClickFix Phantom53 DoH malware and HavoX agents.
Singapore CSA warns of active attacks and public PoC code for CVE-2026-119618, a critical Apache RCE flaw in mod_http2. Update to 2.4.71 immediately.
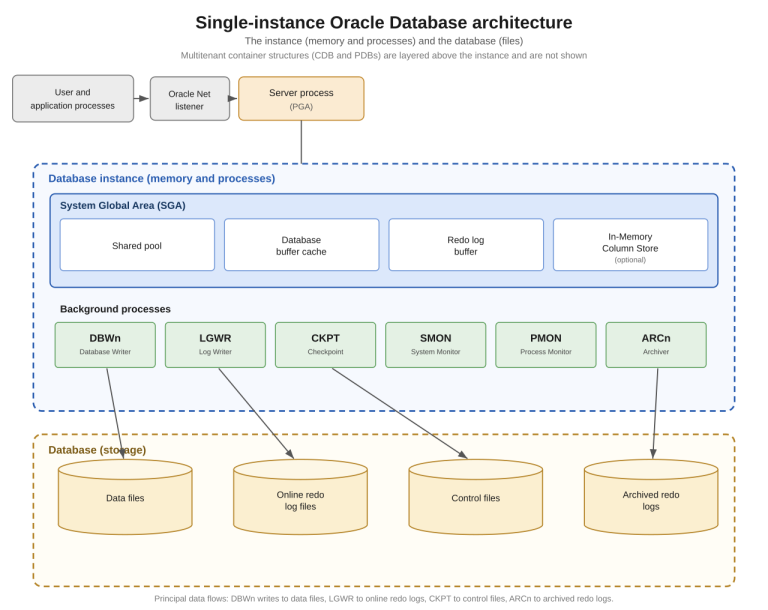
Oracle Database vulnerabilities CVE-2026-114819 and two more score 9.9, while Oracle APEX flaw CVE-2026-114849 needs no login. Patch details.
Broadcom AutoSys Fixes 11 Flaws in version 24.2.01, including critical RCE bugs CVE-2026-126551, CVE-2026-126552, and CVE-2026-126553. Patch now.
Atlassian Fixes 318 Flaws in its November 2026 Security Bulletin, including CVE-2026-4800, CVE-2026-47890, and CVE-2026-21600. Patch Data Center now.
Oracle E-Business Suite gets four unauthenticated CVSS 9.8 fixes, including CVE-2026-114924 and CVE-2026-114925. Affected versions and steps.
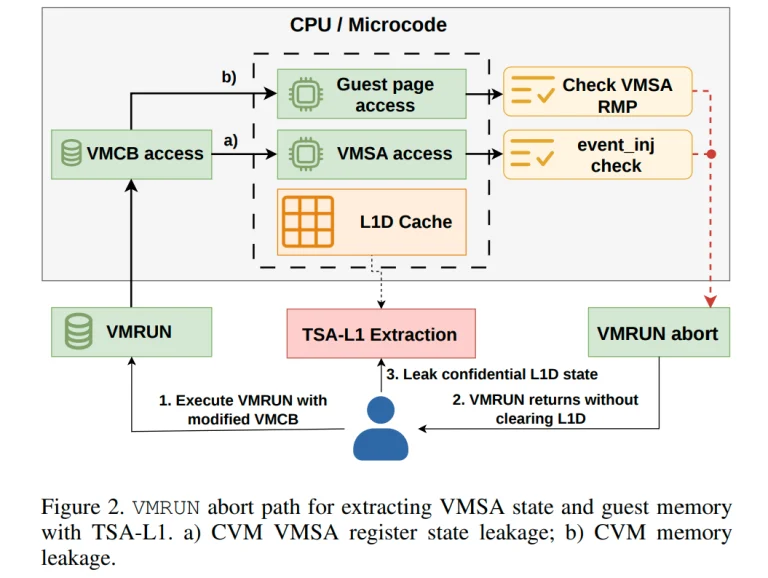
Skyfall attack CVE-2026-40671 lets a malicious host leak AMD SEV-SNP confidential VM data on EPYC CPUs. PoC code is public; microcode fixes are out.
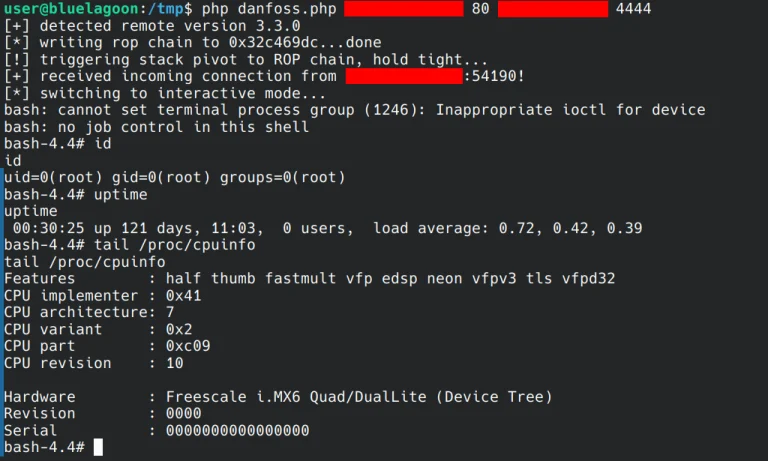
Danfoss AK-SM800A firmware 5.3.2 has six unpatched pre-authentication RCE flaws in its refrigeration controllers. Isolate them from the internet now.
Latest Technology News
A newly discovered Windows 11 OOBE IPv6 limitation prevents users from completing initial setup on IPv6-only networks without active IPv4 routing.
Italy issued an 805 million euro Italy Meta privacy fine over Facebook for Android accessing personal photo galleries without explicit user consent.
Learn how the new Google Project Zero disclosure policy replaces 90+30 rules with Full X deadlines to counter fast AI exploit risks.
Weekly CVE report for Nov 9-15, 2026: 4,647 new CVEs and 12 exploited vulnerabilities added to CISA KEV, with Daily Cybersecurity a day ahead.
Microsoft will remove trust for 10 remaining eMudhra root certificates on November 16, 2026, via automatic Windows, Edge, and WebView2 updates.
Brave Search anti-scraping defenses will soon encrypt search result links via intermediate redirect pages to block surging AI agents and web crawlers.
Google unveils Gemini 4 Hydrogen, a high-speed AI model derived from Carbon with a 1M token window, 2.5x faster speeds, and enhanced agent security.
Microsoft deployed a server-side patch for the Windows 11 KB5132061 update after Windows Sandbox conflicts caused installation failures at 99%.
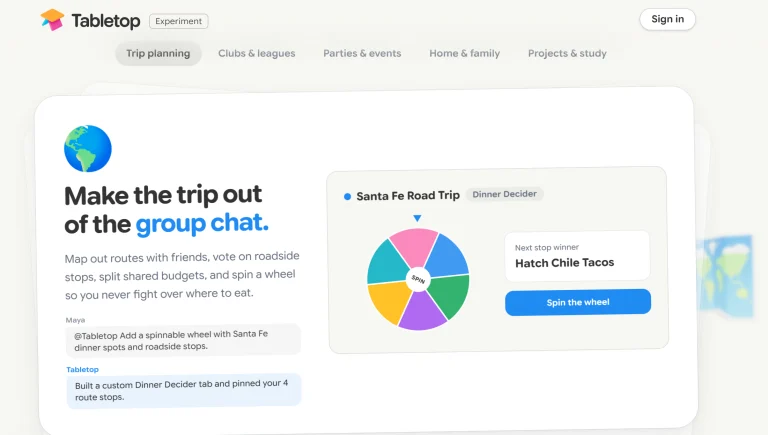
Google Labs Tabletop introduces an experimental AI collaboration hub that lets friends build custom trip planners, polls, and expense splitters.
Apple announced the permanent Apple Support Community shutdown on November 20, 2026, placing the 28-year-old troubleshooting forum into read-only mode.
Latest Security News
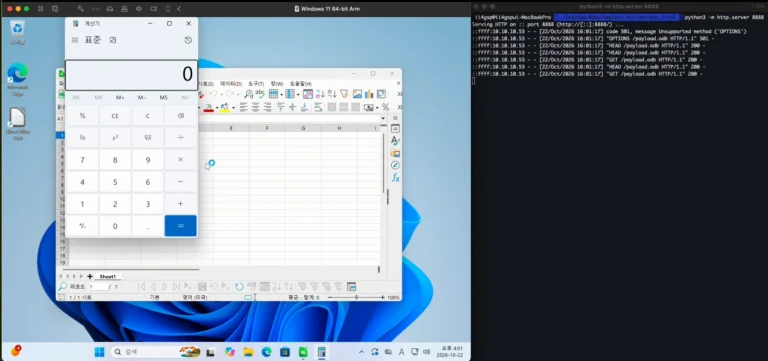
LibreOffice remote code execution PoC for CVE-2026-104007 and CVE-2026-104692 is public: one opened spreadsheet runs code. Update to 26.2.7 or 26.8.2.
Oracle November 2026 update fixes 655 flaws. CVE-2026-91569 in WebLogic and CVE-2026-114835 in Access Manager score 10.0. What to patch first.
Google Chrome 158 Fixes 204 security flaws, including critical bugs CVE-2026-130963, CVE-2026-131031, and CVE-2026-131060. Update your browser now.
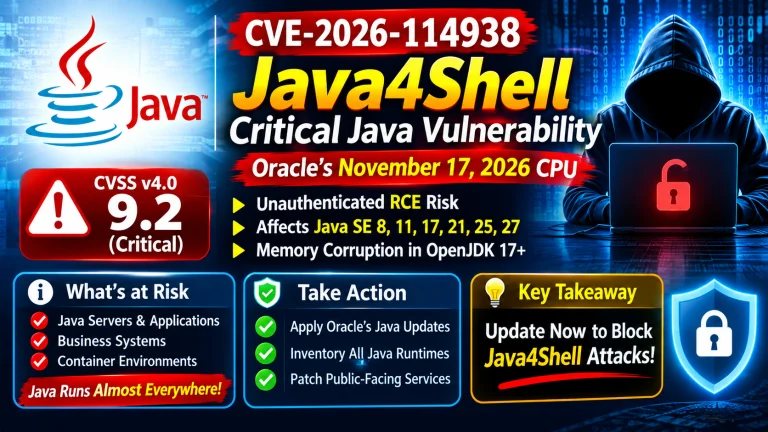
Java4Shell (CVE-2026-114938) is reported as an unauthenticated RCE in Oracle Java SE and OpenJDK 17. What is confirmed, and how to patch.
TYPO3 vulnerability CVE-2026-125160 is actively exploited, and CVE-2026-119623 (CVSS 9.4) enables RCE. Update to TYPO3 14.3.12 or 13.4.40 now.
Apache Roller vulnerability CVE-2026-129448 (CVSS 9.8) allows unauthenticated RCE and is actively exploited. Upgrade to 6.1.6 or later now.
A critical uBlock Origin UXSS vulnerability allowed malicious sites to hijack the Element Picker and inject trusted filter scripts before version 1.76.4.
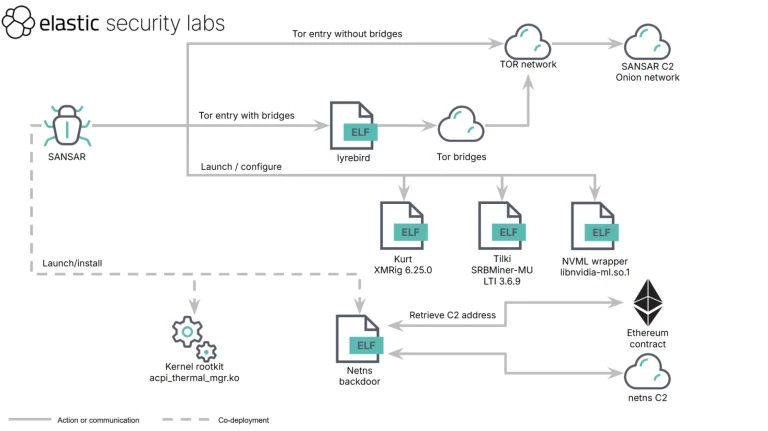
Elastic Security Labs uncovers SANSAR Linux malware. See how the REF3364 SANSAR Linux malware uses Tor C2, an ftrace rootkit, and NVML GPU spoofing.
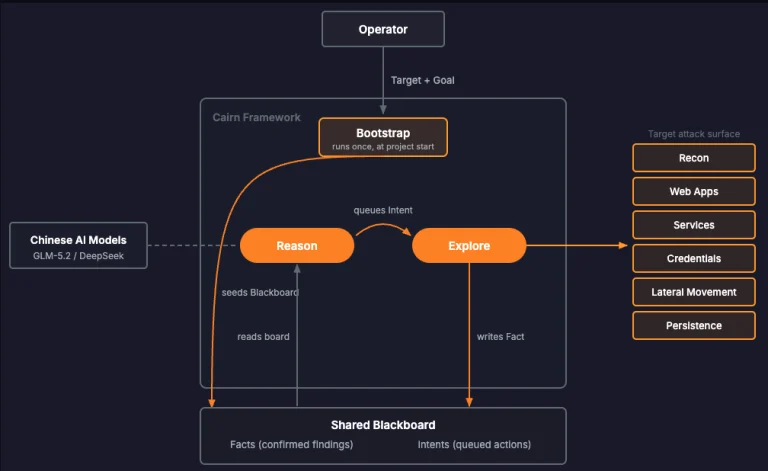
Unit 42 uncovered the Cairn framework CL-STA-1238 campaign using DeepSeek and Zhipu GLM models to autonomously breach 10 organizations.
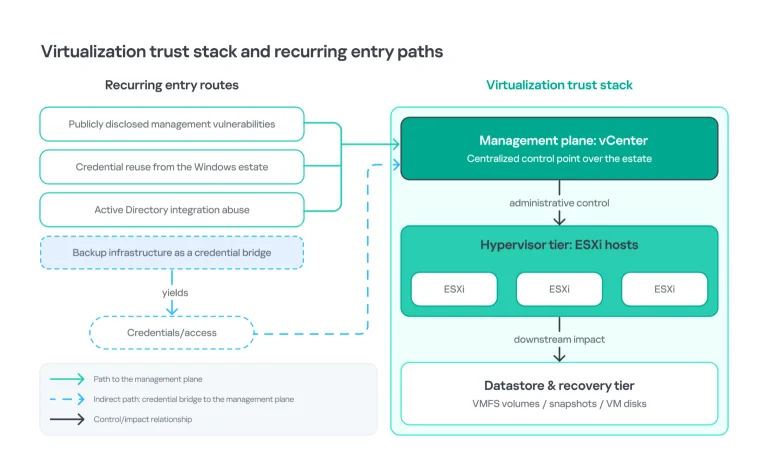
Kaspersky GERT analyzes a BlackNevas ESXi ransomware attack. See how the VMware BlackNevas ESXi ransomware abused vCenter Host Profiles to wipe VMs.
A widespread DarkSword iOS malvertising campaign compromised NextDay Media ad tags across Dutch and Belgian sites, targeting unpatched iPhones.
MiCollab vulnerabilities fixed: MTLVULN-1864 (CVSS 10.0) command injection and a 9.0 XML injection allow unauthenticated attacks. Patch 10.3.0.18.
Latest Technology News
A newly discovered Windows 11 OOBE IPv6 limitation prevents users from completing initial setup on IPv6-only networks without active IPv4 routing.
Italy issued an 805 million euro Italy Meta privacy fine over Facebook for Android accessing personal photo galleries without explicit user consent.
Learn how the new Google Project Zero disclosure policy replaces 90+30 rules with Full X deadlines to counter fast AI exploit risks.
Microsoft will remove trust for 10 remaining eMudhra root certificates on November 16, 2026, via automatic Windows, Edge, and WebView2 updates.
Brave Search anti-scraping defenses will soon encrypt search result links via intermediate redirect pages to block surging AI agents and web crawlers.
Google unveils Gemini 4 Hydrogen, a high-speed AI model derived from Carbon with a 1M token window, 2.5x faster speeds, and enhanced agent security.
Microsoft deployed a server-side patch for the Windows 11 KB5132061 update after Windows Sandbox conflicts caused installation failures at 99%.
Google Labs Tabletop introduces an experimental AI collaboration hub that lets friends build custom trip planners, polls, and expense splitters.
Apple announced the permanent Apple Support Community shutdown on November 20, 2026, placing the 28-year-old troubleshooting forum into read-only mode.
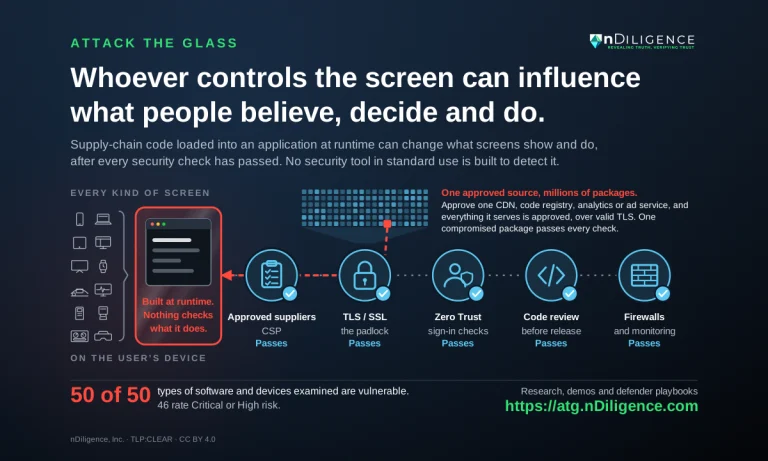
 cybernewswire
San Francisco, California, USA, 12th November 2026, CyberNewswire