 Do Son
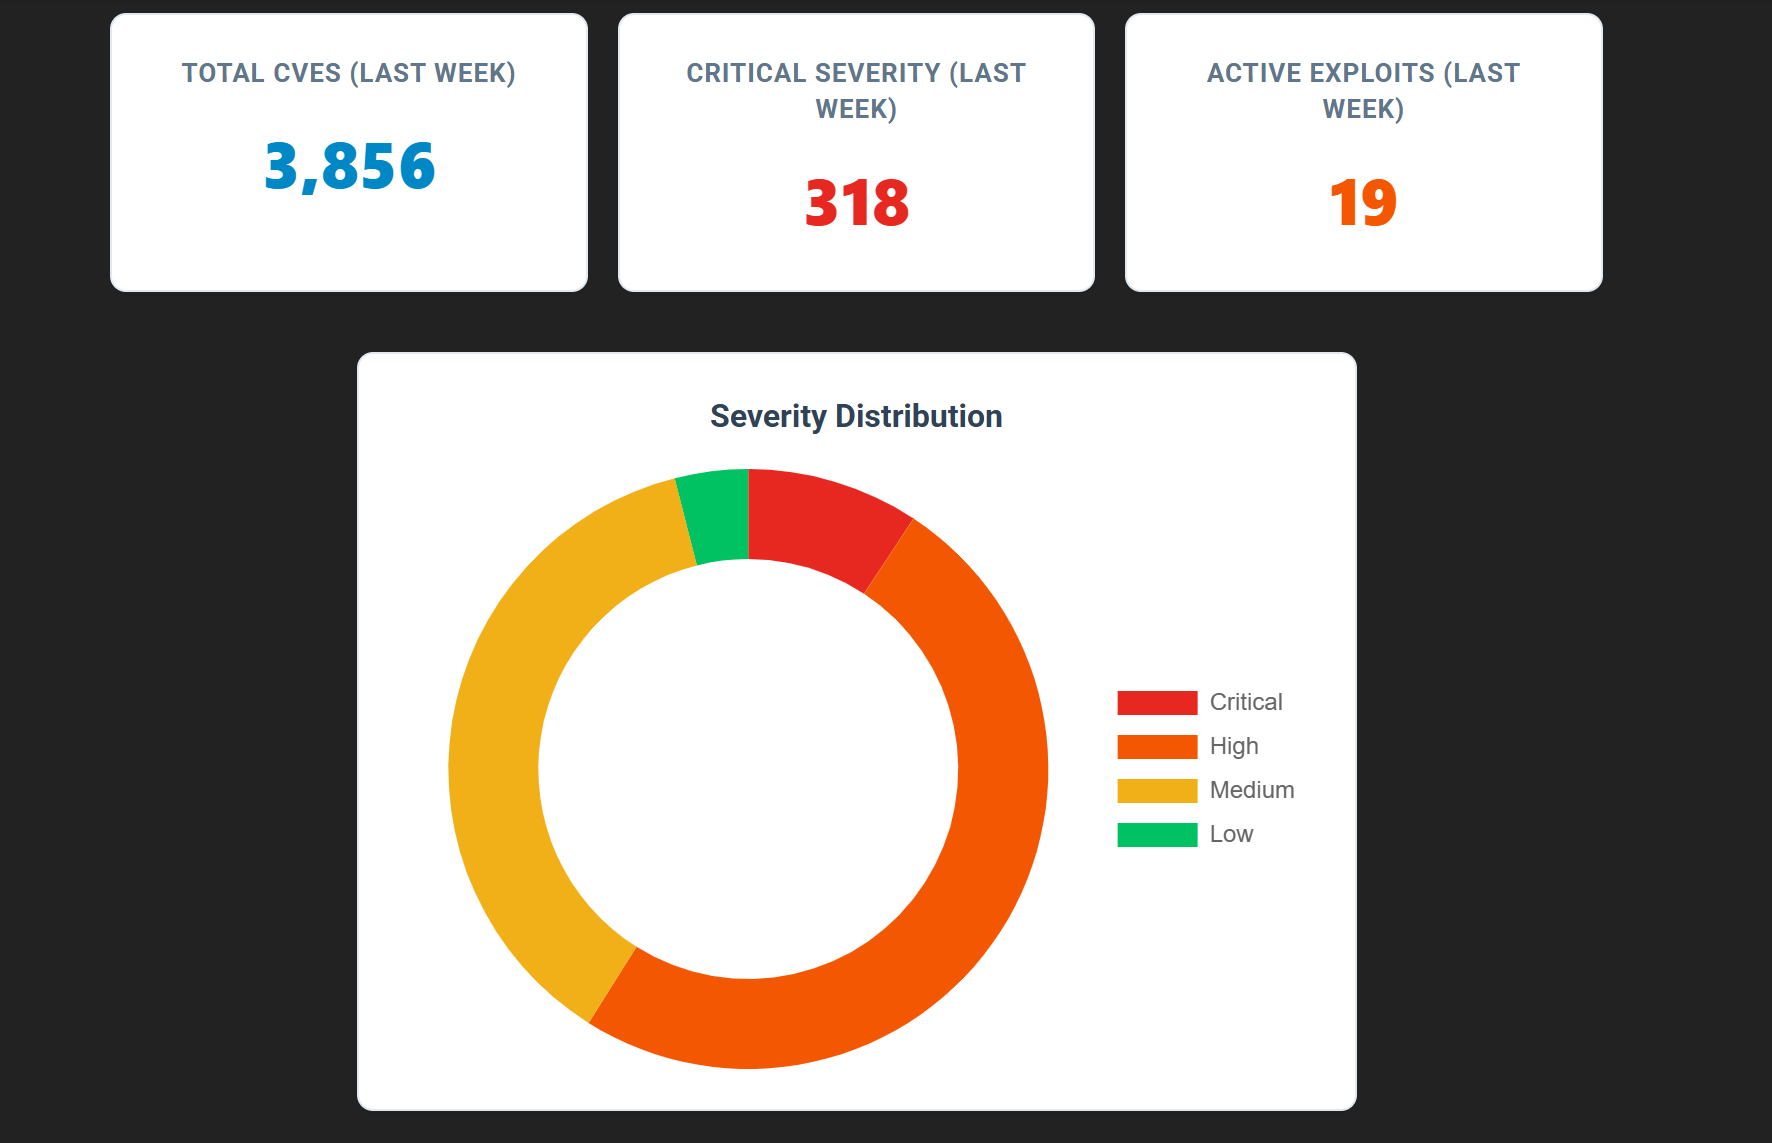
Between September 7 and September 13, 2026, our tracker logged 3,856 new CVEs. This weekly CVE report focuses on the 19 flaws that Daily Cybersecurity flagged as exploited. Ten later reached the CISA Known Exploited Vulnerabilities catalog. Nine did not, which makes them exclusive to our intelligence feed.
The week in numbers
The volume this week stayed high. Our tracker recorded 3,856 new CVEs across all sources. Of those, 318 were rated critical and 1,703 were rated high. In total, 317 flaws carried a CVSS score of 9.0 or above.
The exploited set tells the sharper story. Daily Cybersecurity marked 19 flaws as exploited during the week. Of those, 10 later appeared in the live CISA KEV catalog. The other 9 remain absent from it, so we label them exclusive to DC. On the shared flaws, our feed led by up to three days.
The intelligence lead: Daily Cybersecurity vs CISA KEV
The table below compares our “marked exploited” date against CISA’s “date added.” Verification used the live CISA catalog, version 2026.09.11, released September 11, 2026.
| CVE ID | Affected product | DC marked exploited | CISA KEV date added | Lead time |
|---|---|---|---|---|
| CVE-2026-86060 | MikroTik RouterOS | 2026-09-07 | 2026-09-10 | 3 days earlier |
| CVE-2026-67277 | MikroTik RouterOS | 2026-09-07 | 2026-09-10 | 3 days earlier |
| CVE-2026-86218 | N-able N-central | 2026-09-07 | 2026-09-08 | 1 day earlier |
| CVE-2026-85706 | GitLab CE/EE | 2026-09-11 | 2026-09-11 | Same day |
| CVE-2026-42016 | JFrog Artifactory | 2026-09-11 | 2026-09-11 | Same day |
| CVE-2026-42018 | JFrog Artifactory | 2026-09-11 | 2026-09-11 | Same day |
| CVE-2026-20079 | Cisco Secure Firewall Management Center | 2026-09-09 | 2026-09-09 | Same day |
| CVE-2025-25249 | Fortinet FortiOS | 2026-09-09 | 2026-09-09 | Same day |
| CVE-2026-87491 | Google Chrome (V8) | 2026-09-09 | 2026-09-09 | Same day |
| CVE-2026-75650 | Adobe Commerce | 2026-09-08 | 2026-09-08 | Same day |
| CVE-2026-67276 | MikroTik RouterOS | 2026-09-07 | Not listed | Exclusive to DC |
| CVE-2026-67278 | MikroTik RouterOS | 2026-09-07 | Not listed | Exclusive to DC |
| CVE-2026-67279 | MikroTik RouterOS | 2026-09-07 | Not listed | Exclusive to DC |
| CVE-2026-67281 | MikroTik RouterOS | 2026-09-07 | Not listed | Exclusive to DC |
| CVE-2026-51990 | Sogou Input Method | 2026-09-12 | Not listed | Exclusive to DC |
Table 1. Daily Cybersecurity exploited flaws verified against the live CISA KEV catalog (version 2026.09.11). “Not listed” flaws could still be added later.
The pattern is clear. Daily Cybersecurity led by a day or more on three shared flaws, and matched CISA on the other seven. Nine more flaws surfaced only through our feed, including the confirmed “MikroTrick” entry point CVE-2026-67276. Treat lead time as a feed-to-feed comparison, not a controlled benchmark, since the two dates measure slightly different events.
Exploited vulnerabilities from CISA KEV only
CISA also added four exploited flaws this period that our exploited set did not flag. They appear below for completeness.
| CVE ID | Affected product | Vulnerability type | CVSS | CISA KEV date added |
|---|---|---|---|---|
| CVE-2026-84869 | ConnectWise ScreenConnect | Improper privilege management / missing authorization | 9.9 | 2026-09-11 |
| CVE-2026-19490 | Citrix NetScaler | Actively exploited (see CISA notes) | Pending | 2026-09-09 |
| CVE-2026-81963 | Microsoft Windows | Local privilege escalation | 7.8 | 2026-09-08 |
| CVE-2026-85880 | Microsoft Windows | Local privilege escalation | 7.8 | 2026-09-08 |
Table 2. CISA KEV additions this period not present in the Daily Cybersecurity exploited set.
The flaws that stand out
CVE-2026-86218: pre-auth RCE in N-able N-central
This maximum-severity flaw scores a CVSS of 10.0. It is a static code injection bug (CWE-96) in the N-central RMM platform. An unauthenticated attacker can run code on the server directly. N-able’s incident notice says the flaw “has been observed being exploited in the wild.” The scale is real, too. The Shadowserver Foundation counted nearly 1,500 internet-facing N-central servers. Because one server manages many client networks, a single breach can cascade widely.
CVE-2026-86060 and CVE-2026-67276: MikroTik “MikroTrick”
CERT Polska confirmed active exploitation of a RouterOS SSH chain it named MikroTrick. Attackers pair CVE-2026-67276 with CVE-2026-86060 to take full control without credentials. Notably, exploitation began around September 2, a day before patches shipped. The exposure is huge. Shadowserver counted over 122,500 internet-facing RouterOS SSH instances in one scan. CISA added CVE-2026-86060 and CVE-2026-67277 to KEV on September 10. Curiously, the entry point CVE-2026-67276 is not on KEV, yet our feed flagged it.
CVE-2026-85706: unauthenticated file read in GitLab
GitLab patched this path traversal bug on September 10. It also earns a perfect CVSS of 10.0. According to GitLab, the fix addressed “improper path confinement and missing authentication enforcement in the repository commits API.” watchTowr reported in-the-wild probes starting the next morning, September 11. An attacker can read config files, secrets, and credentials off the server without logging in.
What defenders should do
Patch the internet-facing, unauthenticated flaws first. Start with N-central 2026.3.1.14, GitLab 19.1.8 / 19.2.6 / 19.3.2, and Cisco Secure FMC. Next, update MikroTik RouterOS to 6.49.21, 7.23.4, or 7.24.2, and treat any SSH-exposed device as a suspected compromise. Then apply the FortiOS and Adobe Commerce fixes. Restrict management interfaces to trusted networks wherever a patch must wait. Finally, hunt for signs of compromise on RMM and source-code platforms, since attackers move fast on these targets.
Get the full weekly CVE report data
This premium content is securely locked. You must upgrade your subscription to access the full threat intelligence report, including detailed mitigation steps, deep-dive analysis, and active exploitation metrics. Your attempt to inspect the DOM will only reveal this placeholder text. Please support our work to read the actual coverage.
Unlock Premium Threat Intelligence
This is a premium content. Upgrade to Pro or Team to unlock full access and remove all reading restrictions.
 Buy Me a Coffee
