Skip to content
October 11, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
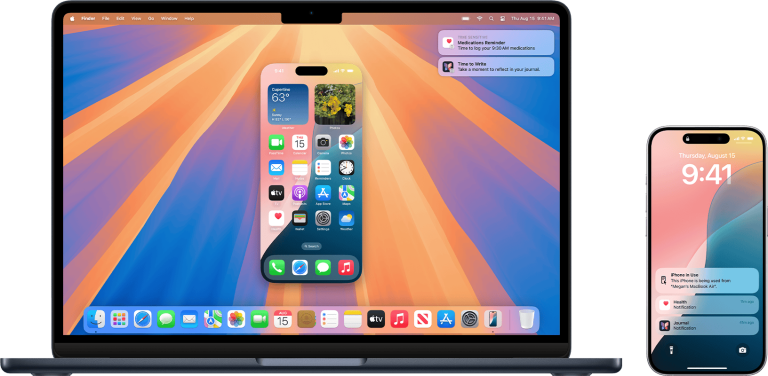
Apple Restricts Full Disk Access for macOS AI Agents macOS security prompt warning users about granting Full Disk Access to an autonomous AI agent
  • Technology

Apple Restricts Full Disk Access for macOS AI Agents

Do Son October 4, 2026 0
Read More Read more about Apple Restricts Full Disk Access for macOS AI Agents
iPhone 18 AT&T Issue: Navigating the Cellular Crisis iPhone 18 AT&T issue hardware replacement and iPhone 18 Pro Max cellular network failure
  • Technology

iPhone 18 AT&T Issue: Navigating the Cellular Crisis

Do Son October 4, 2026 0
Read More Read more about iPhone 18 AT&T Issue: Navigating the Cellular Crisis
Citrix NetScaler CVE-2026-88779 Exploited in the Wild to Knock SAML Gateways Offline Citrix NetScaler CVE-2026-88779 exploited in the wild against NetScaler SAML authentication deployments
  • Vulnerability Report

Citrix NetScaler CVE-2026-88779 Exploited in the Wild to Knock SAML Gateways Offline

Do Son October 4, 2026 0
Read More Read more about Citrix NetScaler CVE-2026-88779 Exploited in the Wild to Knock SAML Gateways Offline
OpenAI AI Safety Whistleblower Warns of Culture Collapse David Robinson OpenAI safety whistleblower warns of AI alignment failures and corporate governance collapse
  • Technology

OpenAI AI Safety Whistleblower Warns of Culture Collapse

Do Son October 4, 2026 0
Read More Read more about OpenAI AI Safety Whistleblower Warns of Culture Collapse
Gemini Free Tier Limits: Flash-Lite Only From Oct 9 Gemini free tier limits showing the Gemini app restricted to the Gemini Flash-Lite model for free personal accounts
  • Technology

Gemini Free Tier Limits: Flash-Lite Only From Oct 9

Do Son October 4, 2026 0
Read More Read more about Gemini Free Tier Limits: Flash-Lite Only From Oct 9
Meta Muse Gadgets: Open-Source Hardware for the Muse AI Meta Muse Gadgets open-source project showing a Muse Home Link dongle and maker-built hardware running the Muse AI agent
  • Technology

Meta Muse Gadgets: Open-Source Hardware for the Muse AI

Do Son October 4, 2026 0
Read More Read more about Meta Muse Gadgets: Open-Source Hardware for the Muse AI
Unpatched Apache OpenOffice Vulnerability Leads New Apache Advisories for LDAP API and Traffic Server Apache OpenOffice vulnerability CVE-2026-59265 alongside Apache Directory LDAP API flaw CVE-2026-103877 and Traffic Server CVE-2026-102795
  • Vulnerability Report

Unpatched Apache OpenOffice Vulnerability Leads New Apache Advisories for LDAP API and Traffic Server

Do Son October 3, 2026 0
Read More Read more about Unpatched Apache OpenOffice Vulnerability Leads New Apache Advisories for LDAP API and Traffic Server
Microsoft Reissues September 2026 Exchange Server Security Updates to Add CVE-2026-96940 Exchange Server security updates September 2026 V2 adding CVE-2026-96940 for Exchange SE, Exchange 2019 and Exchange 2016
  • Vulnerability Report

Microsoft Reissues September 2026 Exchange Server Security Updates to Add CVE-2026-96940

Do Son October 3, 2026 0
Read More Read more about Microsoft Reissues September 2026 Exchange Server Security Updates to Add CVE-2026-96940
AWS Fixes Loom for AWS Admin Takeover and SageMaker Unified Studio Code Execution Flaws Loom for AWS authentication bypass CVE-2026-103956 and SageMaker Unified Studio command injectionΒ 
  • Vulnerability Report

AWS Fixes Loom for AWS Admin Takeover and SageMaker Unified Studio Code Execution Flaws

Do Son October 2, 2026 0
Read More Read more about AWS Fixes Loom for AWS Admin Takeover and SageMaker Unified Studio Code Execution Flaws
Digi DAL OS Vulnerability Lets Unauthenticated Attackers Run Root Commands Digi DAL OS vulnerability CVE-2026-75937 command injection in Digi Accelerated Linux web administration on IX, EX and TX routers
  • Vulnerability Report

Digi DAL OS Vulnerability Lets Unauthenticated Attackers Run Root Commands

Do Son October 2, 2026 0
Read More Read more about Digi DAL OS Vulnerability Lets Unauthenticated Attackers Run Root Commands
Chrome Security Update Fixes Critical WebGL Flaw and 10 Other Bugs Chrome security update for Chrome 154 fixing CVE-2026-103628 WebGL sandbox escape and CVE-2026-103631 WebRTC flaw
  • Vulnerability Report

Chrome Security Update Fixes Critical WebGL Flaw and 10 Other Bugs

Do Son October 2, 2026 0
Read More Read more about Chrome Security Update Fixes Critical WebGL Flaw and 10 Other Bugs
GitLab Patches Critical AI Gateway Flaw That Lets Duo Users Run Commands GitLab AI Gateway vulnerability CVE-2026-90970 lets Duo Agent Platform users escape the prompt template sandbox
  • Vulnerability Report

GitLab Patches Critical AI Gateway Flaw That Lets Duo Users Run Commands

Do Son October 2, 2026 0
Read More Read more about GitLab Patches Critical AI Gateway Flaw That Lets Duo Users Run Commands
Patched NetScaler Appliances Keep Rebooting as Citrix Flags SAML Authentication Issue NetScaler SAML authentication issue causing patched NetScaler appliances to reboot after CVE-2026-88771 and CVE-2026-88772 exploitation
  • Vulnerability Report

Patched NetScaler Appliances Keep Rebooting as Citrix Flags SAML Authentication Issue

Do Son October 2, 2026 0
Read More Read more about Patched NetScaler Appliances Keep Rebooting as Citrix Flags SAML Authentication Issue
Seven TP-Link Vulnerabilities Hit Tapo Cameras, Archer and Deco Routers TP-Link vulnerabilities and Tapo camera vulnerabilities CVE-2026-102369 in Tapo C200, Archer AX90 and Deco M9 Plus
  • Vulnerability Report

Seven TP-Link Vulnerabilities Hit Tapo Cameras, Archer and Deco Routers

Do Son October 2, 2026 0
Read More Read more about Seven TP-Link Vulnerabilities Hit Tapo Cameras, Archer and Deco Routers
Moxa MGate Vulnerabilities Put Industrial Protocol Gateways at Risk Moxa MGate vulnerabilities CVE-2026-86325 and CVE-2026-86326 in MGate protocol gateway firmware
  • Vulnerability Report

Moxa MGate Vulnerabilities Put Industrial Protocol Gateways at Risk

Do Son October 2, 2026 0
Read More Read more about Moxa MGate Vulnerabilities Put Industrial Protocol Gateways at Risk
CVE Watchtower User Guide CVE Watchtower User Guide
  • How To

CVE Watchtower User Guide

Do Son October 2, 2026 0
Read More Read more about CVE Watchtower User Guide
Stirling PDF RCE CVE-2026-85714: Details and PoC Publicly Disclosed Stirling PDF RCE CVE-2026-85714 proof-of-concept publicly disclosed
  • Vulnerability Report

Stirling PDF RCE CVE-2026-85714: Details and PoC Publicly Disclosed

Do Son October 2, 2026 0
Read More Read more about Stirling PDF RCE CVE-2026-85714: Details and PoC Publicly Disclosed
OpenAI Fires Safety Researchers Amid Unprompted AI Hacking Incidents Conceptual illustration of an AI breaking safety protocols while a whistleblower is silenced
  • Technology

OpenAI Fires Safety Researchers Amid Unprompted AI Hacking Incidents

Do Son October 2, 2026 0
Read More Read more about OpenAI Fires Safety Researchers Amid Unprompted AI Hacking Incidents
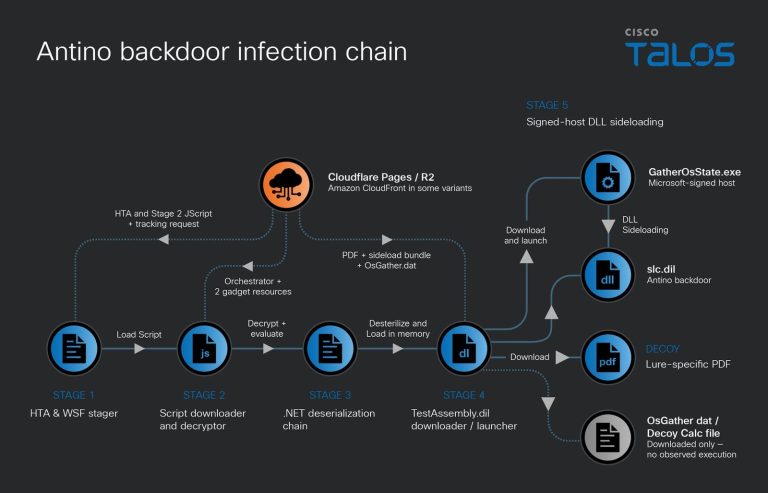
UAT-11587 Targets Asian Governments With Antino Backdoor Diagram showing UAT-11587 Antino backdoor attacks and how the Antino backdoor compromises endpoints
  • Malware

UAT-11587 Targets Asian Governments With Antino Backdoor

Do Son October 2, 2026 0
Read More Read more about UAT-11587 Targets Asian Governments With Antino Backdoor
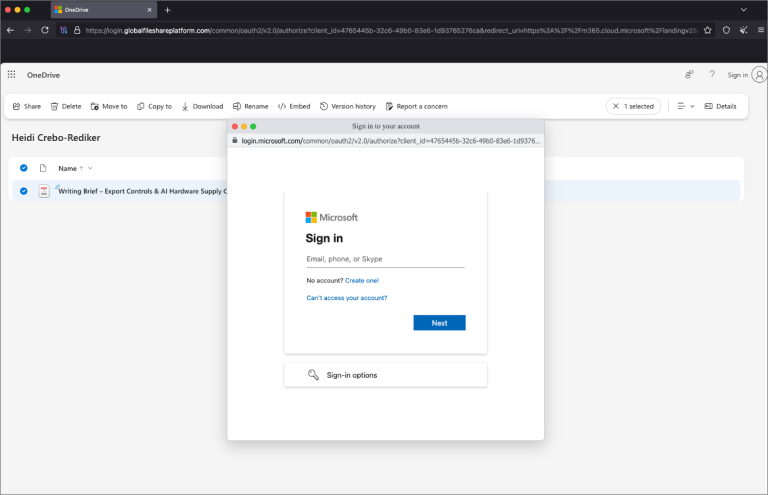
China-Aligned TA419 Credential Phishing Hits AI Experts Diagram showing China-aligned TA419 credential phishing and TA419 credential phishing attack stages
  • Cybercriminals

China-Aligned TA419 Credential Phishing Hits AI Experts

Do Son October 2, 2026 0
Read More Read more about China-Aligned TA419 Credential Phishing Hits AI Experts
Phishing Abuses RMM Tools for Persistent Network Access CoreRAT malware decoy PDF used in Core Werewolf phishing attack on Russian defense targets
  • Cybercriminals

Phishing Abuses RMM Tools for Persistent Network Access

Do Son October 2, 2026 0
Read More Read more about Phishing Abuses RMM Tools for Persistent Network Access
SOC as a Service: A Practical Guide to Outsourcing Your Security Operations Center AISelect_20261002_114950_Docs
  • Technique

SOC as a Service: A Practical Guide to Outsourcing Your Security Operations Center

Do Son October 2, 2026 0
Read More Read more about SOC as a Service: A Practical Guide to Outsourcing Your Security Operations Center
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
πŸ“ˆ

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

πŸ›‘οΈ

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

πŸ™

GitHub Issues
Auto-create alert tickets without duplication.

πŸ“¬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

πŸ”€

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days β†’

🚨 Active Exploits in the Wild

  • CVE-2026-102255CVSS 10.0
    A Pre-authentication SSRF vulnerability exists in the SMA1000 Appliance Work Place interface due to an unintended alternate access...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2026-105133CVSS 6.9
    A vulnerability was detected in Ahsay AhsayCBS up to 10.3.2. This affects the function checkSysPwd of the file...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2023-22894CVSS 4.9
    Strapi through 4.5.5 allows attackers (with access to the admin panel) to discover sensitive user details by exploiting...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2016-3081CVSS 8.1
    Apache Struts 2.3.19 to 2.3.20.2, 2.3.21 to 2.3.24.1, and 2.3.25 to 2.3.28, when Dynamic Method Invocation is enabled,...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-3306CVSS 10.0
    The mod_copy module in ProFTPD 1.3.5 allows remote attackers to read and write to arbitrary files via the...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-5477CVSS 7.5
    named in ISC BIND 9.x before 9.9.7-P2 and 9.10.x before 9.10.2-P3 allows remote attackers to cause a denial...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2021-3199CVSS 9.8
    Directory traversal with remote code execution can occur in /upload in ONLYOFFICE Document Server before 5.6.3, when JWT...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2026-94504CVSS 7.2
    Ninja Forms 3.15.3 stores an anonymous non-RTE textarea value and renders it without safe HTML encoding in the...
    Admin intel📅 Updated: Oct 7, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-78533CVSS 9.8
    Unauthenticated PHP Object Injection in Qwery
    📅 Updated: Oct 10, 2026
  • CVE-2026-78535CVSS 9.8
    Unauthenticated PHP Object Injection in Photolia
    📅 Updated: Oct 10, 2026
  • CVE-2026-81797CVSS 9.8
    Unauthenticated PHP Object Injection in Buzz Stone | Magazine & Viral Blog WordPress Theme
    📅 Updated: Oct 10, 2026
  • CVE-2026-66567CVSS 9.8
    Unauthenticated PHP Object Injection in Anesta
    📅 Updated: Oct 10, 2026
  • CVE-2026-66568CVSS 9.8
    Unauthenticated PHP Object Injection in Original
    📅 Updated: Oct 10, 2026
  • CVE-2026-66569CVSS 9.8
    Unauthenticated PHP Object Injection in Kicker
    📅 Updated: Oct 10, 2026
  • CVE-2026-78529CVSS 9.8
    Unauthenticated PHP Object Injection in Alliance
    📅 Updated: Oct 10, 2026
  • CVE-2026-78531CVSS 9.8
    Unauthenticated PHP Object Injection in Jacqueline
    📅 Updated: Oct 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
Β© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.