 Do Son
TL;DR
On November 13, 2026, Rapid7’s managed detection team caught attackers exploiting CVE-2026-90436 against a customer’s Atlassian Confluence Data Center server. This Confluence Data Center RCE stems from a flaw in Apache Axis 1.x, an old SOAP library bundled with the product. N-able reported attacks against N-central on the same day for a flaw that “strongly correlates” with the same bug.
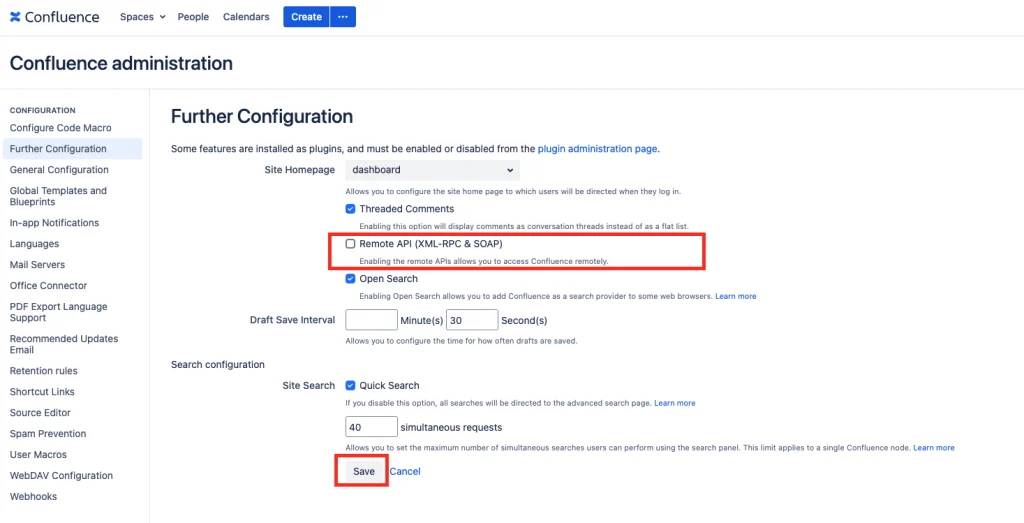
CVE-2026-90436 lets an unauthenticated attacker run code on servers that use Apache Axis 1.x. Confluence Data Center is exposed only when its “Remote API (XML-RPC & SOAP)” setting is on. Upgrade to Confluence 9.2.28 or a 10.x release, or turn the remote API off.
- CVE: CVE-2026-90436
- CVSS: 9.8 (Critical · CVSSv3)
- Product: Apache Software Foundation Apache Axis 1.x (EOL)
- Affected: ≤ 1.4, aac718c6035435d96b39d6aebb9c078a13af7cc8
- Impact: Apache Axis 1.x (EOL): unauthenticated remote class instantiation via SOAP fault exceptionName
- Status: Exploited in the wild
- Patched in: 41f3b4e8d04e310ca81f86b92630ab2c11d608bd
- EPSS: 1.1% (30-day)
- Action: Update to 41f3b4e8d04e310ca81f86b92630ab2c11d608bd now
Why It Matters
Confirmed Attacks on Two Products
Exploitation is no longer theoretical. According to the Rapid7 report, “CVE-2026-90436 is now being actively exploited in the wild against both known affected products.” As a result, Rapid7 recommends “remediating exposed systems on an emergency basis outside of normal patching cycles.”
A Public Exploit Already Exists
Rapid7 also notes that a proof-of-concept exploit targeting N-central appeared on November 12. It was part of a series of public zero-day disclosures against N-central. Researcher Sean Bales published those exploits in a GitHub repository called Able2Shell.
No Upstream Fix
Apache Axis 1.x reached end of life long ago. Consequently, Apache does not plan a fixed 1.x release. Instead, it recommends moving to another SOAP engine, such as Apache Axis 2, or applying its patch to an Axis 1.x build.
How the Attack Works
The flaw is an unsafe reflection bug (CWE-470) in how Axis handles inbound SOAP fault messages. The Apache CVE record explains that Axis loads a class named inside the fault, then creates it, “before checking that it is an AxisFault.”
Loading a class alone runs its startup code. With a suitable class on the application’s classpath, that leads to remote code execution. Notably, Axis parses the fault before any per-service checks, so no login is needed. CISA has scored the flaw 9.8.
Affected Versions
Confluence Data Center
Atlassian lists Confluence Data Center 1.x through 9.x as affected, but only with “Remote API (XML-RPC & SOAP)” enabled. That setting has been off by default for new installations since Confluence 3.0. However, older sites upgraded over the years may still have it on.
Confluence 10.0 removed the feature entirely, so 10.x is not affected. Atlassian Cloud sites are also safe.
N-able N-central
Some N-central versions bundle the affected Axis library. Rapid7 says N-central also needs a non-default setting to be vulnerable.
Other Software
Apache Axis 1.x through 1.4 is affected wherever it runs. Therefore, any in-house Java application that still uses Axis 1.x may face the same Confluence Data Center RCE risk.
Patch and Mitigation
Confluence
Upgrade to Confluence Data Center 9.2.28 or a current 10.x release. If you must wait, the Atlassian security advisory explains how to clear the “Remote API (XML-RPC & SOAP)” checkbox in General Configuration. The change takes effect without a restart. Still, scripts, automations and add-ons that use the API may stop working.
N-central and Others
- N-central customers should follow N-able’s latest hotfix guidance.
- Teams with in-house Axis 1.x code should move to Axis 2 or apply Apache’s patch.
- Prioritize internet-facing servers with the SOAP APIs enabled.
Check for Compromise
Atlassian warns that it “cannot confirm if your instances have been affected by this vulnerability.” Investigate any server that had the API exposed, even after you patch.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
