EC-CUBE AmazonPay Plugin Vulnerability CVE-2026-103671 Actively Exploited in the Wild to Steal Account Data
 Do Son
TL;DR
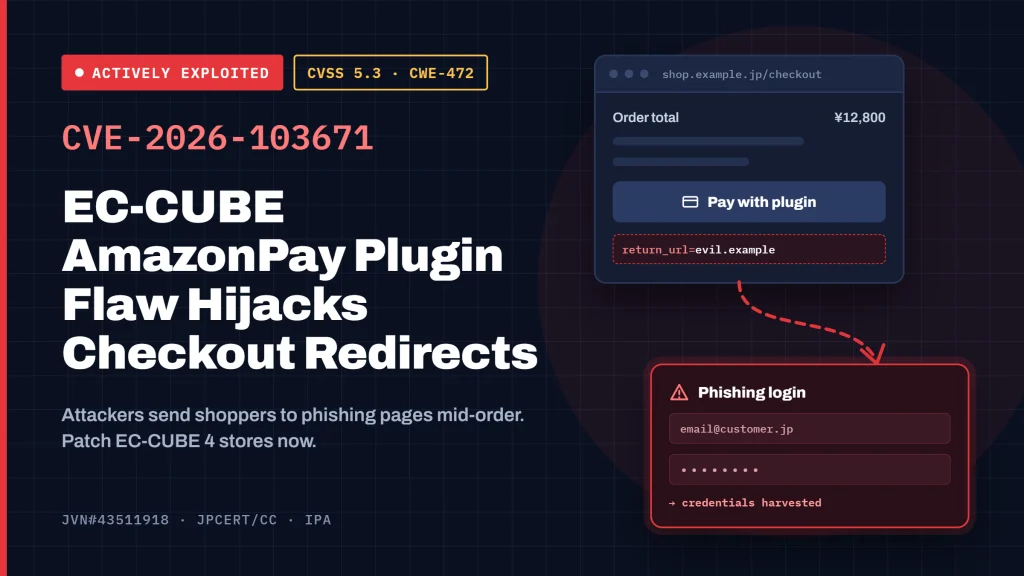
JPCERT/CC, IPA, and EC-CUBE CO.,LTD. warned that threat actors are actively exploiting CVE-2026-103671 in the wild. This EC-CUBE AmazonPay Plugin vulnerability allows unauthenticated attackers to manipulate web parameters and redirect online shoppers to malicious websites. Store administrators running EC-CUBE 4 series must apply the vendor patch immediately to protect customer accounts.
- CVE: CVE-2026-103671
- CVSS: 5.3 (Medium · CVSSv4)
- Product: EC-CUBE CO.,LTD. AmazonPay V2 Plugin (4.0/4.1 series)
- Affected: v1.1.7, v1.0.0, v4.3.1, v4.2.3, v4.2.0, ≤ v1.3.0
- Status: Exploited in the wild
- EPSS: 0.2% (30-day)
- Action: See vendor advisory
Why CVE-2026-103671 Matters for Online Retailers
EC-CUBE powers thousands of e-commerce storefronts across Japan, making payment extensions a primary target for credential harvesting. According to the official JVN#43511918 advisory from JPCERT/CC and IPA, “the developer states that attacks exploiting the vulnerability has been observed.” Although the flaw carries a Medium severity rating (CVSS v4.0 score of 5.3 and CVSS v3.0 score of 4.7), real-world exploitation puts customer payment workflows at immediate risk. However, neither JPCERT/CC nor the vendor has confirmed public proof-of-concept exploit code.
How the EC-CUBE AmazonPay Plugin Attack Works
External Control of Assumed-Immutable Web Parameters
Tracked under CWE-472, the flaw stems from external control of an assumed-immutable web parameter inside the EC-CUBE AmazonPay Plugin. Specifically, the payment module fails to validate sensitive checkout parameters that the server assumes a client browser cannot alter. Consequently, a remote attacker can tamper with checkout requests without prior authentication and with low attack complexity.
Malicious Checkout Redirection
When a shopper interacts with a manipulated payment link during checkout, the application processes the altered parameter value. As the advisory notes, “the user may be redirected to an arbitrary website during the ordering process. As a result, user’s account information may be obtained.” Attackers use these rogue redirects to display phishing pages that capture login credentials and personal data.
Affected Products and Versions
Based on both JVN#43511918 and the MITRE CVE record, CVE-2026-103671 impacts multiple plugin releases for the EC-CUBE 4 series:
- AmazonPay V2 Plugin (4.0/4.1 series): versions v1.0.0 through v1.1.6, and v1.1.7 through v1.1.12.
- AmazonPay V2 Plugin (4.2/4.3 series): versions v4.2.0 through v4.2.2, v4.2.3 through v4.3.1, and v4.3.1 (Bundle Edition).
- AmazonPay Plugin CV1 (4.0 series): version v1.3.0 and earlier.
Patch and Mitigation Steps
To remediate this EC-CUBE AmazonPay Plugin vulnerability, JPCERT/CC advises administrators to “apply the patch according to the information provided by the developer.” Store owners should consult the official EC-CUBE security announcement and patch guide to update their payment extension or apply the code diff right away. Additionally, administrators should review web server logs for suspicious checkout redirects and alert potentially affected customers.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
