 Do Son
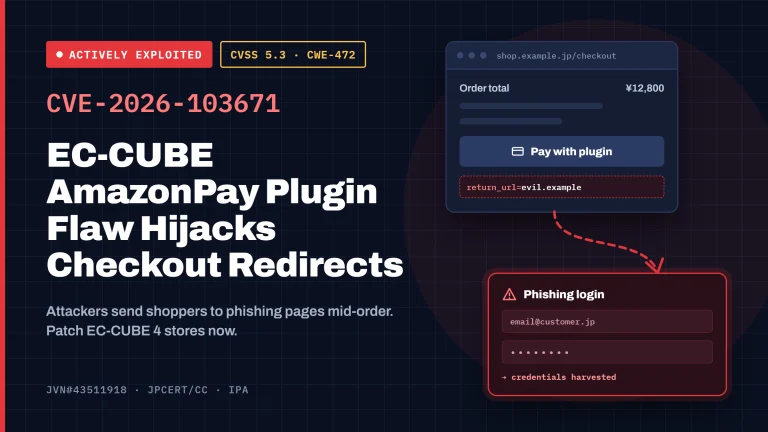
Attackers are exploiting CVE-2026-103671 in the wild, an EC-CUBE AmazonPay Plugin vulnerability that redirects shoppers to steal account credentials.
JPCERT
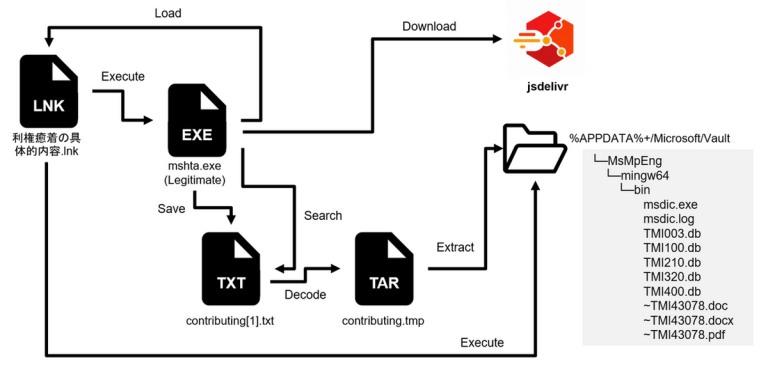
JPCERT/CC details new APT-C-60 attacks on Japan. The group abuses Proton Drive, LNK files, and GitHub to deploy SpyGlace malware.

A Critical RCE flaw (CVE-2025-61932, CVSS 9.8) in Lanscope Endpoint Manager (v9.4.7.1 and earlier) is actively exploited via malicious packets.

JPCERT reports critical flaws in a-blog cms, including CVE-2025-36560 (CVSS 9.2). Attackers could hijack sessions and access sensitive data.

DslogdRAT malware exploited Ivanti Connect Secure via CVE-2025-0282, using web shells and C2 channels to evade detection and persist in networks.

Critical vulnerability (CVE-2025-42599) in Active! mail allows remote code execution. Update to the latest version immediately to protect your systems.