 Do Son
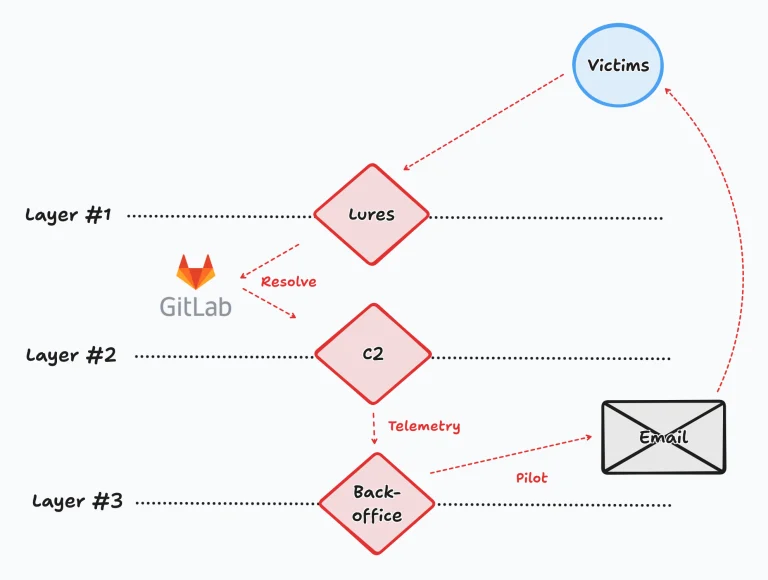
Stormshield exposed the North Korean Trigram campaign spoofing 50 Web3 and AI brands with ClickFix lures and GitLab relays to infect developers.
Latest Security News
Bitdefender exposes the NIKKE game launcher malware. See how the k2f-agent NIKKE game launcher malware hides in a log file to steal wallets and keys.
Copeland XWEB EVO flaw CVE-2026-124010 gives unauthenticated root and is exploited in the wild, alongside CVE-2026-124014. PoC details are public.
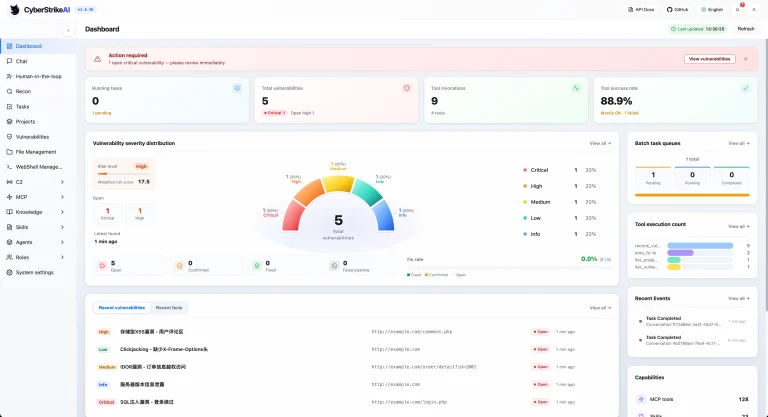
Elastic Security Labs uncovered a CyberStrikeAI AWS intrusion and CyberStrikeAI AWS CloudTrail intrusion that pulled 56 EC2 scripts in 141 milliseconds.
NoisyTCP vulnerability CVE-2026-99288 lets remote attackers panic Linux kernel TCP servers pre-auth. Patch to 6.12.117, 6.18.63 or 7.3.4.
Apache Shiro authentication bypass CVE-2026-129349 lets any password work after one login. Apache also fixes APISIX flaws like CVE-2026-124679.
TrustFall vulnerability CVE-2026-88235 PoC is public: any Windows user can abuse TrustedInstaller to act as SYSTEM. Install the November 2026 update.
Xen Orchestra authentication bypass VSA-2026-062 is exploited in the wild to gain admin and hijack XCP-ng hosts. Update to 6.10.1 or 6.9.2 now.
Zenitel vulnerabilities fixed: CVE-2026-95377 gives root on intercoms via DHCP, and a CVE-2026-95615 chain roots Zenitel Connect. Update to 1.11.0.
Cursor details its October breach in a new Cursor security incident update. See how the Fireworks Cursor security incident poisoned the marketplace cache.
PLANET Technology fixed two PLANET GS-5220-8P2T2S vulnerabilities, CVE-2026-109445 and CVE-2026-2336, in firmware v3.2412b261022. Update switches now.
Latest Technology News
Microsoft introduced an Outlook DMARC email rejection rule, bouncing messages lacking DMARC records with the 550 5.7.1 authentication error.
Google announced the Firebase Studio shutdown for March 2027, urging developers to migrate project workspaces and export AI conversation histories.
A bug involving AMD driver SSD writes causes atieclxx.exe to constantly write gigabytes to storage drives during idle states, prompting an AMD fix.

Key takeaways Managed IT support affects customers directly, because most service channels now run on the same...
Introduction Few large companies run on one neat system any more. A typical firm juggles cloud servers,...
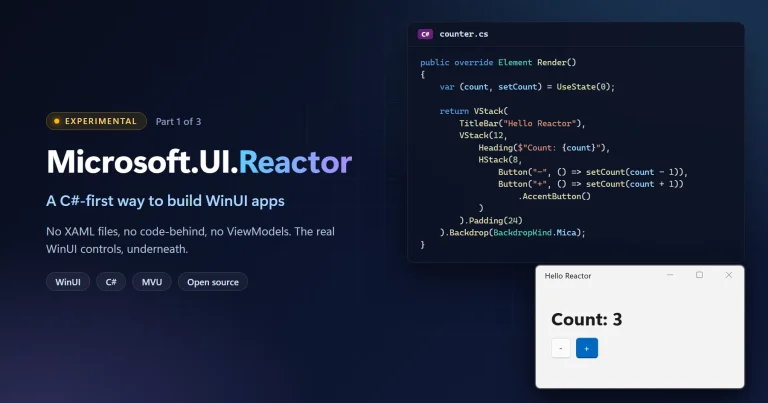
A modern WinUI Registry Editor prototype surfaced in a Microsoft repo, offering a sleek glimpse into potential Windows 11 interface redesigns.
Apple plans an Apple proactive Siri agent for iOS 28, leveraging native App Intents and overhauled development cycles to challenge rivals.
Our weekly CVE report for Nov 2-8, 2026 tracks 3,570 new CVEs and 10 exploited vulnerabilities, including Siemens and Zyxel flaws not in CISA KEV.

Key Takeaways Every platform in this category promises to surface what actually matters, and from a website...

Ask an AI assistant how to mitigate a newly disclosed CVE, or which endpoint protection vendor to...
Latest Security News
Wiz, Sentra, and Mandiant uncovered a supply chain attack abusing Qubole cross-account access and Qubole AWS cross-account access roles to steal S3 data.
Kaspersky uncovers Citrus Ransomware hitting Russian firms. See how the Sn00py Citrus Ransomware group uses VLESS tunnels, Certighost, and LLM scripts.
PostgreSQL security update 18.7 fixes 52 CVEs, including CVE-2026-6460 and 31 other code execution flaws. PostgreSQL 14 reaches end of life.
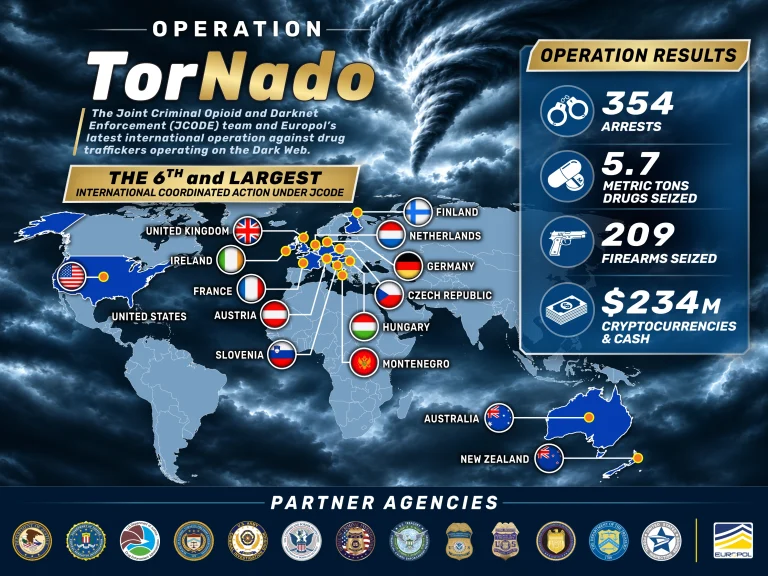
The DOJ and Europol arrested 354 suspects and seized $234M in the Operation TorNado dark web crackdown on fentanyl and opioid vendors.
ManageEngine critical vulnerabilities fixed: CVE-2026-12591 (CVSS 9.9) in M365 Manager Plus, CVE-2026-12507 RCE in ServiceDesk Plus, DDI Central flaws.
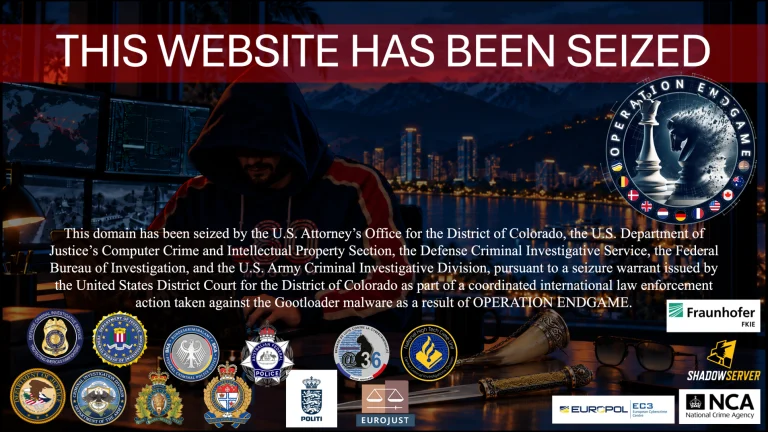
The DOJ and FBI executed a Gootloader malware takedown, wiping the botnet from 100+ WordPress servers after 25,000 infections and $28.8M in losses.
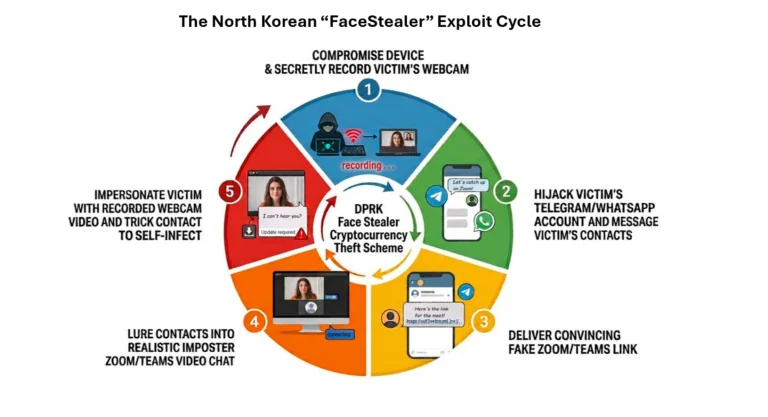
The DOJ and FBI disrupted the North Korea FaceStealer scheme after $400M in crypto thefts and seized $1.2B stolen in a $6B Binance exchange hack.
Red Hat Satellite vulnerabilities fixed: CVE-2026-107360 (CVSS 9.6) sandbox bypass leads 21 new Red Hat CVEs across Satellite, RHEL and Ansible.
Gradle 9.9.1 and 8.14.7 fix three Gradle vulnerabilities, including a CVSS 9.3 version catalog code injection that runs during builds and IDE sync.
Mitel fixes three MiVoice MX-ONE vulnerabilities, including a CVSS 9.4 authentication bypass and command injection. Apply 8.2 SP1 HF2 now.
Plone fixes an anonymous Plone remote code execution chain rated CVSS 9.8. Update to 6.2.3, 6.1.6 or 6.0.16, or install the Plone hotfix.
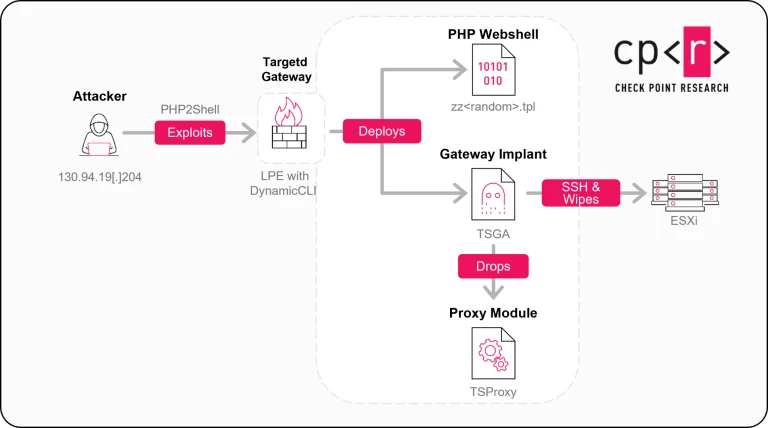
Check Point Gateway vulnerability CVE-2026-123039 exploited with PHP2Shell to gain root, plant backdoors and wipe ESXi. Patch to R82.20 Take 14.
Latest Technology News
Google announced the Firebase Studio shutdown for March 2027, urging developers to migrate project workspaces and export AI conversation histories.
A bug involving AMD driver SSD writes causes atieclxx.exe to constantly write gigabytes to storage drives during idle states, prompting an AMD fix.
Key takeaways Managed IT support affects customers directly, because most service channels now run on the same...
Introduction Few large companies run on one neat system any more. A typical firm juggles cloud servers,...
A modern WinUI Registry Editor prototype surfaced in a Microsoft repo, offering a sleek glimpse into potential Windows 11 interface redesigns.
Apple plans an Apple proactive Siri agent for iOS 28, leveraging native App Intents and overhauled development cycles to challenge rivals.
Our weekly CVE report for Nov 2-8, 2026 tracks 3,570 new CVEs and 10 exploited vulnerabilities, including Siemens and Zyxel flaws not in CISA KEV.
Key Takeaways Every platform in this category promises to surface what actually matters, and from a website...
Ask an AI assistant how to mitigate a newly disclosed CVE, or which endpoint protection vendor to...
Alphabet disclosed a $548M Alphabet Qualcomm stake, highlighting Qualcomm's strategic pivot into AI data centers amid handset revenue declines.