SOC as a Service: A Practical Guide to Outsourcing Your Security Operations Center
 Do Son
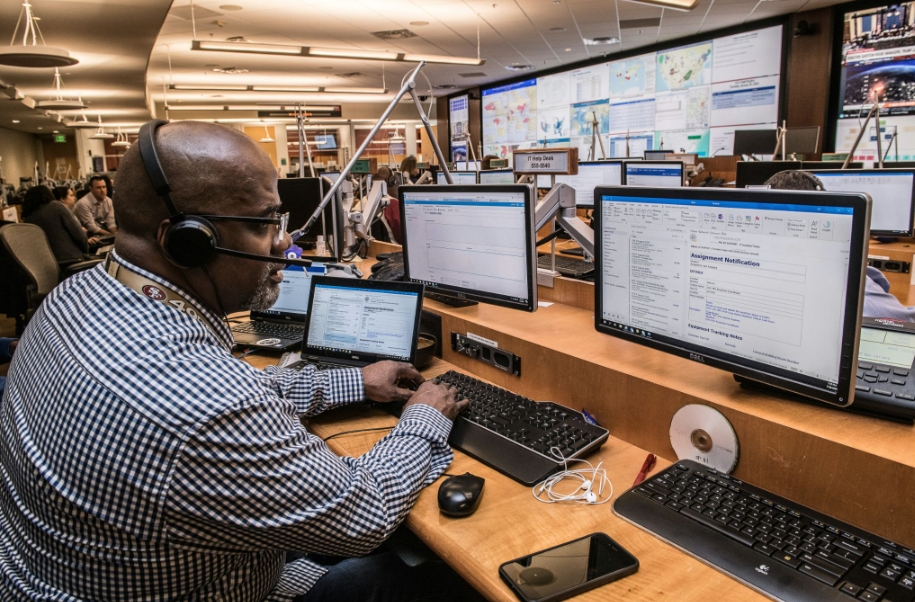
SOC as a Service (SOCaaS) lets organizations outsource 24/7 threat monitoring, detection, and incident response to a specialized third-party team instead of building an in-house Security Operations Center. It gives businesses of any size access to trained analysts, enterprise-grade tools, and round-the-clock coverage without the multi-year buildout and payroll costs of an internal SOC.
What Is SOC as a Service?
SOC as a Service is a subscription-based cybersecurity model in which a third-party provider delivers the core functions of a Security Operations Center. This includes continuous monitoring, threat detection, alert triage, and incident response, all handled remotely by the provider’s analysts.
A traditional in-house SOC requires specialized staff, licensed tools, and a dedicated facility that can take years to assemble properly. Many organizations simply cannot justify that investment, especially as skilled security talent remains scarce and expensive.
With SOCaaS, that entire operation is compressed into a service organizations can activate in weeks rather than years. The provider supplies the people, the platform, and the processes, while the client retains visibility and control over decisions that affect their business.
This arrangement suits companies of every size. Small and mid-sized businesses gain enterprise-level protection they could never staff internally, while larger enterprises use it to extend existing security teams or cover gaps during nights, weekends, and holidays.
SOC as a Service vs. MSSP
SOC as a Service is often confused with a traditional Managed Security Service Provider, though the two are not identical. An MSSP historically focused on managing security tools and forwarding alerts, while SOCaaS typically includes deeper investigation and hands-on response.
The line between the two has blurred in recent years as MSSPs add investigation and response capabilities of their own. When evaluating a provider, it is more useful to ask exactly what actions they take during an incident than to rely on the label they use.
What Does a Managed SOC Actually Cover?
A capable managed SOC is expected to protect the full scope of an organization’s digital footprint. That includes endpoints, servers, cloud workloads, email systems, and any third-party applications connected to the network.
The scope has expanded significantly as organizations move more workloads to hybrid and multi-cloud environments. A managed SOC worth choosing today should demonstrate equally strong visibility across on-premises infrastructure and cloud-native platforms, not just traditional endpoints.
Continuous Monitoring and Detection
The foundation of any SOCaaS engagement is around-the-clock monitoring of logs, network traffic, and endpoint behavior. Analysts and automated tooling work together to flag anomalies before they escalate into serious incidents.
Alert Triage and Investigation
Not every alert represents a genuine threat, and sorting signal from noise is a core SOC function. A managed SOC investigates each flagged event, discards false positives, and prioritizes the incidents that pose real risk.
Incident Response and Containment
When a genuine threat is confirmed, the SOC team acts to contain it before it spreads further across the environment. This can mean isolating an infected endpoint, blocking malicious traffic, or terminating a suspicious process in real time.
Threat Hunting
Beyond reacting to alerts, mature SOCaaS providers proactively hunt for threats that automated tools might miss. This involves analyzing historical data and known attacker behavior to uncover hidden compromises before they cause damage.
Threat Intelligence Integration
A strong managed SOC feeds its detection engine with threat intelligence gathered from across its entire client base and external research. This intelligence helps analysts recognize the fingerprints of known attacker groups and emerging malware campaigns faster than a single organization could on its own.
Providers with global sensor networks are particularly well positioned here, since they often observe new attack techniques before those techniques become widely known. ESET, for example, pairs a 24/7 human-led managed detection and response service with a telemetry network of more than 100 million sensors and 11 research and development centers, and reports a mean time to respond of six minutes. That early visibility can translate directly into faster detection for every client connected to the service.
Log Management and Forensics
Centralized log management is another core function of a managed SOC, since it creates the historical record needed to investigate an incident properly. Logs from endpoints, servers, firewalls, and cloud services are typically aggregated into a single platform the SOC team can search quickly.
When an incident does occur, that log history becomes essential for forensic investigation and root cause analysis. It also helps the organization demonstrate exactly what happened during an audit or a regulatory review.
Reporting and Compliance Support
Most managed SOCs also provide regular reporting on the organization’s security posture and any incidents handled during the period. This documentation is often essential for meeting frameworks such as ISO 27001, HIPAA, or the NIST Cybersecurity Framework.
Why Organizations Are Outsourcing Their SOC
The decision to outsource usually comes down to a mix of cost, expertise, and speed. A few of the most common drivers include the following.
- Access to scarce talent. The global cybersecurity skills shortage makes it difficult to hire and retain qualified analysts, and a managed SOC provides that expertise on demand.
- Lower total cost of ownership. Sharing infrastructure, tooling, and staff across many clients allows providers to offer enterprise-grade protection at a fraction of the cost of building it internally.
- Faster time to protection. A SOCaaS engagement can typically go live in weeks, compared to the years it can take to stand up an internal SOC from scratch.
- Broader threat visibility. Providers monitor threats across many client environments simultaneously, which often means they spot emerging attack patterns before a single in-house team would.
- Scalability. As the business grows or its risk profile changes, a managed SOC can scale coverage up or down without the organization having to hire or lay off staff.
These advantages explain why SOCaaS has grown from a niche offering into a mainstream part of enterprise and SMB security strategy alike. Even organizations with existing security teams increasingly use SOCaaS to fill coverage gaps rather than replace their staff entirely.
Common Challenges When Outsourcing a SOC
Outsourcing a SOC is not without friction, and organizations should go in with realistic expectations. Handing detection and response to an outside team means accepting some loss of direct, hands-on control over daily security operations.
Communication can also become a challenge if the provider and the internal team are not aligned on escalation procedures. Establishing clear protocols for what gets escalated, and how quickly, prevents confusion during an actual incident.
Vendor lock-in is another factor worth considering before signing a long-term contract. Organizations should confirm what happens to their data and configurations if they decide to switch providers or bring the SOC function back in-house later.
Build vs. Outsource: A Quick Comparison
| Factor | In-House SOC | SOC as a Service |
| Time to launch | Months to years | Weeks |
| Upfront cost | High (staff, tools, facility) | Low to moderate (subscription-based) |
| Staffing burden | Ongoing recruitment and retention | Handled by the provider |
| Coverage | Dependent on internal headcount | 24/7 by design |
| Scalability | Slow and resource-intensive | Flexible and fast |
Who Should Consider SOC as a Service?
SOC as a Service tends to make the most sense for organizations that lack the budget or headcount to run security operations around the clock. This covers a wide range of companies, from early-stage startups handling sensitive customer data to established mid-market firms operating without a dedicated security team.
It also fits larger enterprises that already run some security functions internally but need to close specific gaps. A common pattern is using SOCaaS to cover after-hours monitoring while the internal team focuses on strategy, architecture, and daytime response.
Regulated industries such as healthcare, finance, and legal services often benefit the most from this model. These sectors face strict compliance obligations alongside a high volume of sensitive data, and a managed SOC helps meet both requirements simultaneously.
How to Evaluate a SOC as a Service Provider
Not all managed SOC providers operate at the same level, so the evaluation process matters as much as the decision to outsource. Start by examining how deeply the provider’s tools integrate with your existing infrastructure and whether that integration creates any performance overhead.
Ask about the provider’s typical client profile and whether they have direct experience with organizations of your size and industry. A provider built primarily for large enterprises may not offer the right fit or pricing structure for a smaller business, and the reverse is also true.
The quality of the analysts behind the service deserves close attention as well. Look into their certifications, training, and how quickly they can move from detection to actual containment during a live incident.
Speed matters more than almost any other factor in this evaluation. Providers such as ESET combine round-the-clock human-led monitoring with global threat intelligence to bring detection and response times down to just minutes rather than hours or days.
It is also worth confirming what happens after an alert is triaged. Some providers stop at notification, while others include full containment, remediation guidance, and digital forensics as part of the standard engagement.
Making the Decision
Outsourcing a SOC is less about giving up control and more about accessing capabilities that would otherwise be out of reach. For most small and mid-sized businesses, and even many enterprises, the math favors a managed approach over a multi-year internal build.
The right provider should feel like an extension of the internal team rather than a black box handling alerts somewhere offsite. Clear reporting, fast response times, and proven expertise are the qualities worth prioritizing above any single feature on a datasheet.
Ultimately, the goal is continuous, reliable protection rather than a checkbox on a compliance form. A well-chosen SOCaaS partner delivers that protection while freeing internal teams to focus on the strategic work only they can do.
Frequently Asked Questions
What is SOC as a Service? SOC as a Service is a subscription model where a third-party provider delivers threat monitoring, detection, and incident response on behalf of an organization. It replicates the function of an in-house Security Operations Center without requiring the client to build or staff one.
Is SOCaaS suitable for small businesses? Yes, SOCaaS is often the only realistic way for small and mid-sized businesses to access 24/7 security monitoring. It removes the need to hire a dedicated internal team while still delivering enterprise-grade protection.
How is SOC as a Service different from MDR? The terms overlap significantly, and many providers use them interchangeably. In general, MDR emphasizes detection and response around endpoints and networks, while SOCaaS often implies a broader, more holistic security operations function.
How quickly can a SOCaaS provider respond to a threat? Response times vary by provider, but leading services aim to move from detection to initial action within minutes rather than hours. This speed is one of the clearest advantages over a smaller internal team managing alerts alone.