Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
ASUSTOR Fixes Critical ADM Flaw CVE-2026-105324 That Lets Attackers Read NAS Files Without Login ASUSTOR ADM vulnerability CVE-2026-105324 unauthenticated arbitrary file read on NAS fixed in ADM 5.1.4.RM62 and 4.3.3.RY62
  • Vulnerability Report

ASUSTOR Fixes Critical ADM Flaw CVE-2026-105324 That Lets Attackers Read NAS Files Without Login

Do Son October 7, 2026 0

Critical ASUSTOR ADM vulnerability CVE-2026-105324 (CVSS 9.2) allows unauthenticated arbitrary file read on NAS devices. Update ADM now.
HPE Fixes Six Critical AOS-Switch Flaws Enabling Unauthenticated RCE and Admin Access HPE AOS-Switch vulnerabilities CVE-2026-76744 and CVE-2026-76742 unauthenticated remote code execution and authentication bypass fixed in AOS-S 16.11.0032
  • Vulnerability Report

HPE Fixes Six Critical AOS-Switch Flaws Enabling Unauthenticated RCE and Admin Access

Do Son October 7, 2026 0

Nine HPE AOS-Switch vulnerabilities, including unauthenticated RCE flaw CVE-2026-76744 (CVSS 9.8), are fixed. Upgrade to AOS-S 16.11.0032.
Handlebars.js RCE Flaws Disclosed With Public PoC, Threatening 172 Million Monthly Downloads Handlebars.js vulnerability CVE-2026-106445 and CVE-2026-106446 remote code execution flaws with public PoC fixed in version 4.7.10
  • Vulnerability Report

Handlebars.js RCE Flaws Disclosed With Public PoC, Threatening 172 Million Monthly Downloads

Do Son October 7, 2026 0

Two Handlebars.js vulnerability disclosures (CVE-2026-106445, CVE-2026-106446) enable RCE. Details and PoC are public. Update to 4.7.10 now.
Chrome 155 Security Update Fixes 247 Flaws, Including Four Critical Use-After-Free Bugs Chrome 155 security update fixes 247 flaws including critical use after free bugs CVE-2026-106382 and CVE-2026-106197
  • Vulnerability Report

Chrome 155 Security Update Fixes 247 Flaws, Including Four Critical Use-After-Free Bugs

Do Son October 7, 2026 0

The Chrome 155 security update fixes 247 flaws, including critical use after free bugs CVE-2026-106382 and CVE-2026-106197. Update now.
Arista Fixes Critical CloudVision CUE Flaw CVE-2026-102159 and Five More Bugs Arista CloudVision CUE vulnerability CVE-2026-102159 unauthenticated access flaw in CV-CUE backend fixed in WiFi 2026.2.1
  • Vulnerability Report

Arista Fixes Critical CloudVision CUE Flaw CVE-2026-102159 and Five More Bugs

Do Son October 7, 2026 0

Critical Arista CloudVision CUE vulnerability CVE-2026-102159 (CVSS 9.8) and five more flaws hit CV-CUE. Update to WiFi 2026.2.1 now.
HPE Patches 28 ClearPass Policy Manager Flaws, Including Unauthenticated RCE Bugs HPE ClearPass Policy Manager vulnerabilities CVE-2026-76750 and CVE-2026-76752 unauthenticated RCE and authentication bypass fixed in CPPM 6.14.1
  • Vulnerability Report

HPE Patches 28 ClearPass Policy Manager Flaws, Including Unauthenticated RCE Bugs

Do Son October 7, 2026 0

HPE fixes 28 ClearPass Policy Manager vulnerabilities, including unauthenticated RCE flaw CVE-2026-76750 (CVSS 9.8). Upgrade to CPPM 6.14.1.
Veeam Patches Critical Backup & Replication RCE Flaw CVE-2025-64393 and Two More Bugs Veeam Backup vulnerability CVE-2025-64393 remote code execution fixed in build 12.3.2.4934
  • Vulnerability Report

Veeam Patches Critical Backup & Replication RCE Flaw CVE-2025-64393 and Two More Bugs

Do Son October 6, 2026 0

Critical Veeam Backup vulnerability CVE-2025-64393 (CVSS 9.4) enables RCE by low-privileged users. Update to 12.3.2 P4 now.
WordPress 7.1.3 Security Update Fixes Stored XSS, SQL Injection and Five More Flaws WordPress 7.1.3 security update fixing stored XSS and SQL injection in WordPress security release
  • Vulnerability Report

WordPress 7.1.3 Security Update Fixes Stored XSS, SQL Injection and Five More Flaws

Do Son October 6, 2026 0

The WordPress 7.1.3 security update is a WordPress security release that fixes stored XSS, SQL injection and more. Update your site now.
SonicWall Patches CVSS 10 Pre-Auth SSRF Flaw and Three More Bugs in SMA1000 Appliances SonicWall SMA1000 vulnerability CVE-2026-102255 pre-authentication SSRF with CVE-2026-102256 and CVE-2026-102257
  • Vulnerability Report

SonicWall Patches CVSS 10 Pre-Auth SSRF Flaw and Three More Bugs in SMA1000 Appliances

Do Son October 6, 2026 0

SonicWall SMA1000 vulnerability CVE-2026-102255 (CVSS 10) allows pre-auth SSRF. Three more flaws fixed. Upgrade to 12.5.0-03082 now.
Progress Fixes Critical Command Injection Flaw CVE-2026-91140 in DataDirect AI Model Generator Agents Progress DataDirect vulnerability CVE-2026-91140 command injection in Autonomous REST Connector AI Model Generator agents
  • Vulnerability Report

Progress Fixes Critical Command Injection Flaw CVE-2026-91140 in DataDirect AI Model Generator Agents

Do Son October 6, 2026 0

Progress DataDirect vulnerability CVE-2026-91140 enables command injection via crafted OpenAPI files in AI agents. Pull version 2.1 now.
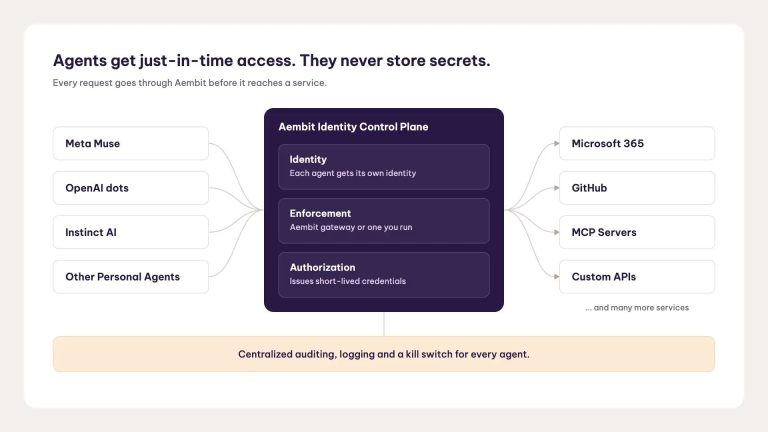
Aembit Extends Access Controls to Personal AI Agents Aembit_Control_Plane_Video_V1_1791234426vgaCNFRKd6
  • Press Release

Aembit Extends Access Controls to Personal AI Agents

cybernewswire October 6, 2026 0
Silver Springs, United States / Maryland, 6th October 2026, CyberNewswire
Read More Read more about Aembit Extends Access Controls to Personal AI Agents
Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management govware_001_1790666482q1kAoPtquQ
  • Press Release

Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management

cybernewswire October 6, 2026 0
Torrance, Californina, 6th October 2026, CyberNewswire
Read More Read more about Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management
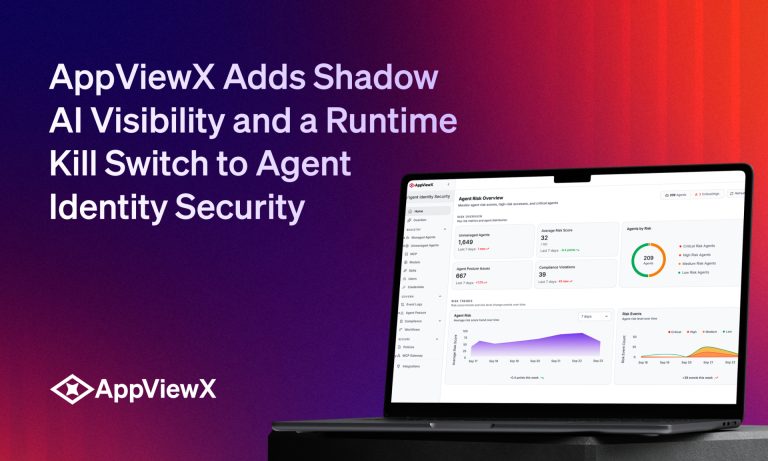
AppViewX Adds Shadow AI Visibility and a Runtime Kill Switch to Agent Identity Security PR_Banner_17912262302FpkG0rOrt
  • Press Release

AppViewX Adds Shadow AI Visibility and a Runtime Kill Switch to Agent Identity Security

cybernewswire October 6, 2026 0
New York, New York, 6th October 2026, CyberNewswire
Read More Read more about AppViewX Adds Shadow AI Visibility and a Runtime Kill Switch to Agent Identity Security
Murrelektronik Will Not Fix Critical AAS Edge Client Flaw CVE-2026-94293, Urges Removal AAS edge client vulnerability CVE-2026-94293 missing authentication in Murrelektronik aas-edge-client reference implementation
  • Vulnerability Report

Murrelektronik Will Not Fix Critical AAS Edge Client Flaw CVE-2026-94293, Urges Removal

Do Son October 6, 2026 0

Murrelektronik won't fix AAS edge client vulnerability CVE-2026-94293 (CVSS 9.8), which allows unauthenticated data changes. Remove it now.
Why Emerging Tech Hubs Are Ideal for Custom Web Development Outsourcing tech-laun
  • Technique

Why Emerging Tech Hubs Are Ideal for Custom Web Development Outsourcing

Do Son October 6, 2026 0
The global tech landscape in 2026 is facing a significant challenge. With a severe tech talent shortage...
Read More Read more about Why Emerging Tech Hubs Are Ideal for Custom Web Development Outsourcing
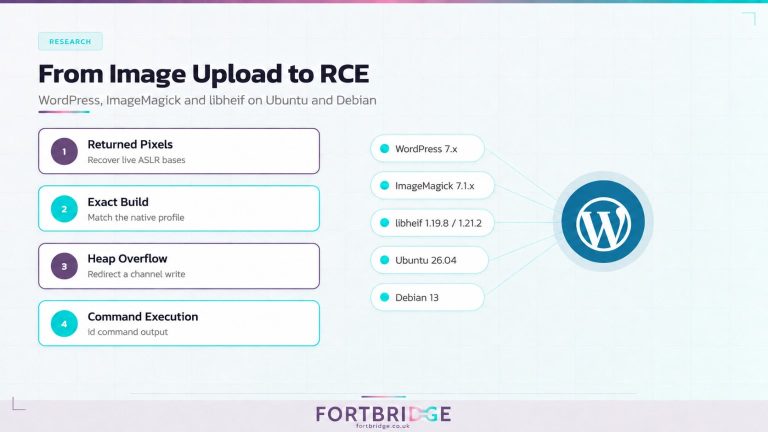
Researchers Publish Full Details and PoC Exploit for a WordPress libheif RCE Chain WordPress libheif RCE chain exploiting GHSA-x8r2-mggj-j6wr heap overflow via authenticated HEIC image upload
  • Vulnerability Report

Researchers Publish Full Details and PoC Exploit for a WordPress libheif RCE Chain

Do Son October 6, 2026 0

A WordPress libheif RCE chain and its PoC are now public. The libheif vulnerability turns an HEIC upload into code execution. Patch to 1.23.3.
ClingSTUN Linux Backdoor Turns Unpatched IoT Devices Into Proxy Nodes Diagram showing the MemTensor MemOS compromise details and how the MemTensor MemOS compromise affects developers
  • Malware

ClingSTUN Linux Backdoor Turns Unpatched IoT Devices Into Proxy Nodes

Do Son October 6, 2026 0

The ClingSTUN backdoor hijacks unpatched IoT devices and hides in traffic to public STUN servers. Learn how it spreads and how to stop it.
Apple Safari Chrome Tracking: A New Antitrust Defense Tool Apple Safari Chrome tracking telemetry data analysis
  • Technology

Apple Safari Chrome Tracking: A New Antitrust Defense Tool

Do Son October 6, 2026 0

Apple introduces Safari Chrome tracking through telemetry to gather defensive data against Google for UK and EU antitrust investigations and DMA compliance.
Poland Launches Google Antitrust Investigation Over Media Pay Polish UOKiK officials launching a Google antitrust investigation into media copyright violations and AI search algorithm data transparency
  • Technology

Poland Launches Google Antitrust Investigation Over Media Pay

Do Son October 6, 2026 0

Discover why Poland initiated a massive Google antitrust investigation over media licensing, AI search features, and alleged copyright circumvention.
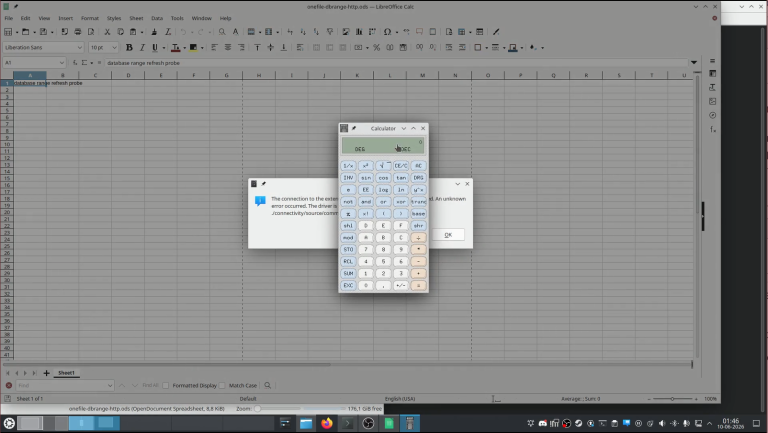
PoC Exploit and Technical Details Released for LibreOffice Calc Code Execution Flaw CVE-2026-63277 LibreOffice Calc vulnerability CVE-2026-63277 code execution with public PoC, plus file read and write flaws CVE-2026-63266 and CVE-2026-63267
  • Vulnerability Report

PoC Exploit and Technical Details Released for LibreOffice Calc Code Execution Flaw CVE-2026-63277

Do Son October 6, 2026 0

PoC released for LibreOffice Calc vulnerability CVE-2026-63277, which runs code when a file opens. Five more flaws fixed. Upgrade to 26.2.5.
OpenAI Text Watermarking Arrives Under the EU AI Act OpenAI text watermarking with textGrain detector for EU AI Act compliance
  • Technology

OpenAI Text Watermarking Arrives Under the EU AI Act

Do Son October 6, 2026 0

OpenAI text watermarking rolls out to ChatGPT and Codex in the EU under the EU AI Act, with opt-in API access and limited detector access.
Critical Atlassian Flaw CVE-2026-21589 Exposes Files in Jira, Confluence, Bitbucket and Five More Products Atlassian Data Center vulnerability CVE-2026-21589 arbitrary file access in Jira, Confluence, Bitbucket, Bamboo, Crowd, Fisheye and Crucible
  • Vulnerability Report

Critical Atlassian Flaw CVE-2026-21589 Exposes Files in Jira, Confluence, Bitbucket and Five More Products

Do Son October 6, 2026 0

Atlassian Data Center vulnerability CVE-2026-21589 (CVSS 9.3) allows arbitrary file access in Jira, Confluence and Bitbucket. Patch now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    📅 Updated: Oct 30, 2026
  • CVE-2023-22793CVSS 9.3
    A vulnerability allowing an unauthenticated attacker to perform remote code execution (RCE) on servers running the Veeam Virtualization...
    📅 Updated: Oct 29, 2026
  • CVE-2026-61707CVSS 9.0
    SOCFortress CoPilot focuses on providing a single pane of glass for all your security operations needs. Prior to...
    📅 Updated: Oct 29, 2026
  • CVE-2026-61645CVSS 9.1
    Docat is a tool for hosting versioned static documentation. In the affected implementation, an arbitrary file upload vulnerability...
    📅 Updated: Oct 29, 2026
  • CVE-2026-31158CVSS 9.8
    SQL Injection vulnerability in CRM SOFTTRADE Infotech (aka softtradeindia) 1.0 allows a remote attacker to execute arbitrary code...
    📅 Updated: Oct 29, 2026
  • CVE-2026-107032CVSS 9.1
    Insecure permissions in Bulk Share : Location Sender v2.1.0 (versionCode 5) allows unauthorized attackers to invoke an exported...
    📅 Updated: Oct 29, 2026
  • CVE-2024-8517CVSS 9.8
    SPIP before 4.3.2, 4.2.16, and 4.1.18 is vulnerable to a command injection issue. A remote and unauthenticated attacker...
    📅 Updated: Oct 29, 2026
  • CVE-2026-82854CVSS 9.3
    Nodemailer before 8.0.4 is vulnerable to SMTP command injection through the unsanitized envelope.size parameter. When an application passes...
    📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.