 Do Son
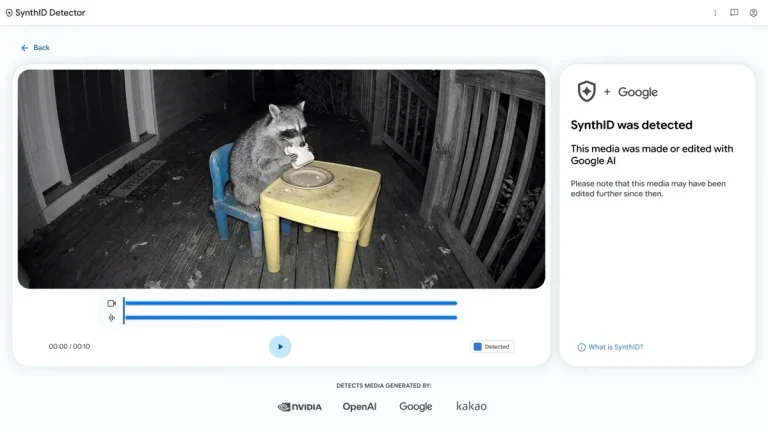
Discover how the new Google SynthID AI detector helps the public identify deepfakes and AI-generated content from top tech giants, including Apple.
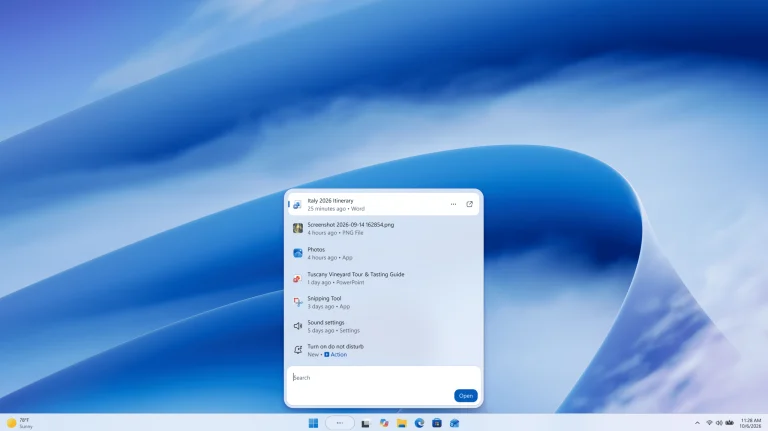
Discover how Windows Hybrid Intelligence transforms the search menu into an intent-driven AI hub, leveraging MXC sandboxes for unmatched local privacy.
Discover how the new Google Playground AI platform revolutionizes game creation, allowing anyone to build 3D multiplayer games using simple text prompts.
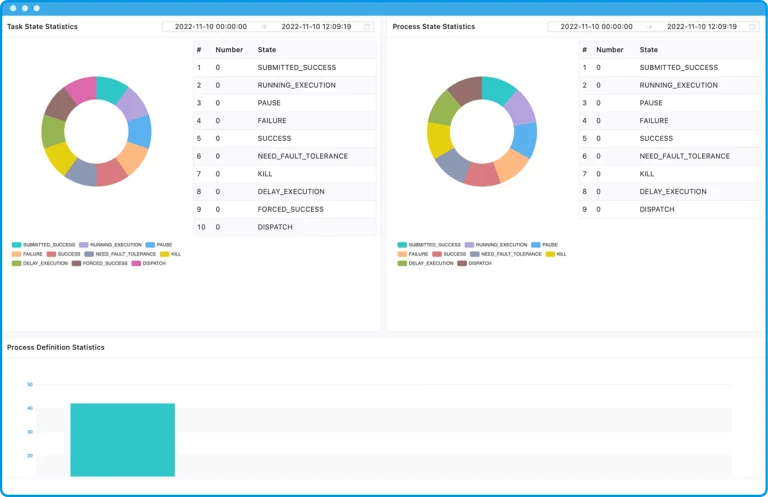
Six Apache DolphinScheduler vulnerabilities, including CVE-2026-71896 and Kubernetes credential leak CVE-2026-71895, are fixed in 3.4.3.
wolfSSH 1.6.0 fixes five wolfSSH vulnerabilities, including critical host key flaw CVE-2026-16516 and Windows login bug CVE-2026-83540.
A Cisco Finesse vulnerability, SSRF flaw CVE-2026-20362, has been publicly disclosed. Fixes arrive in early 2027, with no workarounds.
A VMware VMXNET3 vulnerability, CVE-2026-59346 (CVSS 9.3), allows VM escape. Full details and PoC exploit code are now public. Patch to 26H1u1.
Splunk fixes 22 Splunk Enterprise vulnerabilities, including critical Patroni API flaw CVE-2026-76268 and CVE-2026-76281. Upgrade to 10.4.3 now.

Discover top industrial IoT and embedded firmware development partners in Europe. Compare expertise in IIoT architecture, RTOS, and hardware integration.
An active WordPress XSS campaign exploits Ninja Forms flaw CVE-2026-94504 and CVE-2026-93836 to plant hidden admin accounts. Patch now.
Cisco License On-Prem vulnerabilities include CVSS 10 flaw CVE-2026-76482 and password reset bug CVE-2026-20328. APIC and Meraki also patched.
Cisco NX-OS vulnerabilities fixed, including critical NX-API RCE flaw CVE-2026-76471 and CVE-2026-76455, across Nexus, MDS and UCS gear. Patch now.
Four critical Cisco Nexus vulnerabilities, including CVE-2026-76485 and CVE-2026-76465 (CVSS 9.8), allow root RCE on NX-OS switches. Patch now.
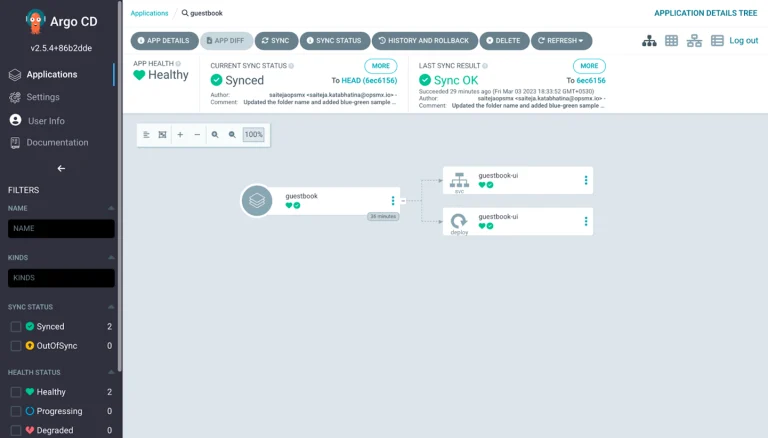
Four critical Argo CD vulnerabilities, including AppProject bypass CVE-2026-77459, threaten the repo-server and clusters. Upgrade to v3.5.4 now.
Two Apache Jackrabbit vulnerabilities, including critical session hijack flaw CVE-2026-92414 (CVSS 9.3), are fixed. Upgrade to 2.23.6 now.
A Gitea security update fixes 27 flaws, including SSRF bug CVE-2026-101027 and SSH key flaw CVE-2026-103059. Upgrade to Gitea 28.1.0 now.
eSentire tracks four clusters behind CVE-2026-88771 exploitation, planting NetScaler web shells and backdoor accounts. Learn how to detect them.
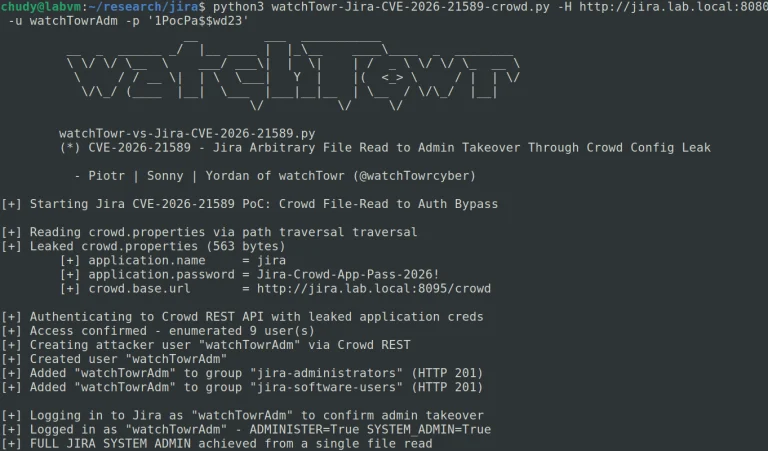
CVE-2026-21589 exploitation is underway against Atlassian servers after researchers published arbitrary file read PoC and technical details.
An Anthropic IPO draft seen by Reuters shows CEO Dario Amodei made $18 million in 2025, as the firm eyes a fall listing near $2 trillion.
Elastic fixes 14 Elastic Stack vulnerabilities, including Kibana flaw CVE-2026-102406 and Elasticsearch bug CVE-2026-103007. Upgrade now.
Four ASUS router vulnerabilities are fixed, including critical XSS flaw CVE-2026-14911 and code execution bug CVE-2026-19386. Update firmware now.
A ccTLD registry hijack of .gh, .sl, and .as let attackers obtain rogue TLS certificates. See how Chrome responded and how to check yours.