Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Veeam Patches Critical Backup & Replication RCE Flaw CVE-2025-64393 and Two More Bugs Veeam Backup vulnerability CVE-2025-64393 remote code execution fixed in build 12.3.2.4934
  • Vulnerability Report

Veeam Patches Critical Backup & Replication RCE Flaw CVE-2025-64393 and Two More Bugs

Do Son October 6, 2026 0

Critical Veeam Backup vulnerability CVE-2025-64393 (CVSS 9.4) enables RCE by low-privileged users. Update to 12.3.2 P4 now.
WordPress 7.1.3 Security Update Fixes Stored XSS, SQL Injection and Five More Flaws WordPress 7.1.3 security update fixing stored XSS and SQL injection in WordPress security release
  • Vulnerability Report

WordPress 7.1.3 Security Update Fixes Stored XSS, SQL Injection and Five More Flaws

Do Son October 6, 2026 0

The WordPress 7.1.3 security update is a WordPress security release that fixes stored XSS, SQL injection and more. Update your site now.
SonicWall Patches CVSS 10 Pre-Auth SSRF Flaw and Three More Bugs in SMA1000 Appliances SonicWall SMA1000 vulnerability CVE-2026-102255 pre-authentication SSRF with CVE-2026-102256 and CVE-2026-102257
  • Vulnerability Report

SonicWall Patches CVSS 10 Pre-Auth SSRF Flaw and Three More Bugs in SMA1000 Appliances

Do Son October 6, 2026 0

SonicWall SMA1000 vulnerability CVE-2026-102255 (CVSS 10) allows pre-auth SSRF. Three more flaws fixed. Upgrade to 12.5.0-03082 now.
Progress Fixes Critical Command Injection Flaw CVE-2026-91140 in DataDirect AI Model Generator Agents Progress DataDirect vulnerability CVE-2026-91140 command injection in Autonomous REST Connector AI Model Generator agents
  • Vulnerability Report

Progress Fixes Critical Command Injection Flaw CVE-2026-91140 in DataDirect AI Model Generator Agents

Do Son October 6, 2026 0

Progress DataDirect vulnerability CVE-2026-91140 enables command injection via crafted OpenAPI files in AI agents. Pull version 2.1 now.
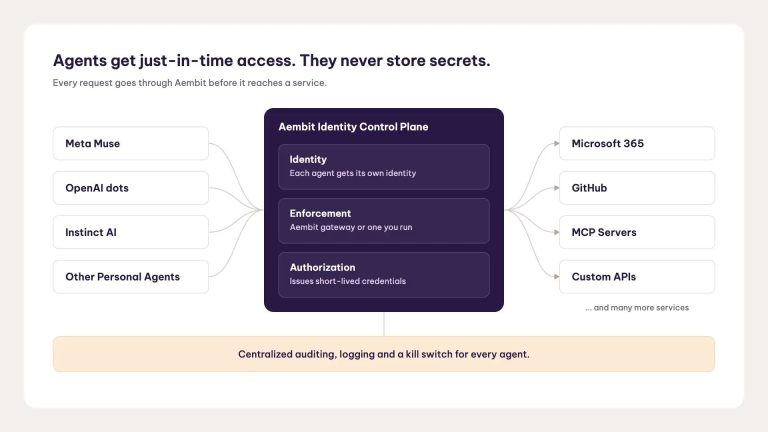
Aembit Extends Access Controls to Personal AI Agents Aembit_Control_Plane_Video_V1_1791234426vgaCNFRKd6
  • Press Release

Aembit Extends Access Controls to Personal AI Agents

cybernewswire October 6, 2026 0
Silver Springs, United States / Maryland, 6th October 2026, CyberNewswire
Read More Read more about Aembit Extends Access Controls to Personal AI Agents
Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management govware_001_1790666482q1kAoPtquQ
  • Press Release

Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management

cybernewswire October 6, 2026 0
Torrance, Californina, 6th October 2026, CyberNewswire
Read More Read more about Criminal IP Introduces AITEM as the Next Evolution of Attack Surface Management
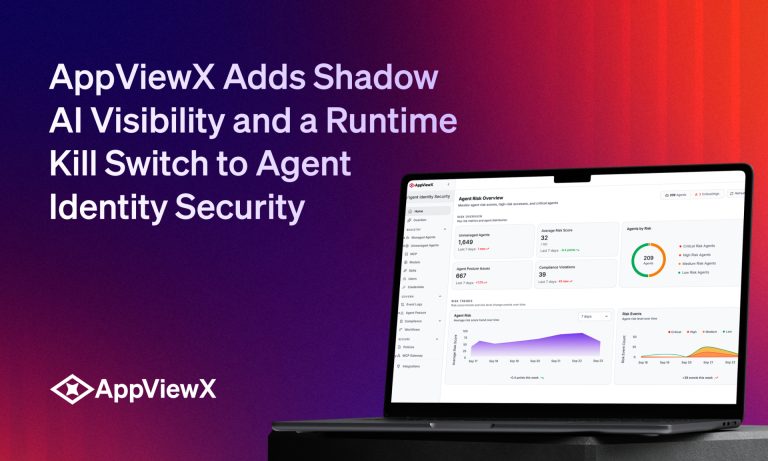
AppViewX Adds Shadow AI Visibility and a Runtime Kill Switch to Agent Identity Security PR_Banner_17912262302FpkG0rOrt
  • Press Release

AppViewX Adds Shadow AI Visibility and a Runtime Kill Switch to Agent Identity Security

cybernewswire October 6, 2026 0
New York, New York, 6th October 2026, CyberNewswire
Read More Read more about AppViewX Adds Shadow AI Visibility and a Runtime Kill Switch to Agent Identity Security
Murrelektronik Will Not Fix Critical AAS Edge Client Flaw CVE-2026-94293, Urges Removal AAS edge client vulnerability CVE-2026-94293 missing authentication in Murrelektronik aas-edge-client reference implementation
  • Vulnerability Report

Murrelektronik Will Not Fix Critical AAS Edge Client Flaw CVE-2026-94293, Urges Removal

Do Son October 6, 2026 0

Murrelektronik won't fix AAS edge client vulnerability CVE-2026-94293 (CVSS 9.8), which allows unauthenticated data changes. Remove it now.
Why Emerging Tech Hubs Are Ideal for Custom Web Development Outsourcing tech-laun
  • Technique

Why Emerging Tech Hubs Are Ideal for Custom Web Development Outsourcing

Do Son October 6, 2026 0
The global tech landscape in 2026 is facing a significant challenge. With a severe tech talent shortage...
Read More Read more about Why Emerging Tech Hubs Are Ideal for Custom Web Development Outsourcing
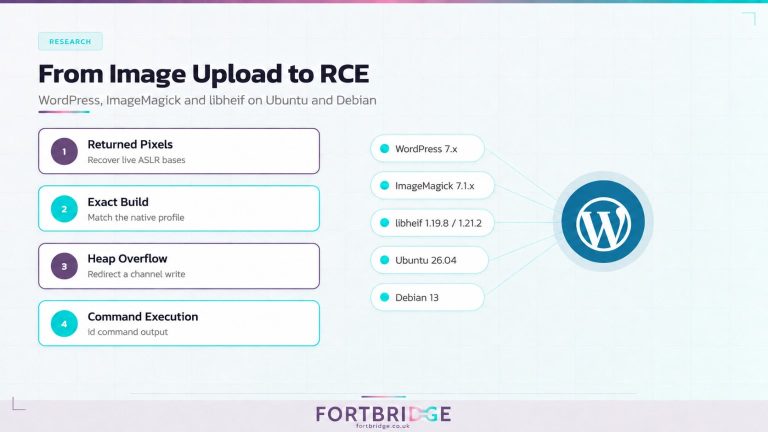
Researchers Publish Full Details and PoC Exploit for a WordPress libheif RCE Chain WordPress libheif RCE chain exploiting GHSA-x8r2-mggj-j6wr heap overflow via authenticated HEIC image upload
  • Vulnerability Report

Researchers Publish Full Details and PoC Exploit for a WordPress libheif RCE Chain

Do Son October 6, 2026 0

A WordPress libheif RCE chain and its PoC are now public. The libheif vulnerability turns an HEIC upload into code execution. Patch to 1.23.3.
ClingSTUN Linux Backdoor Turns Unpatched IoT Devices Into Proxy Nodes Diagram showing the MemTensor MemOS compromise details and how the MemTensor MemOS compromise affects developers
  • Malware

ClingSTUN Linux Backdoor Turns Unpatched IoT Devices Into Proxy Nodes

Do Son October 6, 2026 0

The ClingSTUN backdoor hijacks unpatched IoT devices and hides in traffic to public STUN servers. Learn how it spreads and how to stop it.
Apple Safari Chrome Tracking: A New Antitrust Defense Tool Apple Safari Chrome tracking telemetry data analysis
  • Technology

Apple Safari Chrome Tracking: A New Antitrust Defense Tool

Do Son October 6, 2026 0

Apple introduces Safari Chrome tracking through telemetry to gather defensive data against Google for UK and EU antitrust investigations and DMA compliance.
Poland Launches Google Antitrust Investigation Over Media Pay Polish UOKiK officials launching a Google antitrust investigation into media copyright violations and AI search algorithm data transparency
  • Technology

Poland Launches Google Antitrust Investigation Over Media Pay

Do Son October 6, 2026 0

Discover why Poland initiated a massive Google antitrust investigation over media licensing, AI search features, and alleged copyright circumvention.
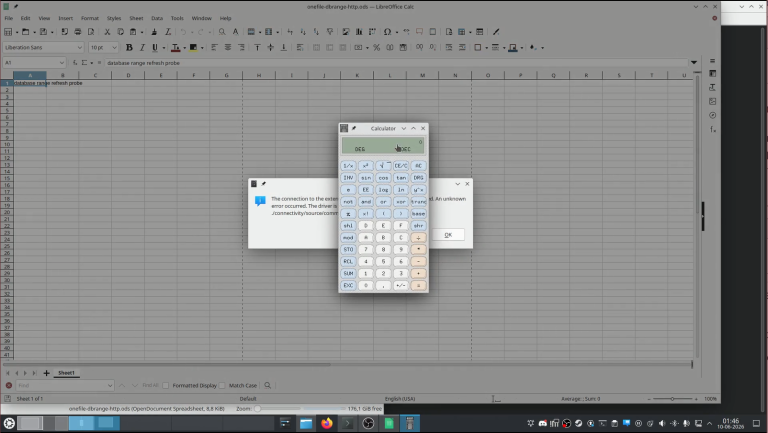
PoC Exploit and Technical Details Released for LibreOffice Calc Code Execution Flaw CVE-2026-63277 LibreOffice Calc vulnerability CVE-2026-63277 code execution with public PoC, plus file read and write flaws CVE-2026-63266 and CVE-2026-63267
  • Vulnerability Report

PoC Exploit and Technical Details Released for LibreOffice Calc Code Execution Flaw CVE-2026-63277

Do Son October 6, 2026 0

PoC released for LibreOffice Calc vulnerability CVE-2026-63277, which runs code when a file opens. Five more flaws fixed. Upgrade to 26.2.5.
OpenAI Text Watermarking Arrives Under the EU AI Act OpenAI text watermarking with textGrain detector for EU AI Act compliance
  • Technology

OpenAI Text Watermarking Arrives Under the EU AI Act

Do Son October 6, 2026 0

OpenAI text watermarking rolls out to ChatGPT and Codex in the EU under the EU AI Act, with opt-in API access and limited detector access.
Critical Atlassian Flaw CVE-2026-21589 Exposes Files in Jira, Confluence, Bitbucket and Five More Products Atlassian Data Center vulnerability CVE-2026-21589 arbitrary file access in Jira, Confluence, Bitbucket, Bamboo, Crowd, Fisheye and Crucible
  • Vulnerability Report

Critical Atlassian Flaw CVE-2026-21589 Exposes Files in Jira, Confluence, Bitbucket and Five More Products

Do Son October 6, 2026 0

Atlassian Data Center vulnerability CVE-2026-21589 (CVSS 9.3) allows arbitrary file access in Jira, Confluence and Bitbucket. Patch now.
Twenty CRM Flaw CVE-2026-105763 Exposes Plaintext Email Passwords to Any Workspace Member Twenty CRM vulnerability CVE-2026-105763 exposing plaintext IMAP SMTP CalDAV passwords via GraphQL
  • Vulnerability Report

Twenty CRM Flaw CVE-2026-105763 Exposes Plaintext Email Passwords to Any Workspace Member

Do Son October 6, 2026 0

Twenty CRM vulnerability CVE-2026-105763 (CVSS 9.6) enables plaintext password disclosure of IMAP and SMTP accounts. Upgrade to 2.7.0.
Trump Mobile Data Breach Exposes 3,615 Customers in BYOD Leak leak
  • Data Leak

Trump Mobile Data Breach Exposes 3,615 Customers in BYOD Leak

Do Son October 6, 2026 0

Trump Mobile data breach: BYOD leaks Trump Mobile customer data for 3,615 people, including Trump allies, via an infostealer and no MFA.
IBM Patches 25 Langflow Vulnerabilities, Including Two Critical Remote Code Execution Flaws Langflow vulnerabilities fixed in Langflow 1.12.3 including critical CVE-2026-104334 and CVE-2026-93674 remote code execution
  • Vulnerability Report

IBM Patches 25 Langflow Vulnerabilities, Including Two Critical Remote Code Execution Flaws

Do Son October 6, 2026 0

IBM fixes 25 Langflow vulnerabilities, including critical RCE flaw CVE-2026-104334 (CVSS 9.8). Upgrade to Langflow 1.12.3 now.
Apache Thrift 0.25.0 Fixes 61 Vulnerabilities, Including Two Critical Heap Overflows Apache Thrift vulnerabilities fixed in Apache Thrift 0.25.0 including CVE-2026-83632 and CVE-2026-91135
  • Vulnerability Report

Apache Thrift 0.25.0 Fixes 61 Vulnerabilities, Including Two Critical Heap Overflows

Do Son October 6, 2026 0

Apache Thrift 0.25.0 fixes 61 Apache Thrift vulnerabilities, including critical heap overflow CVE-2026-91135. Upgrade every binding now.
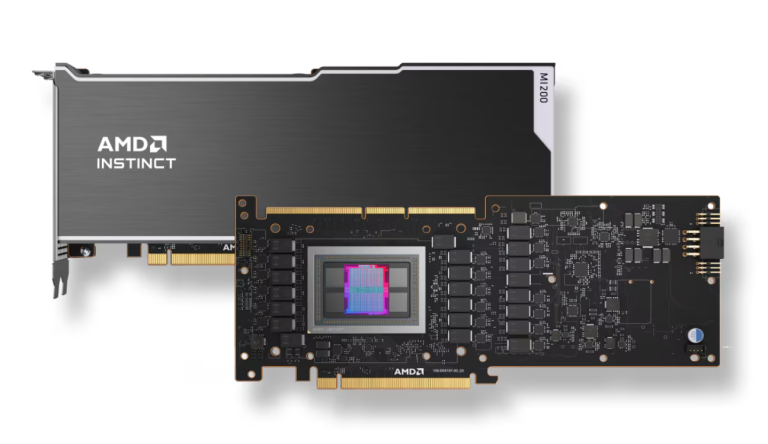
AMD RCCL Vulnerability Could Enable Remote Code Execution on Instinct GPU Clusters AMD RCCL vulnerability CVE-2026-43598 in the ROCm Communication Collectives Library on AMD Instinct GPUs
  • Vulnerability Report

AMD RCCL Vulnerability Could Enable Remote Code Execution on Instinct GPU Clusters

Do Son October 6, 2026 0

AMD RCCL vulnerability CVE-2026-43598 in the ROCm Communication Collectives Library could allow RCE on Instinct GPUs. Update to ROCm 7.14.
Who Can Actually Compel Your Hosting Provider: A Jurisdiction Guide for Security Teams DCMTK vulnerabilities enabling path traversal file write in the DICOM toolkit (CVE-2026-50003)
  • Technique

Who Can Actually Compel Your Hosting Provider: A Jurisdiction Guide for Security Teams

Do Son October 5, 2026 0

Server location is not jurisdiction. How the CLOUD Act, EU e-Evidence and Swiss law reach your host, and why the upstream network shapes the outcome.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121379CVSS 9.6
    The Tournamatch WordPress plugin before 4.7.1 does not validate or restrict the path of a previously stored profile...
    📅 Updated: Nov 7, 2026
  • CVE-2026-121491CVSS 9.0
    The Fiber Admin WordPress plugin before 4.0.1 does not validate or escape a request header before writing it...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119516CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Mamunur Rashid Radius Booking — Booking Calendar for Appointments & Services radius-booking...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.