 Do Son
At a Glance
| Organization | Trump Mobile (access allegedly gained via partner Liberty Mobile) |
| Data exposed | Names, emails, phone numbers, home addresses and order details |
| People affected | 3,615 customers – claimed by the attackers, partly verified by reporters |
| Cause | Alleged infostealer infection of a Liberty Mobile employee; no MFA, per the attackers |
| Disclosure status | Not confirmed by Trump Mobile; data published on BYOD’s leak site |
| Source | International Cyber Digest, Straight Arrow News |
TL;DR
The BYOD ransomware gang has dumped personal data on 3,615 Trump Mobile customers. Reporters say people in the leak confirmed their details are real. Trump Mobile has not confirmed the Trump Mobile data breach.
What Was Exposed
The dump holds names, email addresses, phone numbers, home addresses and order details. On its leak site, BYOD wrote that “all 3615 customers and their PII, alongside telecom details are now up for grabs.”
The 3,615 figure comes from the gang itself. Still, two outlets have checked parts of the file. Straight Arrow News reports that people listed in the data confirmed their details are accurate. So the Trump Mobile customer data appears genuine, although no one has verified the full count.
How It Happened
International Cyber Digest spoke with the threat actor. According to its interview with the BYOD operator, the gang infected a Liberty Mobile employee with an infostealer. From there, it reached Trump Mobile’s systems.
The attacker also claims neither company used multi-factor authentication. In addition, BYOD says it still has access to Trump Mobile’s backend. None of these claims has been independently confirmed.
Who Is Affected
Most victims are ordinary customers. However, the list also includes people close to President Trump. International Cyber Digest examined the leaked Trump Mobile data and found several well-known names. They include adviser Jason Miller, Congressman Mike Kelly, singer Larry Gatlin, EchoStar cofounder Charlie Ergen and influencer Bo Loudon.
Ironically, the file also includes the Trump Organization executive who oversees its information security. The story quickly drew wide attention and began trending on X.
Not the First Incident
This is a separate event from May 2026. Back then, Trump Mobile admitted a third-party flaw had exposed customer details online. That earlier exposure involved a different discoverer and a different record count.
What Affected People Should Do
- Expect targeted phishing that quotes your real order details.
- Watch for SIM swap attempts and add a carrier account PIN.
- Never share login codes with callers, even if they know your address.
- Turn on MFA for your email and phone carrier accounts.
Company Response
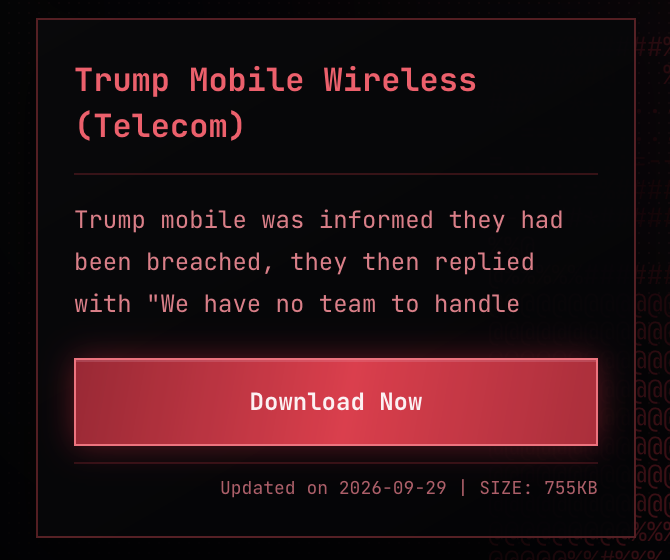
Trump Mobile has not publicly confirmed the Trump Mobile data breach. It also did not answer Straight Arrow News before publication. By contrast, BYOD paints a grim picture. The gang says the company replied, “We have no team to handle this.”
BYOD also told International Cyber Digest that no security team or outside firm is handling the incident. The attackers accused the company of having “no care for customers whatsoever.” We will update this story if Trump Mobile responds.
Support Our Threat Intelligence
Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
