Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Synology DSM Patches 8 Flaws, Two Critical Unauthenticated Synology DSM vulnerabilities patched in advisory SA_26_13, including two critical unauthenticated remote flaws on DiskStation Manager NAS devices
  • Vulnerability Report

Synology DSM Patches 8 Flaws, Two Critical Unauthenticated

Do Son September 18, 2026 0

Synology fixed 8 DSM vulnerabilities, including two critical unauthenticated flaws (CVE-2026-13684, CVE-2026-13639) on DiskStation Manager. Update now.
Critical HCL BigFix Vulnerabilities Expose Admin Accounts Diagram of critical HCL BigFix vulnerabilities and database exploitation paths
  • Vulnerability Report

Critical HCL BigFix Vulnerabilities Expose Admin Accounts

Do Son September 18, 2026 0

HCL Software patched critical HCL BigFix vulnerabilities, including CVE-2026-67100 and CVE-2026-18963. Patch now to prevent total account takeovers.
4 Linux Kernel LPE Flaws Disclosed With Public PoC Exploits Four Linux kernel privilege escalation vulnerabilities disclosed with public proof-of-concept exploits granting local root
  • Vulnerability Report

4 Linux Kernel LPE Flaws Disclosed With Public PoC Exploits

Do Son September 18, 2026 0

Four Linux kernel privilege escalation flaws were disclosed with public PoC exploits granting local root. Details and patches are now out. Update now.
PAPERMILL Cybercrime Cluster Delivers VenomRAT via Tax Lures Rust supply chain attack on arrayref crate with proc-macro1 typosquat and DPRK infrastructure overlap
  • Cybercriminals

PAPERMILL Cybercrime Cluster Delivers VenomRAT via Tax Lures

Do Son September 18, 2026 0

Security researchers uncovered the new PAPERMILL cybercrime cluster. Learn how the PAPERMILL cybercrime cluster uses tax lures to deploy VenomRAT.
Tajin Group Phishing Network Linked to Guarantee Marketplaces Tajin Group phishing network and Tajin Group money laundering scheme
  • Cybercriminals

Tajin Group Phishing Network Linked to Guarantee Marketplaces

Do Son September 18, 2026 0

A new Tajin Group phishing network emerged on Telegram. Discover how Tajin Group money laundering fuels illicit guarantee marketplaces across the globe.
Critical Google Chrome Vulnerabilities Fixed in Update Diagram showing critical Google Chrome vulnerabilities and patch for Google Chrome vulnerabilities
  • Vulnerability Report

Critical Google Chrome Vulnerabilities Fixed in Update

Do Son September 18, 2026 0

Google patched critical Google Chrome vulnerabilities. Update now to address multiple Google Chrome vulnerabilities like CVE-2026-93374 and stay secure.
Critical Dokploy OS Command Injection Exposes Servers Diagram of the Dokploy OS command injection and CVE-2026-72878 execution path
  • Vulnerability Report

Critical Dokploy OS Command Injection Exposes Servers

Do Son September 18, 2026 0

A critical Dokploy OS command injection flaw exposes servers to root takeover via backups. Patch this Dokploy OS command injection now.
GhostCode Phishing Kit Targets Enterprise Microsoft Accounts Redirect to legitimate device code sign-in page
  • Cybercriminals

GhostCode Phishing Kit Targets Enterprise Microsoft Accounts

Do Son September 18, 2026 0

Security researchers uncovered a new GhostCode phishing kit. Learn how the GhostCode phishing kit bypasses MFA to hijack enterprise Microsoft 365 accounts.
CVE-2026-86863 (CVSS 9.8): pgAdmin 4 Authentication Bypass Flaw Diagram showing the critical pgAdmin 4 authentication bypass vulnerability
  • Vulnerability Report

CVE-2026-86863 (CVSS 9.8): pgAdmin 4 Authentication Bypass Flaw

Do Son September 18, 2026 0

A critical pgAdmin 4 authentication bypass (CVE-2026-86863) allows remote admin takeover. Patch this pgAdmin 4 authentication bypass vulnerability now.
WordPress 7.1.1 Fixes 11 Security Flaws, Update Now WordPress 7.1.1 security release patching 11 vulnerabilities including stored cross-site scripting and path traversal flaws
  • Vulnerability Report

WordPress 7.1.1 Fixes 11 Security Flaws, Update Now

Do Son September 18, 2026 0

The WordPress 7.1.1 security release fixes 11 flaws, including stored cross-site scripting and path traversal. Update your sites immediately.
HP Fixes Critical HPLIP Vulnerabilities Diagram showing critical HPLIP vulnerabilities and HPLIP vulnerabilities patch
  • Vulnerability Report

HP Fixes Critical HPLIP Vulnerabilities

Do Son September 17, 2026 0

HP patched critical HPLIP vulnerabilities. Update your print drivers to fix HPLIP vulnerabilities and prevent remote code execution.
Critical HP Advance Vulnerabilities Enable RCE (CVE-2026-89082) Diagram illustrating the critical HP Advance vulnerabilities and remote code execution paths
  • Vulnerability Report

Critical HP Advance Vulnerabilities Enable RCE (CVE-2026-89082)

Do Son September 17, 2026 0

HP released updates to fix critical HP Advance vulnerabilities (CVE-2026-89082). Patch these HP Advance vulnerabilities to stop remote code execution.
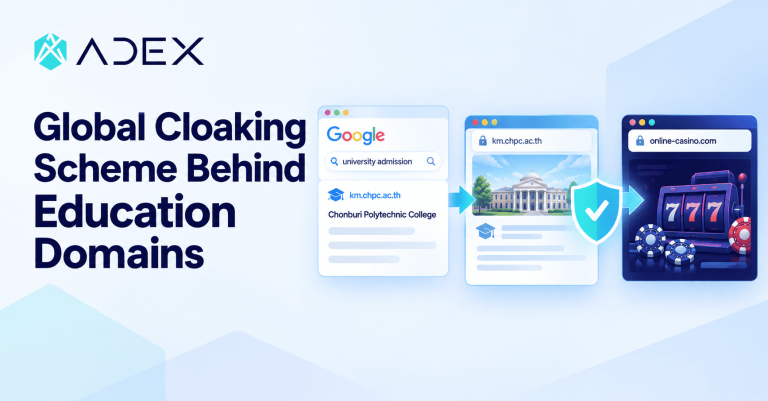
ADEX Uncovers Global Cloaking Scheme Behind Education Domains ADEX Uncovers Global Cloaking Scheme Behind Education Domains, cover
  • Technique

ADEX Uncovers Global Cloaking Scheme Behind Education Domains

Do Son September 17, 2026 0
A hacked education website was used to route users to an online casino, the latest case in...
Read More Read more about ADEX Uncovers Global Cloaking Scheme Behind Education Domains
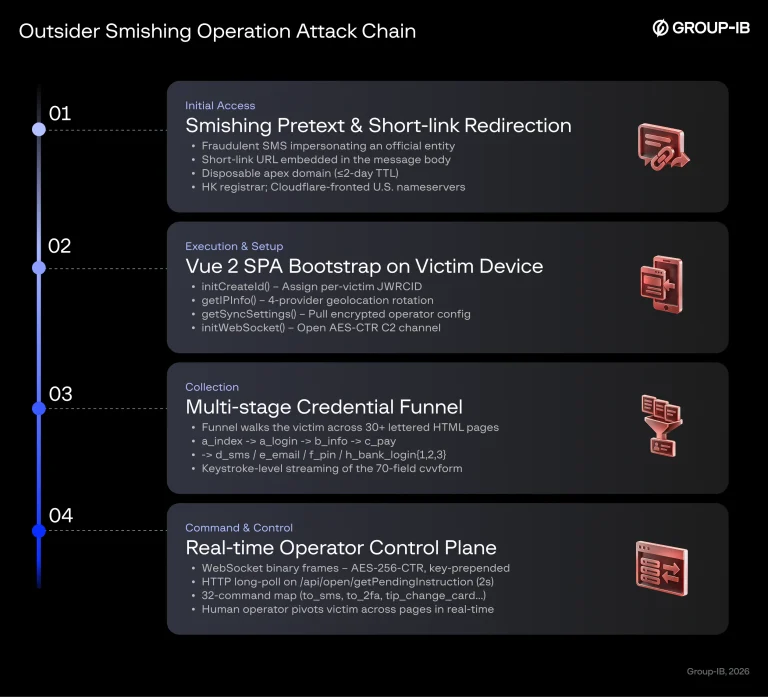
Smishing Triad Phishing Kit Exposed by Group-IB The new Smishing Triad phishing kit architecture and Smishing Triad phishing kit attack diagram
  • Cybercriminals

Smishing Triad Phishing Kit Exposed by Group-IB

Do Son September 17, 2026 0

Group-IB exposed a new Smishing Triad phishing kit used by Outsider. Learn how this Smishing Triad phishing kit steals financial data worldwide.
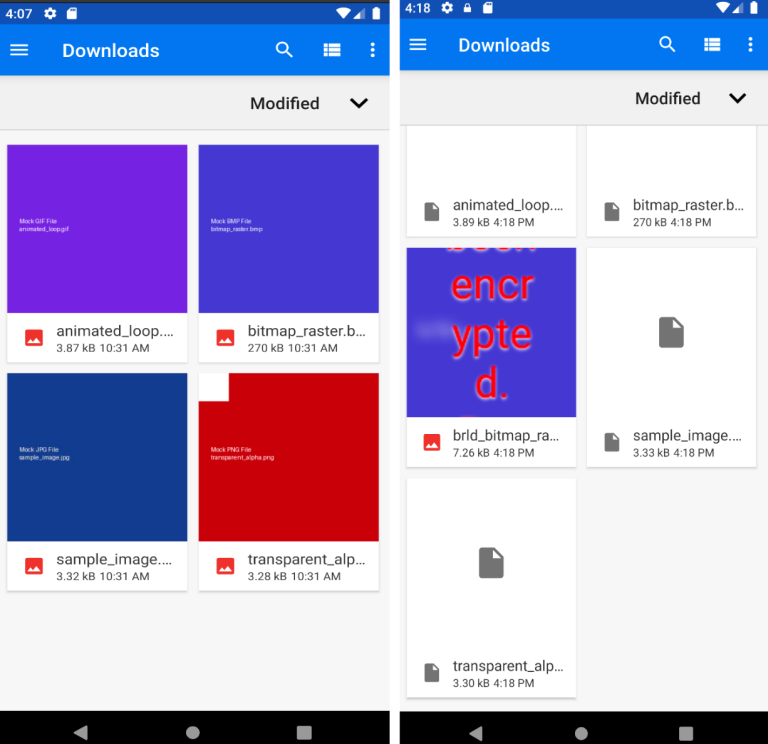
Mantax Otax Android Malware: Spyware Meets Ransomware Mantax Otax Android malware infection screen
  • Malware

Mantax Otax Android Malware: Spyware Meets Ransomware

Do Son September 17, 2026 0

Zimperium zLabs discovered Mantax Otax Android malware, a fierce Indonesian mobile ransomware integrating spyware to hijack, record, and extort victims.
North Korean IT Worker Scam Infiltrates Tech Jobs GoSerpent backdoor cyber espionage attack chain against Southeast Asian government networks
  • Cybercriminals

North Korean IT Worker Scam Infiltrates Tech Jobs

Do Son September 17, 2026 0

Silent Push uncovered a North Korean IT worker scam recruiting proxies. Learn how a North Korean IT worker uses Discord to bypass corporate hiring filters.
Google Home Adds MCP Support for AI Agent Control Google Home MCP support letting AI agents like Claude control Nest and Matter smart home devices
  • Technology

Google Home Adds MCP Support for AI Agent Control

Do Son September 17, 2026 0

Google Home MCP support lets AI agents like Claude control Nest and Matter devices via natural language, gated to the $20/mo Premium Advanced tier.
Apache NiFi Vulnerabilities Expose Data Pipelines to Attacks Diagram of Apache NiFi vulnerabilities and path manipulation vectors
  • Vulnerability Report

Apache NiFi Vulnerabilities Expose Data Pipelines to Attacks

Do Son September 17, 2026 0

Learn about recent Apache NiFi vulnerabilities (CVE-2026-87976, CVE-2026-70469) and Apache MyFaces flaws. Apply Apache security updates to prevent DoS attacks.
Unbound DNS Vulnerabilities Expose Resolvers to RCE Diagram illustrating critical Unbound DNS vulnerabilities and DNSSEC heap corruption
  • Vulnerability Report

Unbound DNS Vulnerabilities Expose Resolvers to RCE

Do Son September 17, 2026 0

NLnet Labs patched critical Unbound DNS vulnerabilities. Upgrade now to fix Unbound DNS vulnerabilities and block remote code execution attacks.
CVE-2026-89775 (CVSS 9.3): Linux Kernel LPE to Gain Root Flaw in KVM Diagram of KVM guest escape showing critical KVM guest escape flaw
  • Vulnerability Report

CVE-2026-89775 (CVSS 9.3): Linux Kernel LPE to Gain Root Flaw in KVM

Do Son September 17, 2026 0

A critical KVM guest escape (CVE-2026-89775) enables an LPE to gain root on Linux hosts. Patch this KVM guest escape vulnerability now.
Critical Docker Sandboxes Vulnerabilities Patched Diagram illustrating critical Docker Sandboxes vulnerabilities and guest escape vectors
  • Vulnerability Report

Critical Docker Sandboxes Vulnerabilities Patched

Do Son September 17, 2026 0

Docker released an update for critical Docker Sandboxes vulnerabilities (CVE-2026-77179, CVE-2026-79994). Patch these Docker Sandboxes vulnerabilities today.
CVE-2026-39919: Ghostscript Flaw Allows Unauthenticated Remote Code Execution Ghostscript buffer overflow diagram showing Ghostscript buffer overflow flaw and CVE-2026-39919
  • Vulnerability Report

CVE-2026-39919: Ghostscript Flaw Allows Unauthenticated Remote Code Execution

Do Son September 17, 2026 0

A Ghostscript buffer overflow enables unauthenticated remote code execution. Patch this Ghostscript buffer overflow flaw (CVE-2026-39919) immediately.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-94423CVSS 9.1
    Net::LibSSH versions before 0.004 for Perl authenticate to an unverified server because connect never checks the host key...
    📅 Updated: Oct 30, 2026
  • CVE-2026-93680CVSS 9.8
    IBM Langflow OSS 1.0.0 through 1.12.8 could allow a remote attacker to bypass security restrictions due to improper...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90865CVSS 9.0
    An OS command injection vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90866CVSS 9.1
    A path traversal vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows could...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90868CVSS 9.9
    An OS command injection vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows...
    📅 Updated: Oct 30, 2026
  • CVE-2026-89111CVSS 10.0
    The SAP Cloud SDK for Python contains an OAuth2 SSRF vulnerability affecting multi-tenant BTP applications. An attacker who...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90863CVSS 9.1
    Missing authorization in the administrative interface of Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on...
    📅 Updated: Oct 30, 2026
  • CVE-2026-90864CVSS 9.1
    A path traversal vulnerability in Progress Software WS_FTP Server versions prior to 2024.0.7 and 2025.0.4 on Windows could...
    📅 Updated: Oct 30, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.