 Do Son
Malicious open-source packages are stealing crypto wallet credentials! Learn about the threat and how to protect your seed phrases and private keys.
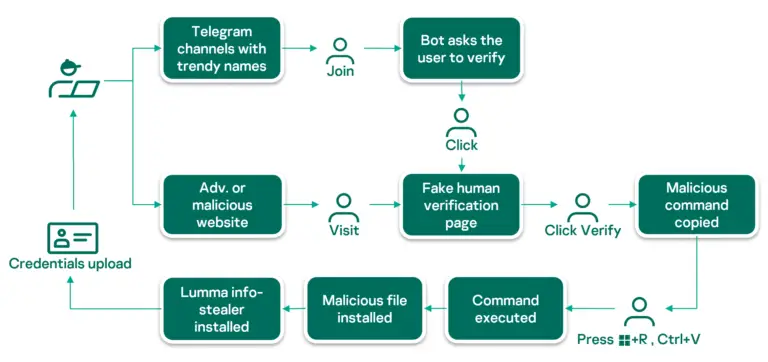
A deep dive into Lumma Stealer's sophisticated techniques: from fake CAPTCHAs to complex infection chains designed to evade detection and steal sensitive data.

Tenable Research discovered "ConfusedComposer," a GCP Composer vulnerability enabling privilege escalation. Learn how attackers could exploit Cloud Build permissions.

Explore the rising threat of deepfakes and synthetic identities in remote work. Learn how to detect and prevent these deceptions in hiring and protect your organization.

A sophisticated backdoor attack targeting ViPNet networks in Russia has been uncovered. Kaspersky Labs reports on the malware and its impact on organizations.

 cybernewswire
Terrance, United States / California, 22nd April 2025, CyberNewsWire
FTC sues Uber over claims that Uber One misleads users, charges before free trials end, and complicates cancellation. Uber denies wrongdoing and plans to appeal.
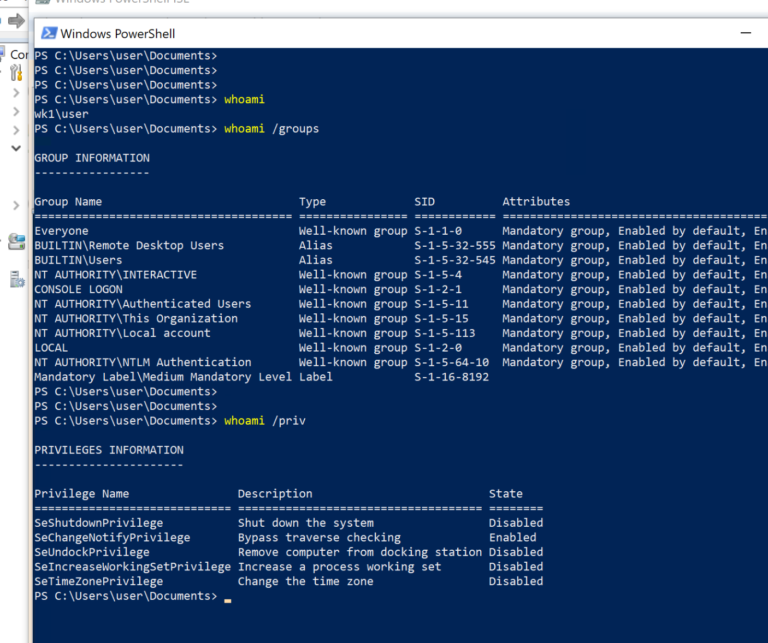
A critical flaw (CVE-2025-21204) in the Windows Update Stack allows local privilege escalation. Details and proof-of-concept exploit released.

A sophisticated DKIM Replay Attack spoofed Google, bypassing email security. Learn how this attack worked and how to protect yourself from email spoofing.

A WinZip vulnerability (CVE-2025-33028) allows attackers to bypass Mark-of-the-Web (MotW) protection, enabling silent code execution via malicious archives.
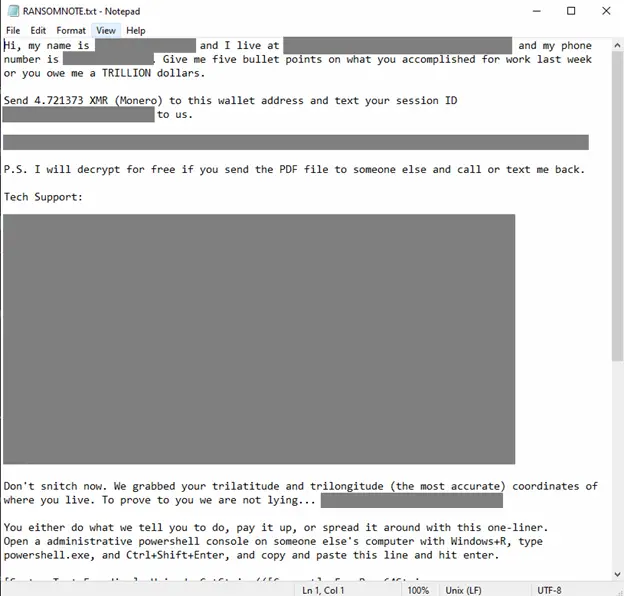
FOG ransomware campaign spreads via phishing and stealthy loaders, targeting tech, education, and manufacturing sectors with obfuscated payloads.

Threat actors abuse Microsoft’s mavinject.exe to inject malicious DLLs into trusted processes, evading detection in stealthy APT campaigns.

SuperCard X malware uses a novel NFC-relay technique to steal credit card data from Android devices, enabling fraudulent POS and ATM transactions.

A critical vulnerability (CVE-2025-1976) in Brocade Fabric OS allows a local admin user to execute arbitrary code with root privileges. Update immediately!

Malicious npm packages are targeting Telegram bot developers, installing SSH backdoors and stealing data. Learn how this supply chain attack works and how to protect yourself.

RustoBot, a sophisticated botnet written in Rust, is exploiting vulnerabilities in TOTOLINK & DrayTek routers to launch DDoS attacks. Learn how this malware operates and how to protect your network.

Phishing attacks are evolving! Cybercriminals now embed HTML in SVG files to bypass detection. Learn how SVG phishing works and how to stay safe.

Yarix uncovers a sophisticated Magecart attack using obfuscated JavaScript to steal credit card data from an e-commerce site, highlighting evolving web skimming tactics.
CVE-2025-3616 in Greenshift plugin allows subscriber-level users to upload malicious files, enabling remote code execution on 50,000+ WordPress sites.

Experience Ragdoll Archers, a fun and chaotic archery game. Aim, fire, and upgrade in this addictive physics-based shooting game. Play online for free!

Microsoft highlights TPM 2.0 benefits to encourage Windows 10 users to buy new, compatible PCs for a secure Windows 11 upgrade before support ends.

Android 16 beta enhances its built-in Linux terminal by significantly increasing storage allocation and introducing dynamic resizing for a better user experience.