Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Two Critical RCE Flaws Expose Yi IOT Smart Cameras to Full Device Takeover Yi IOT vulnerabilities, remote command execution
  • Vulnerability

Two Critical RCE Flaws Expose Yi IOT Smart Cameras to Full Device Takeover

Do Son April 23, 2025 0

Two critical CVEs in Yi IOT smart cameras allow unauthenticated RCE and root access via ports 6789 and 999, exposing users to full device compromise.

Unveiling a Multi-Stage Malware Attack: Cloudflare Abuse and AsyncRAT Delivery Infection chains distributing AsyncRAT
  • Malware

Unveiling a Multi-Stage Malware Attack: Cloudflare Abuse and AsyncRAT Delivery

Do Son April 23, 2025 0

A deep dive into a sophisticated multi-stage malware attack using Cloudflare to deliver AsyncRAT. Learn how attackers evade detection and compromise systems.

Zyxel Patches High-Severity Security Flaws in USG FLEX H Firewalls Zyxel Vulnerability Firewall Security
  • Vulnerability

Zyxel Patches High-Severity Security Flaws in USG FLEX H Firewalls

Do Son April 23, 2025 0

Zyxel releases patches for USG FLEX H firewalls to address critical vulnerabilities. Learn about the security flaws and how to protect your network.
Malicious Packages Stealing Crypto Credentials: A Warning for Developers npm package, crypto drainer Malicious Packages Cryptocurrency Theft
  • Malware

Malicious Packages Stealing Crypto Credentials: A Warning for Developers

Do Son April 23, 2025 0

Malicious open-source packages are stealing crypto wallet credentials! Learn about the threat and how to protect your seed phrases and private keys.
Lumma Stealer: Unpacking Its Evasive Tactics and Complex Infection Chains Lumma Stealer Malware Distribution
  • Malware

Lumma Stealer: Unpacking Its Evasive Tactics and Complex Infection Chains

Do Son April 23, 2025 0

A deep dive into Lumma Stealer's sophisticated techniques: from fake CAPTCHAs to complex infection chains designed to evade detection and steal sensitive data.

“ConfusedComposer”: GCP Composer Vulnerability Allows Privilege Escalation GCP Composer Privilege Escalation
  • Vulnerability

“ConfusedComposer”: GCP Composer Vulnerability Allows Privilege Escalation

Do Son April 23, 2025 0

Tenable Research discovered "ConfusedComposer," a GCP Composer vulnerability enabling privilege escalation. Learn how attackers could exploit Cloud Build permissions.

Deepfakes and Deception: The Rise of Synthetic Identities in Remote Work Deepfakes Synthetic Identity
  • Cybercriminals

Deepfakes and Deception: The Rise of Synthetic Identities in Remote Work

Do Son April 23, 2025 0

Explore the rising threat of deepfakes and synthetic identities in remote work. Learn how to detect and prevent these deceptions in hiring and protect your organization.

Sophisticated Backdoor Attack Targets ViPNet Networks Backdoor ViPNet
  • Malware

Sophisticated Backdoor Attack Targets ViPNet Networks

Do Son April 22, 2025 0

A sophisticated backdoor attack targeting ViPNet networks in Russia has been uncovered. Kaspersky Labs reports on the malware and its impact on organizations.

Criminal IP to Showcase Advanced Threat Intelligence at RSAC™ 2025 2_1745287116p85jnfM33F
  • Press Release

Criminal IP to Showcase Advanced Threat Intelligence at RSAC™ 2025

cybernewswire April 22, 2025 0
Terrance, United States / California, 22nd April 2025, CyberNewsWire
Read More Read more about Criminal IP to Showcase Advanced Threat Intelligence at RSAC™ 2025
FTC Sues Uber Over Misleading Uber One Subscription Practices Uber One, FTC complaint
  • Technology

FTC Sues Uber Over Misleading Uber One Subscription Practices

Do Son April 22, 2025 0

FTC sues Uber over claims that Uber One misleads users, charges before free trials end, and complicates cancellation. Uber denies wrongdoing and plans to appeal.
CVE-2025-21204: SYSTEM-Level Privilege Escalation in Windows Update Stack Exposed, PoC Released CVE-2025-21204, Windows Update Stack
  • Vulnerability

CVE-2025-21204: SYSTEM-Level Privilege Escalation in Windows Update Stack Exposed, PoC Released

Do Son April 22, 2025 0

A critical flaw (CVE-2025-21204) in the Windows Update Stack allows local privilege escalation. Details and proof-of-concept exploit released.

Google Spoofed in Sophisticated DKIM Replay Attack Exploiting Email Trust Mechanisms DKIM Replay Attack Email Spoofing
  • Cybercriminals

Google Spoofed in Sophisticated DKIM Replay Attack Exploiting Email Trust Mechanisms

Do Son April 22, 2025 0

A sophisticated DKIM Replay Attack spoofed Google, bypassing email security. Learn how this attack worked and how to protect yourself from email spoofing.

CVE-2025-33028: WinZip Flaw Exposes Users to Silent Code Execution via MotW Bypass, No Patch WinZip vulnerability MotW bypass CVE-2025-33028
  • Vulnerability

CVE-2025-33028: WinZip Flaw Exposes Users to Silent Code Execution via MotW Bypass, No Patch

Do Son April 22, 2025 0

A WinZip vulnerability (CVE-2025-33028) allows attackers to bypass Mark-of-the-Web (MotW) protection, enabling silent code execution via malicious archives.
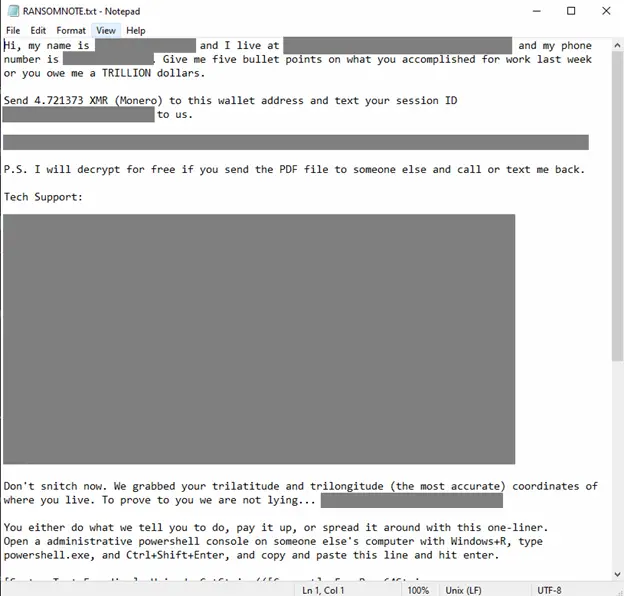
FOG Ransomware Campaign Targets Multiple Sectors with Phishing and Payload Obfuscation FOG ransomware, phishing
  • Malware

FOG Ransomware Campaign Targets Multiple Sectors with Phishing and Payload Obfuscation

Do Son April 22, 2025 0

FOG ransomware campaign spreads via phishing and stealthy loaders, targeting tech, education, and manufacturing sectors with obfuscated payloads.

Legitimate Windows Tool Abused: mavinject.exe Used for Stealthy DLL Injection by Threat Actors mavinject.exe, DLL Injection
  • Cybercriminals

Legitimate Windows Tool Abused: mavinject.exe Used for Stealthy DLL Injection by Threat Actors

Do Son April 22, 2025 0

Threat actors abuse Microsoft’s mavinject.exe to inject malicious DLLs into trusted processes, evading detection in stealthy APT campaigns.

SuperCard X: Android Malware Steals Cards via NFC Relay Attacks super
  • Malware

SuperCard X: Android Malware Steals Cards via NFC Relay Attacks

Do Son April 22, 2025 0

SuperCard X malware uses a novel NFC-relay technique to steal credit card data from Android devices, enabling fraudulent POS and ATM transactions.

Critical CVE-2025-1976 Vulnerability in Brocade Fabric OS Actively Exploited Brocade Fabric OS, CVE-2025-1976
  • Vulnerability

Critical CVE-2025-1976 Vulnerability in Brocade Fabric OS Actively Exploited

Do Son April 22, 2025 0

A critical vulnerability (CVE-2025-1976) in Brocade Fabric OS allows a local admin user to execute arbitrary code with root privileges. Update immediately!

Malicious npm Packages Backdoor Telegram Bot Developers npm Malware, Telegram Bots
  • Malware

Malicious npm Packages Backdoor Telegram Bot Developers

Do Son April 22, 2025 0

Malicious npm packages are targeting Telegram bot developers, installing SSH backdoors and stealing data. Learn how this supply chain attack works and how to protect yourself.

RustoBot Botnet Exploits Router Flaws in Sophisticated Attacks RustoBot, Router Vulnerability
  • Malware
  • Vulnerability

RustoBot Botnet Exploits Router Flaws in Sophisticated Attacks

Do Son April 22, 2025 0

RustoBot, a sophisticated botnet written in Rust, is exploiting vulnerabilities in TOTOLINK & DrayTek routers to launch DDoS attacks. Learn how this malware operates and how to protect your network.

SVG Files Weaponized: Phishing Attacks Embed HTML Code phish-svg
  • Cybercriminals

SVG Files Weaponized: Phishing Attacks Embed HTML Code

Do Son April 22, 2025 0

Phishing attacks are evolving! Cybercriminals now embed HTML in SVG files to bypass detection. Learn how SVG phishing works and how to stay safe.

Magecart Attack Uncovered: Obfuscated JavaScript Steals Credit Card Data WordPress Backdoor
  • Malware

Magecart Attack Uncovered: Obfuscated JavaScript Steals Credit Card Data

Do Son April 22, 2025 0

Yarix uncovers a sophisticated Magecart attack using obfuscated JavaScript to steal credit card data from an e-commerce site, highlighting evolving web skimming tactics.
Over 50k WordPress Sites at Takeover Risk Via Vulnerable Plugin Greenshift plugin WordPress vulnerability
  • Vulnerability

Over 50k WordPress Sites at Takeover Risk Via Vulnerable Plugin

Do Son April 21, 2025 0

CVE-2025-3616 in Greenshift plugin allows subscriber-level users to upload malicious files, enabling remote code execution on 50,000+ WordPress sites.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-89126CVSS 10.0
    SAP Web Dispatcher does not sufficiently validate certain network input processed by an internal component. An unauthenticated attacker...
    📅 Updated: Nov 10, 2026
  • CVE-2026-89119CVSS 9.6
    SAP Web Dispatcher and SAP NetWeaver Application Server ABAP (Internet Communication Manager) do not perform sufficient request validation...
    📅 Updated: Nov 10, 2026
  • CVE-2026-89103CVSS 10.0
    SAP Gateway activates the default Access Control List with high privileges allowing categorization of external attacker as internal...
    📅 Updated: Nov 10, 2026
  • CVE-2026-76964CVSS 10.0
    SAP NetWeaver Application Server ABAP does not sufficiently validate certain network input processed by an internal component. An...
    📅 Updated: Nov 10, 2026
  • CVE-2026-76965CVSS 9.9
    SAP NetWeaver Application Server ABAP and ABAP Platform does not perform necessary authorization checks for certain internal functionality....
    📅 Updated: Nov 10, 2026
  • CVE-2026-120017CVSS 10.0
    SAP NetWeaver AS ABAP and ABAP Platform does not perform sufficient verification of incoming authentication assertions under certain...
    📅 Updated: Nov 10, 2026
  • CVE-2026-109803CVSS 9.9
    SAP NetWeaver Knowledge Management (XML Forms) does not sufficiently restrict the selection of XSL transformations processed by the...
    📅 Updated: Nov 10, 2026
  • CVE-2026-109795CVSS 9.9
    SAP NetWeaver does not perform necessary authorization checks and lacks sufficient input validation in certain remote-enabled functionality. An...
    📅 Updated: Nov 10, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.