Skip to content
October 31, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Critical Fortinet Vulnerabilities Expose Networks to Attack Diagram illustrating the three new Fortinet vulnerabilities including CVE-2026-84390 and CVE-2026-26084
  • Vulnerability Report

Critical Fortinet Vulnerabilities Expose Networks to Attack

Do Son September 8, 2026 0

Fortinet fixed three critical Fortinet vulnerabilities. Attackers can exploit CVE-2026-84390 and CVE-2026-26084 to access corporate data.
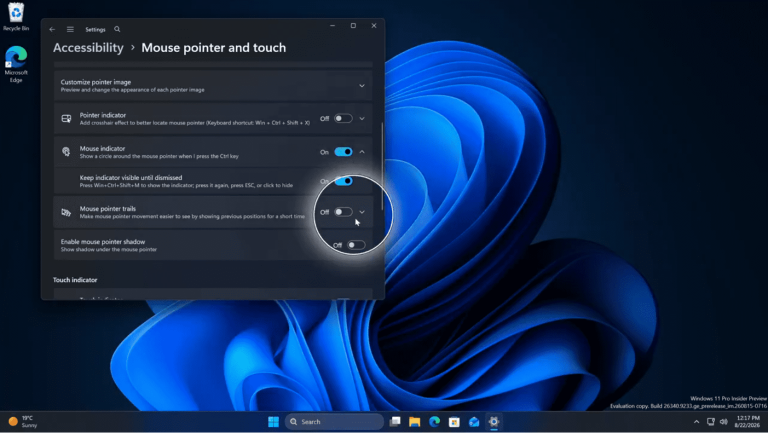
Windows 11 Performance Enhancements Target 8GB RAM Devices Windows 11 performance optimization showing improved memory usage and faster boot on 8GB RAM PCs
  • Windows

Windows 11 Performance Enhancements Target 8GB RAM Devices

Do Son September 8, 2026 0

Microsoft is upgrading Windows 11 performance to ensure faster boot times and fluid experiences for PCs equipped with just 8GB of RAM.
Ivanti Fixes High Severity Ivanti Vulnerabilities in Sentry and EPMM High severity Ivanti vulnerabilities affecting Sentry and EPMM
  • Vulnerability Report

Ivanti Fixes High Severity Ivanti Vulnerabilities in Sentry and EPMM

Do Son September 8, 2026 0

Ivanti released patches for high severity Ivanti vulnerabilities affecting Sentry and EPMM. Secure your enterprise deployments against these flaws now.
PyPI File Hosting Errors: 502s Traced to Fastly Cache PyPI file hosting errors dashboard showing Fastly CDN 502 and 503 cache node failures
  • Technology

PyPI File Hosting Errors: 502s Traced to Fastly Cache

Do Son September 8, 2026 0

PyPI file hosting errors caused weeks of 502s. See how a Fastly CDN 502 error was traced to one cache node and fixed by August 28.
Broadcom Removes VDDK Downloads, Complicating VMware Migrations Broadcom VDDK download removal error screen halting a VMware migration process
  • Technology

Broadcom Removes VDDK Downloads, Complicating VMware Migrations

Do Son September 8, 2026 0

Broadcom's unexpected VDDK download removal has severely disrupted VMware migrations. Learn how this impacts Azure and Red Hat enterprise transitions.
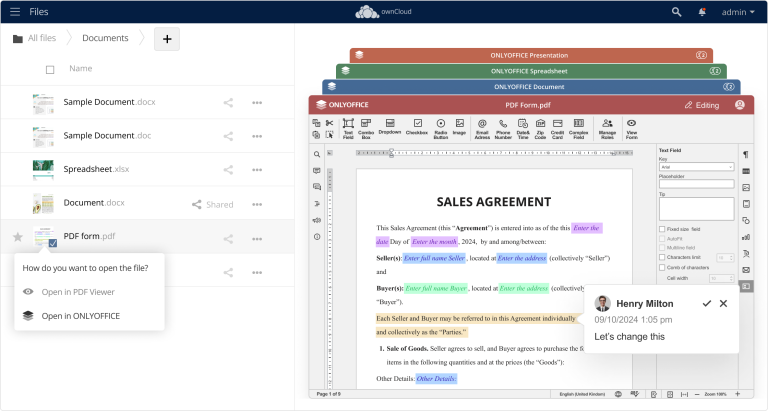
ONLYOFFICE ownCloud Plugin SSRF Vulnerability ONLYOFFICE ownCloud plugin SSRF vulnerability CVE-2026-84282
  • Vulnerability Report

ONLYOFFICE ownCloud Plugin SSRF Vulnerability

Do Son September 8, 2026 0

A new ONLYOFFICE ownCloud plugin SSRF vulnerability, tracked as CVE-2026-84282, allows attackers to trigger unauthorized internal network requests.
Ivanti Neurons for ITSM Remote Code Execution Flaws: 8 CVEs, CVSS Up to 9.9 Ivanti Neurons ITSM remote code execution deserialization missing authorization CVE-2026-12744 CVE-2026-12650 critical vulnerability patch
  • Vulnerability Report

Ivanti Neurons for ITSM Remote Code Execution Flaws: 8 CVEs, CVSS Up to 9.9

Do Son September 8, 2026 0

Ivanti Neurons ITSM RCE: 8 CVEs including unauthenticated code execution flaws (CVSS 9.8-9.9). Patch on-prem deployments now - cloud already fixed.
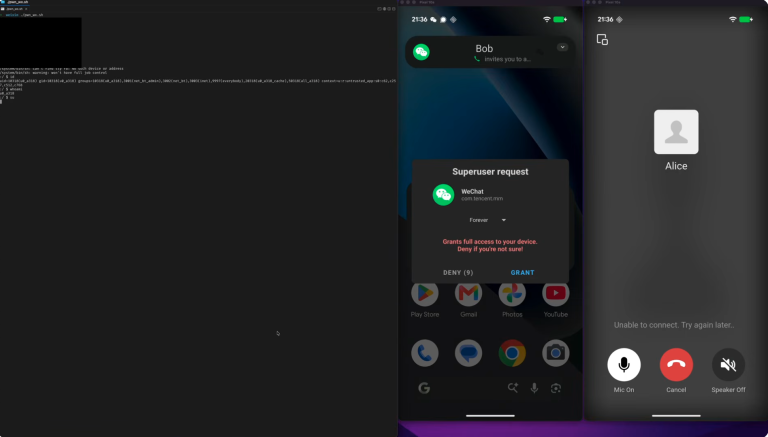
WeWorm: First Zero-Click Worm Spreads Through WeChat Calls on iOS and Android WeWorm first zero-click worm WeChat VoIP RCE iOS Android Calif security research
  • Vulnerability Report

WeWorm: First Zero-Click Worm Spreads Through WeChat Calls on iOS and Android

Do Son September 8, 2026 0

WeWorm is the first zero-click worm to spread via WeChat calls on iOS and Android. Calif researchers found the WeChat RCE flaw - now patched by Tencent.
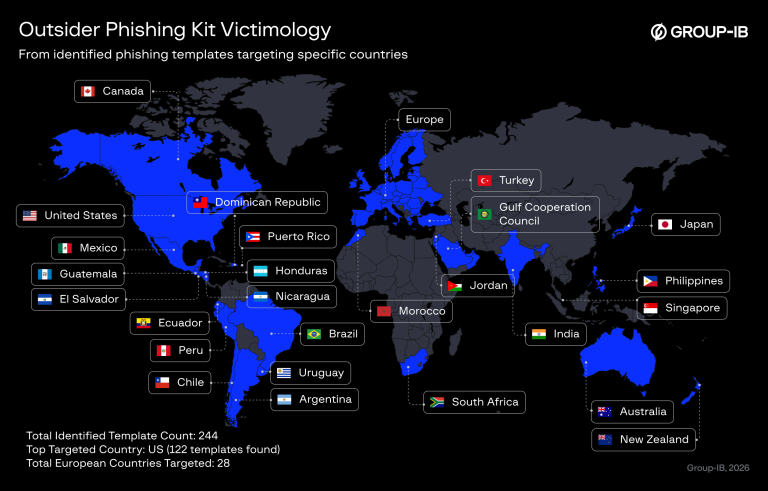
Outsider Phishing Kit Survives Operation Ghost Hook Takedown Outsider Phishing Kit tracking panel and ChenLun Outsider PhaaS kit dashboard
  • Cybercriminals

Outsider Phishing Kit Survives Operation Ghost Hook Takedown

Do Son September 8, 2026 0

The Outsider Phishing Kit persists despite the Operation Ghost Hook takedown. Discover how the ChenLun Outsider PhaaS kit bypasses MFA via AiTM attacks.
Reflectiz Launches Agentic Pentesting for Websites: Up to 10x Coverage vs Conventional Pentests image_5_1788857508pakUwabkhz
  • Press Release

Reflectiz Launches Agentic Pentesting for Websites: Up to 10x Coverage vs Conventional Pentests

cybernewswire September 8, 2026 0
Boston, MA, USA, 8th September 2026, CyberNewswire
Read More Read more about Reflectiz Launches Agentic Pentesting for Websites: Up to 10x Coverage vs Conventional Pentests
Phantom Deal Scam Targets Executives With Fake NDAs Phantom Deal campaign document tracking diagram illustrating the Phantom Deal scam
  • Cybercriminals

Phantom Deal Scam Targets Executives With Fake NDAs

Do Son September 8, 2026 0

The Phantom Deal campaign uses fake acquisition documents to target executives. Gen exposed the Phantom Deal fraud after tracking bogus payment demands.
September 2026 SAP Security Patch Day Fixes Critical Flaws September 2026 SAP Security Patch Day dashboard showing CVE-2026-44756 alerts
  • Vulnerability Report

September 2026 SAP Security Patch Day Fixes Critical Flaws

Do Son September 8, 2026 0

The September 2026 SAP Security Patch Day resolves 20 flaws. Apply these SAP Security Patch Day updates to fix CVE-2026-44756 and secure your environment.
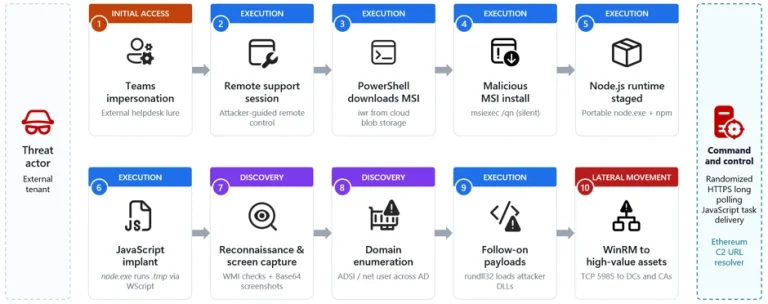
Microsoft Teams IT Support Impersonation Leads to Domain Takeover Microsoft Teams IT support impersonation attack chain from external tenant contact to Node.js implant and WinRM lateral movement toward domain controllers
  • Cybercriminals

Microsoft Teams IT Support Impersonation Leads to Domain Takeover

Do Son September 8, 2026 0

Microsoft Teams IT support impersonation lets attackers plant a Node.js implant and pivot to domain controllers over WinRM. See how to defend.
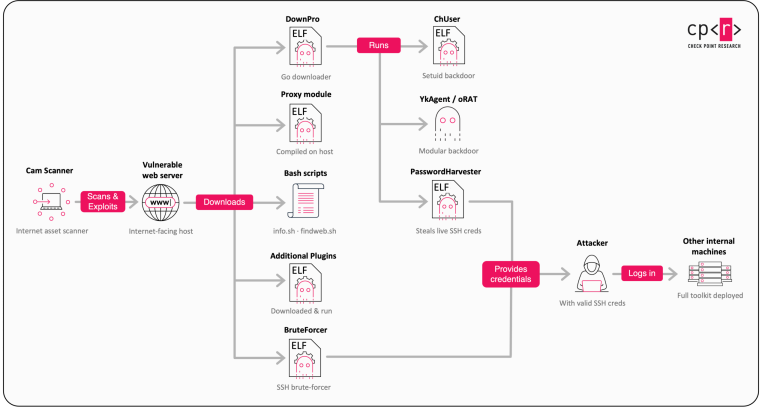
Chinese Actor Gambling Goblin Hijacks Brazilian Gov Sites Gambling Goblin campaign targeting government servers with Gambling Goblin malware
  • Cybercriminals

Chinese Actor Gambling Goblin Hijacks Brazilian Gov Sites

Do Son September 8, 2026 0

The Gambling Goblin campaign turns Brazilian government websites into an SEO weapon. Suspected Gambling Goblin operators push illicit gambling pages.
ASUS Patches Control Center Express and Armoury Crate Flaws ASUS Control Center Express and Armoury Crate vulnerabilities allowing host takeover and NTLM hash theft, fixed in the latest software update
  • Vulnerability Report

ASUS Patches Control Center Express and Armoury Crate Flaws

Do Son September 8, 2026 0

An ASUS vulnerability (CVE-2026-19397) lets a nearby attacker take over a host, while an Armoury Crate flaw leaks NTLM hashes. Update now.
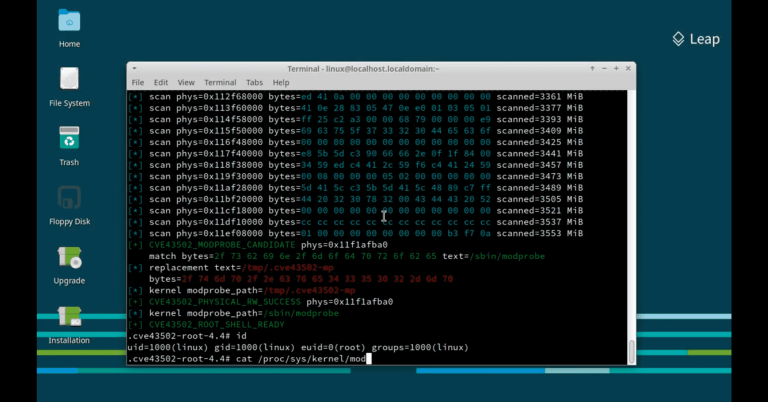
Public PoC Disclosed for ZcopyReaper Linux Vulnerability (CVE-2026-43502) ZcopyReaper Linux vulnerability PoC exploit code execution in the Linux kernel
  • Vulnerability Report

Public PoC Disclosed for ZcopyReaper Linux Vulnerability (CVE-2026-43502)

Do Son September 8, 2026 0

The details and PoC exploit code for the ZcopyReaper Linux vulnerability (CVE-2026-43502) are publicly disclosed, posing a privilege escalation risk.
Liquid Network Security Incident: The White Hat Dilemma Liquid Network hack diagram showing Bitcoin transfer and white hat bounty negotiation
  • Cybercriminals

Liquid Network Security Incident: The White Hat Dilemma

Do Son September 8, 2026 0

Discover the details of the Liquid Network hack. A white hat attacker stole 4,000 Bitcoins but returned most of the funds to force a bug bounty payment.
Windows 11 Battery Widget: New Connected Device Status Windows 11 battery widget displaying connected peripheral power levels
  • Windows

Windows 11 Battery Widget: New Connected Device Status

Do Son September 8, 2026 0

Discover the upcoming Windows 11 battery widget that elegantly displays peripheral power levels and connection statuses directly on your lock screen.
Pegasus Spyware Hits Serbian Student Activist via Zero-Click iMessage Pegasus spyware zero-click iMessage infection on a Serbian student activist iPhone, part of the largest documented surveillance wave in Serbia
  • Malware

Pegasus Spyware Hits Serbian Student Activist via Zero-Click iMessage

Do Son September 8, 2026 0

Pegasus spyware infected a Serbian activist through a zero-click iMessage exploit, part of Serbia's largest spyware wave. Update iOS now.
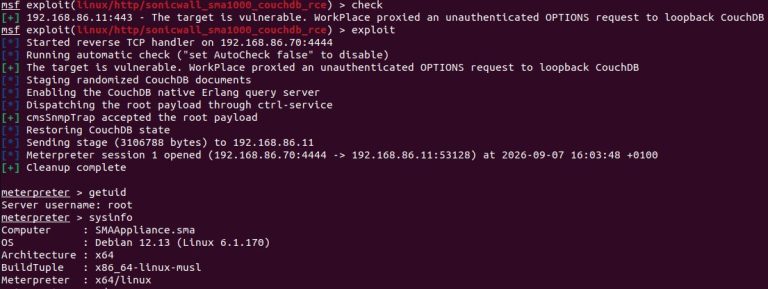
SonicWall SMA 1000 Vulnerabilities Exploited in Wild (PoC) SonicWall SMA 1000 vulnerabilities being exploited using the SonicWall SMA 1000 exploit chain
  • Vulnerability Report

SonicWall SMA 1000 Vulnerabilities Exploited in Wild (PoC)

Do Son September 8, 2026 0

SonicWall SMA 1000 vulnerabilities are exploited in the wild. Public PoC exploit code is disclosed for the critical SonicWall SMA 1000 exploit chain.
JetBrains Vulnerabilities: 29 Flaws Patched in Hub and YouTrack Security bulletin addressing critical JetBrains vulnerabilities and JetBrains vulnerabilities
  • Vulnerability Report

JetBrains Vulnerabilities: 29 Flaws Patched in Hub and YouTrack

Do Son September 8, 2026 0

JetBrains fixed 29 JetBrains vulnerabilities in Hub and YouTrack. Learn how these critical 9.8 CVSS bugs impact developer servers and how to patch now.
Node.js Malware Attacks Target Tech and Finance Sectors Node.js malware attacks diagram showing Node.js malware execution flow
  • Malware

Node.js Malware Attacks Target Tech and Finance Sectors

Do Son September 8, 2026 0

Recent Node.js malware attacks target global firms. Attackers deploy Node.js malware using trusted runtimes and smart contracts to evade detection.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-48383CVSS 10.0
    Adobe Experience Manager is affected by an Incorrect Authorization vulnerability that could result in arbitrary code execution in...
    📅 Updated: Oct 31, 2026
  • CVE-2026-75732CVSS 9.9
    Adobe Experience Manager is affected by an Incorrect Authorization vulnerability that could result in arbitrary code execution in...
    📅 Updated: Oct 31, 2026
  • CVE-2026-83662CVSS 9.3
    Adobe Experience Manager is affected by a reflected Cross-Site Scripting (XSS) vulnerability. An attacker could exploit this vulnerability...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119261CVSS 9.6
    Improper input validation in Skia in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119263CVSS 9.6
    Memory corruption in GarbageCollection in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Oct 31, 2026
  • CVE-2026-89078CVSS 9.9
    GitLab has remediated an issue in GitLab CE/EE affecting all versions from 19.2 before 19.2.7, 19.3 before 19.3.3,...
    📅 Updated: Oct 31, 2026
  • CVE-2026-93577CVSS 9.9
    GitLab has remediated an issue in GitLab CE/EE affecting all versions from 19.2 before 19.2.7, 19.3 before 19.3.3,...
    📅 Updated: Oct 31, 2026
  • CVE-2026-110264CVSS 10.0
    An issue has been discovered in GitLab CE/EE affecting all versions from 7.0 before 18.11.13, 19.0 before 19.0.10,...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.