 Do Son
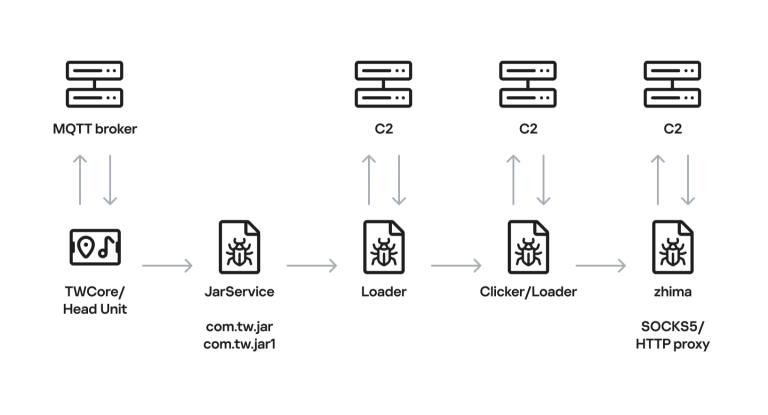
Kaspersky exposed Android head unit malware turned into a botnet. Discover how this Android head unit malware botnet infects smart cars.
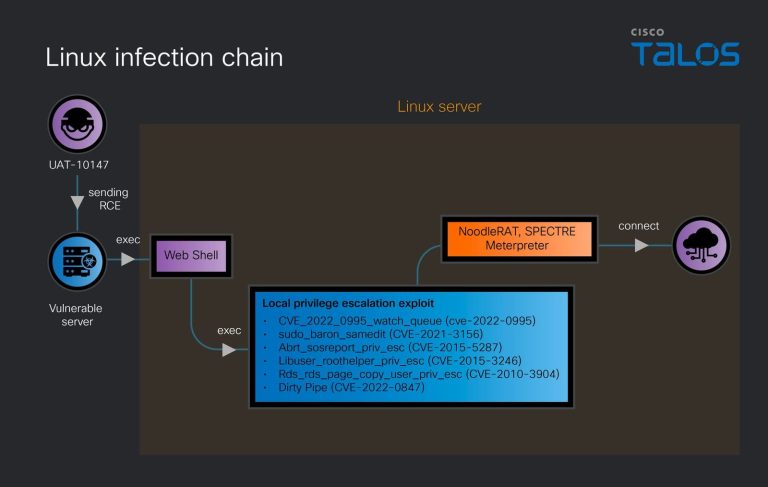
Cisco Talos revealed how UAT-10147 agentic AI attacks target global servers. Learn how UAT-10147 agentic AI tools automate intrusions and data theft.
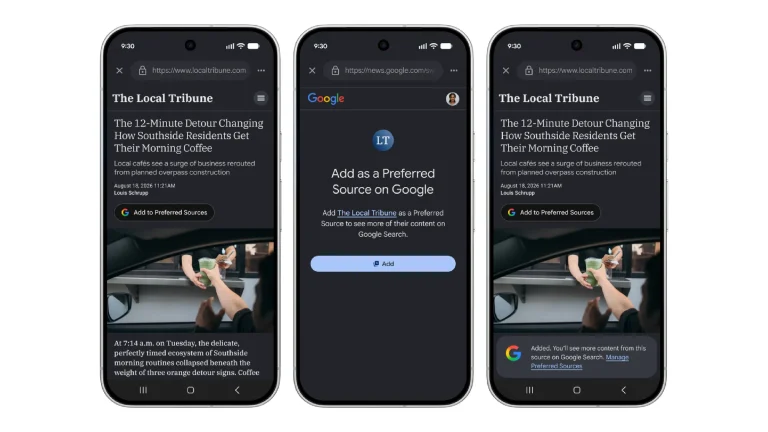
Discover how the new Google Preferred Sources button empowers publishers, integrates Gemini into Discover, and transforms modern SEO strategies.
CVE-2026-67567 (CVSS 9.9) leads three Red Hat privilege escalation flaws in ACM and FreeIPA. Two FreeIPA bugs can reach full domain compromise.
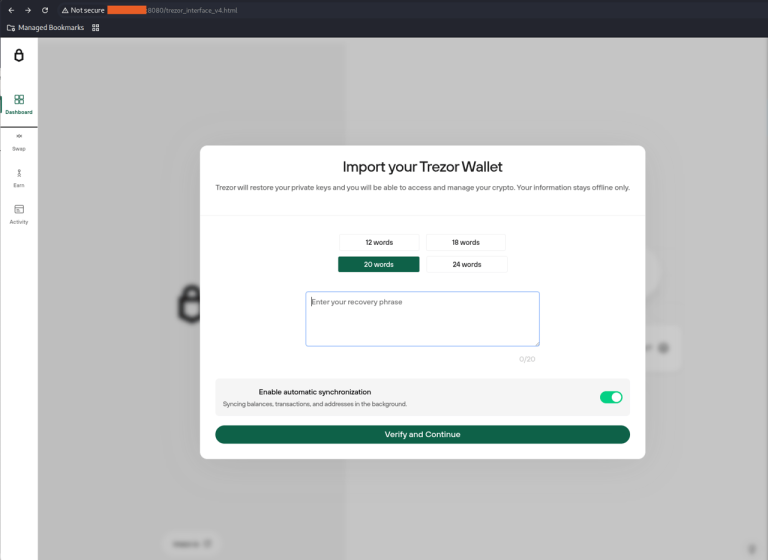
Rapid7 exposed Operation ASTERIX, a crypto fraud operation using AI, vishing, and fake wallet apps to steal seed phrases from validated holders.
CVE-2026-32475 (CVSS 9.8) is an Elementor Pro arbitrary file upload flaw risking complete site compromise across 6 million WordPress sites. Update to 4.2.2.
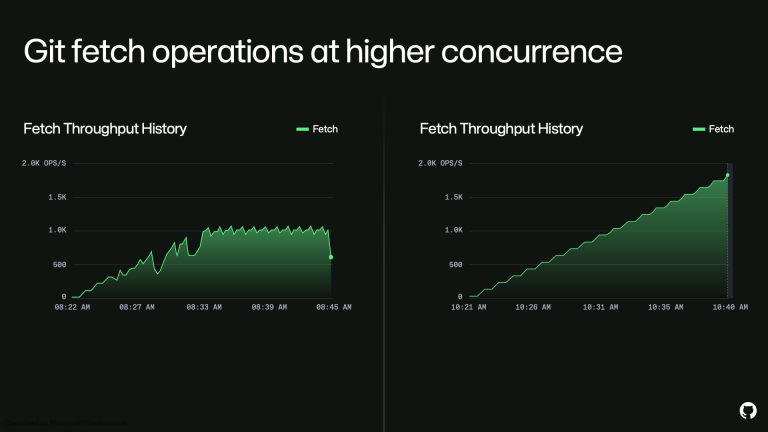
Discover the real reasons behind the recent GitHub infrastructure outage. A massive surge to 2.9 billion monthly commits forced emergency Azure migrations.
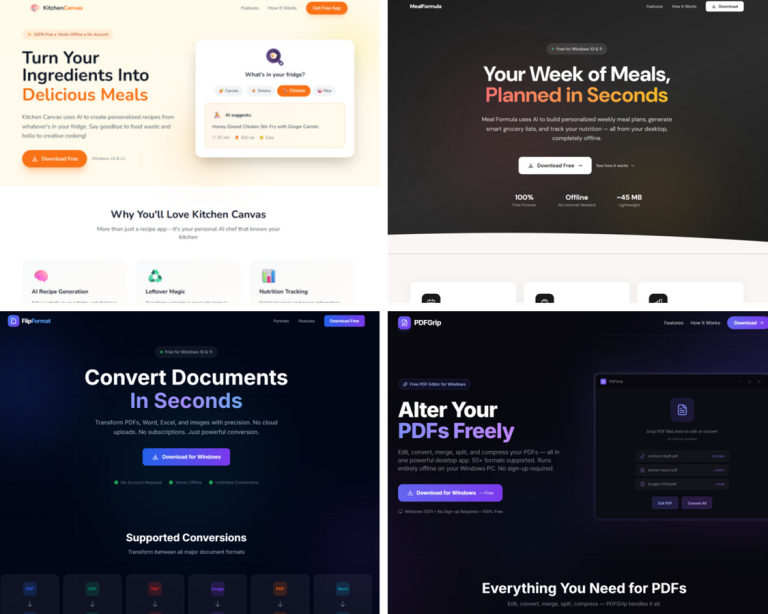
G DATA details Projextor, an Electron malware hidden in working PDF and recipe apps that runs injected scripts and captures the desktop.
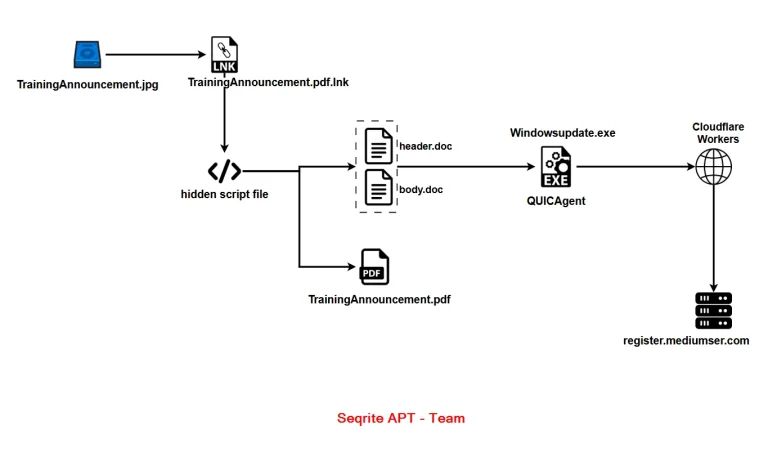
Seqrite links Operation QUICSILVER to a China-nexus actor deploying the QUICAgent Go backdoor against Myanmar government targets via a VHD lure.
Discover how Android 17 memory limits will terminate apps with severe leaks. Learn about new tools to improve your app performance and stop memory leaks.
Microsoft investigates Windows 11 gaming issues causing crashes and stuttering in the 24H2 and 25H2 August updates. Learn how to fix these anomalies.
Sakura Internet disclosed a breach of its customer management system affecting 1.36 million accounts, though passwords were hashed and salted and no ransom was demanded.
CVE-2026-77647 (CVSS 9.8) is an unauthenticated SPIP remote code execution flaw exploited in the wild. Update to SPIP 4.4.20 now.
CVE-2026-19586 (CVSS 9.3) is a pre-authentication OS command injection in TP-Link Omada gateways running OpenVPN Server. Patch the firmware now.
CVE-2026-69836 is a CVSS 10 Entra ID remote code execution flaw exploited in the wild. Microsoft has fully mitigated it server-side.
CVE-2026-59270 (CVSS 9.4) tops four Spring Security vulnerabilities. Its embedded LDAP flaw lets attackers read or modify in-memory directory entries.
CVE-2026-77176 lets a malicious operator mount arbitrary guest rootfs paths in Kata Containers Confidential Containers. Upgrade to Kata 4.1.0.
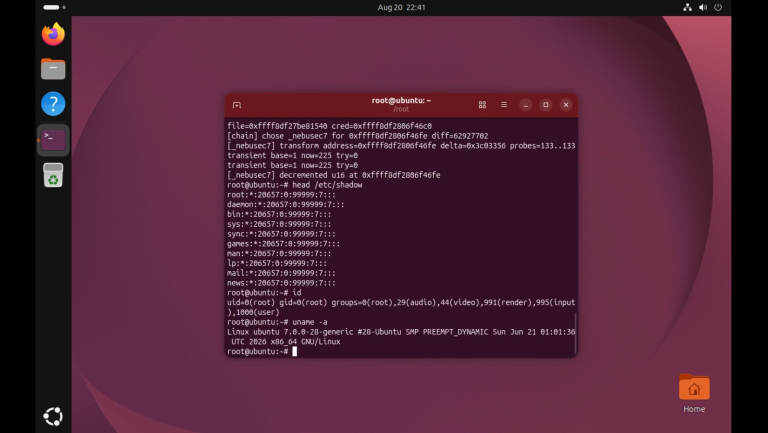
Public PoC exploit code for CVE-2026-52929, a Linux kernel SCTP flaw, escalates to root. Full vulnerability details are now disclosed.
Seven Spring GraphQL vulnerabilities were patched on August 20, including CVE-2026-59285, an unsafe deserialization flaw that can lead to remote code execution.
CISA confirms two TrueConf Server flaws, CVE-2026-72529 and CVE-2026-72530, are exploited in the wild to deliver PhantomCore malware. Patch now.
A Rust supply chain attack poisoned arrayref and two other crates to run malware at build time. Wiz ties the infrastructure to DPRK campaigns.
Google patches CVE-2026-76017, a critical use-after-free in Chrome, among 7 security fixes. Update to 151.0.7922.173 or later now.