Skip to content
October 31, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
OpenAI Advocates Stricter California AI Regulations OpenAI logo and gavel representing California AI regulations and compliance
  • Technology

OpenAI Advocates Stricter California AI Regulations

Do Son August 24, 2026 0

Discover why OpenAI now supports stricter California AI regulations and the SB 53 bill to prevent frontier models from escaping testing environments.
Weekly Threat Intelligence Report: Late August 2026 Chart summarizing the CVE weekly report with 9 exploited vulnerabilities added to the CISA KEV catalog
  • Weekly Recap

Weekly Threat Intelligence Report: Late August 2026

Do Son August 24, 2026 0

This CVE weekly report tracks 3,179 new CVEs and 9 exploited vulnerabilities added to CISA KEV, from Ray and MLflow to VMware and Apple.
Data Recovery Basics: How to Restore Lost Files Without Causing More Damage Picture1
  • Technique

Data Recovery Basics: How to Restore Lost Files Without Causing More Damage

Do Son August 24, 2026 0

Learn the basics of data recovery, avoid common mistakes, and restore lost files safely with a simple step-by-step process.
CVE-2026-19478: GitLab Flaw Exploited in the Wild, PoC Public GitLab CVE-2026-19478 critical vulnerability warning showing unauthenticated attackers delete public projects exploited in the wild
  • Vulnerability Report

CVE-2026-19478: GitLab Flaw Exploited in the Wild, PoC Public

Do Son August 23, 2026 0

GitLab CVE-2026-19478 vulnerability lets unauthenticated attackers delete public projects. Exploited in the wild with public PoC. Patch now.
LinkedIn AI Slop Reduction: A Necessary Course Correction LinkedIn platform interface showing the new report AI slop button reducing artificial content views
  • Technology

LinkedIn AI Slop Reduction: A Necessary Course Correction

Do Son August 23, 2026 0

Discover how LinkedIn successfully reduced AI slop views by 40% using a new user reporting tool. Learn about the platform's shift in generative AI policies.
Take-Two Subpoenas Microsoft and Discord Over GTA VI “Cyberleek” Leaks Take-Two GTA VI leak subpoena Microsoft Discord Cyberleek Rockstar
  • Data Leak

Take-Two Subpoenas Microsoft and Discord Over GTA VI “Cyberleek” Leaks

Do Son August 23, 2026 0

Take-Two has subpoenaed Microsoft and Discord for account data, IPs, and device IDs tied to "Cyberleek," the source behind a wave of GTA VI gameplay leaks.
Apple Music AI Labels: Combating Algorithmically Generated Spam Apple Music AI labels interface displaying artificially generated track warnings
  • Technology

Apple Music AI Labels: Combating Algorithmically Generated Spam

Do Son August 23, 2026 0

Apple Music introduces mandatory AI labels to combat the flood of algorithmically generated spam songs, ensuring transparency and protecting creator royalties.
AliExpress Audio Fingerprinting Hijacks Your Bluetooth Diagram of hidden AliExpress audio fingerprinting scripts running a silent WebAudio browser fingerprint graph
  • Data Leak

AliExpress Audio Fingerprinting Hijacks Your Bluetooth

Do Son August 23, 2026 0

AliExpress audio fingerprinting uses hidden WebAudio scripts for browser fingerprinting, silently seizing your Bluetooth audio. Learn to block it.
ChatGPT iMessage Integration: A macOS Privacy Clash ChatGPT iMessage integration interface displaying privacy warnings and Mac access prompts
  • Data Leak

ChatGPT iMessage Integration: A macOS Privacy Clash

Do Son August 23, 2026 0

Discover how the new ChatGPT iMessage integration on macOS operates. Uncover the severe privacy concerns and Apple's potential security retaliation.

TikTok Secures $400 Million Privacy Settlement TikTok logo next to a gavel representing the massive $400 million US Department of Justice settlement
  • Technology

TikTok Secures $400 Million Privacy Settlement

Do Son August 23, 2026 0

TikTok and ByteDance finalize a massive $400 million settlement with the US Department of Justice, resolving severe violations of children's privacy laws.
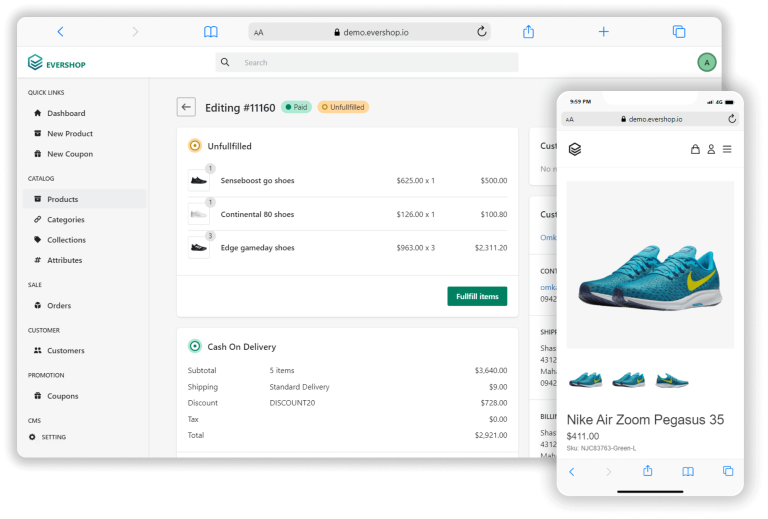
EverShop CVE-2026-72843 Flaw Allows Unauthenticated Account Takeover Diagram showing the EverShop account takeover flow and eCommerce platform vulnerability mechanism.
  • Vulnerability Report

EverShop CVE-2026-72843 Flaw Allows Unauthenticated Account Takeover

Do Son August 23, 2026 0

A critical EverShop account takeover flaw, CVE-2026-72843, exposes systems to an eCommerce platform vulnerability. Update to version 2.2.1 immediately.
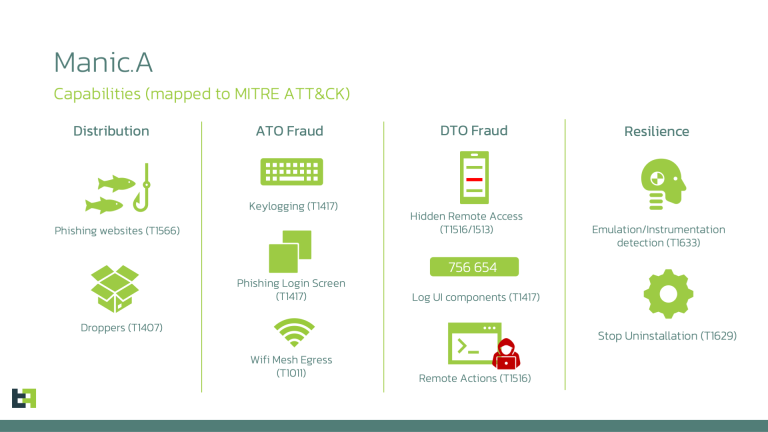
Manic Android Malware Steals Data Without Active Internet Manic Android malware utilizing offline mesh relay to steal data
  • Malware

Manic Android Malware Steals Data Without Active Internet

Do Son August 23, 2026 0

A new Manic Android malware campaign combines banking fraud and spyware, using a unique offline mesh relay to steal data even without internet access.
CVE-2026-77806: SPIP Unauthenticated RCE Exploited in the Wild as Public Exploit Lands SPIP CVE-2026-77806 unauthenticated remote code execution vulnerability exploited in the wild public exploit patch 4.4.21
  • Vulnerability Report

CVE-2026-77806: SPIP Unauthenticated RCE Exploited in the Wild as Public Exploit Lands

Do Son August 21, 2026 0

CVE-2026-77806 (CVSS 9.8) is a SPIP unauthenticated RCE exploited in the wild, with public exploit code now available. Update to SPIP 4.4.21 now.
Spring Data REST and Spring AI Vulnerabilities: Four High-Severity Flaws Patched Spring vulnerabilities advisory covering Spring Data REST and Spring AI four high severity flaws CVE-2026-47849
  • Vulnerability Report

Spring Data REST and Spring AI Vulnerabilities: Four High-Severity Flaws Patched

Do Son August 21, 2026 0

Four Spring vulnerabilities hit Spring Data REST and Spring AI, including CVE-2026-47849, a privilege escalation flaw. Patch to the fixed versions now.
CVE-2026-75501: Public PoC for Calix Router Flaw That Bypasses NAT and Firewall Protections Calix GS7 XGS router CVE-2026-75501 UPnP missing authentication flaw bypass NAT and firewall protections public PoC
  • Vulnerability Report

CVE-2026-75501: Public PoC for Calix Router Flaw That Bypasses NAT and Firewall Protections

Do Son August 21, 2026 0

CVE-2026-75501 exposes an unauthenticated UPnP service on Calix routers. Public PoC code shows how attackers bypass NAT and firewall protections.
CVE-2026-19598: Pods Plugin Flaw Enables Complete Site Takeover, Attacks Seen in the Wild Pods WordPress plugin CVE-2026-19598 privilege escalation vulnerability enabling complete site takeover attacks in the wild
  • Vulnerability Report

CVE-2026-19598: Pods Plugin Flaw Enables Complete Site Takeover, Attacks Seen in the Wild

Do Son August 21, 2026 0

CVE-2026-19598 (CVSS 9.8) in the Pods WordPress plugin enables complete site takeover. Wordfence is blocking attacks in the wild. Update now.
CVE-2026-50112: Apache CloudStack Flaw Allows Cross-Tenant Remote Code Execution on KVM Hosts Apache CloudStack CVE-2026-50112 remote code execution vulnerability on KVM hypervisor host security release advisory
  • Vulnerability Report

CVE-2026-50112: Apache CloudStack Flaw Allows Cross-Tenant Remote Code Execution on KVM Hosts

Do Son August 21, 2026 0

CVE-2026-50112 is a critical Apache CloudStack flaw enabling cross-tenant remote code execution as root on KVM hosts. Upgrade to 4.20.3.1 or 4.22.1.1.
IBM AIX Vulnerabilities: Remote Code Execution Flaws Hit CVSS 9.9 IBM AIX vulnerabilities remote code execution CVSS 9.9 security patch chart
  • Vulnerability Report

IBM AIX Vulnerabilities: Remote Code Execution Flaws Hit CVSS 9.9

Do Son August 21, 2026 0

IBM AIX vulnerabilities include remote code execution flaws rated up to CVSS 9.9. Patch AIX 7.2, 7.3, and PowerVM VIOS 4.1 now.
uutils coreutils stdbuf Flaw Lets Local Users Execute Arbitrary Code uutils coreutils vulnerability stdbuf LD_PRELOAD world-writable library flaw diagram
  • Vulnerability Report

uutils coreutils stdbuf Flaw Lets Local Users Execute Arbitrary Code

Do Son August 21, 2026 0

A uutils coreutils vulnerability in stdbuf uses a world-writable libstdbuf.so via LD_PRELOAD, letting local users execute arbitrary code.
RDK-B WebUI Vulnerabilities Let Attackers Bypass Login RDK-B WebUI vulnerabilities authentication bypass CVE-2026-19505 broadband gateway diagram
  • Vulnerability Report

RDK-B WebUI Vulnerabilities Let Attackers Bypass Login

Do Son August 21, 2026 0

Five RDK-B WebUI vulnerabilities let attackers bypass authentication and gain admin access on broadband gateways. No patch is available yet.
Leaked Corporate AWS Keys Expose Full Admin Rights leak
  • Data Leak

Leaked Corporate AWS Keys Expose Full Admin Rights

Do Son August 21, 2026 0

Truffle Security found leaked corporate AWS keys holding full control. See how leaked corporate AWS keys admin rights expose enterprise cloud accounts.
CVE-2026-18963: Unauthenticated Account Takeover Flaw Hits Keycloak Keycloak account takeover CVE-2026-18963 unauthenticated password reset flaw diagram
  • Vulnerability Report

CVE-2026-18963: Unauthenticated Account Takeover Flaw Hits Keycloak

Do Son August 21, 2026 0

A Keycloak account takeover flaw, CVE-2026-18963, lets attackers reset any user's password with no email verification. Update to 26.7.2 now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-118235CVSS 9.8
    The SimpleForm – Form Maker to Chat Apps with Quiz, Poll and Multi Lead Notifications plugin for WordPress...
    📅 Updated: Oct 31, 2026
  • CVE-2026-103882CVSS 9.1
    The Acadlix LMS – AI Quiz Maker, Online Exam & Course Plugin for WordPress plugin for WordPress is...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119096CVSS 9.8
    The Uncanny Toolkit for LearnDash plugin for WordPress is vulnerable to Authentication Bypass in versions up to, and...
    📅 Updated: Oct 31, 2026
  • CVE-2026-116512CVSS 9.8
    The Project Manager – AI Powered Project Management, Task Management, Kanban Board & Time Tracker plugin for WordPress...
    📅 Updated: Oct 31, 2026
  • CVE-2026-89270CVSS 9.1
    The Popup Builder – Create highly converting, mobile friendly marketing popups. plugin for WordPress is vulnerable to authorization...
    📅 Updated: Oct 31, 2026
  • CVE-2026-116557CVSS 9.1
    The WP Booking System - Booking Calendar plugin for WordPress is vulnerable to unauthorized modification of data due...
    📅 Updated: Oct 31, 2026
  • CVE-2026-109220CVSS 9.8
    The PDF Invoice for WooCommerce + Drag and Drop Template Builder plugin for WordPress is vulnerable to PHP...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119263CVSS 9.6
    Memory corruption in GarbageCollection in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.