
 Do Son
an attacker could exploit the CVE-2022-32917 vulnerability to execute arbitrary code with kernel privileges.
Latest Technology News

Apache Calcite released the latest security bulletin on September 11, which contains an XML External Entity (XEE) vulnerability (CVE-2022-39135)

an attacker could exploit the CVE-2022-2964 vulnerability to execute arbitrary code or cause a denial of service condition on the system
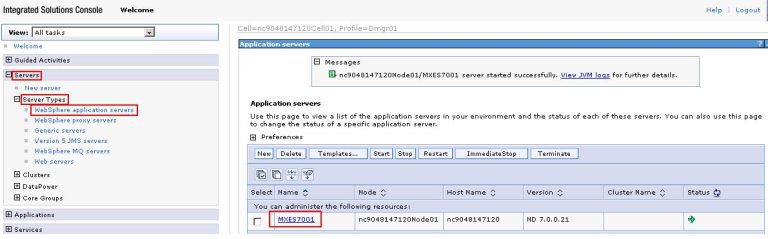
The security hole that allows HTTP header injection is tracked as CVE-2022-34165, and this is "caused by improper validation."

CVE-2022-31474 allows an attacker to view the contents of any file on your server that can be read by your WordPress installation

CISA this week added 12 new actively exploited vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog

Traced as CVE-2022-30078, the security weakness impacts the Netgear R6200_v2 and R6300v2 routers with the latest firmware

About four decades ago, the world started to see the corporate world being revolutionized. With numerous new...

CVE-2022-20923 affects Cisco Small Business RV110W, RV130, RV130W, RV215W Routers and it can be exploited by remote, unauthenticated attacker

The CVE-2022-20696 hole can impact several Cisco products if they are running a Cisco SD-WAN vManage Software prior to 20.9.1.
Latest Technology News
Apache Calcite released the latest security bulletin on September 11, which contains an XML External Entity (XEE) vulnerability (CVE-2022-39135)
an attacker could exploit the CVE-2022-2964 vulnerability to execute arbitrary code or cause a denial of service condition on the system
The security hole that allows HTTP header injection is tracked as CVE-2022-34165, and this is "caused by improper validation."
CVE-2022-31474 allows an attacker to view the contents of any file on your server that can be read by your WordPress installation
CISA this week added 12 new actively exploited vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog
Traced as CVE-2022-30078, the security weakness impacts the Netgear R6200_v2 and R6300v2 routers with the latest firmware
About four decades ago, the world started to see the corporate world being revolutionized. With numerous new...
CVE-2022-20923 affects Cisco Small Business RV110W, RV130, RV130W, RV215W Routers and it can be exploited by remote, unauthenticated attacker
The CVE-2022-20696 hole can impact several Cisco products if they are running a Cisco SD-WAN vManage Software prior to 20.9.1.
CVE-2022-26447 allows a remote attacker to execute arbitrary code on the system, caused by an out-of-bounds write