Skip to content
September 16, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Accelerating Business Growth: 8 Tips and Considerations Andariel APT
  • Technique

Accelerating Business Growth: 8 Tips and Considerations

Do Son June 8, 2026 0
Read More Read more about Accelerating Business Growth: 8 Tips and Considerations
Check Point VPN Vulnerability Exploited in the Wild with Ransomware Links Check Point VPN vulnerability exploited in the wild Check Point VPN exploit CVE-2026-50751 zero-day Checkmarx Breach Supply Chain Attack Ivanti EPMM RCE CVE-2026-1281 Modular DS Vulnerability CVE-2026-23550 D-Link RCE Vulnerability CVE-2026-0625 Christmas 2025 GreyNoise Campaign, Japan-Based Initial Access Broker React2Shell Zero-Day, APT Active Exploitation WordPress vulnerability, authentication bypass FreePBX, zero-day Trend Micro Apex One, Remote Code Execution BitoPro Hack, Crypto Theft UNC5337 - CVE-2022-47945 Safe{Wallet} hack Fortinet vulnerability, CVE-2024-21762, FortiGate attack Balloonfly, Play ransomware Ivanti EPMM CVE-2025-4427 and CVE-2025-4428
  • Vulnerability Report

Check Point VPN Vulnerability Exploited in the Wild with Ransomware Links

Do Son June 8, 2026 0
Read More Read more about Check Point VPN Vulnerability Exploited in the Wild with Ransomware Links
Best B2B Tech Marketing Agencies tech
  • Technique

Best B2B Tech Marketing Agencies

Do Son June 8, 2026 0
Read More Read more about Best B2B Tech Marketing Agencies
Cyber Espionage Campaign Targets Global Stock Exchange Executive AdaptixC2 Abuse, Russian Cybercrime RondoDox Botnet, Exploit Shotgun China Cyber Power, Red Hackers Nvidia cyberattack
  • Cybercriminals

Cyber Espionage Campaign Targets Global Stock Exchange Executive

Do Son June 8, 2026 0
Read More Read more about Cyber Espionage Campaign Targets Global Stock Exchange Executive
Massive Smishing Error524 Campaign Evades Traditional Security Filters Worldwide Smishing Error524 campaign Group-IB phishing report
  • Cybercriminals

Massive Smishing Error524 Campaign Evades Traditional Security Filters Worldwide

Do Son June 8, 2026 0
Read More Read more about Massive Smishing Error524 Campaign Evades Traditional Security Filters Worldwide
Instagram Account Recovery Flaw Exploited via AI Support Tool Instagram account recovery flaw Meta incident notification Meta AI data center Louisiana Meta AI news partnerships Meta AI Shopping Assistant Meta Vibes standalone app Meta Oversight Board account ban, Instagram permanent suspension review Meta Compute initiative 2026, personal superintelligence nuclear power Meta AI News Licensing Publisher Content Deal Meta Project Mercury Omnilingual ASR 1600 Languages Meta $600B Investment, AI Data Centers Meta AI strategy, Llama models Meta AI Glasses, Smart Glasses
  • Data Leak

Instagram Account Recovery Flaw Exploited via AI Support Tool

Do Son June 8, 2026 0
Read More Read more about Instagram Account Recovery Flaw Exploited via AI Support Tool
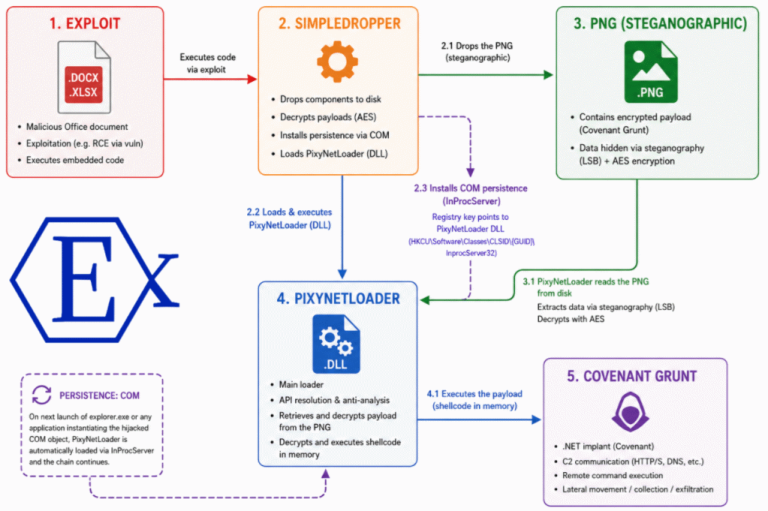
PixyNetLoader Malware Analysis: How APT28 Hides Payloads Inside PNG Files PixyNetLoader malware analysis APT28 steganography attack
  • Malware

PixyNetLoader Malware Analysis: How APT28 Hides Payloads Inside PNG Files

Do Son June 8, 2026 0
Read More Read more about PixyNetLoader Malware Analysis: How APT28 Hides Payloads Inside PNG Files
Redis DarkReplica Exploit: Full PoC Code and Technical Details Released CVE-2022-35951 Redis DarkReplica exploit CVE-2026-23631 public disclosure
  • Vulnerability

Redis DarkReplica Exploit: Full PoC Code and Technical Details Released

Do Son June 8, 2026 0
Read More Read more about Redis DarkReplica Exploit: Full PoC Code and Technical Details Released
Broadcom Fixes Critical VMware Stored XSS Bugs VMware stored XSS bugs Broadcom security updates CVE-2023-34039 VMware RCE, virtualization security
  • Vulnerability Report

Broadcom Fixes Critical VMware Stored XSS Bugs

Do Son June 8, 2026 0
Read More Read more about Broadcom Fixes Critical VMware Stored XSS Bugs
Infrastructure Anomaly: GitHub Suffers Unidentified Global Outage GitHub outage today
  • Technology

Infrastructure Anomaly: GitHub Suffers Unidentified Global Outage

Do Son June 8, 2026 0
Read More Read more about Infrastructure Anomaly: GitHub Suffers Unidentified Global Outage
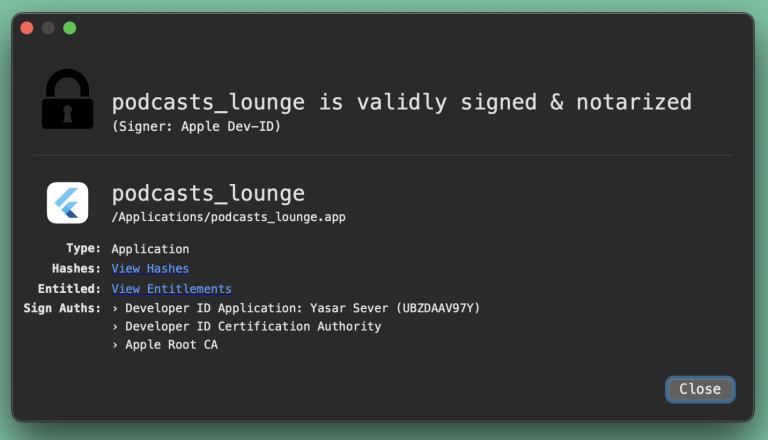
Operation FlutterBridge Malware Targets macOS Platforms with Backdoor Capabilities Operation FlutterBridge malware WebView-based architecture
  • Malware

Operation FlutterBridge Malware Targets macOS Platforms with Backdoor Capabilities

Do Son June 8, 2026 0
Read More Read more about Operation FlutterBridge Malware Targets macOS Platforms with Backdoor Capabilities
Financial Exposure in the Cloud: Persistent Gemini API Caching Flaw Incurs Severe Billing Anomalies Gemini API billing bug
  • Technology

Financial Exposure in the Cloud: Persistent Gemini API Caching Flaw Incurs Severe Billing Anomalies

Do Son June 8, 2026 0
Read More Read more about Financial Exposure in the Cloud: Persistent Gemini API Caching Flaw Incurs Severe Billing Anomalies
Sovereign Portability: Google Password Manager Embraces Credential Exchange Protocols Google passkey import export
  • Technology

Sovereign Portability: Google Password Manager Embraces Credential Exchange Protocols

Do Son June 8, 2026 0
Read More Read more about Sovereign Portability: Google Password Manager Embraces Credential Exchange Protocols
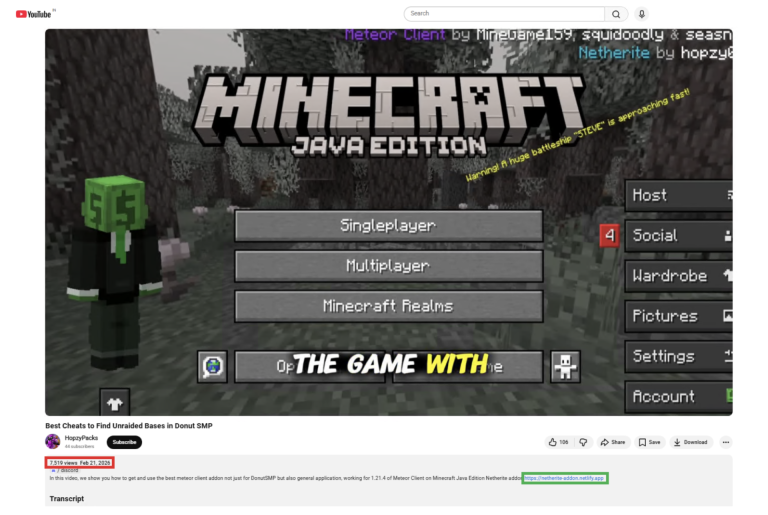
Deceptive WeedHack Malware Campaign Infects Thousands of Minecraft Players WeedHack malware campaign free Minecraft mods
  • Malware

Deceptive WeedHack Malware Campaign Infects Thousands of Minecraft Players

Do Son June 8, 2026 0
Read More Read more about Deceptive WeedHack Malware Campaign Infects Thousands of Minecraft Players
The Fractured Evolution of Wireless Connectivity: Stagnant Wi-Fi 7 Adoption and the Emergence of Wi-Fi 8 Wi-Fi 8 standard features
  • Technology

The Fractured Evolution of Wireless Connectivity: Stagnant Wi-Fi 7 Adoption and the Emergence of Wi-Fi 8

Do Son June 8, 2026 0
Read More Read more about The Fractured Evolution of Wireless Connectivity: Stagnant Wi-Fi 7 Adoption and the Emergence of Wi-Fi 8
Shopper Laravel Flaw Exploit Sparks Urgent E-Commerce Security Warning Shopper Laravel flaw Shopper Laravel flaw exploit
  • Vulnerability Report

Shopper Laravel Flaw Exploit Sparks Urgent E-Commerce Security Warning

Do Son June 8, 2026 0
Read More Read more about Shopper Laravel Flaw Exploit Sparks Urgent E-Commerce Security Warning
Verizon IMS Vulnerability: Critical VoLTE Flaw Discovered VoLTE signaling vulnerability Verizon IMS security
  • Vulnerability Report

Verizon IMS Vulnerability: Critical VoLTE Flaw Discovered

Do Son June 8, 2026 0
Read More Read more about Verizon IMS Vulnerability: Critical VoLTE Flaw Discovered
Critical Sitefinity Vulnerabilities: CVSS 10.0 Security Alert Sitefinity critical vulnerabilities Sitefinity security update CVE-2024-7763 - CVE-2024-8785 exploit CVE-2025-1758
  • Vulnerability Report

Critical Sitefinity Vulnerabilities: CVSS 10.0 Security Alert

Do Son June 8, 2026 0
Read More Read more about Critical Sitefinity Vulnerabilities: CVSS 10.0 Security Alert
Collibra Platform Agent Flaws Allow Remote Code Execution Without Authentication Collibra Platform Agent flaw Zip Slip vulnerability during extraction
  • Vulnerability Report

Collibra Platform Agent Flaws Allow Remote Code Execution Without Authentication

Do Son June 8, 2026 0
Read More Read more about Collibra Platform Agent Flaws Allow Remote Code Execution Without Authentication
Weekly Threat Intelligence: June 1 to June 7, 2026 Weekly Threat Intelligence Vulnerability Management Report
  • Weekly Recap

Weekly Threat Intelligence: June 1 to June 7, 2026

Do Son June 8, 2026 0
Read More Read more about Weekly Threat Intelligence: June 1 to June 7, 2026
Critical Cloud Foundry Key Disclosure Bug Exposes JWT Signing Keys Cloud Foundry UAA vulnerability SAML authentication bypass, CVE-2026-41005 Cloud Foundry key disclosure Elliptic Curve private keys
  • Vulnerability Report

Critical Cloud Foundry Key Disclosure Bug Exposes JWT Signing Keys

Do Son June 8, 2026 0
Read More Read more about Critical Cloud Foundry Key Disclosure Bug Exposes JWT Signing Keys
Millions of Servers At Risk: Crucial MariaDB Flaw Carries Maximum 10.0 CVSS Score MariaDB security flaw community server releases
  • Vulnerability Report

Millions of Servers At Risk: Crucial MariaDB Flaw Carries Maximum 10.0 CVSS Score

Do Son June 7, 2026 0
Read More Read more about Millions of Servers At Risk: Crucial MariaDB Flaw Carries Maximum 10.0 CVSS Score
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2026-87886
    Exploitation of this vulnerability has been detected in the wild in limited, targeted attacks against Acronis Backup plugin...
    Admin intel📅 Updated: Sep 16, 2026
  • CVE-2026-87827CVSS 10.0
    Certain KGUARD DVR devices running vulnerable firmware expose a system command execution service on all network interfaces without...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-78006CVSS 9.8
    The The Events Calendar plugin for WordPress is vulnerable to Remote Code Execution in all versions up to,...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-39364
    Vite is a frontend tooling framework for JavaScript. From 7.1.0 to before 7.3.2 and 8.0.5, on the Vite...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-27540CVSS 9.0
    Unrestricted Upload of File with Dangerous Type vulnerability in Rymera Web Co Pty Ltd. Woocommerce Wholesale Lead Capture...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-76461CVSS 9.8
    A vulnerability in the email parsing of Cisco AsyncOS Software for Cisco Secure Email Gateway could allow an...
    CISA KEV📅 Added to KEV: Sep 14, 2026
  • CVE-2026-51990
    A critical remote code execution vulnerability in Sogou Input Method, one of the most widely used Chinese-language input...
    Admin intel📅 Updated: Sep 12, 2026
  • CVE-2026-85706CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, an unauthenticated user could have read arbitrary files from...
    Admin intelCISA KEV📅 Added to KEV: Sep 11, 2026📅 Updated: Sep 11, 2026
Powered by CVE Watchtower

🔴 Live Critical Threats

  • CVE-2026-73807CVSS 9.8
    The mySCADA myPRO Manager command API does not properly enforce authentication for...
  • CVE-2026-81855CVSS 9.1
    A hardcoded cryptographic client authentication key vulnerability exists in the robot testing...
  • CVE-2026-78225CVSS 9.0
    A hardcoded cryptographic server key vulnerability exists in the deployer-ng Update Controller...
  • CVE-2026-61560CVSS 9.8
    `@zereight/mcp-gitlab` is a Model Context Protocol server for GitLab. Prior to version...
  • CVE-2026-73437CVSS 9.6
    On affected platforms running Arista EOS with Dynamic Host Configuration Protocol (DHCP)...
  • CVE-2026-61559CVSS 9.6
    `@zereight/mcp-gitlab` is a Model Context Protocol server for GitLab. Starting in version...
  • CVE-2026-91939CVSS 9.8
    Cotonti 1.0.0 Comments plugin passes the ci GET parameter to unserialize() without...
  • CVE-2026-61568CVSS 9.6
    `@zereight/mcp-gitlab` is a Model Context Protocol server for GitLab. Versions prior to...
  • CVE-2026-66887CVSS 9.6
    The affected products are missing authorization on state-changing CGIs and session checks...
  • CVE-2026-66890CVSS 9.6
    The affected products use hard-coded credentials, which could allow remote access to...
Powered by CVE WATCHTOWER

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.